
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
279 results
stackrox preview

stackrox

GitHubstackrox/stackrox

The StackRox Kubernetes Security Platform performs a risk analysis of the container environment, delivers visibility and runtime alerts, and provides…
anomaly-detectioncloud-infrastructure-securitycloud-security+6
1.3k
8h 56m ago
KQL-threat-hunting-queries preview

KQL-threat-hunting-queries

GitHubcyb3rmik3/kql-threat-hunting-queries

A repository of KQL queries focused on threat hunting and threat detecting for Microsoft Sentinel & Microsoft XDR (Former Microsoft 365 Defender).
ctfcurated-resourceseducation+4
8029h 23m ago
kismet preview

kismet

GitHubkismetwireless/kismet

Github mirror of official Kismet repository
information-gatheringintrusion-detectionnetwork-security+2
2.3k12 hours ago
vulnerability-poc preview

vulnerability-poc

GitHubfankh/vulnerability-poc

CVE proof-of-concept labs, exploit scripts, and detection/prevention rules (Nginx, Apache, Snort, YARA) for high-severity CVEs. Authorized security…

ctfeducationexploitation+5
12013h 37m ago
zeek preview

zeek

GitHubzeek/zeek

Zeek is a powerful network analysis framework that is much different from the typical IDS you may know.
anomaly-detectionanti-botdefensive-tools+14
8.2k16h 16m ago
Azure-Sentinel preview

Azure-Sentinel

GitHubazure/azure-sentinel

Cloud-native SIEM for intelligent security analytics for your entire enterprise.

cloud-securitycurated-resourcesdefensive-tools+5
6.2k18h 16m ago
suricata preview

suricata

GitHuboisf/suricata

Open-source network IDS/IPS/NSM engine for real-time traffic inspection, intrusion detection and prevention, protocol analysis, and rule-based threat…

anomaly-detectionanti-botdefensive-tools+9
6.8k1 day ago
jev-ids preview

jev-ids

GitHubjev-sec/jev-ids

Blazing-Fast Token-Efficient Intrusion Detection System (IDS) based on TypeSafe's Jev.
anomaly-detectiondefensive-toolsintrusion-detection+5
301 day ago
detection-rules preview

detection-rules

GitHubelastic/detection-rules

Develop, validate, and publish SIEM detection rules for Elastic Security, with Python CLI tooling, KQL parsing, Kibana integration, and packaged…

anomaly-detectioncurated-resourcesdefensive-tools+3
2.9k1 day ago
signature-base preview

signature-base

GitHubneo23x0/signature-base

YARA signature and IOC database for my scanners and tools
curated-resourcesdigital-forensicsforensics+7
3.1k2 days ago
pySigma-backend-opensearch preview

pySigma-backend-opensearch

GitHubsigmahq/pysigma-backend-opensearch

pySigma OpenSearch backend

defensive-toolsintrusion-detectionlog-analysis+1
152 days ago
stop-bots preview

stop-bots

GitHubivankovic/stop-bots

Automate stopping bad bots from accessing your server
anti-botconfiguration-auditingdefensive-tools+6
103 days ago
sigma-cli preview

sigma-cli

GitHubsigmahq/sigma-cli

The Sigma command line interface based on pySigma

defensive-toolsintrusion-detectionlog-analysis+2
2203 days ago
yeti preview

yeti

GitHubyeti-platform/yeti

Your Everyday Threat Intelligence

digital-forensicseducationforensics+8
2.0k3 days ago
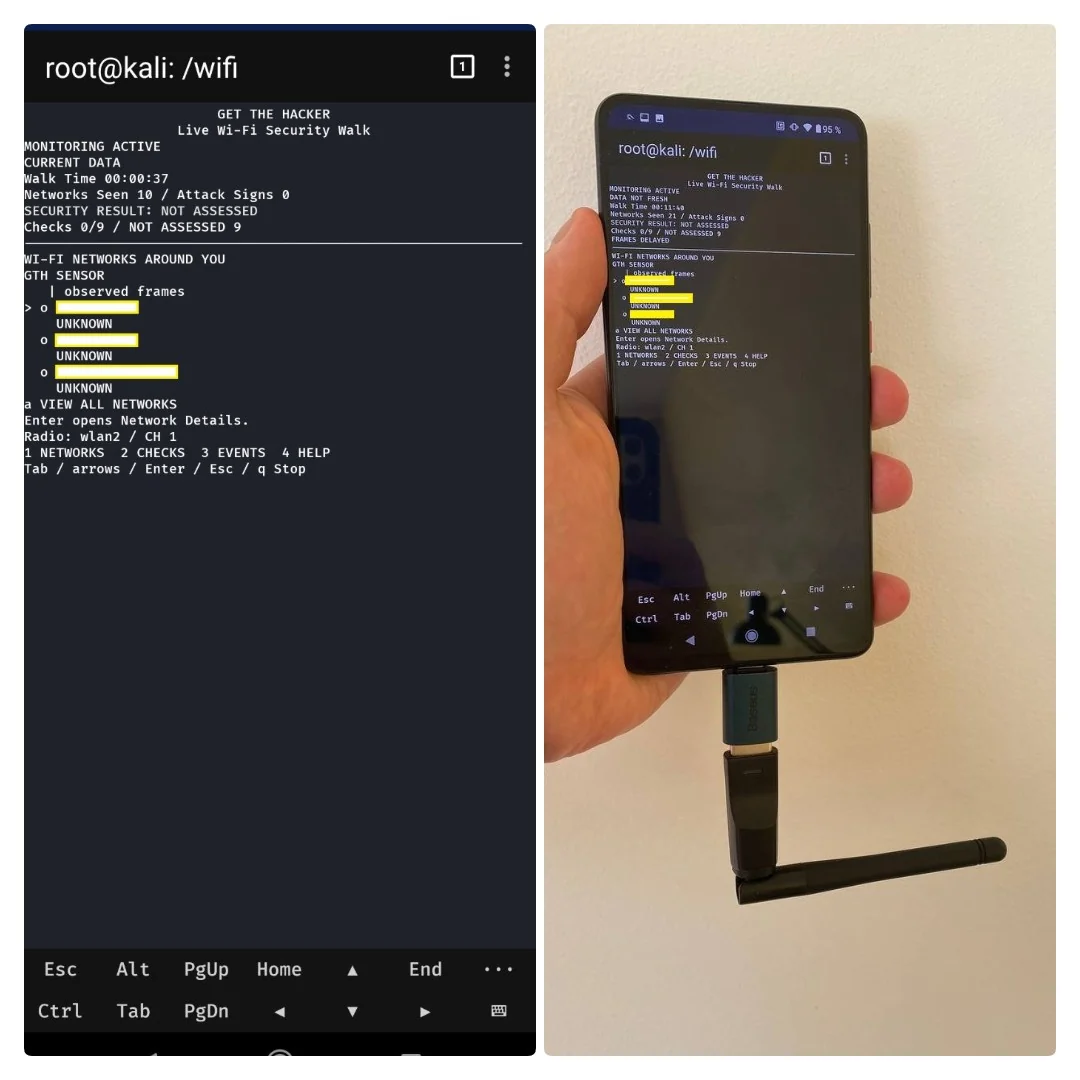
get-the-hacker preview

get-the-hacker

GitHubbuybitart/get-the-hacker

Hunt WiFi threats silently. Catch the hackers.

defensive-toolsincident-responseintrusion-detection+5
4 days ago
Threat-Hunting preview

Threat-Hunting

GitHuba2awais/threat-hunting

Curated collection of threat hunting and detection queries for CrowdStrike Falcon (CQL) and Microsoft Defender XDR (KQL), mapped to MITRE ATT&CK…

educationincident-responseinformation-gathering+4
864 days ago
Lab4PurpleSec preview

Lab4PurpleSec

GitHub0xmr007/lab4purplesec

Lab4PurpleSec is a modular Purple Team homelab combining a vulnerable Active Directory environment (GOAD), a Docker-based web DMZ, pfSense +…
educationids-ips-evasionintrusion-detection+5
3334 days ago
ecs-logstash-mappings preview

ecs-logstash-mappings

GitHubcorelight/ecs-logstash-mappings

Mapping Corelight or Zeek data to Elastic Common Schema logs

incident-responseintrusion-detectionlog-analysis+2
125 days ago
Previous12…16Next