
detection-rules
 elastic/detection-rules
Develop, validate, and publish SIEM detection rules for Elastic Security, with Python CLI tooling, KQL parsing, Kibana integration, and packaged…
anomaly-detectioncurated-resourcesdefensive-tools+3
2.9k
elastic/detection-rulesDevelop, validate, and publish SIEM detection rules for Elastic Security, with Python CLI tooling, KQL parsing, Kibana integration, and packaged…
 neo23x0/signature-base
YARA signature and IOC database for my scanners and tools
 azure/azure-sentinel
Cloud-native SIEM for intelligent security analytics for your entire enterprise.
 ivankovic/stop-bots
Automate stopping bad bots from accessing your server
 gitlab-security-oss/tldr
Sigma-based detection rules, log queries, atomic tests, and response procedures for monitoring and threat hunting in GitLab environments.
 sigmahq/sigma-cli
The Sigma command line interface based on pySigma
 arpsyndicate/vedas-signatures
VEDAS-Driven Autonomous Generation + Community Contributions of Suricata & Nuclei Rules for over 15k CVEs

 huntresslabs/threat-intel
This repository contains supplemental items including IOCs, and signatures discussed in Huntress blogposts, and other media.
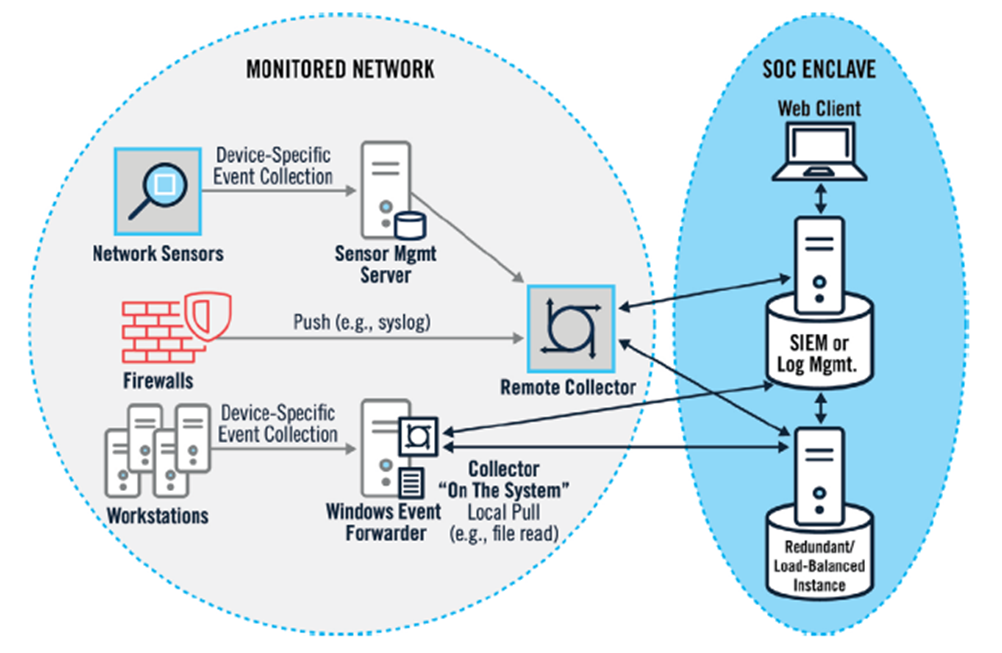 cyb3rxp/awesome-soc
A curated knowledge base to build, run and mature a SOC (including CSIRT).
 misp/misp
MISP (core software) - Open Source Threat Intelligence and Sharing Platform
 manishrawat21/detection-rules
This repository contains validated detection rules for adversary behaviors observed during APT29 simulation. Each rule was tested against the actual…
 jdinovo/spade
SPaT Attack Detection and Evaluation dataset
 chpratik/nginx_2026_cve_bundle_cti_report
Covered CVEs: CVE-2026-28755, CVE-2026-42926, CVE-2026-9256, CVE-2026-42055, CVE-2026-42533
 ttlab-research/awesome-wazuh
🛡️Awesome lists about all kinds of interesting topics of Wazuh XDR/SIEM
 anuththara2007-w/cve-2026-20127-exploit-extension
Offline browser extension providing defensive analysis and detection guidance for CVE-2026-20127, with packet visualization, IOC extraction, and…
 the-dfir-report/sigma-rules
Rules generated from our investigations.
 trustedsec/sysmoncommunityguide
TrustedSec Sysinternals Sysmon Community Guide