libpcap
 the-tcpdump-group/libpcap
System-independent library for user-level packet capture and filtering. Provides a portable framework for low-level network monitoring, security…
dns-analysisinformation-gatheringintrusion-detection+3
3.2k
the-tcpdump-group/libpcapSystem-independent library for user-level packet capture and filtering. Provides a portable framework for low-level network monitoring, security…
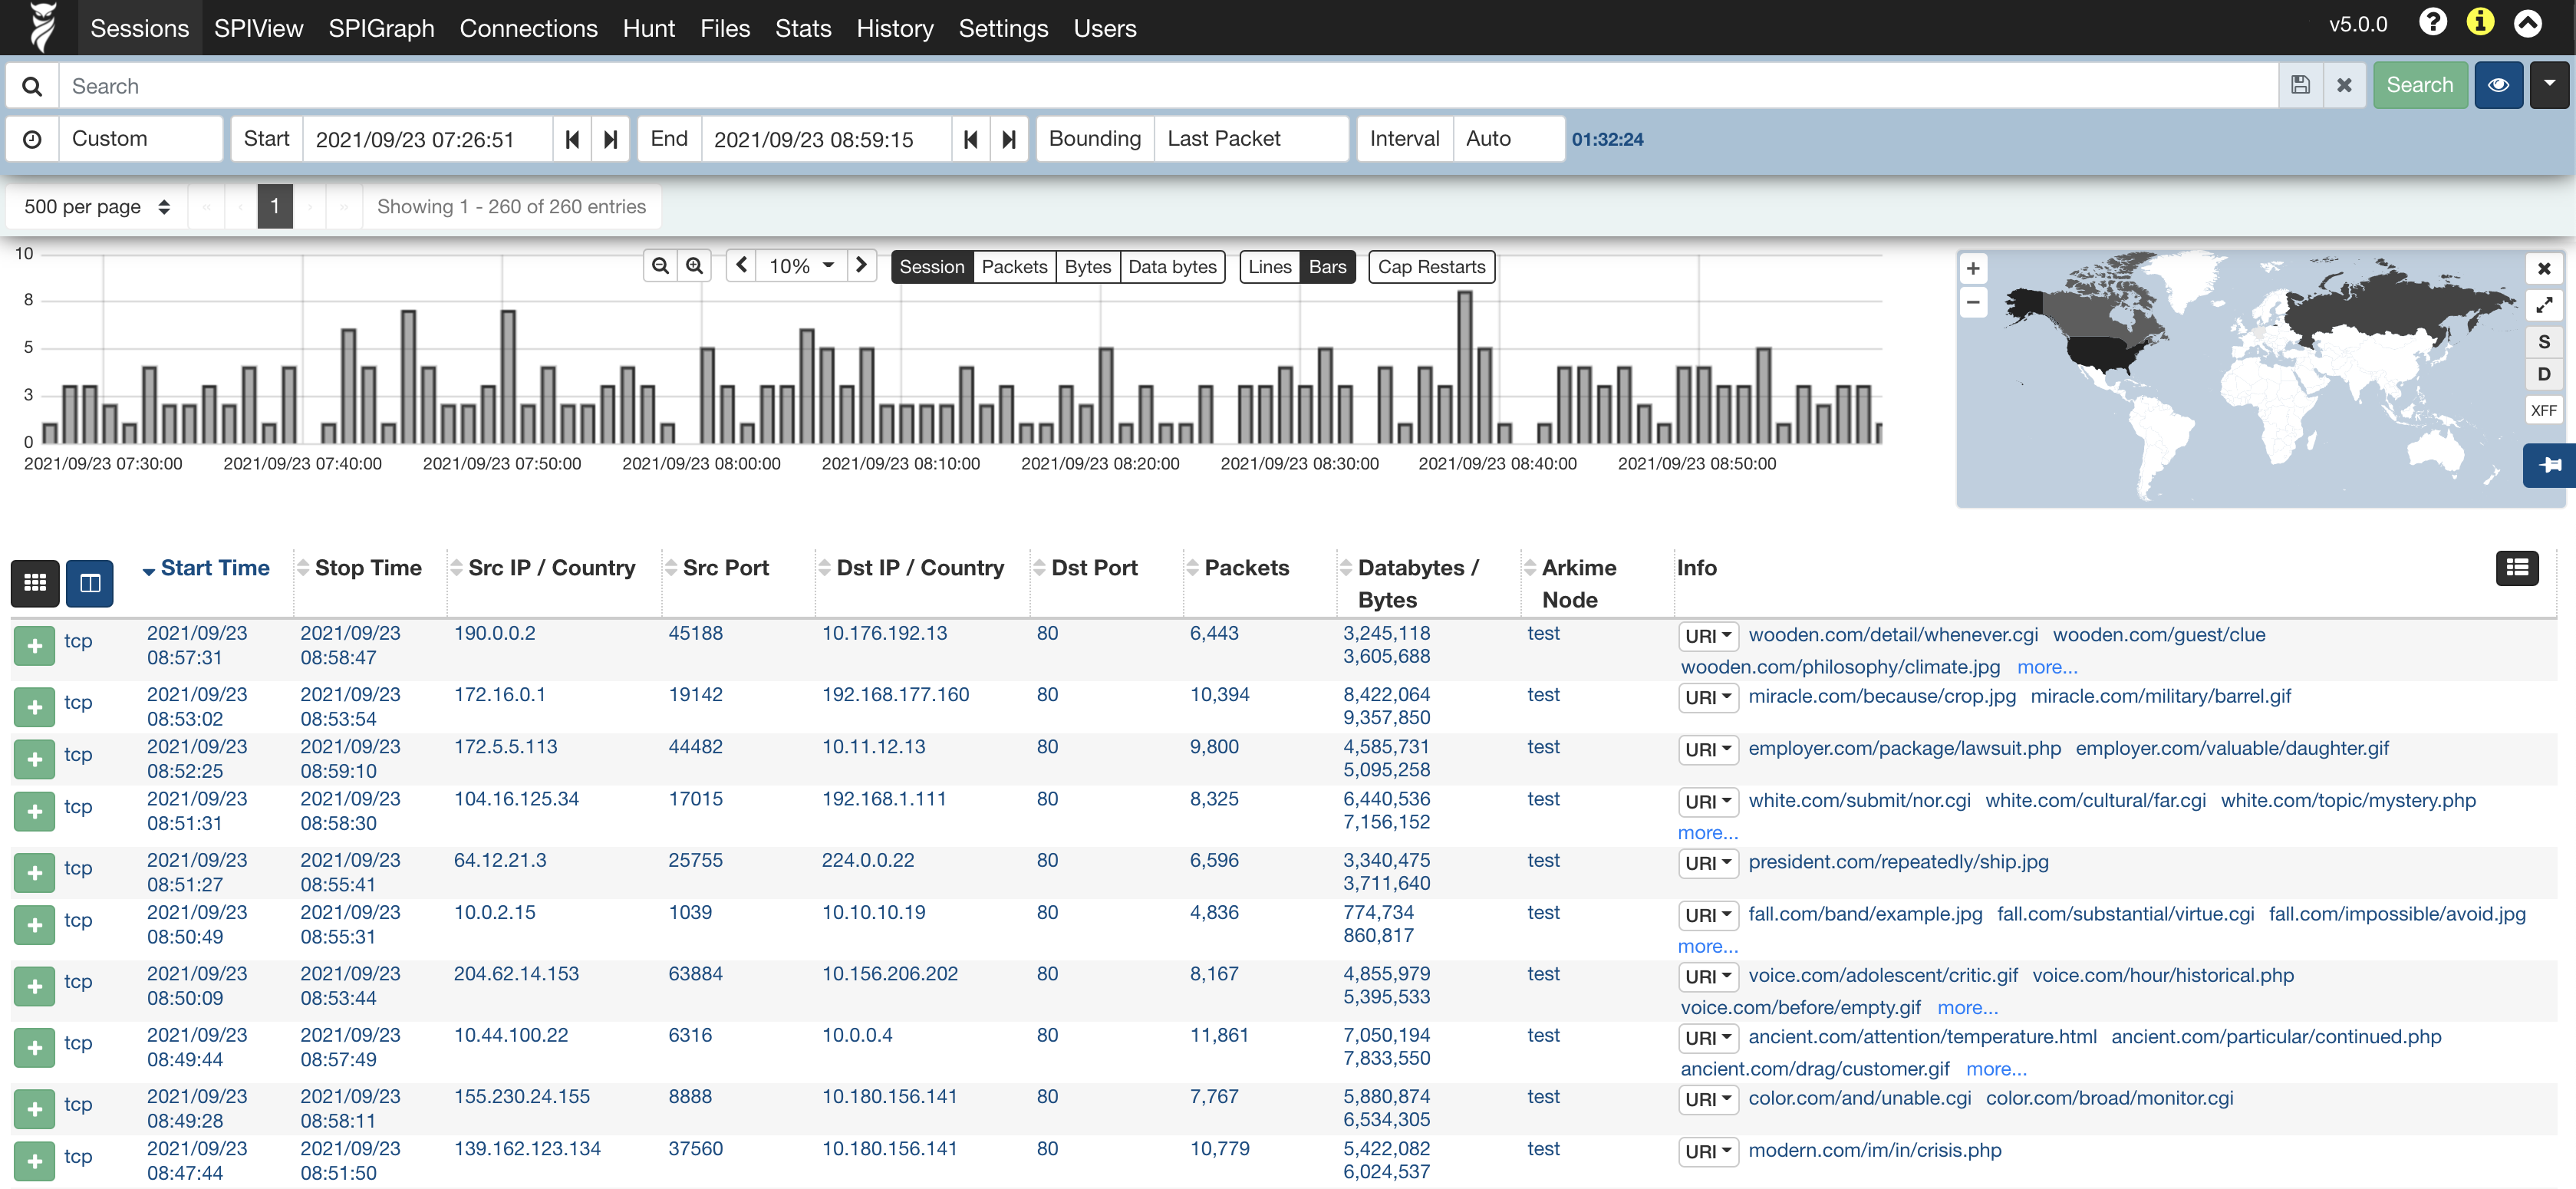 arkime/arkime
Arkime is an open source, large scale, full packet capturing, indexing, and database system.
 kismetwireless/kismet
Github mirror of official Kismet repository
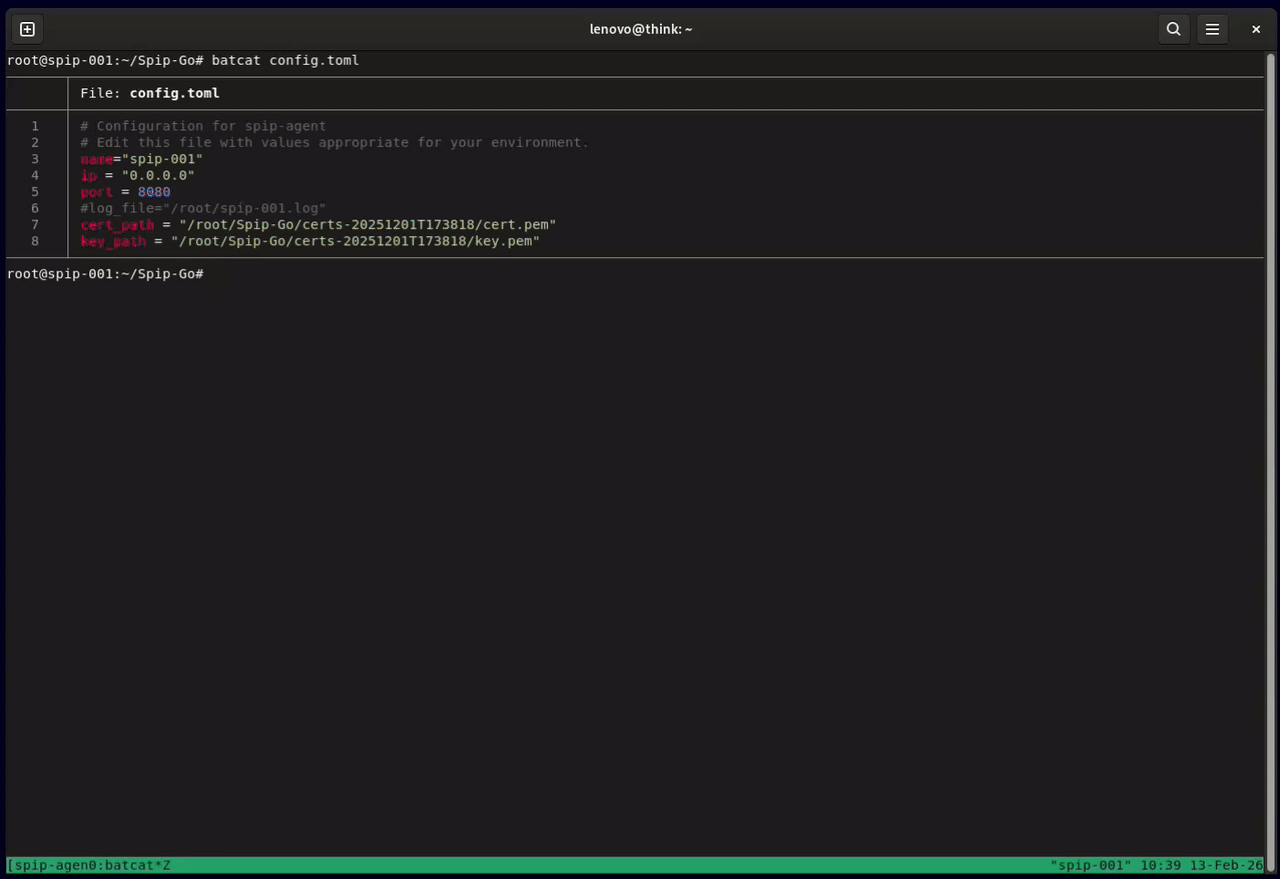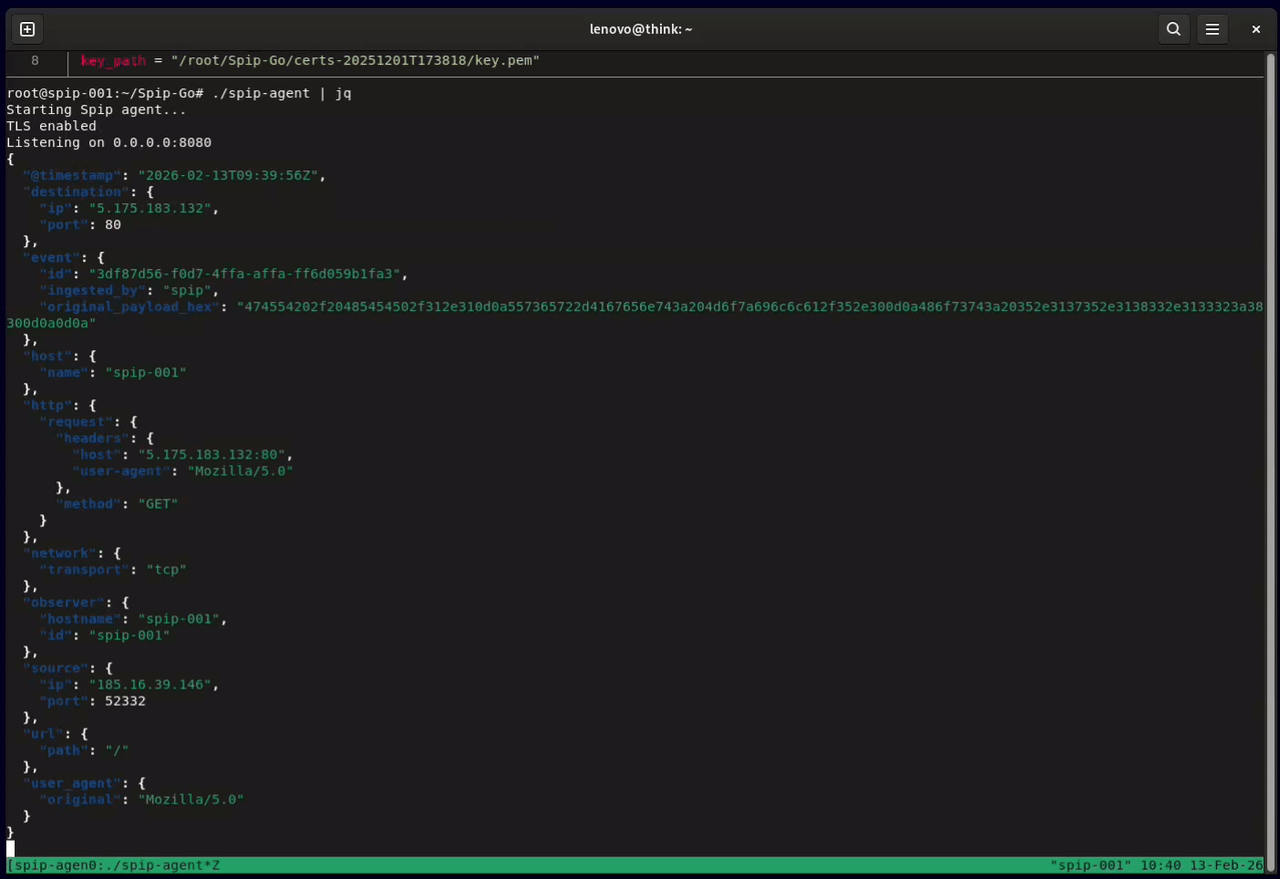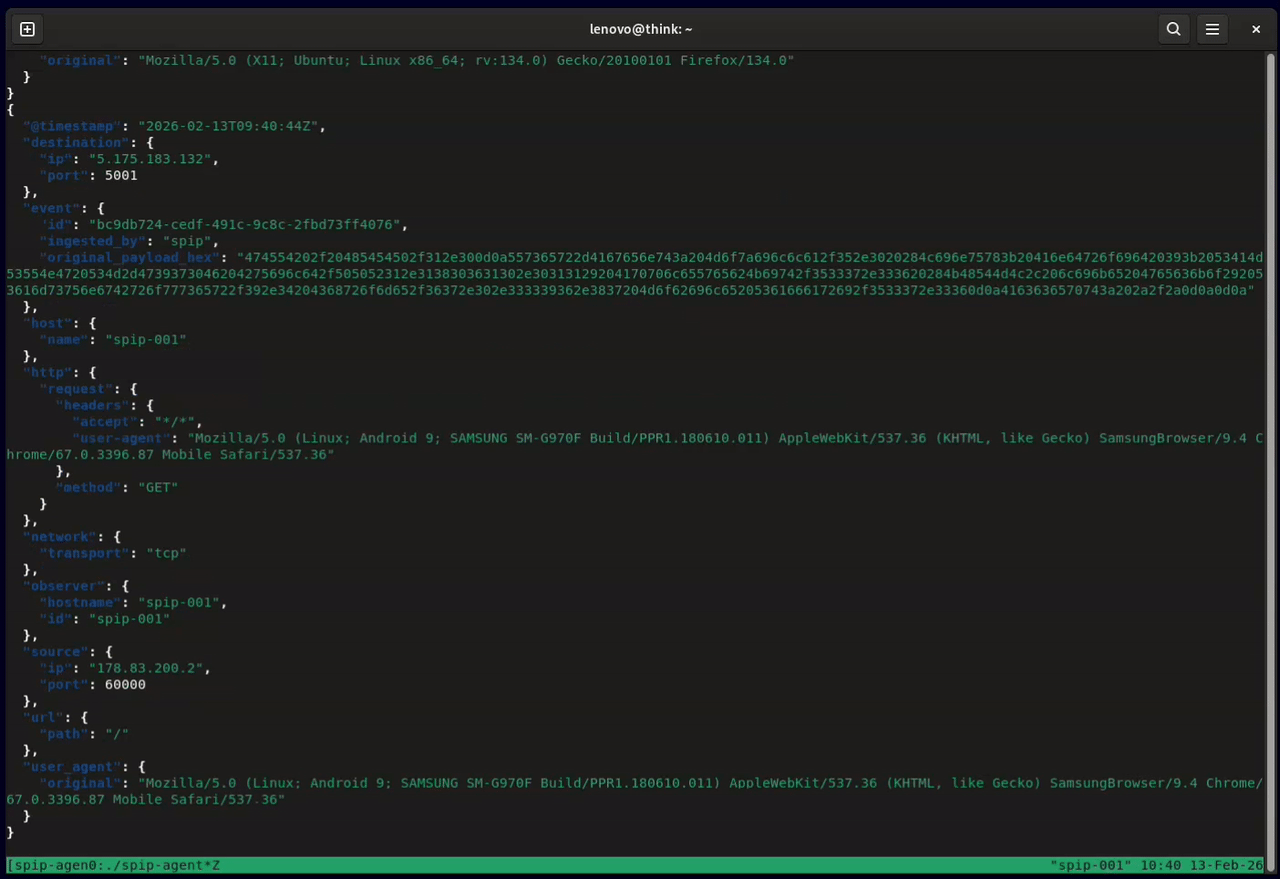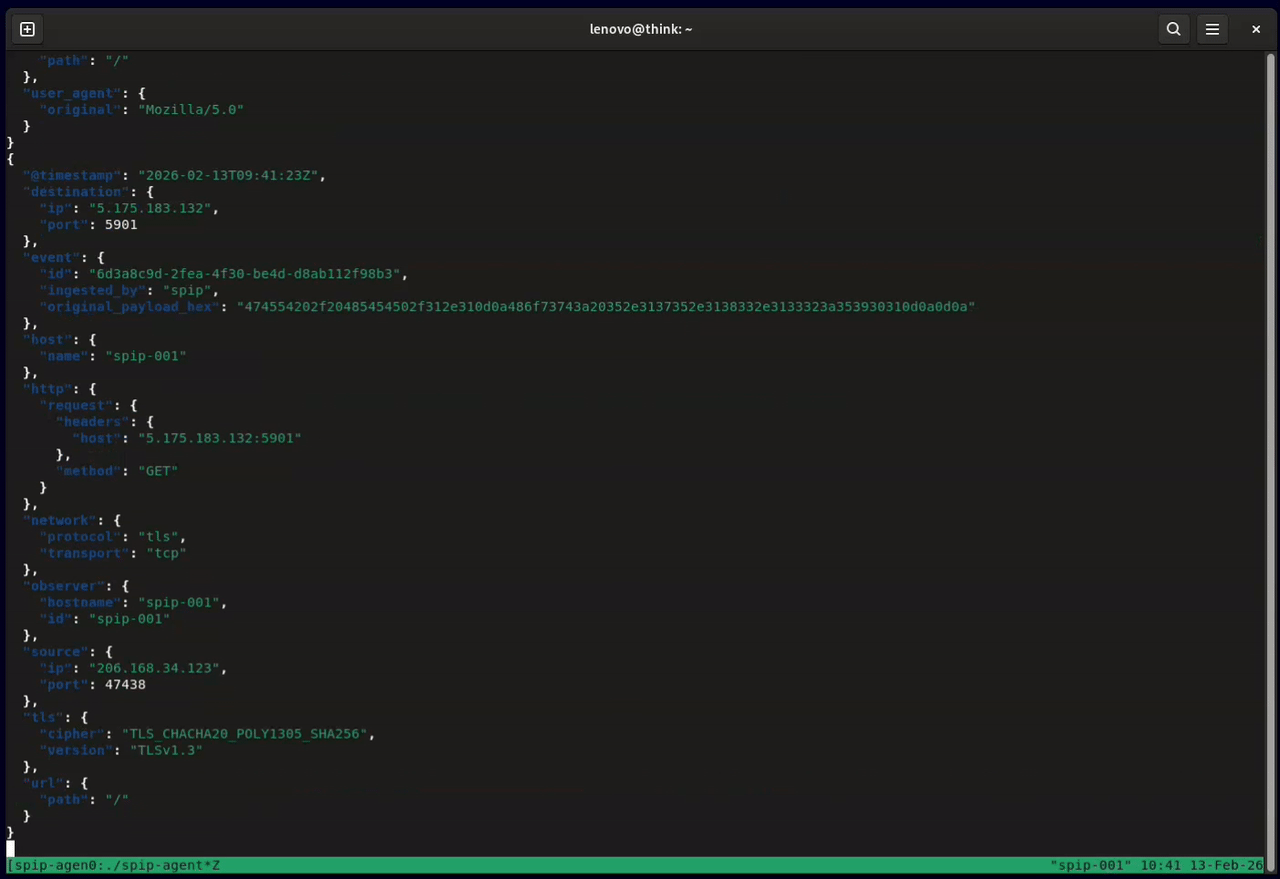 honeylabshq/spip-go
Spip network sensor written in Go
 backbay-labs/thrunt-god
Threat hunting command system for agentic IDEs
 pedramamini/threatingestor
Automated threat intelligence aggregation tool that extracts and normalizes indicators from multiple sources (OSINT feeds, malware reports) into a…
 certtools/intelmq
IntelMQ is a solution for IT security teams for collecting and processing security feeds using a message queuing protocol.
 mcastens/alycon-threat-landscape
Training-free anomaly detection framework using Shannon Entropy, Fisher Information, and Wasserstein Distance to map system states into geometrically…
 logisek/baconsampler
Sniffs outbound traffic for suspicious, beacon-like callbacks, because if it keeps coming back on schedule, it's probably not breakfast.
 strainxx/react2shell-honeypot
My attempt to make honeypot for React2Shell vulnerability (CVE-2025-66478)
 ma111e/melody
Melody is a transparent internet sensor built for threat intelligence. Supports custom tagging rules and vulnerable application simulation.
 corelight/icanntld
Zeek script using the official ICANN Top-Level Domain (TLD) list with the Input Framework to extract the relevant information from a DNS query and…
 stratosphereips/aip
Generates efficient IPv4 blocklists from Zeek network flows using multiple prioritization models (new, consistent, random forest) to identify…
 hpfeeds/hpfeeds
Honeynet Project generic authenticated datafeed protocol
 corelight/zeek-openvpn
A Zeek OpenVPN protocol analyzer plugin.
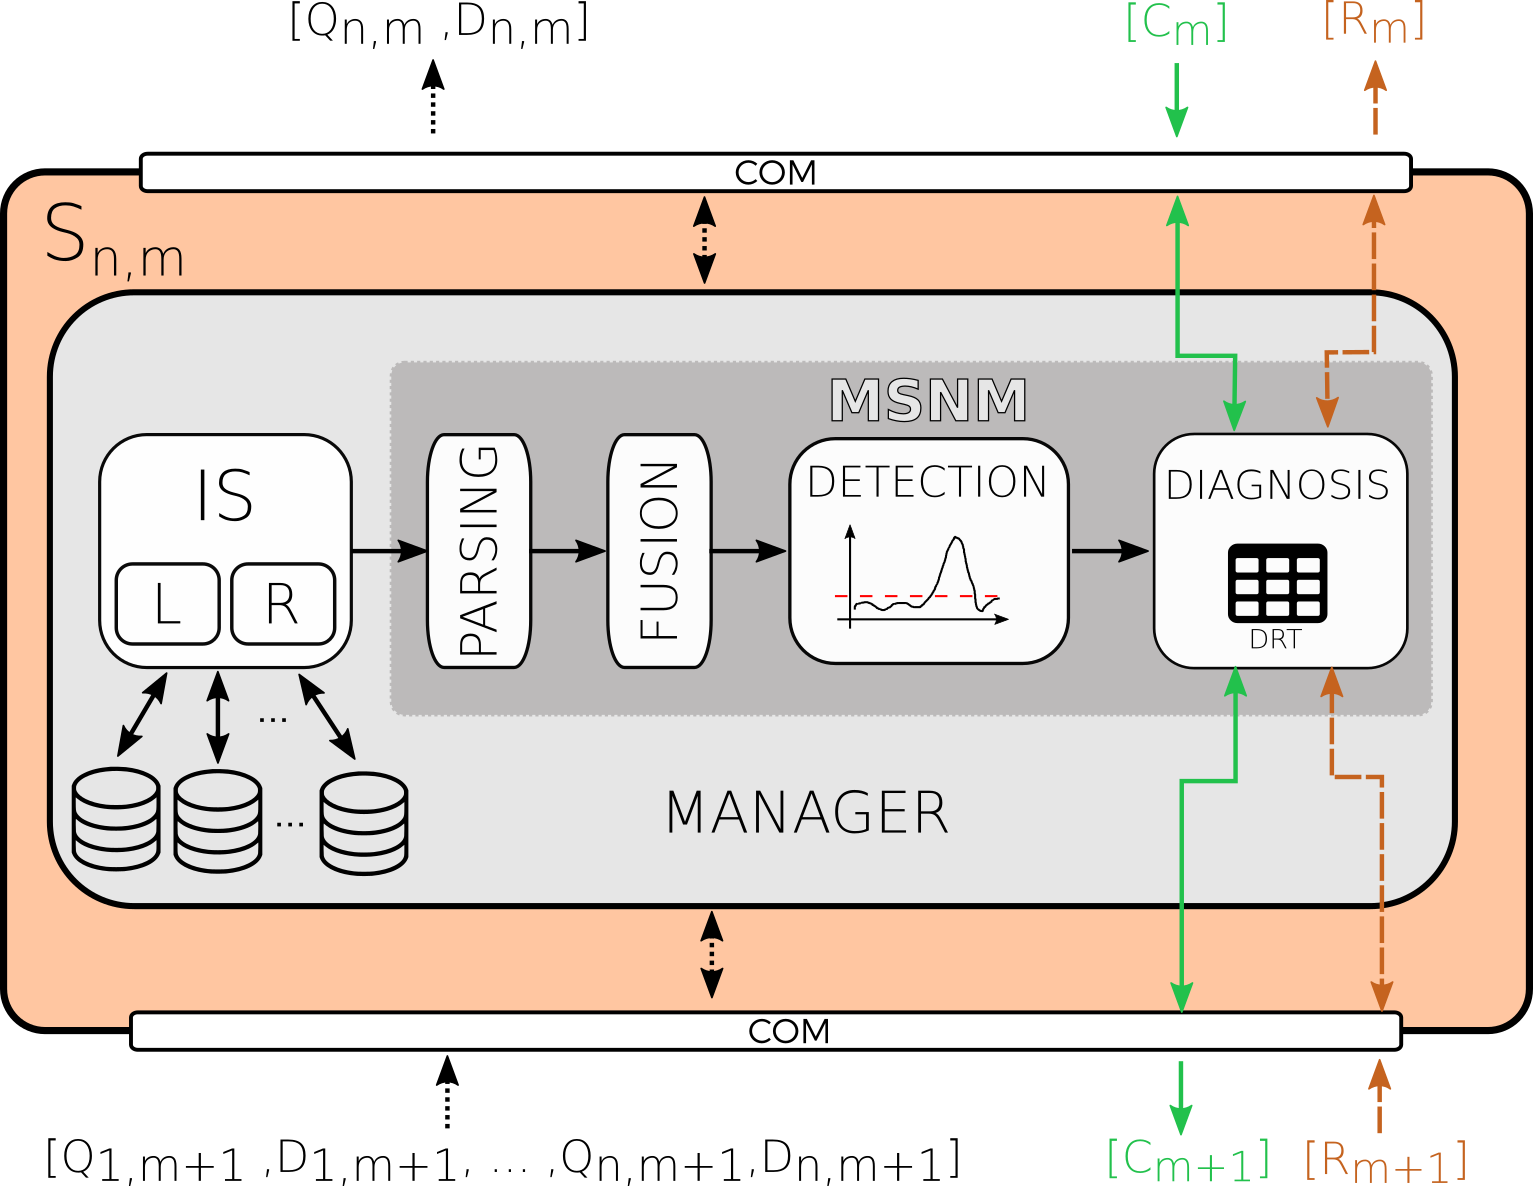 nesg-ugr/msnm-sensor
Multivariate statistical network monitoring sensor that detects anomalies using PCA-based techniques, aggregating lightweight statistics from…