

ntopng
 ntop/ntopng
Web-based Traffic and Cybersecurity Network Traffic Monitoring
anomaly-detectiondns-analysisintrusion-detection+6
ntop/ntopngWeb-based Traffic and Cybersecurity Network Traffic Monitoring
 criticalpathsecurity/zeek-intelligence-feeds
Aggregated Zeek-format threat intelligence feeds with combined indicators from public and curated sources for continuous IDS and network threat…
 jev-sec/jev-ids
Blazing-Fast Token-Efficient Intrusion Detection System (IDS) based on TypeSafe's Jev.
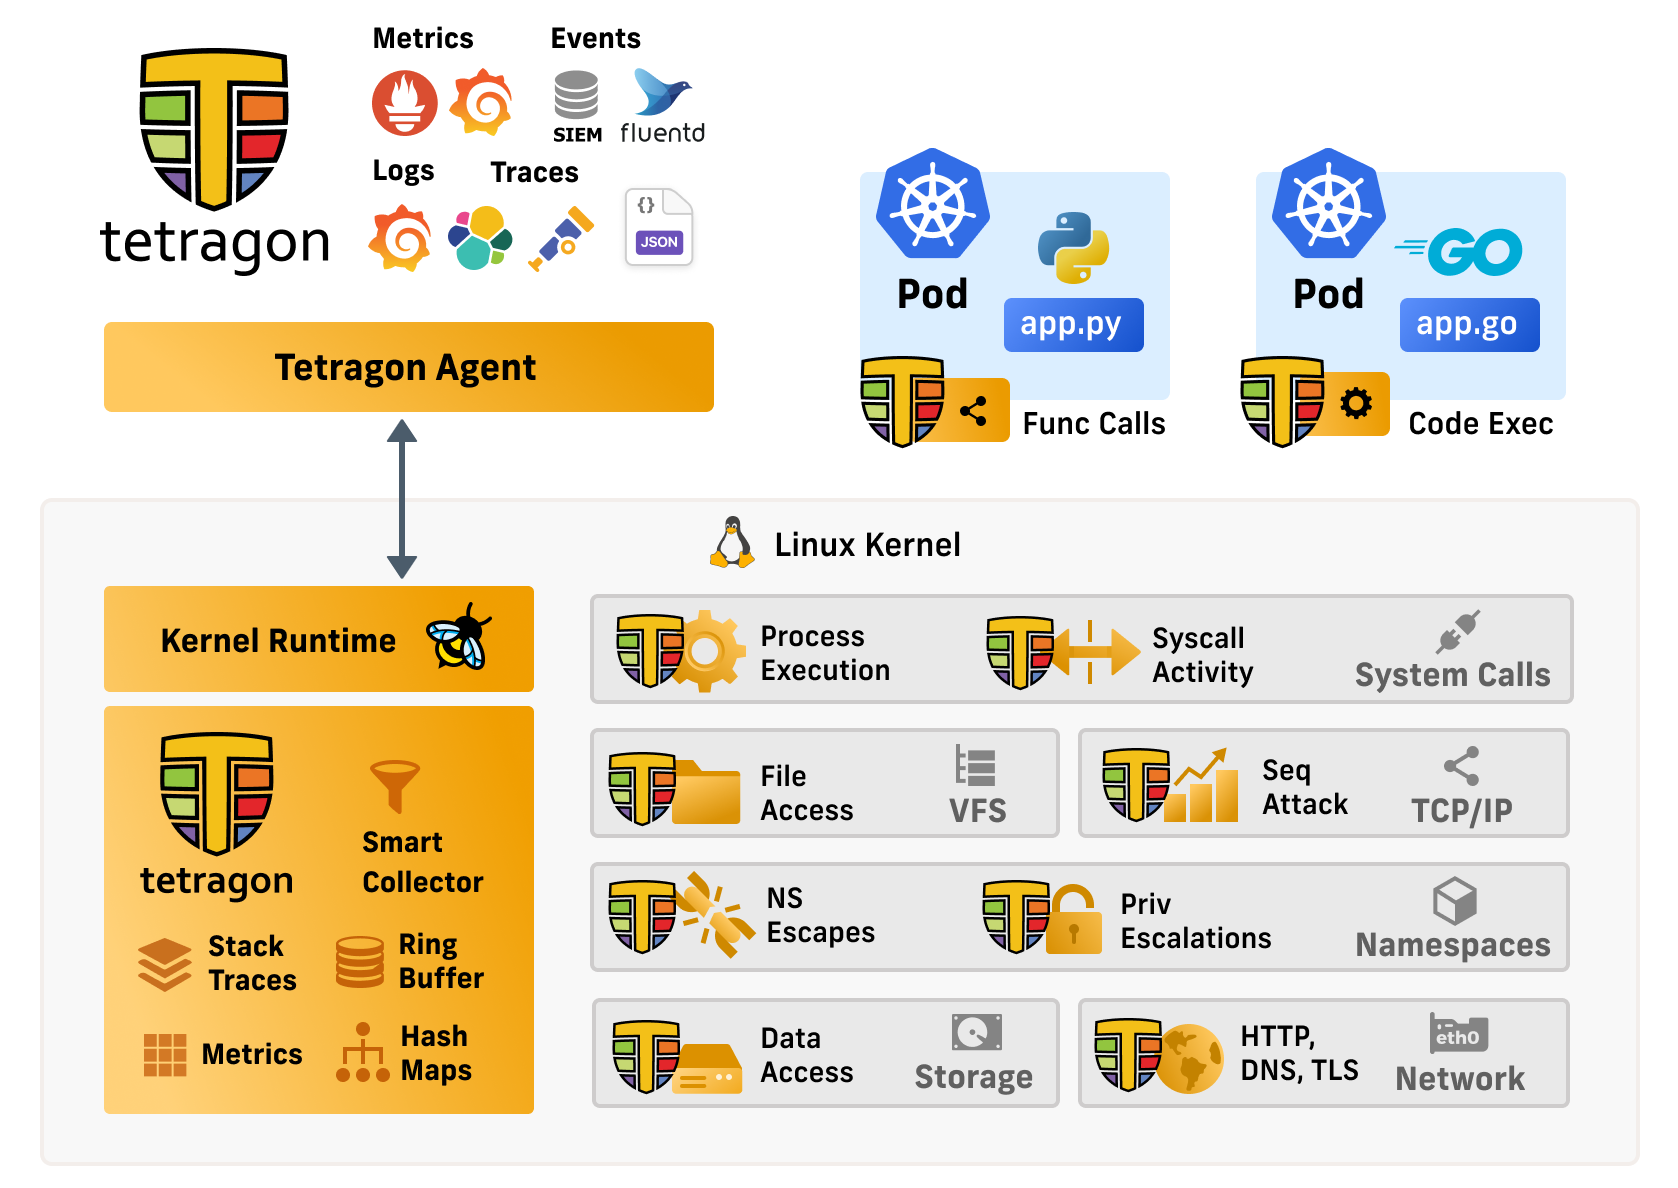 cilium/tetragon
eBPF-based Security Observability and Runtime Enforcement
 rbidou/pyrasp
Runtime Application Self Protection for Python web servers, serverless functions and MCP servers, detecting attacks, prompt injection and data leaks…
 bombinisecurity/bombini
eBPF Security Monitoring and Sandboxing Agent Based on Aya
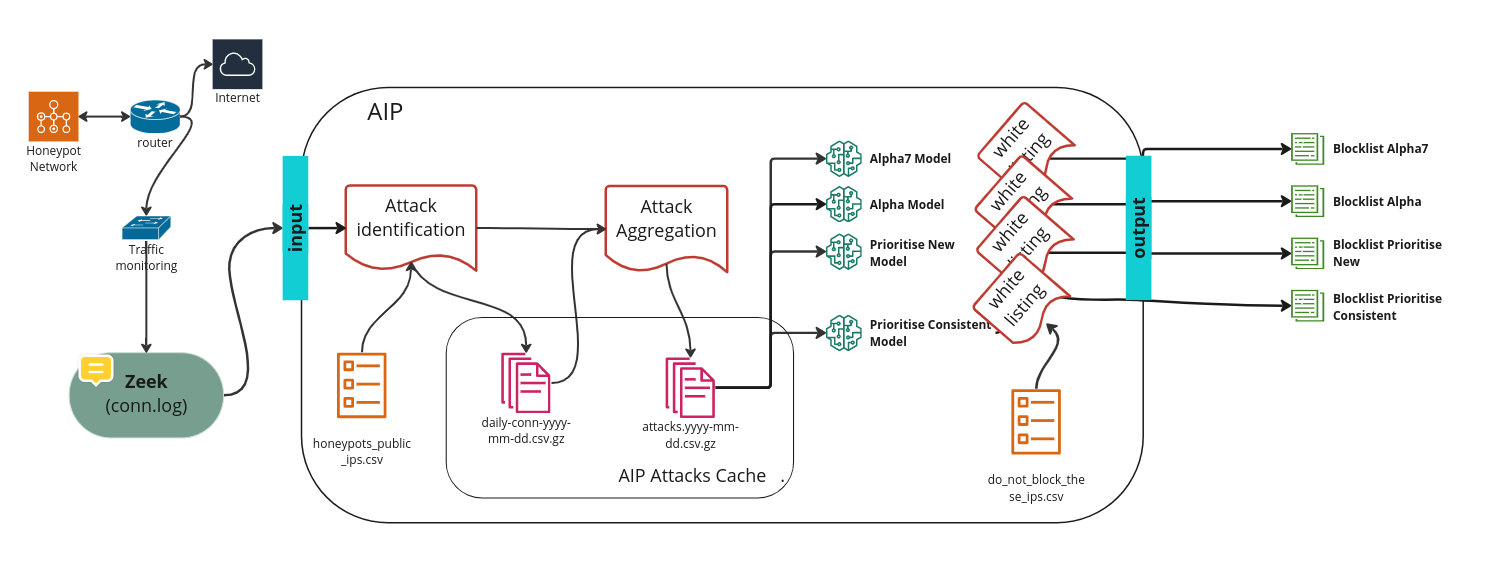 stratosphereips/aip
Generates efficient IPv4 blocklists from Zeek network flows using multiple prioritization models (new, consistent, random forest) to identify…
 sigmahq/sigma-cli
The Sigma command line interface based on pySigma
 mfthomps/labtainers
Labtainers: A Docker-based cyber lab framework
 harshiys/cve-2007-2447-exploitation-siem-detection-lab
Isolated AD/Linux attack lab: exploited CVE-2007-2447 via Metasploit, detected with Wazuh SIEM mapped to MITRE ATT&CK (T1190, T1059)
 millikanjohnl-blip/dirtyfrag-detection-rules
Detection rules and analysis for Dirty Frag (CVE-2026-43284/CVE-2026-43500) Linux kernel LPE vulnerability. Based on community research and health…
 0xkirisame/spica
eBPF-based Linux rootkit detector using multi-channel cross-view analysis (sched_switch, NMI, /proc) to detect DKOM, tracepoint tampering, and…
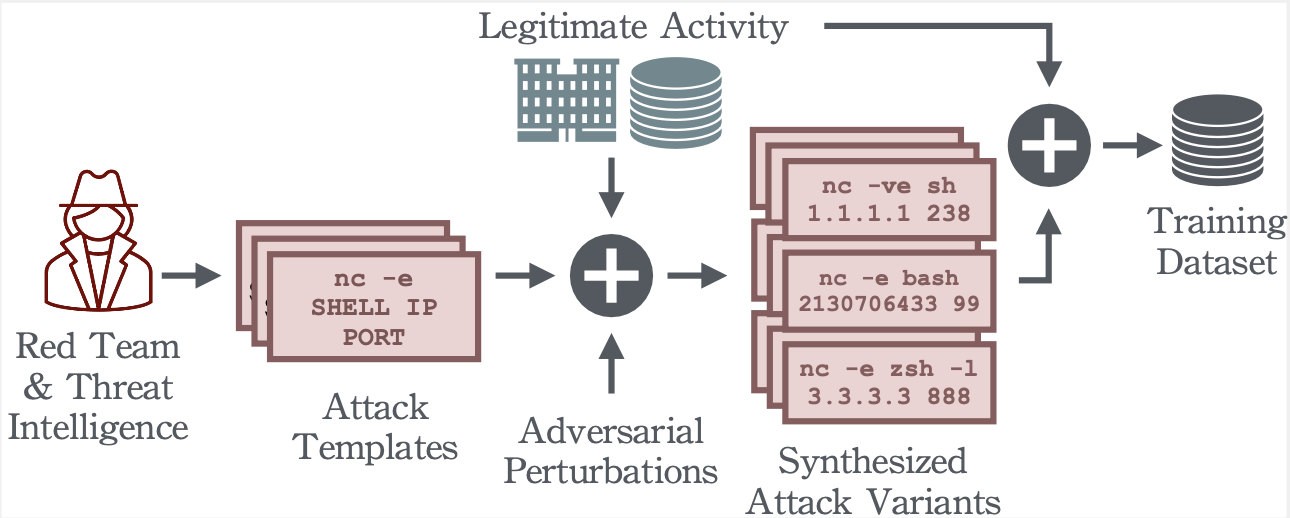 dtrizna/quasarnix
Reverse Shell Detection with Machine Learning
 kouf320/docker-lab-cve-2017-5638-cve-2021-41773
Docker-based multi-stage attack emulation lab demonstrating CVE-2017-5638 and CVE-2021-41773 exploitation, lateral movement, and Suricata IDS…
 corelight/zeek-spicy-openvpn
A Zeek OpenVPN protocol analyzer, based on Spicy.
 rohitmalik7/cve-2024-38063-detection-mitigation-system
End-to-end cybersecurity project demonstrating detection and mitigation of CVE-2024-38063 using IDS, host-based monitoring, and virtual lab attack…
 owasp/intrusion-alert-educational-network-ids
Lightweight Python-based IDS that monitors network traffic in real-time using Scapy, detecting DoS/DDoS attacks via per-IP request rate analysis with…
 17patmaks/my-sigma-rule-collection
Sigma Rule for CVE-2025-49666