
AiSOC
 beenuar/aisoc
Open-source AI-powered Security Operations Center — alert fusion, purple-team drills, agent-assisted triage, MITRE ATT&CK investigation.…
ai-securityanomaly-detectiondefensive-tools+5
2.4k12h 19m ago
beenuar/aisocOpen-source AI-powered Security Operations Center — alert fusion, purple-team drills, agent-assisted triage, MITRE ATT&CK investigation.…
 cyb3rxp/awesome-soc
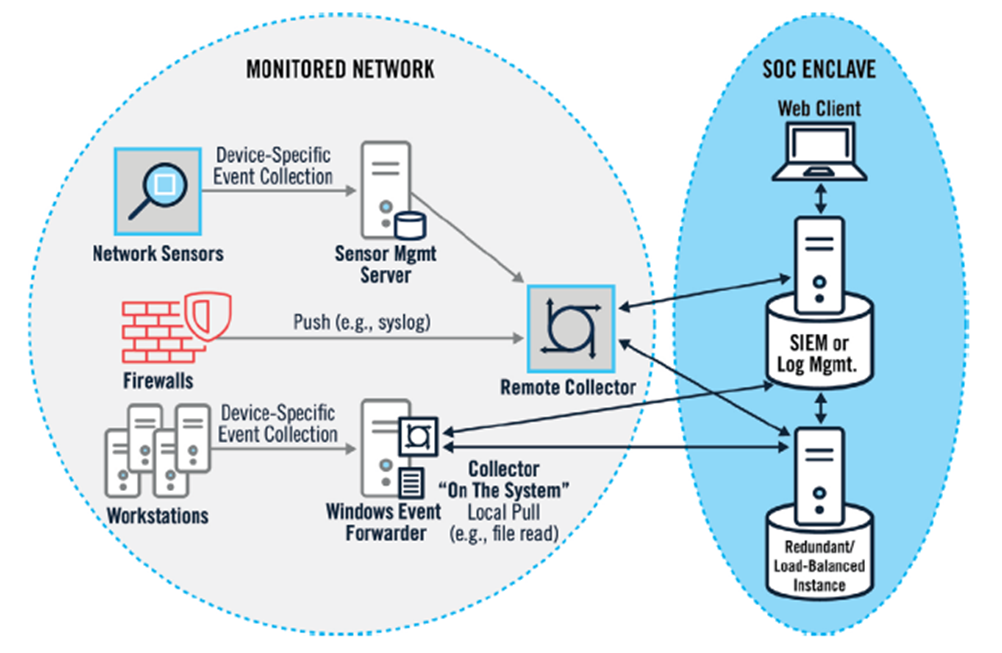
A curated knowledge base to build, run and mature a SOC (including CSIRT).
 beelzebub-labs/beelzebub
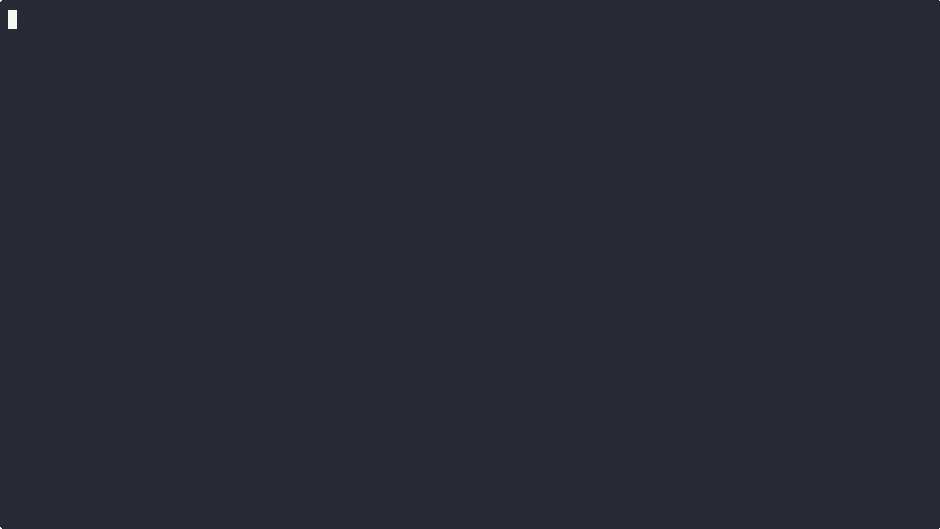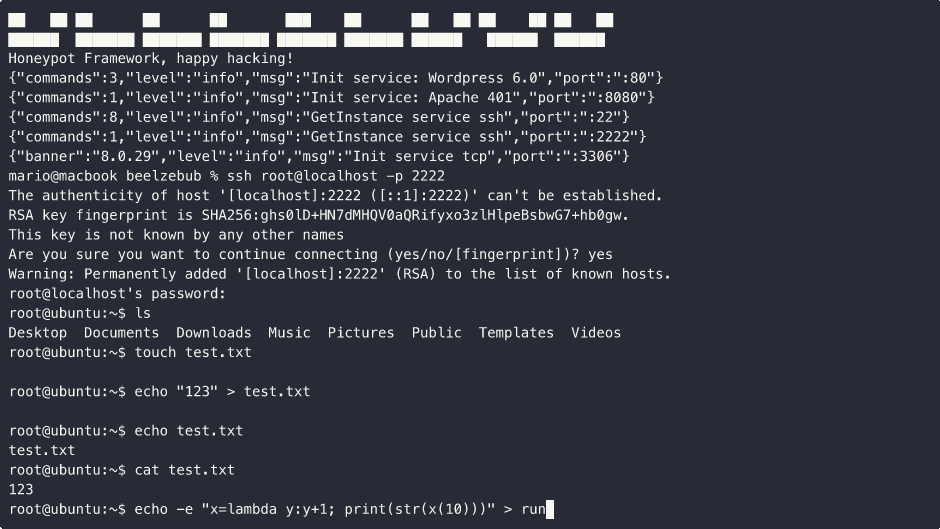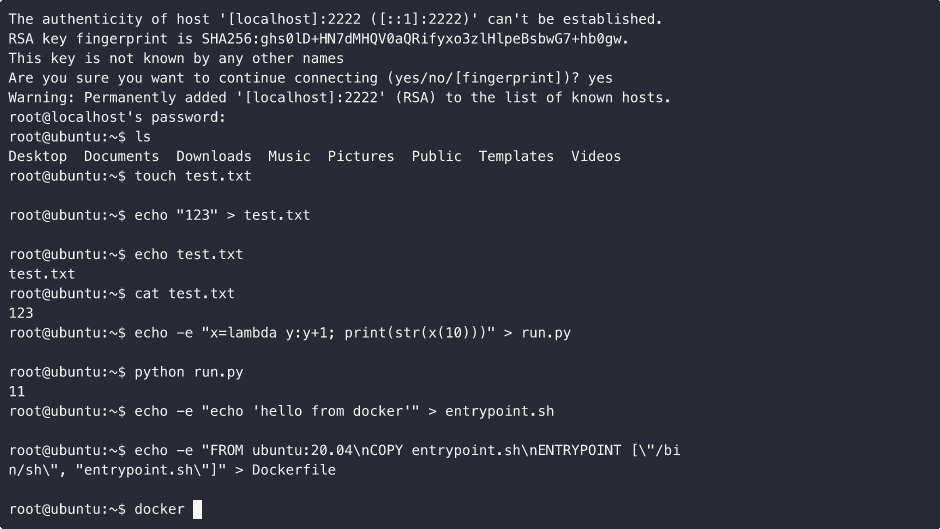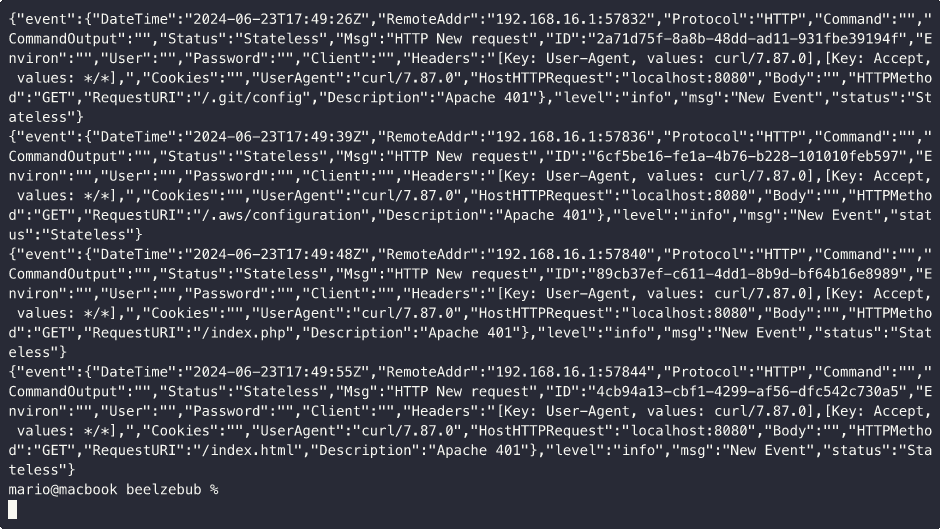
A secure low code deception runtime framework, leveraging AI for System Virtualization.
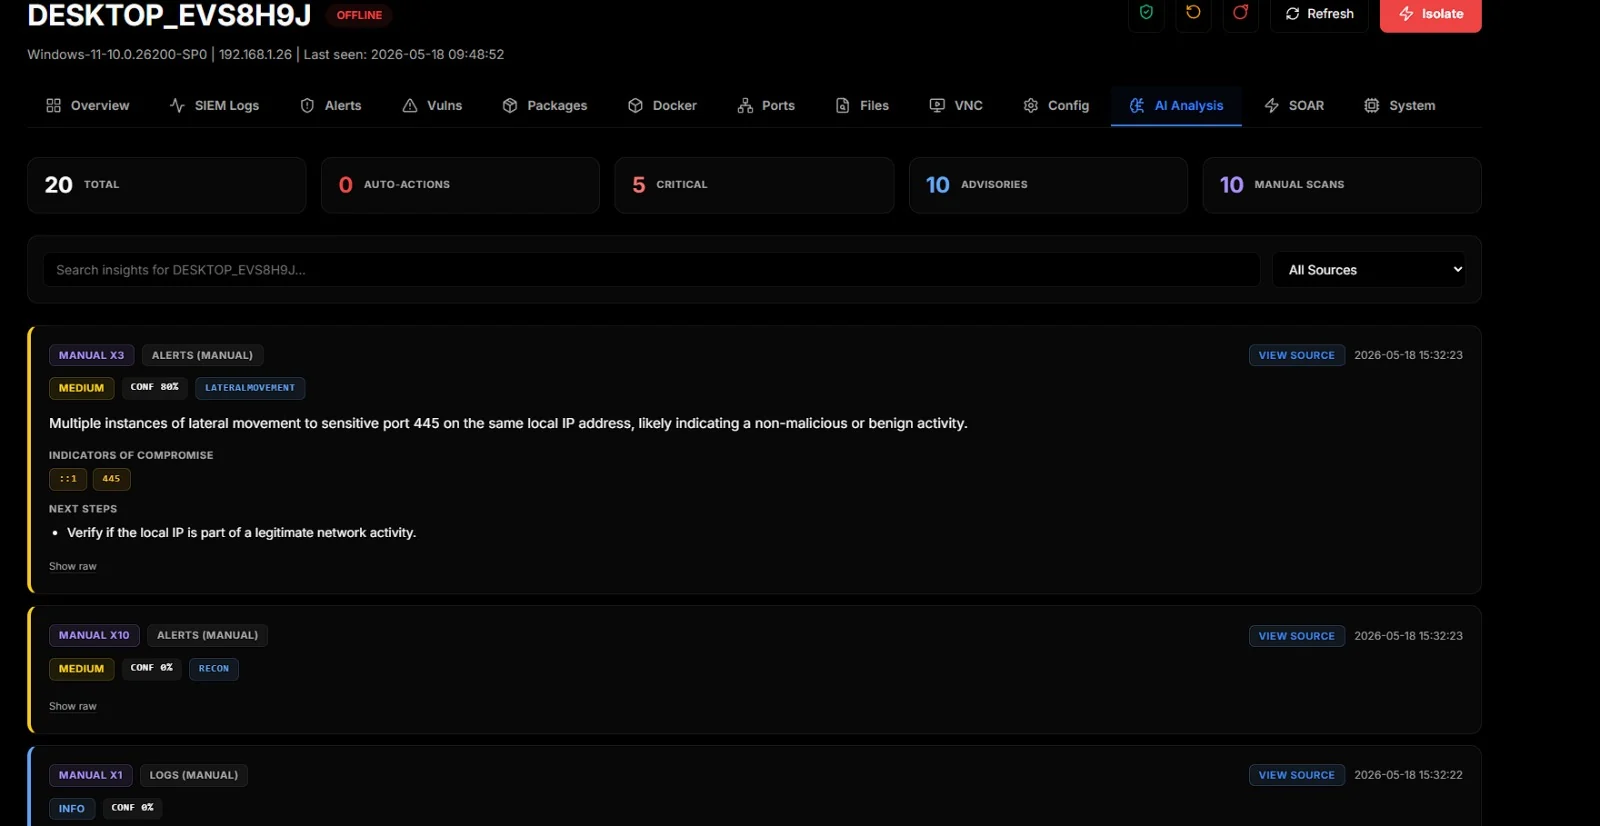 d3vhex/sentora
An open-source, self-hosted AI-powered SIEM, EDR and SOAR platform for modern security operations.
 falcosecurity/falco
Real-time cloud-native runtime security agent for Linux that monitors syscalls and container/Kubernetes metadata to detect anomalous behavior and…
 jay123anta/laravel-threat-detection
Passive Laravel middleware that detects and logs SQL injection, XSS, RCE, bot scanners, and 175+ attack patterns. Features a built-in dashboard,…
 misp/misp
MISP (core software) - Open Source Threat Intelligence and Sharing Platform
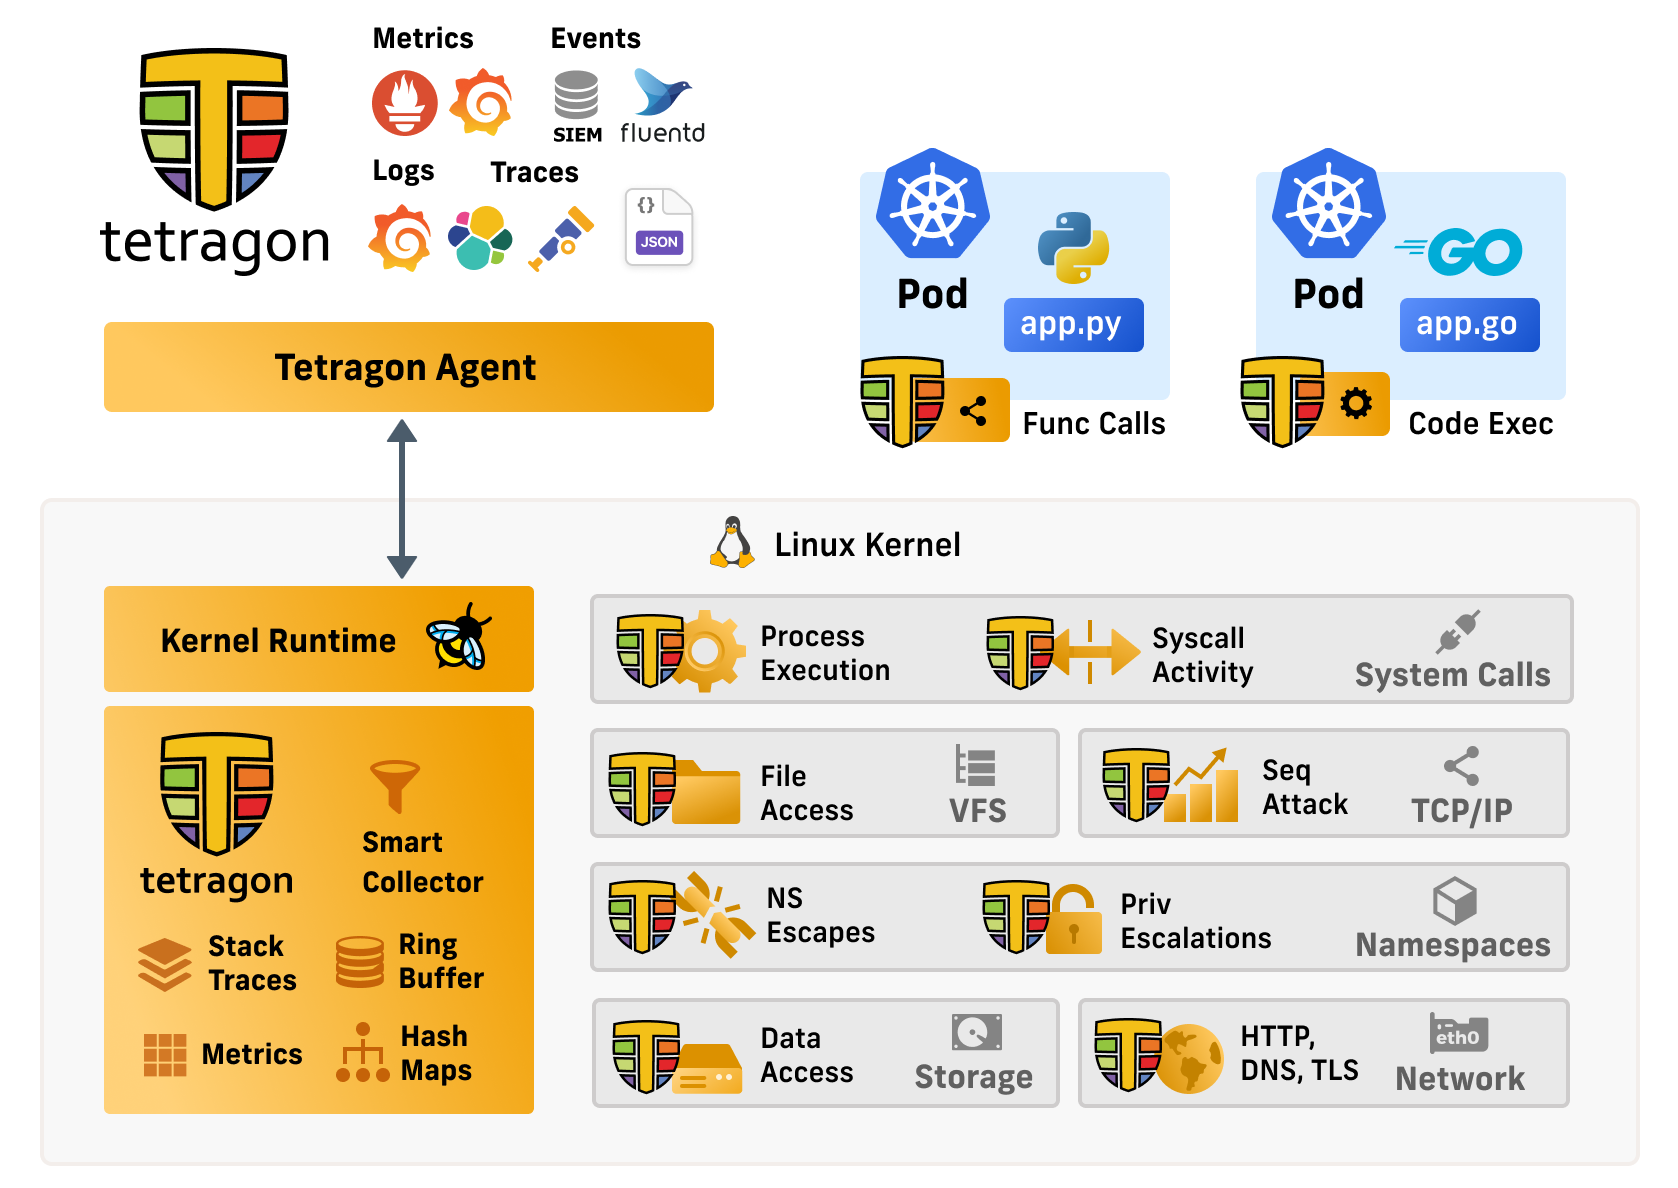 cilium/tetragon
eBPF-based Security Observability and Runtime Enforcement
 infokom-ki/zimbra-cve-2026-73570-rules
Wazuh detection rules for CVE-2026-73570, an OS command injection in Zimbra Collaboration Suite, monitoring web access logs and zimbra.log for…
 mattijsmoens/intentshield
Pre-execution intent verification for AI agents. Audits what your AI is about to do, not what it says. Zero dependencies, deterministic, hash-sealed.
 hackspeak/cve-2026-23479
Redis UAF RCE PoC collection for CVE-2026-23479: safe version checker, exploit module, GDB-assisted PoC, and Sigma detection rules for authorized…
 bytespulse-oe/wp2shell-hestia-scanner
Read-only WordPress security scanner for HestiaCP servers. Detects wp2shell compromise indicators (CVE-2026-63030 / CVE-2026-60137) across all hosted…
 agentshield-ai/sigma-ai
Sigma detection rules for AI agent security monitoring
 j-dahl7/mcp-attack-detection-sentinel
Sentinel detection lab for MCP attack chains: CVE-2026-26118 SSRF token theft, tool poisoning, cross-server exfiltration, identity post-exploitation.…
 facebook/mcpguard-dynamic
Kernel-level eBPF sandbox for securing LLM agent tool calls made through the Model Context Protocol (MCP)
 securityclaw/securityclaw
A modular, skill-based autonomous Security Operations Center (SOC) agent that monitors OpenSearch/Elasticsearch data, builds RAG-based behavioral…
 eyesecurity/wp2shell-compromise-scanner-plugin
Read-only WordPress plugin that scans for artifacts of the wp2shell exploit chain (CVE-2026-63030 / CVE-2026-60137)
 fusion1110/ebpf-hid_guard
Linux kernel-space HID injection attack detector using eBPF. Monitors USB and Bluetooth HID devices for anomalous keystroke timing and automatically…