
vulnerability-poc
 fankh/vulnerability-poc
CVE proof-of-concept labs, exploit scripts, and detection/prevention rules (Nginx, Apache, Snort, YARA) for high-severity CVEs. Authorized security…
ctfeducationexploitation+5
119
fankh/vulnerability-pocCVE proof-of-concept labs, exploit scripts, and detection/prevention rules (Nginx, Apache, Snort, YARA) for high-severity CVEs. Authorized security…
 stamparm/maltrail
Real-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…
 stackrox/stackrox
The StackRox Kubernetes Security Platform performs a risk analysis of the container environment, delivers visibility and runtime alerts, and provides…
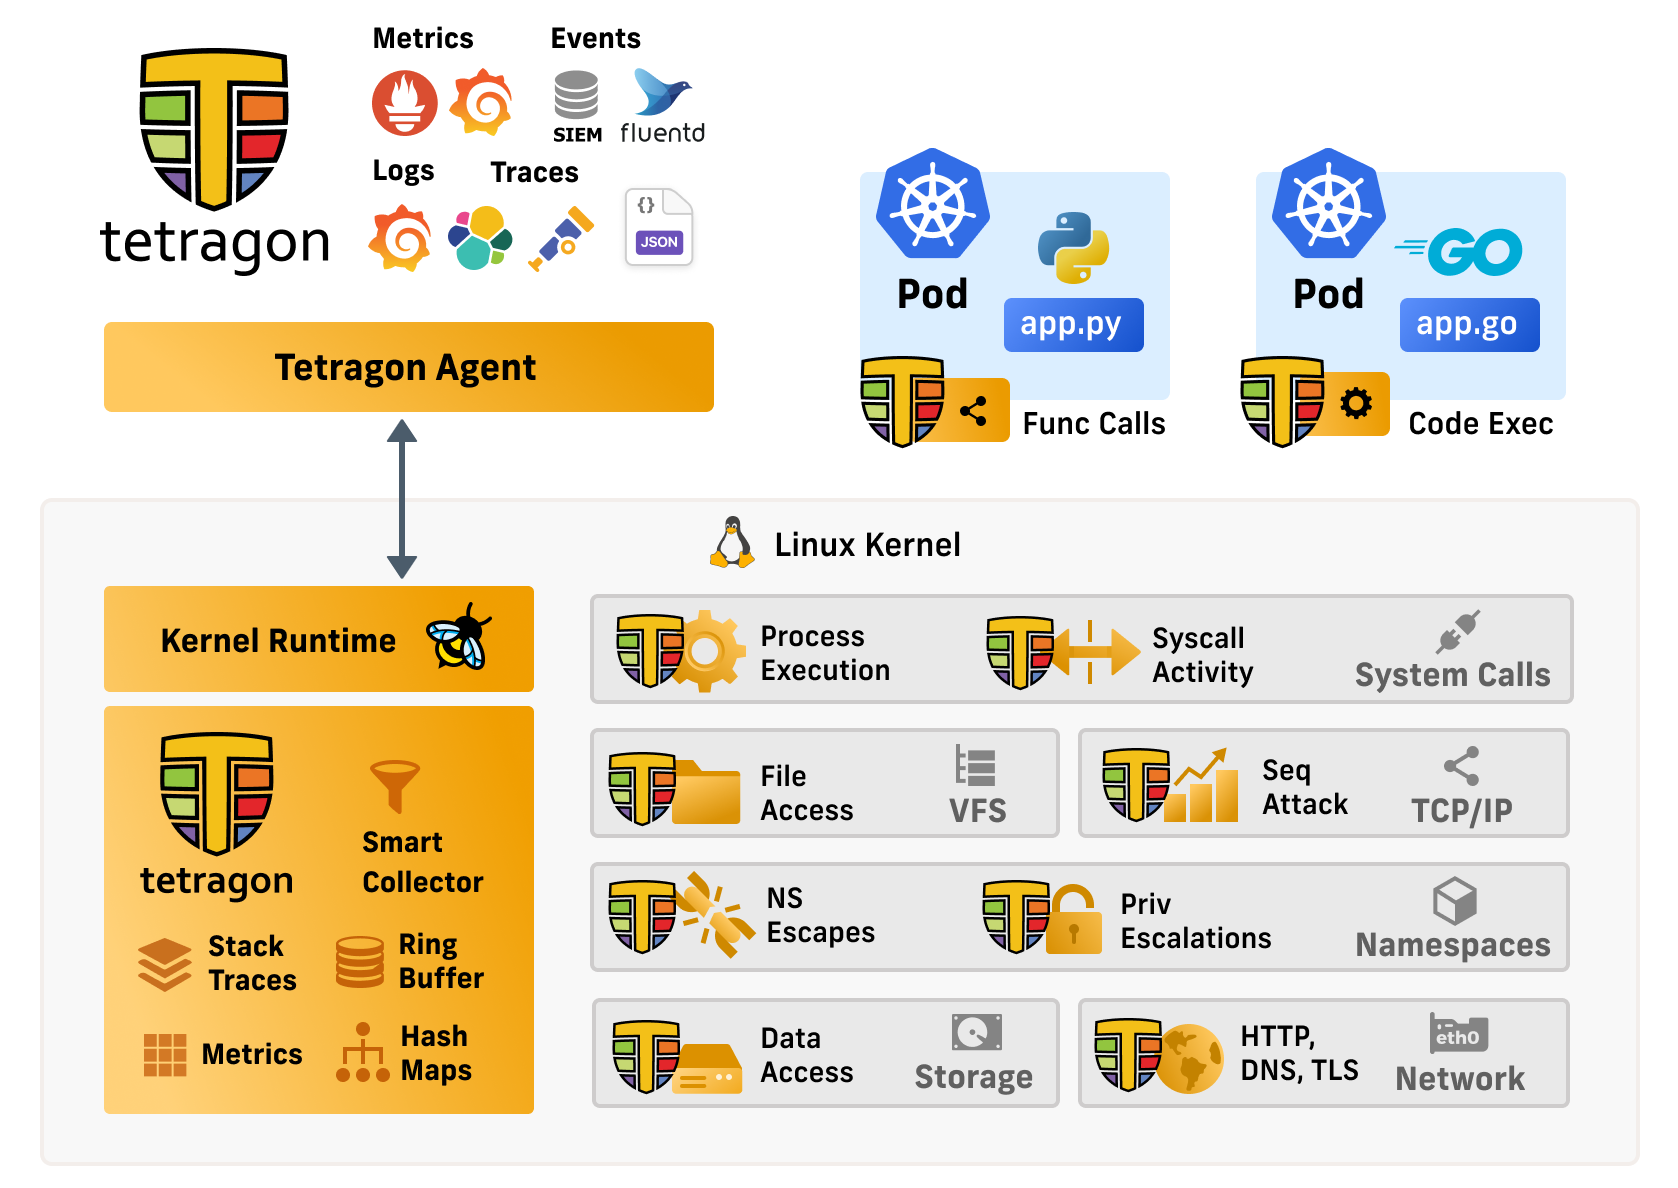 cilium/tetragon
eBPF-based Security Observability and Runtime Enforcement
 azure/azure-sentinel
Cloud-native SIEM for intelligent security analytics for your entire enterprise.
 ntop/ntopng
Web-based Traffic and Cybersecurity Network Traffic Monitoring
 crowdsecurity/crowdsec
Open-source IDS/IPS and WAF engine that analyzes logs and HTTP requests to detect and block malicious IPs, leveraging a crowdsourced community…
 beenuar/aisoc
Self-hostable AI SOC that fuses security alerts, auto-triages via agentic AI, runs MITRE ATT&CK investigations, and logs every agent decision in a…
 criticalpathsecurity/zeek-intelligence-feeds
Aggregated Zeek-format threat intelligence feeds with combined indicators from public and curated sources for continuous IDS and network threat…
 julioliraup/antiphishing
Advanced Phishing Protection: Suricata rulesets open and free
 kismetwireless/kismet
Github mirror of official Kismet repository
 osquery/osquery
SQL powered operating system instrumentation, monitoring, and analytics.
 bert-janp/open-source-threat-intel-feeds
This repository contains Open Source freely usable Threat Intel feeds that can be used without additional requirements. Contains multiple types such…
 zeek/zeek
Zeek is a powerful network analysis framework that is much different from the typical IDS you may know.
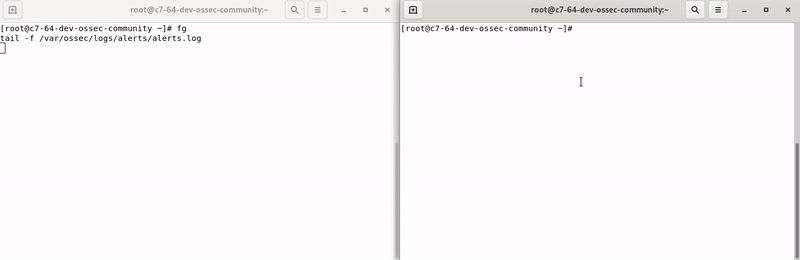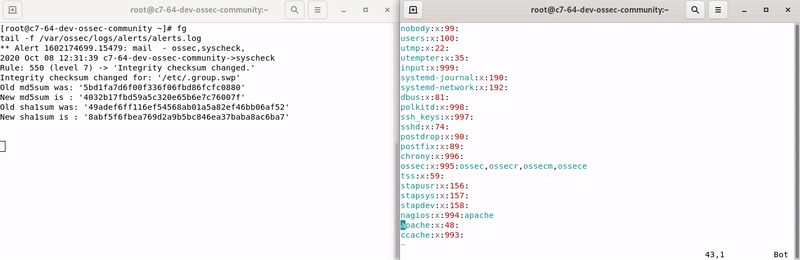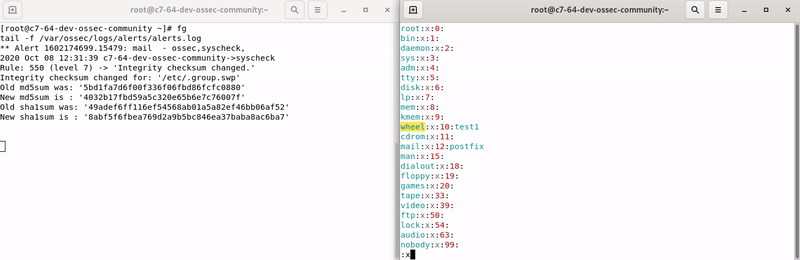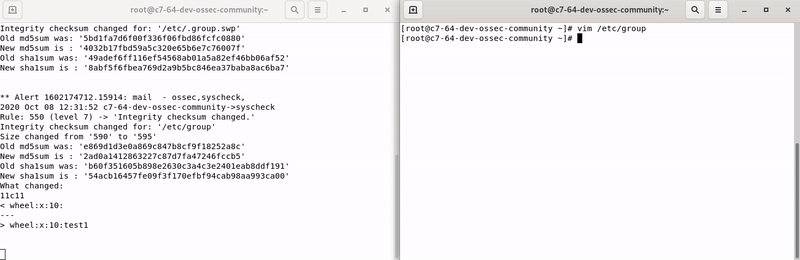 ossec/ossec-hids
OSSEC is an Open Source Host-based Intrusion Detection System that performs log analysis, file integrity checking, policy monitoring, rootkit…

 nzymeorg/nzyme
WiFi, Bluetooth and Ethernet Threat Detection.
 sigmahq/sigma-cli
The Sigma command line interface based on pySigma