
ossec-hids
 ossec/ossec-hids
OSSEC is an Open Source Host-based Intrusion Detection System that performs log analysis, file integrity checking, policy monitoring, rootkit…
defensive-toolsintrusion-detectionlog-analysis
ossec/ossec-hidsOSSEC is an Open Source Host-based Intrusion Detection System that performs log analysis, file integrity checking, policy monitoring, rootkit…
 zeek/zeek
Zeek is a powerful network analysis framework that is much different from the typical IDS you may know.
 sigmahq/pysigma-backend-opensearch
pySigma OpenSearch backend
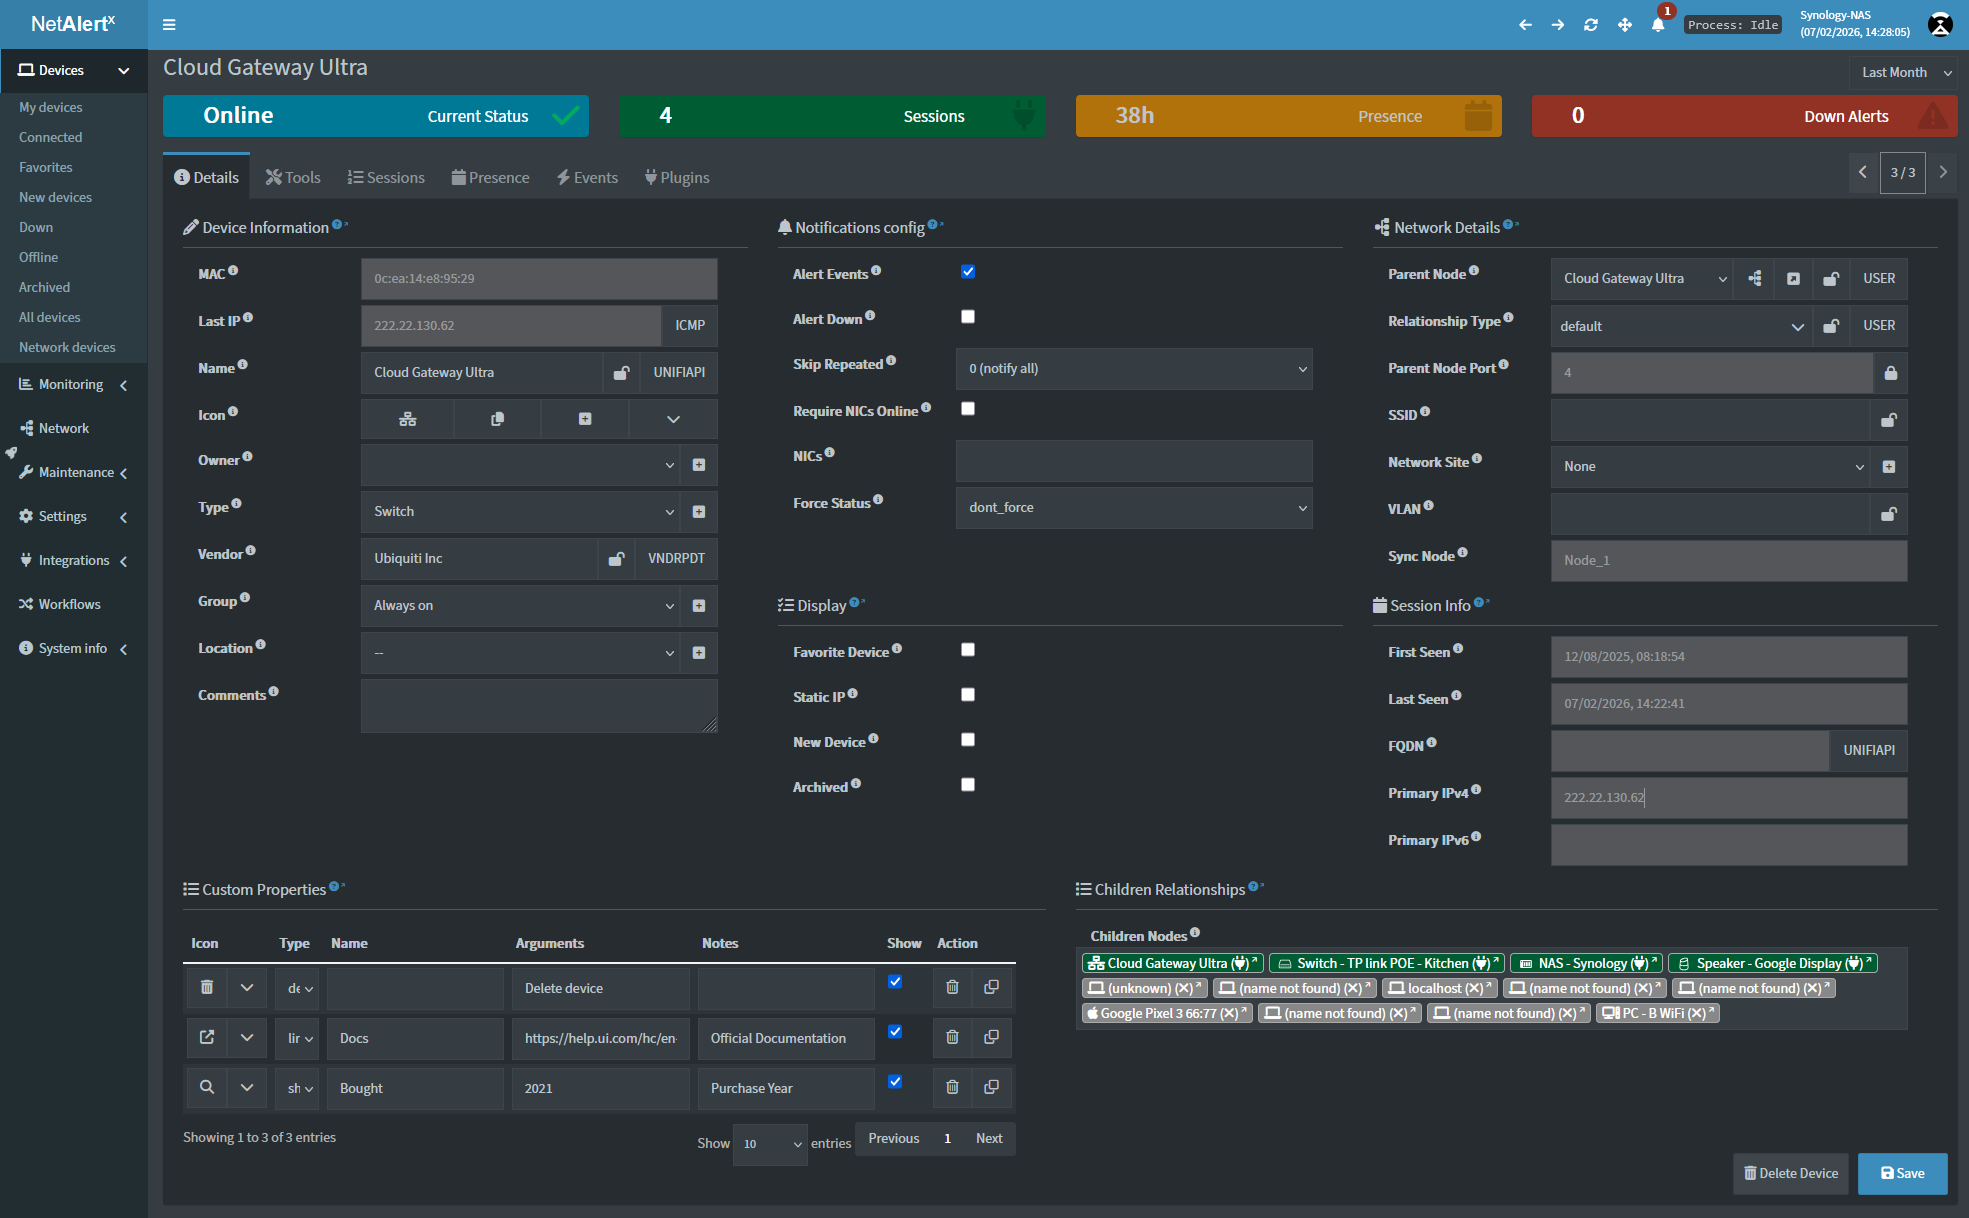 netalertx/netalertx
Centralized network visibility and continuous asset discovery. Monitor devices, detect change, and stay aware across distributed networks.
 gopasteverything/gpewebdefender
Lightweight web-attack monitor. One Go binary + SQLite. Not OSSEC, not a WAF.
 johnearle/coalmine
Cloud Canary Object Orchestration Management Platform
 fusion1110/ebpf-hid_guard
Linux kernel-space HID injection attack detector using eBPF. Monitors USB and Bluetooth HID devices for anomalous keystroke timing and automatically…
 mr-r3b00t/cve-2026-0300
Deceptive honeypot designed to simulate and monitor exploitation attempts targeting CVE-2026-0300, capturing attacker behavior for analysis and…
 owasp/intrusion-alert-educational-network-ids
Lightweight Python-based IDS that monitors network traffic in real-time using Scapy, detecting DoS/DDoS attacks via per-IP request rate analysis with…
 sleuthco/clawshield-public
Security proxy for AI agents. Scans every message for prompt injection, PII, and secrets. Defense-in-depth: Go proxy + iptables firewall + eBPF…
 matheuzsecurity/ksentinel
Linux kernel integrity monitor for detecting syscall hooking
 baidu/openrasp
Runtime application self-protection engine that hooks into application servers to monitor and block malicious database queries, file operations, and…
 ma111e/melody
Melody is a transparent internet sensor built for threat intelligence. Supports custom tagging rules and vulnerable application simulation.
 hardenedvault/ved-ebpf
eBPF-based runtime kernel security monitor detecting exploits and rootkits via control flow integrity (wCFI) and privilege escalation detection (PSD)…
 gmh5225/crowarmor
Linux kernel security driver using LSM to harden the system, monitor and restore syscall table integrity, and protect CPU control registers against…
 alperenugurlu/network_assessment
With Wireshark or TCPdump, you can determine whether there is harmful activity on your network traffic that you have recorded on the network you…
 theflink/hunt-weird-syscalls
ETW based POC to identify direct and indirect syscalls