Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
30 results
Zeek-Intelligence-Feeds preview

Zeek-Intelligence-Feeds

GitHubcriticalpathsecurity/zeek-intelligence-feeds

Aggregated Zeek-format threat intelligence feeds with combined indicators from public and curated sources for continuous IDS and network threat…

command-and-controlintrusion-detectionnetwork-security+3

406
10h 37m ago
Open-Source-Threat-Intel-Feeds preview

Open-Source-Threat-Intel-Feeds

GitHubbert-janp/open-source-threat-intel-feeds

This repository contains Open Source freely usable Threat Intel feeds that can be used without additional requirements. Contains multiple types such…

intrusion-detectionioc-managementnetwork-security+3
96819h 14m ago
OshoosiClaw preview

OshoosiClaw

GitHuboyesanyf/oshoosiclaw

Autonomous Rust endpoint security agent combining Ring-0 Windows driver and Linux eBPF pre-execution blocking, YARA detection, MITRE ATT&CK mapping,…

ai-securityanomaly-detectioncommand-and-control+8
621h 9m ago
Threat-Hunting preview

Threat-Hunting

GitHuba2awais/threat-hunting

Curated collection of threat hunting and detection queries for CrowdStrike Falcon (CQL) and Microsoft Defender XDR (KQL), mapped to MITRE ATT&CK…

educationincident-responseinformation-gathering+4
863 days ago
c2detect preview

c2detect

GitHubcognis-digital/c2detect

C2 server fingerprinter — Cobalt Strike, Sliver, Mythic, Havoc, Brute Ratel

command-and-controldefensive-toolsfingerprint-spoofing+8
431 month ago
beacon-hunter preview

beacon-hunter

GitHubmrcord77/beacon-hunter

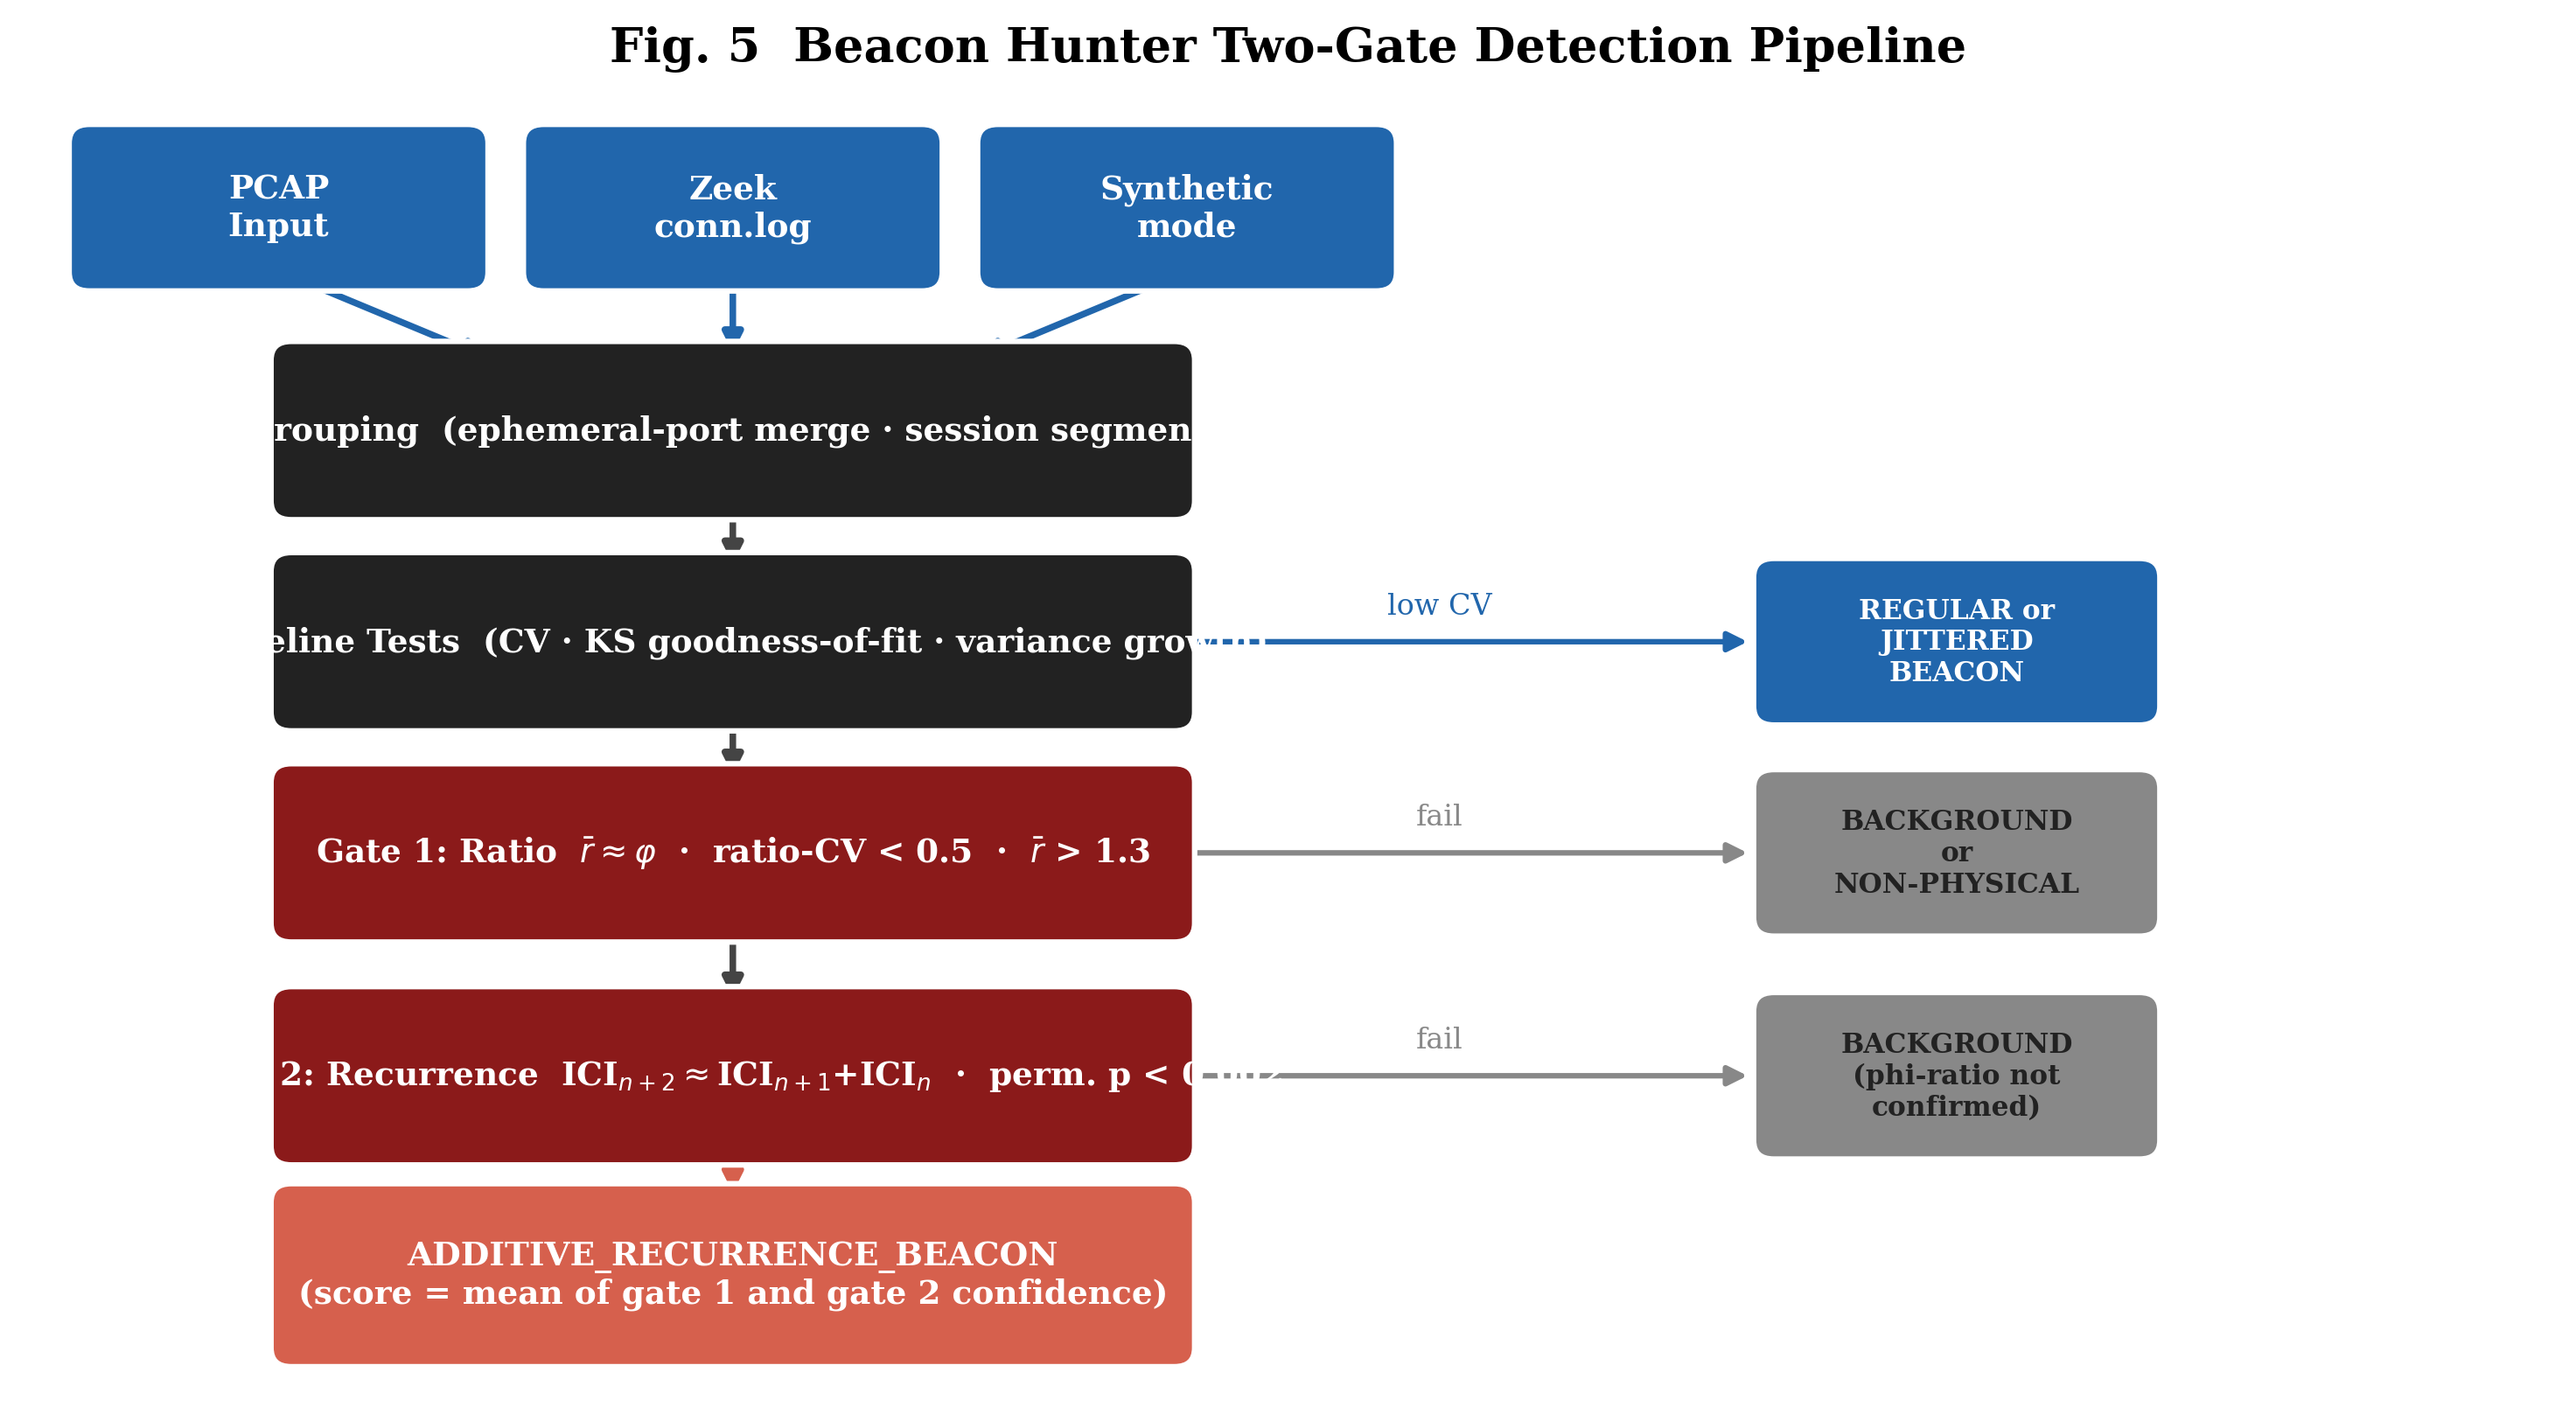
Detects phi-structured C2 beacons that evade RITA and standard regularity-based detectors

anomaly-detectioncommand-and-controleducation+5
92 months ago
NexaCorp-DFIR-INC-2026-001 preview

NexaCorp-DFIR-INC-2026-001

GitHubjhatchi/nexacorp-dfir-inc-2026-001

DFIR investigation + 7 Suricata rules on a simulated NexaCorp intrusion (vsftpd 2.3.4 CVE-2011-2523 + MITRE Caldera C2). 4-day solo engagement…

digital-forensicseducationincident-response+6
4 months ago
CVE-2026-24207 preview

CVE-2026-24207

GitHuboffseckit/cve-2026-24207

CVE-2026-24207 — NVIDIA Triton SageMaker auth bypass to unauth RCE. Detection script, bypass demo, RCE-chain PoC, and IDS rules.

authenticationcloud-securitycommand-and-control+8
14 months ago
cpanel-cve-41940-detector preview

cpanel-cve-41940-detector

GitHublimo57640-crypto/cpanel-cve-41940-detector

Read-only cPanel CVE-2026-41940 IOC detector for .sorry ransomware, Mr_Rot13 Filemanager backdoors, C2 callbacks, cron, SSH, and logs.

digital-forensicsforensicsincident-response+6
4 months ago
rita preview

rita

GitHubactivecm/rita

Real Intelligence Threat Analytics (RITA) is a framework for detecting command and control communication through network traffic analysis.

anomaly-detectioncommand-and-controldns-analysis+4
6674 months ago
CVE-2022-30190-Follina-Lab preview

CVE-2022-30190-Follina-Lab

GitHubu1tr0nex/cve-2022-30190-follina-lab

Full exploit chain lab and Suricata IDS detection for CVE-2022-30190 (Follina) - MSDT RCE

command-and-controleducationexploitation+7
5 months ago
cpanel-cve-2026-41940-fix preview

cpanel-cve-2026-41940-fix

GitHubshahidmallaofficial/cpanel-cve-2026-41940-fix

One-shot detection and remediation for cPanel/WHM servers compromised via CVE-2026-41940, including IOC checks, malware cleanup, C2 blocking, and…

cloud-infrastructure-securityconfiguration-auditingdigital-forensics+5
46 months ago
BerrySentinel preview

BerrySentinel

GitHubdereeqw/berrysentinel

Berry Sentinel v5.0 — Advanced behavioral C2 and reverse shell detector for Linux/Windows/Unix systems. Features real-time connection analysis,…

anomaly-detectioncommand-and-controldefensive-tools+8
138 months ago
Loki preview

Loki

GitHubneo23x0/loki

IOC and YARA-based scanner for detecting indicators of compromise via file name regex, YARA signatures, hash matching, and C2 back-connect checks on…

anomaly-detectiondigital-forensicsdisk-forensics+11
3.8k9 months ago
zeek-agenttesla-detector preview

zeek-agenttesla-detector

GitHubcorelight/zeek-agenttesla-detector

A Zeek based Agent Tesla malware C2 detector.

intrusion-detectionmalware-analysisnetwork-security+1
211 months ago
zeek-quasarrat-detector preview

zeek-quasarrat-detector

GitHubcorelight/zeek-quasarrat-detector

Zeek detector for QuasarRat

anomaly-detectionintrusion-detectionmalware-analysis+2
31 year ago
pingback preview

pingback

GitHubcorelight/pingback

A Zeek package to detect the Pingback malware ICMP tunnel command and control (C2) network traffic.

command-and-controlintrusion-detectionmalware-analysis+2
121 year ago
zeek-netsupport-detector preview

zeek-netsupport-detector

GitHubcorelight/zeek-netsupport-detector

A Zeek based NetSupport detector. NetSupport is often abused by attackers in malware.

command-and-controldefensive-toolsintrusion-detection+3
31 year ago
Previous12Next