Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
104 results
dns_watchdog_windows2 preview

dns_watchdog_windows2

GitHubmicrolaser/dns_watchdog_windows2

PowerShell script that monitors Windows DNS traffic via pktmon to detect poisoning, spoofing, rogue resolver responses, and gateway MAC changes,…

anomaly-detectiondefensive-toolsdns-analysis+5
15 days ago
hardstop preview

hardstop

GitHubjoseluispino/hardstop

Reference implementation for "Hard Stop: Kernel-Level Preemption and Containment for Rogue Agentic Execution". Out-of-band Epistemic Andon Cord,…

ai-securityanomaly-detectioncloud-security+7
55 days ago
ddos-reduction-system preview

ddos-reduction-system

GitHubdevinblack001/ddos-reduction-system

Adaptive two-stage Layer 4 DDoS mitigation gateway using behavioral traffic analysis, Random Forest classification, and kernel-level ipset/iptables…
anomaly-detectiondefensive-toolsincident-response+6
26 days ago
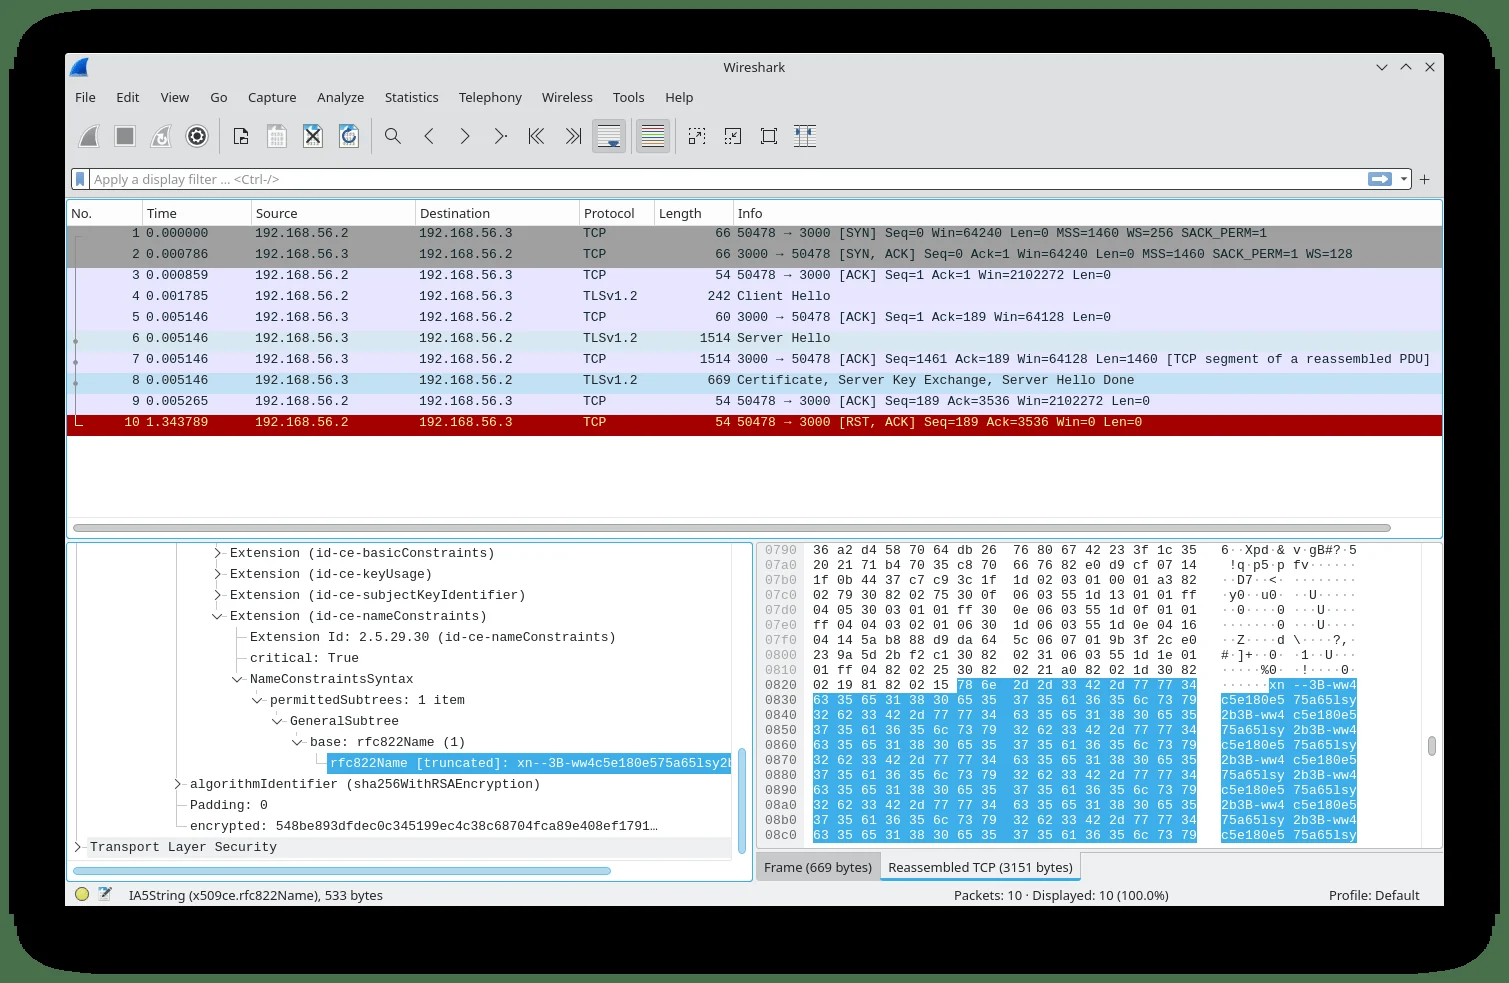
spookyssl-pcaps preview

spookyssl-pcaps

GitHubfox-it/spookyssl-pcaps

PCAPs and Suricata signatures for detecting OpenSSL CVE-2022-3602 exploitation attempts, including malicious client/server traffic and legitimate…
intrusion-detectionnetwork-securitypacket-sniffing-analysis+2
103 years ago
lazarus-sigma-rules preview

lazarus-sigma-rules

GitHubwithsecurelabs/lazarus-sigma-rules

Sigma rules for detecting Lazarus Group TTPs, covering malicious document execution, PowerShell abuse, scheduled tasks, and credential access,…
defensive-toolsincident-responseintrusion-detection+2
205 years ago
CVE-2026-34159-Vulnerability-Research-Analysis-Detection preview

CVE-2026-34159-Vulnerability-Research-Analysis-Detection

GitHubrohithronanki/cve-2026-34159-vulnerability-research-analysis-detection

Critical buffer validation bypass in deserialize_tensor() (llama.cpp < b8492). Null tensor buffer skips bounds check, enabling unauthenticated…
binary-analysisexploitationintrusion-detection+2
5 months ago
CVE-2021-44228 preview

CVE-2021-44228

GitHubmr-r3b00t/cve-2021-44228

PowerShell-based backdoor detection tool for VMware Horizon connection servers, targeting CVE-2021-44228. Includes canary with optional submission…
defensive-toolsincident-responseintrusion-detection+1
134 years ago
redsun-bluehammer-undefend-detection-pack preview

redsun-bluehammer-undefend-detection-pack

GitHubletlaka/redsun-bluehammer-undefend-detection-pack

Microsoft Defender XDR KQL detections for RedSun, BlueHammer, UnDefend, and CVE-2026-33825-related Defender abuse behaviors.

cloud-securitydefensive-toolsincident-response+4
95 months ago
detection-defense-library preview

detection-defense-library

GitLabwattocyber/detection-defense-library

Detection-engineering reference mapping Windows, cloud, container, identity, and ICS attack classes to Sigma rules, trust-boundary models, BYOVD…
cloud-securitycontainer-securitycurated-resources+7
1 month ago
windows-malware-behavioral-analysis preview

windows-malware-behavioral-analysis

GitHub0x0allenace/windows-malware-behavioral-analysis

Behavioral Malware Analysis of a Simulated Multi-Stage Windows Malware Sample using FLARE-VM and REMnux. Evidence-driven DFIR investigation with IOC…
digital-forensicsdynamic-analysis-sandboxingeducation+8
12 months ago
DShield-SIEM preview

DShield-SIEM

GitHubbruneaug/dshield-siem

DShield Sensor Log Collection with ELK

defensive-toolsincident-responseintrusion-detection+4
501 month ago
NetScope preview

NetScope

GitHubspectralzero/netscope

Offline-first network investigation and response platform for Windows. Turns a pcap or live capture into a full forensic verdict — attack story,…
anomaly-detectiondigital-forensicsincident-response+5
31 month ago
Raccine preview

Raccine

GitHubneo23x0/raccine

A Simple Ransomware Vaccine
anomaly-detectiondefensive-toolsincident-response+3
9832 years ago
pySigma-backend-opensearch preview

pySigma-backend-opensearch

GitHubsigmahq/pysigma-backend-opensearch

pySigma OpenSearch backend
defensive-toolsintrusion-detectionlog-analysis+1
152 months ago
sigma-cli preview

sigma-cli

GitHubsigmahq/sigma-cli

The Sigma command line interface based on pySigma
defensive-toolsintrusion-detectionlog-analysis+2
2160 days ago
sysmon-modular preview

sysmon-modular

GitHubolafhartong/sysmon-modular

A repository of sysmon configuration modules
defensive-toolsdigital-forensicsincident-response+2
3.1k17 days ago
yellow preview

yellow

GitHubsinge/yellow

A simple binary wrapper for DNS canarytokens.
defensive-toolsintrusion-detectionnetwork-security
254 years ago
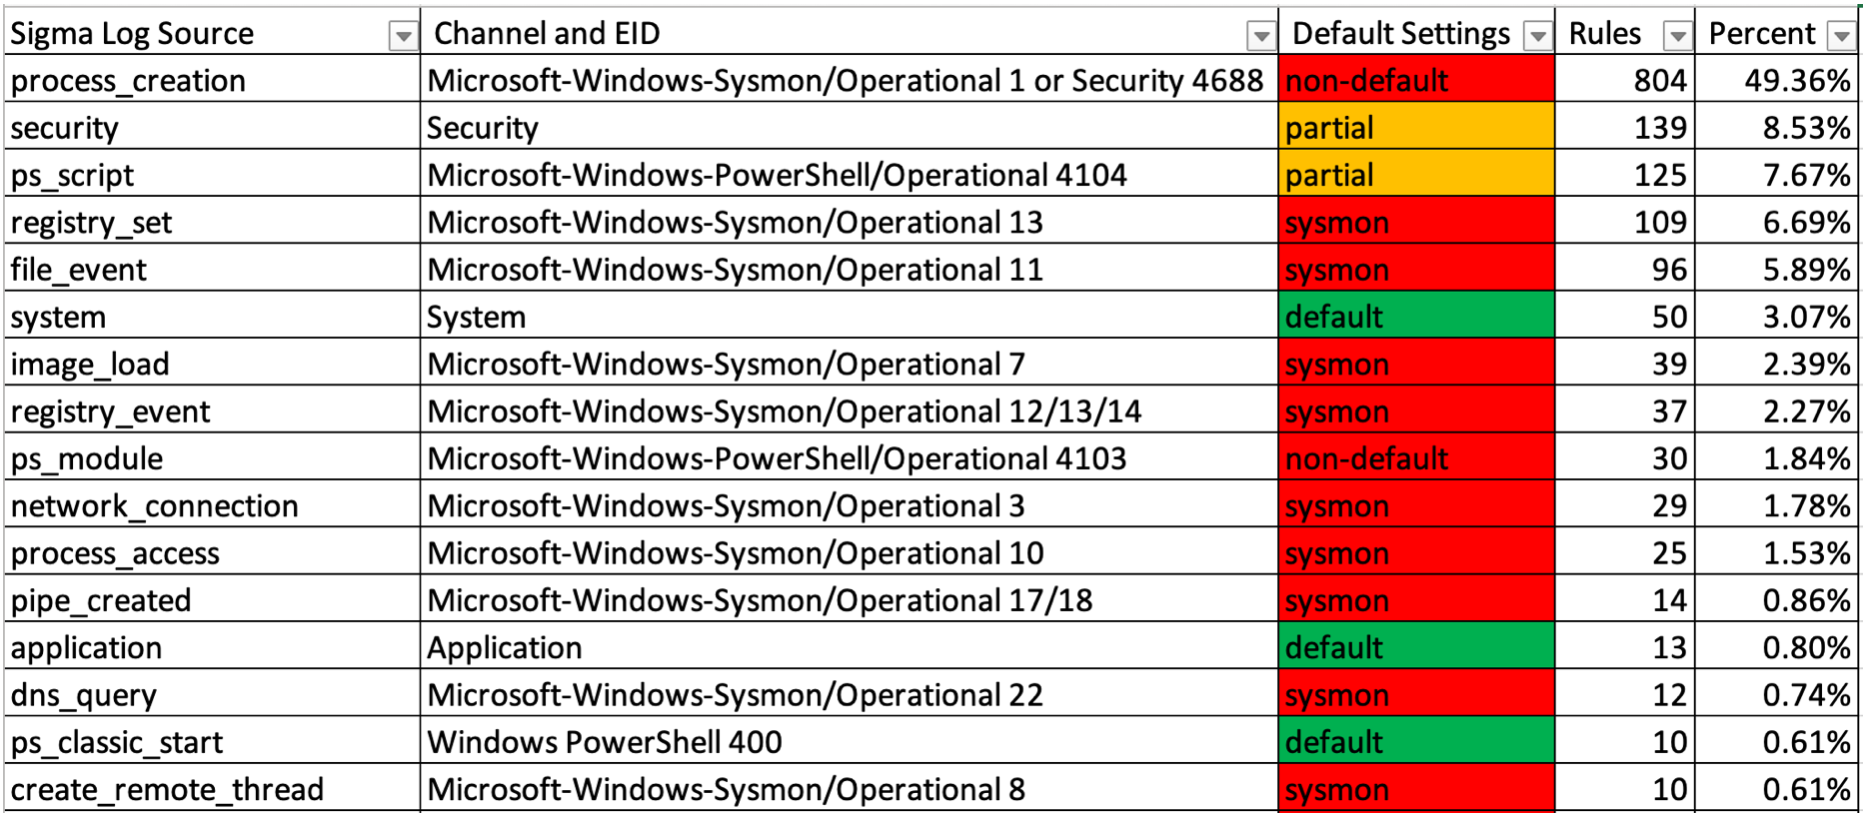
EnableWindowsLogSettings preview

EnableWindowsLogSettings

GitHubyamato-security/enablewindowslogsettings

Documentation and scripts to properly enable Windows event logs.

configuration-auditingdefensive-toolsdigital-forensics+3
7231 year ago
Previous123456Next