

jev-ids
 jev-sec/jev-ids
Blazing-Fast Token-Efficient Intrusion Detection System (IDS) based on TypeSafe's Jev.
anomaly-detectiondefensive-toolsintrusion-detection+5
2616h 27m ago
jev-sec/jev-idsBlazing-Fast Token-Efficient Intrusion Detection System (IDS) based on TypeSafe's Jev.
 rbidou/pyrasp
Runtime Application Self Protection for Python web servers, serverless functions and MCP servers, detecting attacks, prompt injection and data leaks…
 bombinisecurity/bombini
eBPF Security Monitoring and Sandboxing Agent Based on Aya
 harshiys/cve-2007-2447-exploitation-siem-detection-lab
Isolated AD/Linux attack lab: exploited CVE-2007-2447 via Metasploit, detected with Wazuh SIEM mapped to MITRE ATT&CK (T1190, T1059)
 immersive-labs-sec/bruteratel-detectiontools
A collection of Tools and Rules for decoding Brute Ratel C4 badgers
 sigmahq/sigma-cli
The Sigma command line interface based on pySigma
 criticalpathsecurity/zeek-intelligence-feeds
Aggregated Zeek-format threat intelligence feeds with combined indicators from public and curated sources for continuous IDS and network threat…
 theflink/hunt-weird-syscalls
ETW based POC to identify direct and indirect syscalls
 millikanjohnl-blip/dirtyfrag-detection-rules
Detection rules and analysis for Dirty Frag (CVE-2026-43284/CVE-2026-43500) Linux kernel LPE vulnerability. Based on community research and health…
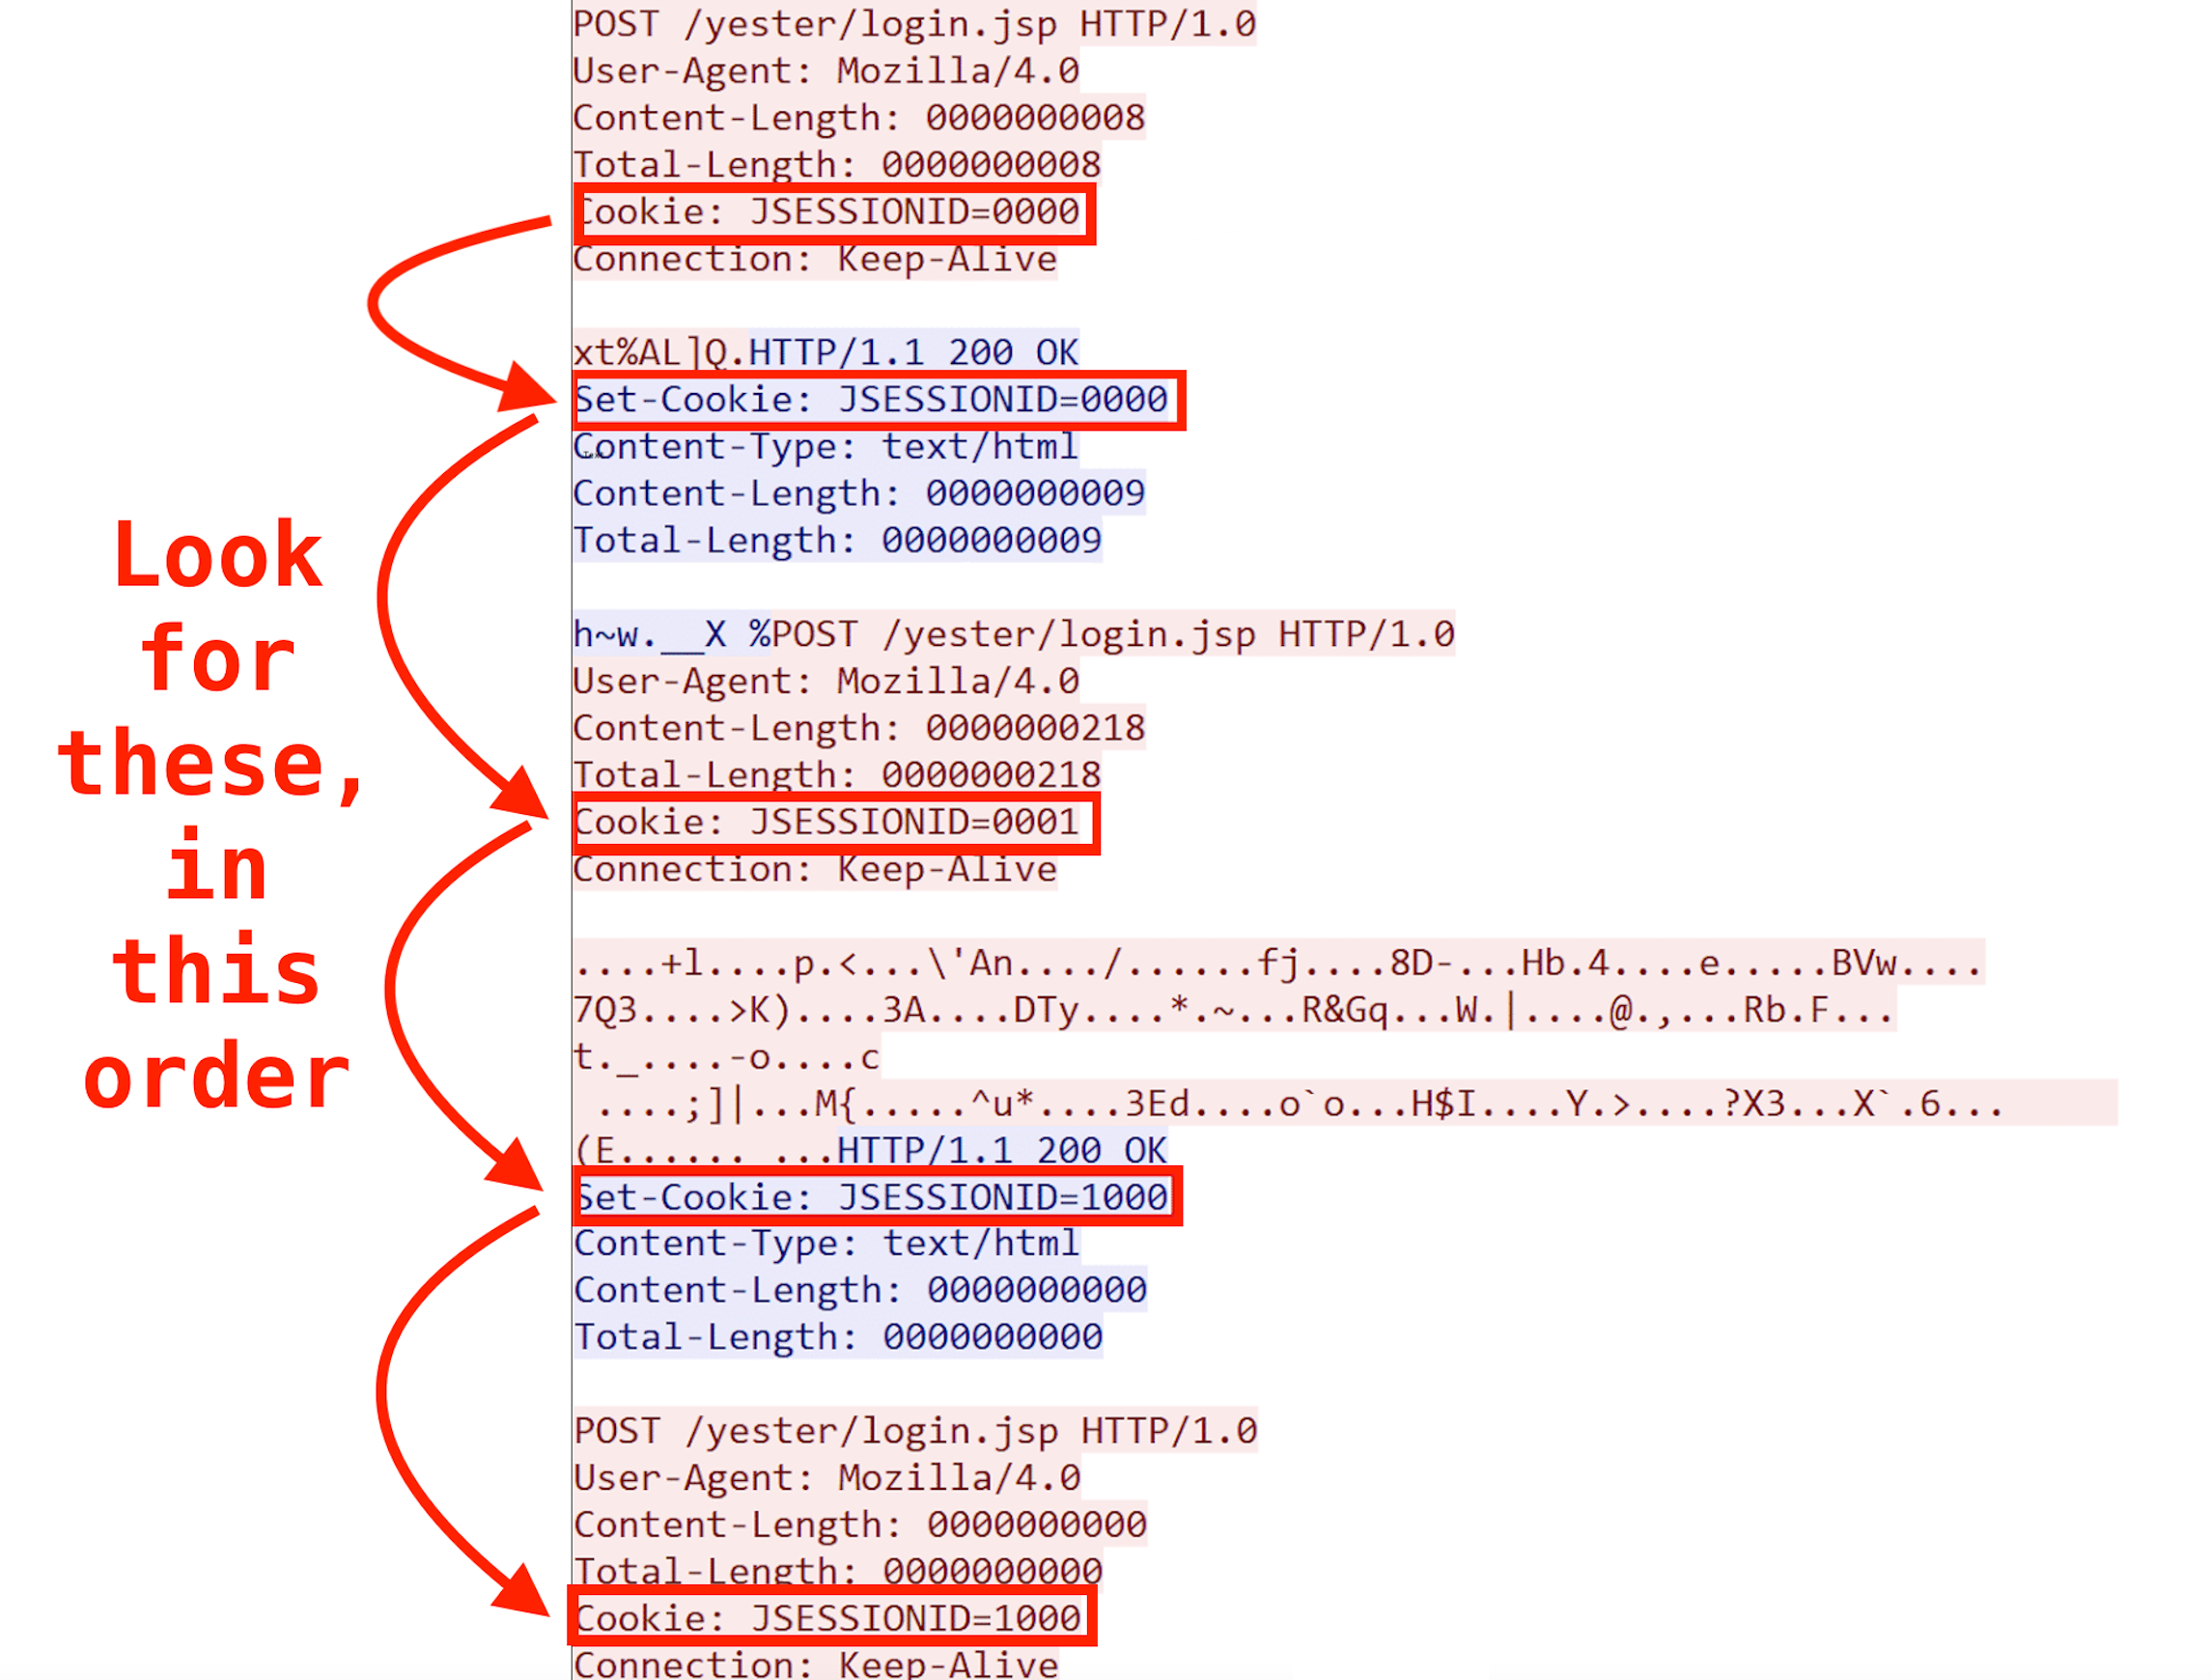 corelight/redxor
Detection of Linux Malware C2 RedXOR - demonstration
 corelight/zeek-agenttesla-detector
A Zeek based Agent Tesla malware C2 detector.
 corelight/zeek-asyncrat-detector
A Zeek based AsyncRAT malware detector.
 corelight/zeek-caldera-detector
A Zeek based Mitre Caldera detector.
 corelight/zeek-gozi-detector
A Zeek based Gozi banking malware detector.
 corelight/zeek-netsupport-detector
A Zeek based NetSupport detector. NetSupport is often abused by attackers in malware.
 corelight/zeek-spicy-ipsec
A Zeek IPSec protocol analyzer based on Spicy.
 corelight/zeek-spicy-facefish
A Zeek protocol analyzer for the Facefish rootkit, based on Spicy.