
SSHintel
 sonitbahl/sshintel
Self-contained SSH honeypot for capturing attacker interactions and turning them into structured security intelligence.
incident-responseintrusion-detectionlog-analysis+2
3
sonitbahl/sshintelSelf-contained SSH honeypot for capturing attacker interactions and turning them into structured security intelligence.
 duggytuxy/syswarden
Host-local Linux security orchestrator enforcing nftables policy with HIDS/HIPS telemetry, bounded threat-intelligence feeds, out-of-band WAAP log…
 withsecurelabs/lazarus-sigma-rules
Sigma rules for detecting Lazarus Group TTPs, covering malicious document execution, PowerShell abuse, scheduled tasks, and credential access,…
 thinkst/opencanary
Low-resource honeypot that emulates common network services to detect post-breach attacker activity, with extensible protocol modules and…
 infokom-ki/zimbra-cve-2026-73570-rules
Wazuh detection rules for CVE-2026-73570, an OS command injection in Zimbra Collaboration Suite, monitoring web access logs and zimbra.log for…
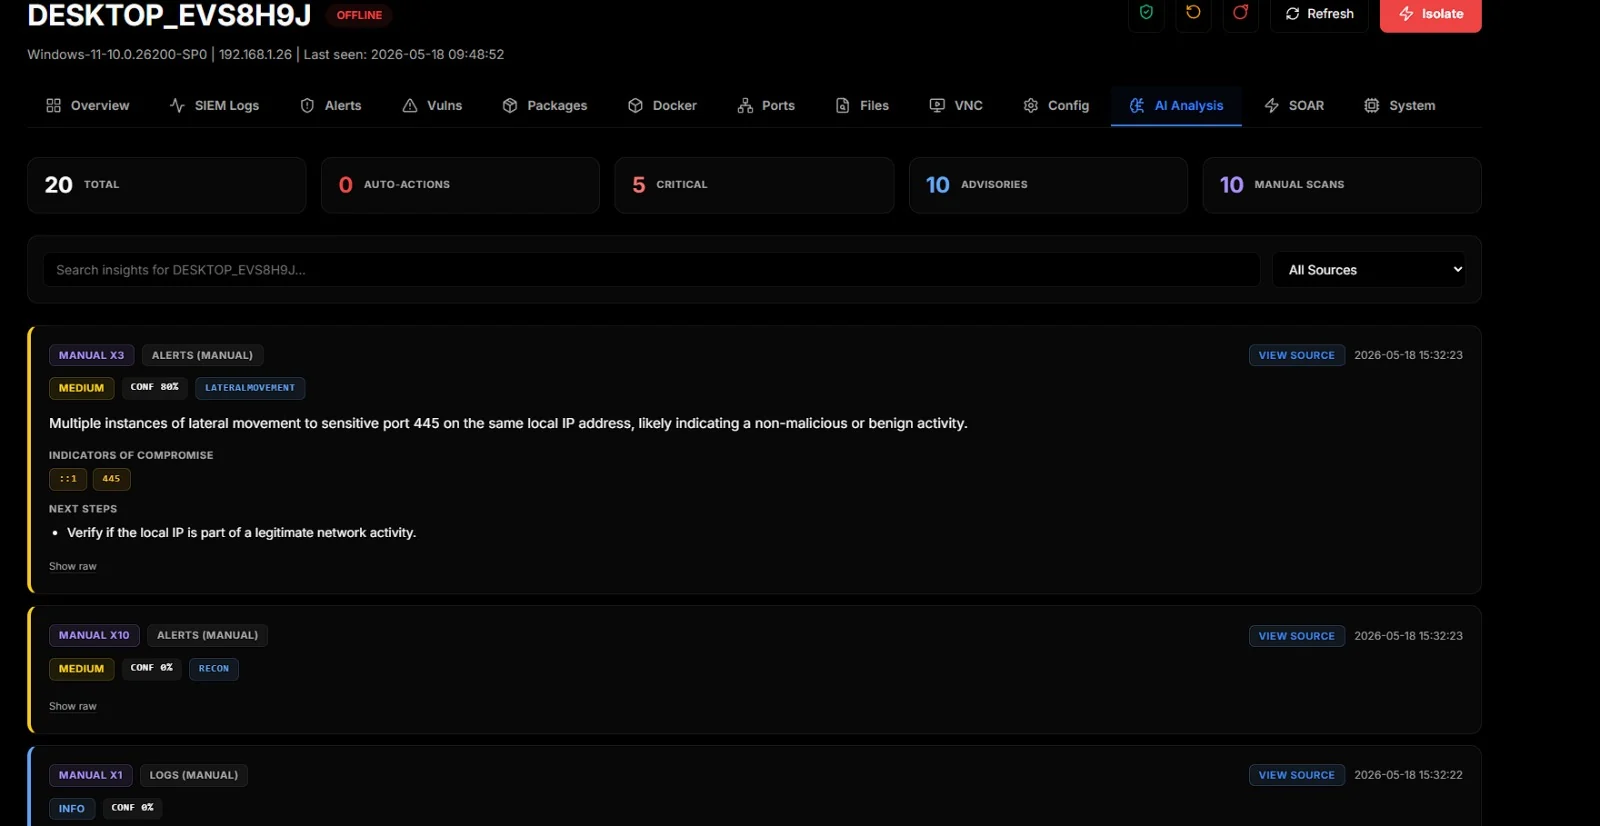 d3vhex/sentora
An open-source, self-hosted AI-powered SIEM, EDR and SOAR platform for modern security operations.
 unfold-security/cve-2026-41940-detection
Detection signatures for CVE-2026-41940 and shemas for cPanel logs
 srozb/reditrap
Minimal Redis honeypot detecting RediShell (CVE-2025-49844) exploits.
 garethmsheldon/cve-2026-22557-unifi-detection
Detection content for CVE-2026-22557 — UniFi Network Application unauthenticated path traversal (CVSS 10.0). Includes YARA, Sigma, KQL, Splunk SPL,…
 0x4d31/awesome-threat-detection
Curated list of threat detection and hunting resources: detection rules, SIEM and log analysis tools, endpoint/network monitoring, datasets,…
 mgreen27/detectraptor
A repository to share publicly available Velociraptor detection content
 graylog2/graylog2-server
Centralized log management platform for collecting, indexing, and analyzing streaming logs, with alerting and event correlation for security…
 security-onion-solutions/securityonion
Open-source security monitoring platform for threat hunting, intrusion detection, log management, incident response, and endpoint visibility with…
 bruneaug/dshield-siem
DShield Sensor Log Collection with ELK

 sigmahq/pysigma-backend-opensearch
pySigma OpenSearch backend
 sigmahq/sigma-cli
The Sigma command line interface based on pySigma
 gossithedog/threathunting
Tools for hunting for threats.