
CVE-2025-32433-LAB
 damnkrishna/cve-2025-32433-lab
A Flaw in SSH protocol message handling, a malicious actor could gain unauthorized access to affected systems and execute arbitrary commands without…
container-securityeducationexploitation+6
damnkrishna/cve-2025-32433-labA Flaw in SSH protocol message handling, a malicious actor could gain unauthorized access to affected systems and execute arbitrary commands without…
 devinblack001/ddos-reduction-system
Adaptive two-stage Layer 4 DDoS mitigation gateway using behavioral traffic analysis, Random Forest classification, and kernel-level ipset/iptables…
 douglas-042/douglas-042-hq
Central console for Douglas-042 HEADQUARTERS collectors. Sweeps a fleet, correlates results across hosts, and manages IOC feeds and SIEM delivery…
 bombinisecurity/bombini
eBPF Security Monitoring and Sandboxing Agent Based on Aya
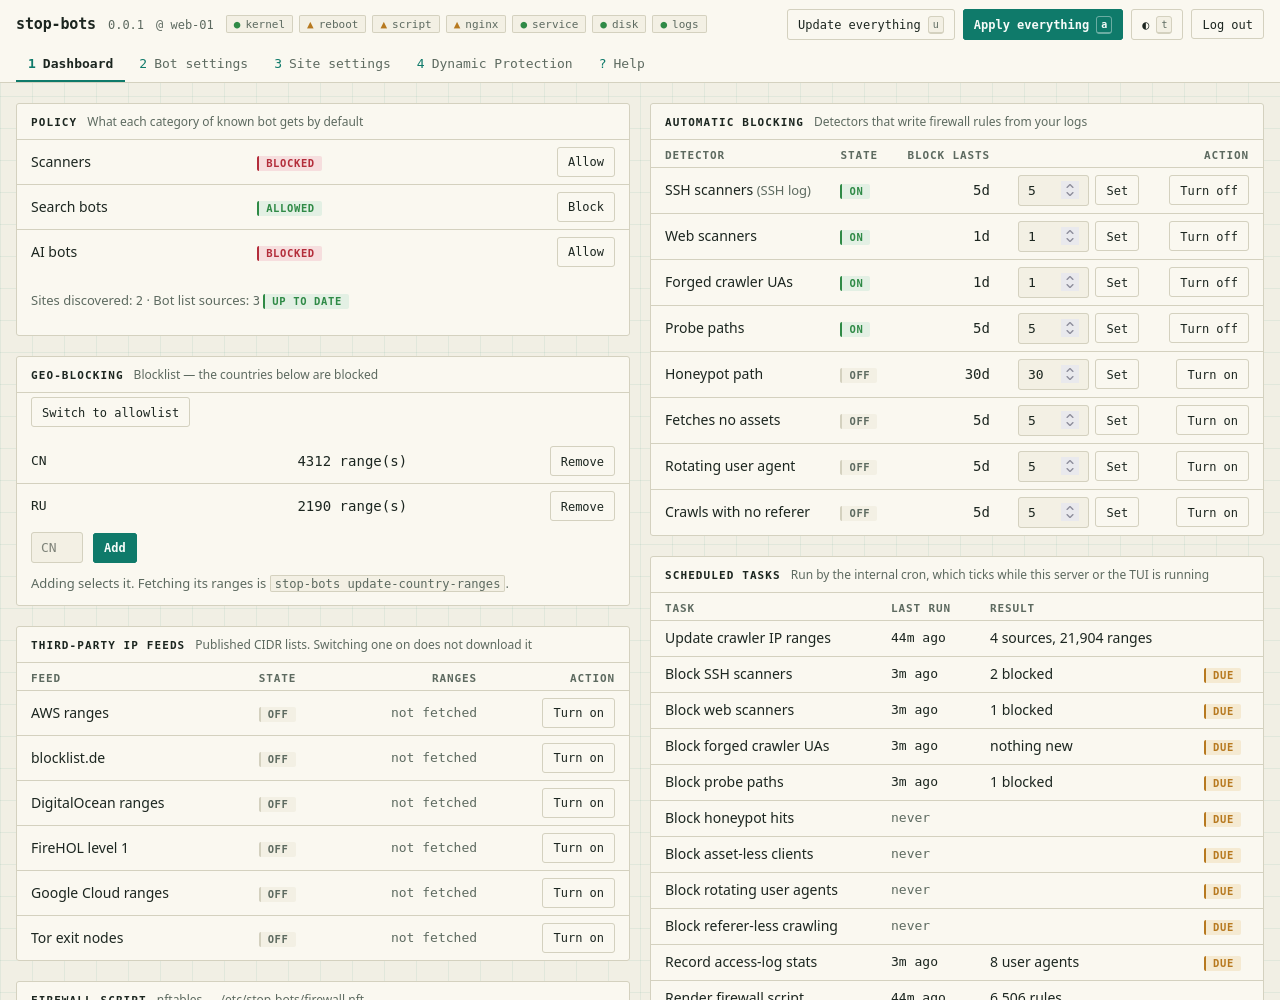 ivankovic/stop-bots
Automate stopping bad bots from accessing your server
 falconforceteam/falcondash
Azure workbook dashboard that visualizes and explores detection performance metrics, helping security teams measure and proactively maintain their…
 sonitbahl/sshintel
Self-contained SSH honeypot for capturing attacker interactions and turning them into structured security intelligence.
 jithinkrishnanrs/stylesmuggler-ioc-toolkit
StyleSmuggler (CVE-2026-75650) IOC toolkit for Magento Open Source and Adobe Commerce. Detect compromised stores, Rust implants, PHP web shells,…
 safeagent-beihang/clawguard
Enterprise AI agent security toolkit providing pre-flight auditing, configuration hardening, runtime threat detection, and active defense against…
 duggytuxy/syswarden
Host-local Linux security orchestrator enforcing nftables policy with HIDS/HIPS telemetry, bounded threat-intelligence feeds, out-of-band WAAP log…
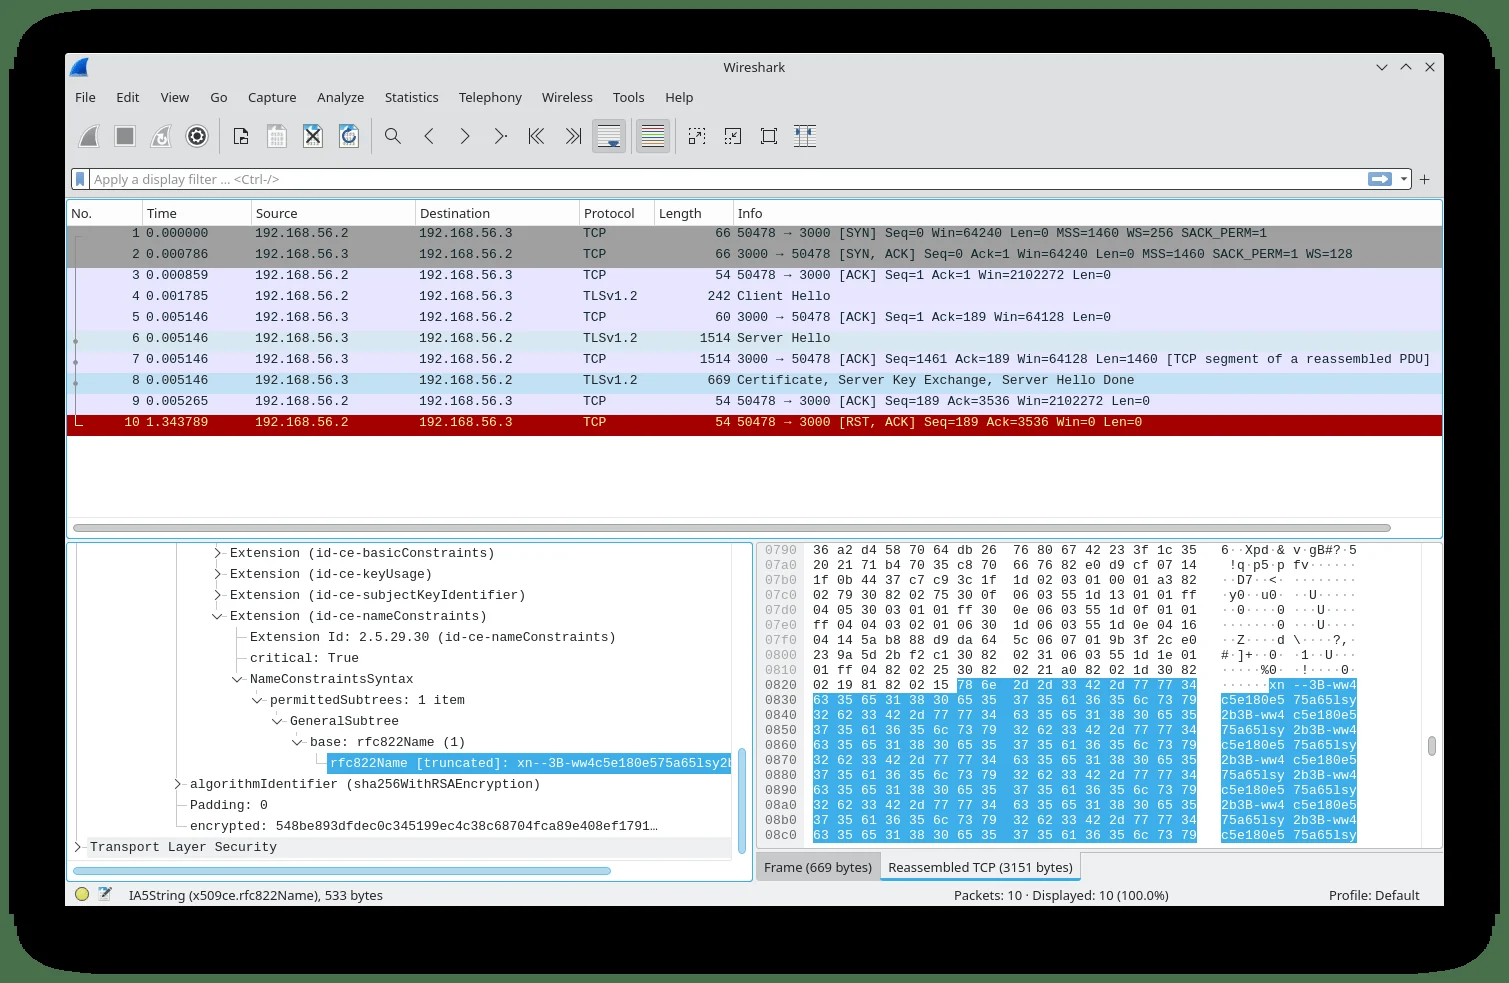 fox-it/spookyssl-pcaps
PCAPs and Suricata signatures for detecting OpenSSL CVE-2022-3602 exploitation attempts, including malicious client/server traffic and legitimate…
 jdinovo/spade
SPaT Attack Detection and Evaluation dataset
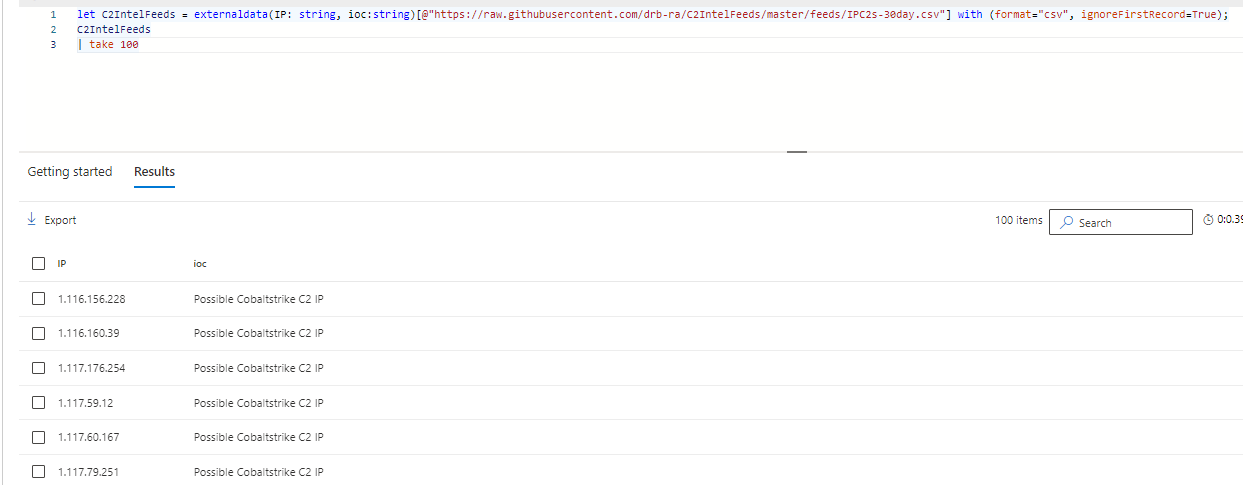 bert-janp/open-source-threat-intel-feeds
This repository contains Open Source freely usable Threat Intel feeds that can be used without additional requirements. Contains multiple types such…
 fankh/vulnerability-poc
CVE proof-of-concept labs, exploit scripts, and detection/prevention rules (Nginx, Apache, Snort, YARA) for high-severity CVEs. Authorized security…
 gmh5225/crowarmor
Linux kernel security driver using LSM to harden the system, monitor and restore syscall table integrity, and protect CPU control registers against…
 withsecurelabs/lazarus-sigma-rules
Sigma rules for detecting Lazarus Group TTPs, covering malicious document execution, PowerShell abuse, scheduled tasks, and credential access,…
 elihiho/security-operations-labs
Threat Modeling, IT-/OT-Segmentierung, Snort Detection und reproduzierbare Validierung eines Drupal-Detection-Profils.
 thinkst/opencanary
Low-resource honeypot that emulates common network services to detect post-breach attacker activity, with extensible protocol modules and…