
reditrap
 srozb/reditrap
Minimal Redis honeypot detecting RediShell (CVE-2025-49844) exploits.
intrusion-detectionlog-analysisnetwork-security+2
srozb/reditrapMinimal Redis honeypot detecting RediShell (CVE-2025-49844) exploits.
 r4j3sh-com/cve-2025-55182
Lightweight Go toolkit plus a Dockerized Next.js lab to explore and triage CVE-2025-55182.
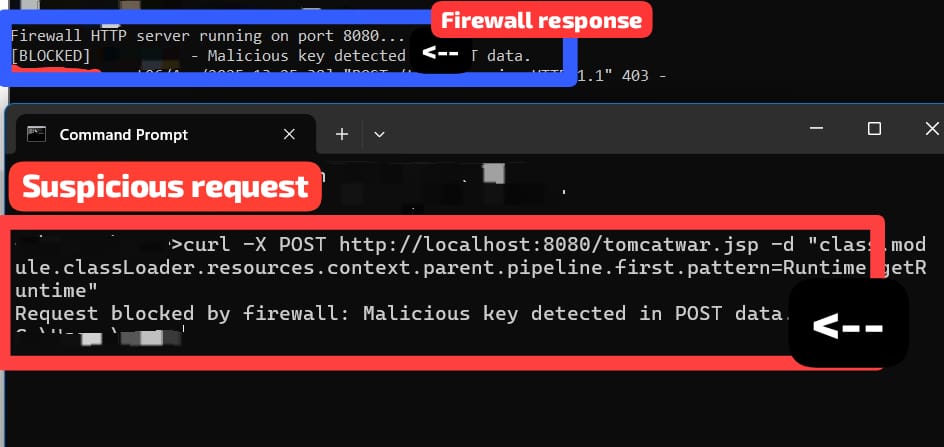 salo-404/firewall
🔒 Spring4Shell Firewall Defense — Cybersecurity Incident Simulation This project is part of a Cybersecurity Job Simulation I completed in August…
 tinashelorenzi/cve-2025-55182
Proof-of-concept exploit for CVE-2025-55182, a critical unauthenticated RCE in React Server Components. Includes automated Python exploit, technical…
 solidevil14/suricata-rule-for-detecting-cve-2025-55182
CVE‑2025‑55182 Detection
 travisbgreen/cve-2025-8088
cve-2025-8088_detection
 te0rwx/cve-2025-32433-detection
Custom YARA rule for detecting artifacts of CVE-2025-32433, an Erlang/OTP SSH pre-authentication RCE vulnerability. Validated against public PoCs and…
 garethmsheldon/cve-2025-60787-detection-motioneye-rce-via-config-injection
Detection rules and YARA/KQL signatures for CVE-2025-60787, an unauthenticated RCE in motionEye via config injection, with process execution and file…
 daryllundy/cve-2025-32463
Detection framework for CVE-2025-32463 sudo privilege escalation vulnerability. Provides real-time monitoring, forensic analysis, and SIEM…
 elshaheedy/cve-2025-29927-sigma-rule
Sigma rule for detecting CVE-2025-29927 exploitation via suspicious x-middleware-subrequest HTTP headers in Next.js applications, with detection…
 t0tooro/cve-2025-24054-lab
Blue-team lab: detecting & mitigating CVE-2025-24054 (Windows NTLM hash disclosure) with Sysmon, Wazuh SIEM, and Group Policy
 adnansiyat/how-to-patch-cve-2025-32709
Real-world patching workflow for CVE-2025-32709. From hotfix install to SIEM alert validation—this repo documents every step with screenshots,…
 rickgeex/cve-2025-5777-citrixbleed
CitrixBleed-2 (CVE-2025-5777) – proof-of-concept exploit for NetScaler ADC/Gateway “memory bleed”
 darses/cve-2025-32433
Security research on Erlang/OTP SSH CVE-2025-32433.