

pyrasp
 rbidou/pyrasp
Runtime Application Self Protection for Python web servers, serverless functions and MCP servers, detecting attacks, prompt injection and data leaks…
ai-securityanomaly-detectionapi-security+6
39
rbidou/pyraspRuntime Application Self Protection for Python web servers, serverless functions and MCP servers, detecting attacks, prompt injection and data leaks…
 gopasteverything/gpewebdefender
Lightweight web-attack monitor. One Go binary + SQLite. Not OSSEC, not a WAF.
 rohithronanki/cve-2026-34159-vulnerability-research-analysis-detection
Critical buffer validation bypass in deserialize_tensor() (llama.cpp < b8492). Null tensor buffer skips bounds check, enabling unauthenticated…
 kadir/copy-fail-cve-2026-31431-ioc
Detection, mitigation, and IOC toolkit for Copy Fail CVE-2026-31431 Linux kernel page-cache privilege escalation
 hslatman/awesome-industrial-control-system-security
A curated list of resources related to Industrial Control System (ICS) security.
 bruneaug/dshield-siem
DShield Sensor Log Collection with ELK
 ion-storm/sysmon-config
Advanced Sysmon ATT&CK configuration focusing on Detecting the Most Techniques per Data source in MITRE ATT&CK, Provide Visibility into Forensic…
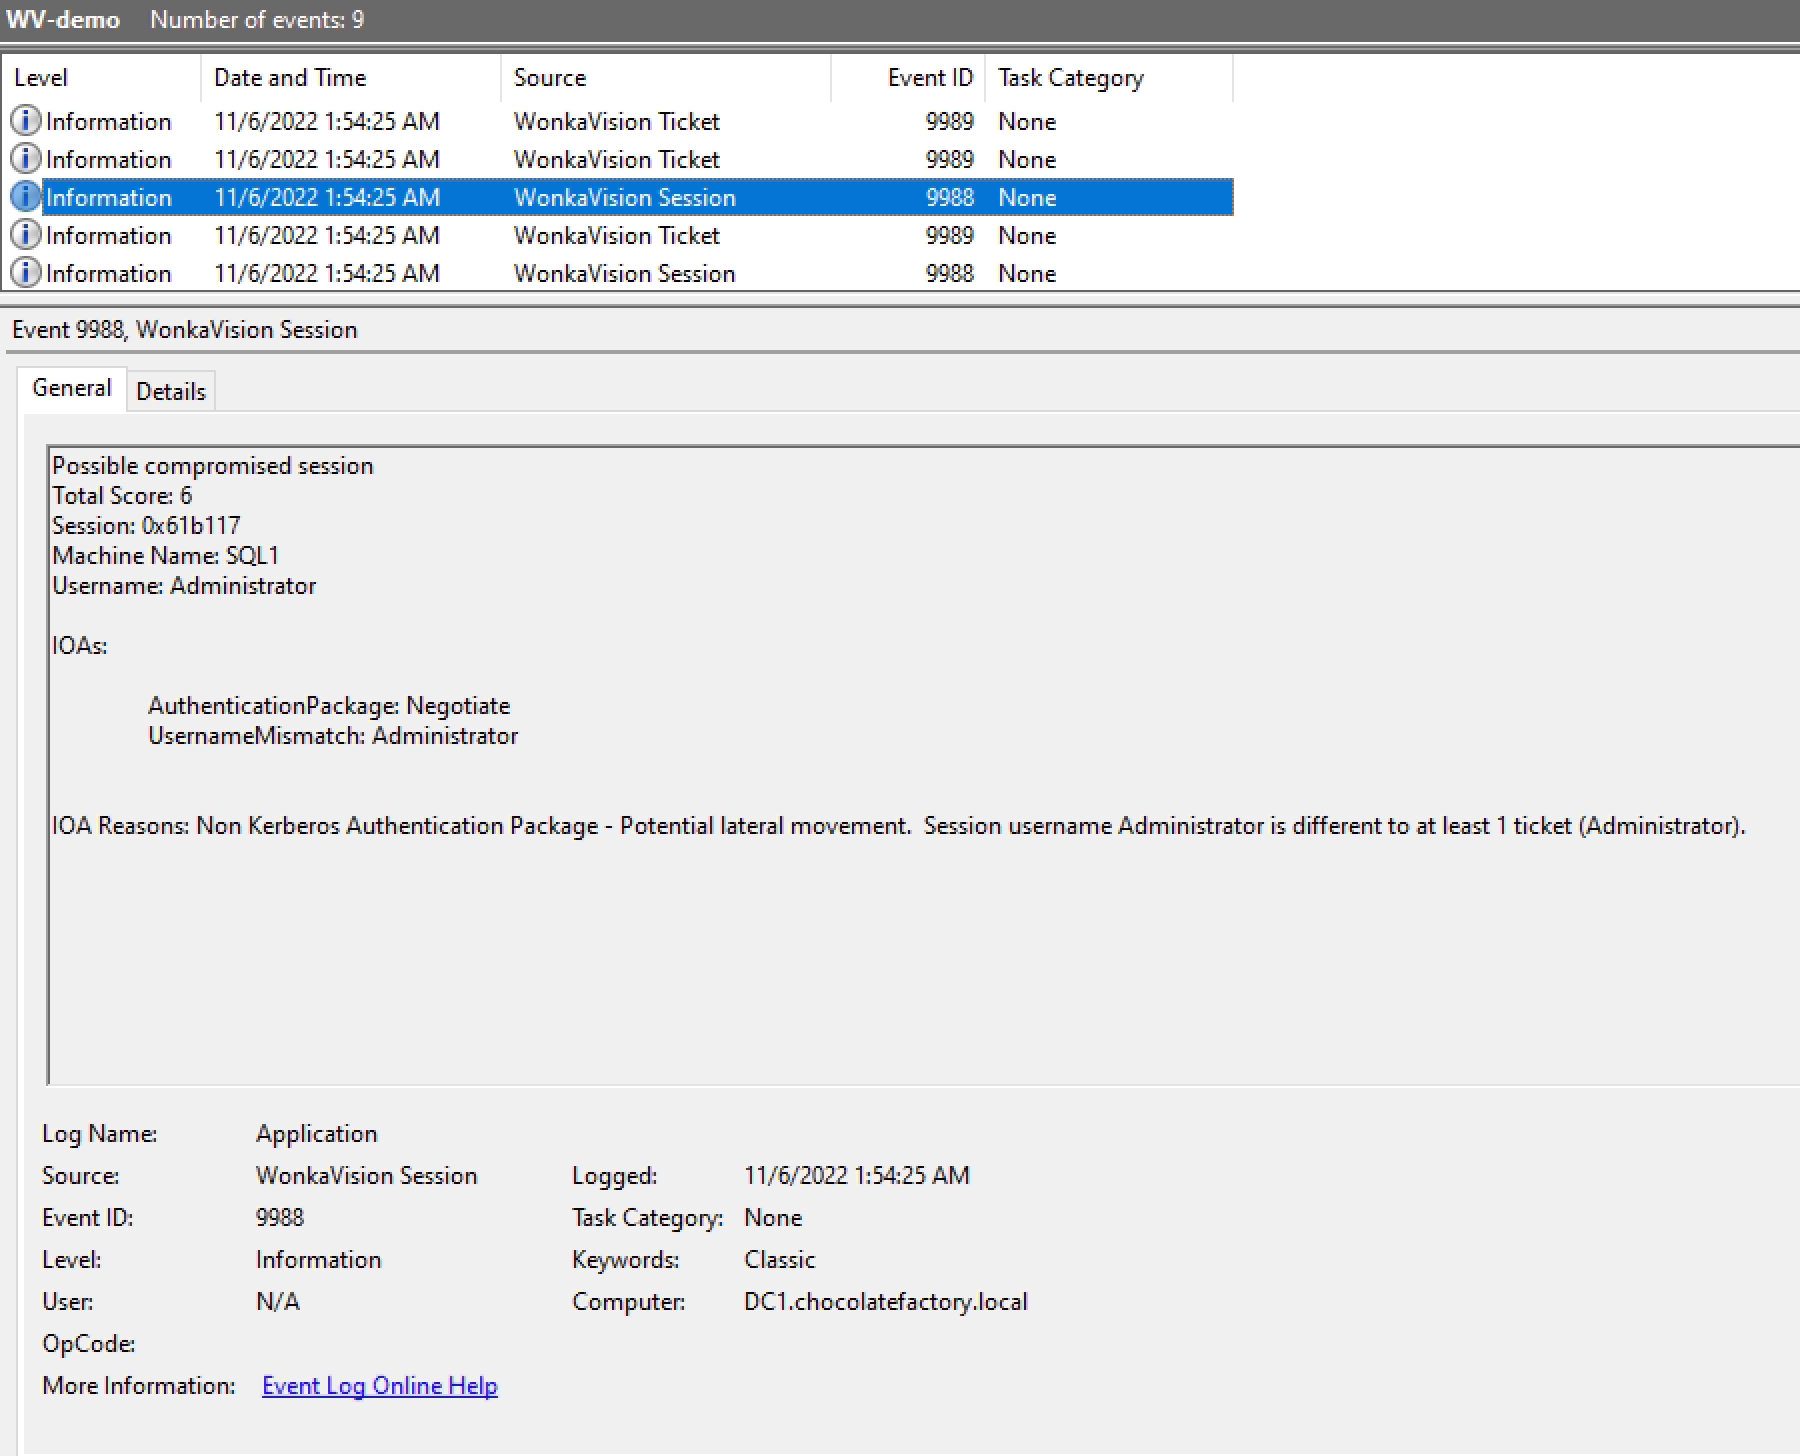 0xe7/wonkavision
Detects forged Kerberos tickets by dumping session and ticket data, scoring anomalies, and generating Windows event-log indicators for SIEM-based…
 criticalpathsecurity/zeek-intelligence-feeds
Aggregated Zeek-format threat intelligence feeds with combined indicators from public and curated sources for continuous IDS and network threat…
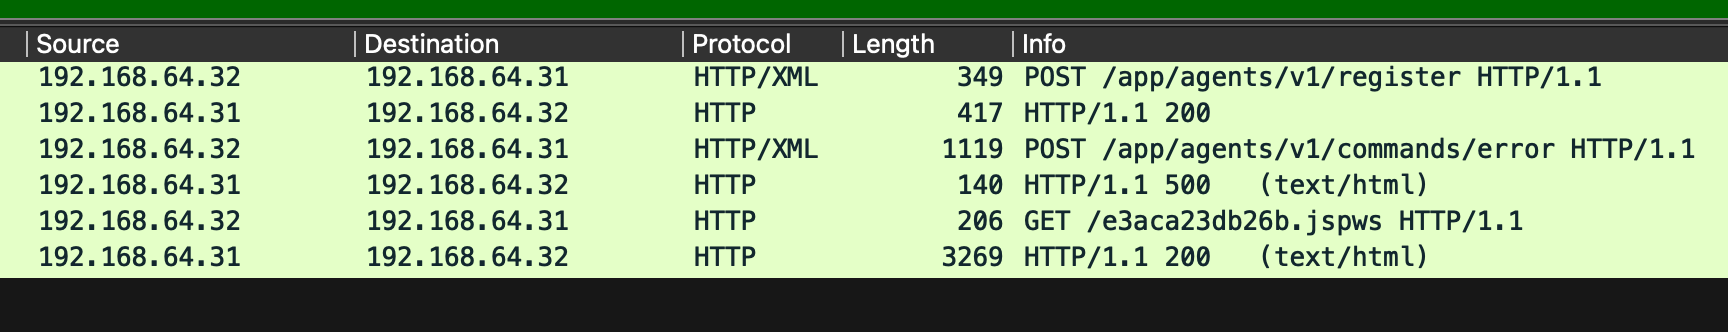 boredhackerblog/teamcity-cve-2026-63077-pcap
teamcity teamcity-CVE-2026-63077 exploitation pcap
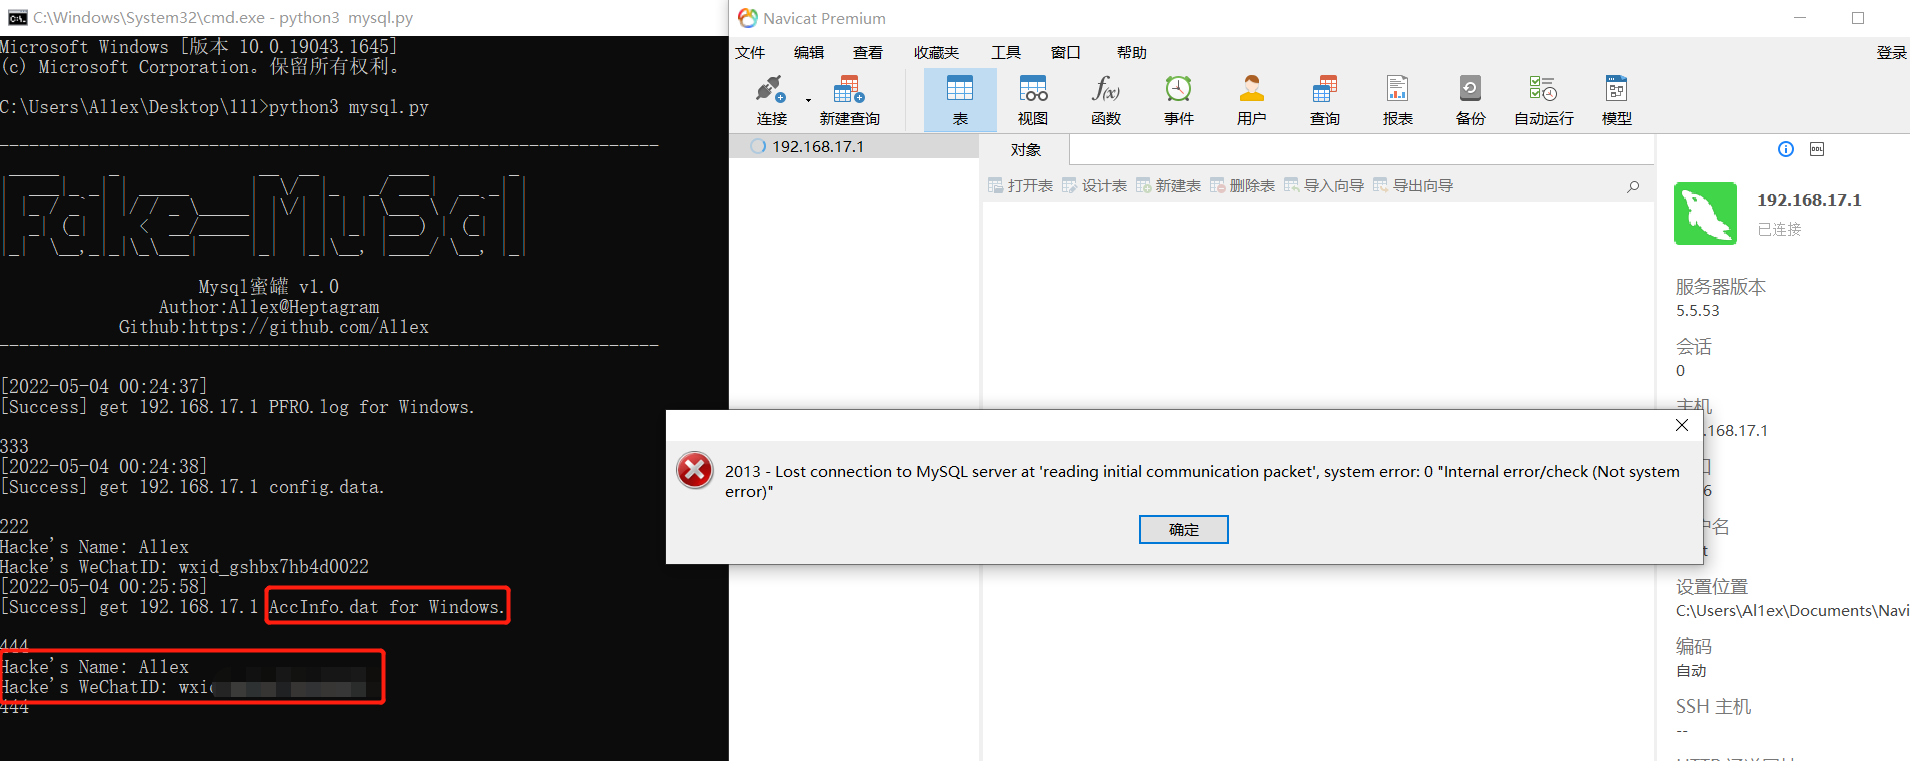 al1ex/mysqlhoneypot
MysqlHoneypot
 corelight/community-id-spec
An open standard for hashing network flows into identifiers, a.k.a "Community IDs".
 corelight/http-stalling-detector
Detect HTTP stalling attacks like slowloris with Bro
 corelight/icanntld
Zeek script using the official ICANN Top-Level Domain (TLD) list with the Input Framework to extract the relevant information from a DNS query and…
 corelight/petitpotam-notest
Zeek package for detecting PetitPotam NTLM relay attacks via EFS DCERPC over unencrypted SMB, distinguishing successful and unsuccessful exploit…
 corelight/threat-hunting-guide
Structured guide to threat hunting using Zeek logs, aligned with MITRE ATT&CK framework for proactive detection of adversary tactics and techniques.
 corelight/top-dns
Top DNS Measurement for Bro
 corelight/zeek-openvpn
A Zeek OpenVPN protocol analyzer plugin.