
csumguard
 mchorfa/csumguard
Restricted eBPF TC ingress guard, CO-RE detector, verified loader, and C11 VMM launch supervisor for CVE-2026-99999
configuration-auditingcontainer-securitydefensive-tools+7
3
mchorfa/csumguardRestricted eBPF TC ingress guard, CO-RE detector, verified loader, and C11 VMM launch supervisor for CVE-2026-99999
 h1z3-br0/cve-2026-98432
Laboratory toolkit for CVE-2026-98432 Linux TCP ireq_opt use-after-free: race trigger with heap-reuse oracle, leak parser, KASLR resolver, pcap…
 al4n4n/cve-2026-98432
PoC, non-destructive version scanner, KASAN crash verifier, and Suricata/Sigma detection rules for the Linux kernel TCP/IPv4 IP-options…
 xsanflip/dangdut
Passive wireless intrusion detection system for ESP32-S3 and Flipper Zero that detects Wi-Fi deauthentication and disassociation attacks in real…
 wagga40/logstotal
Self-hosted multi-engine Sigma detection for event logs
 dragon-lady/netward-standalone
User-space bot and DDoS deflection for small HTTP services
 phpatch/weblogchecker
Free access-log compromise analyzer: webshell interactions, exploitation patterns and brute-force bursts in your Apache/nginx logs - severity,…
 d3lightfu1/quietphase
Pwsh tool for AD Group Enumeration Auditing
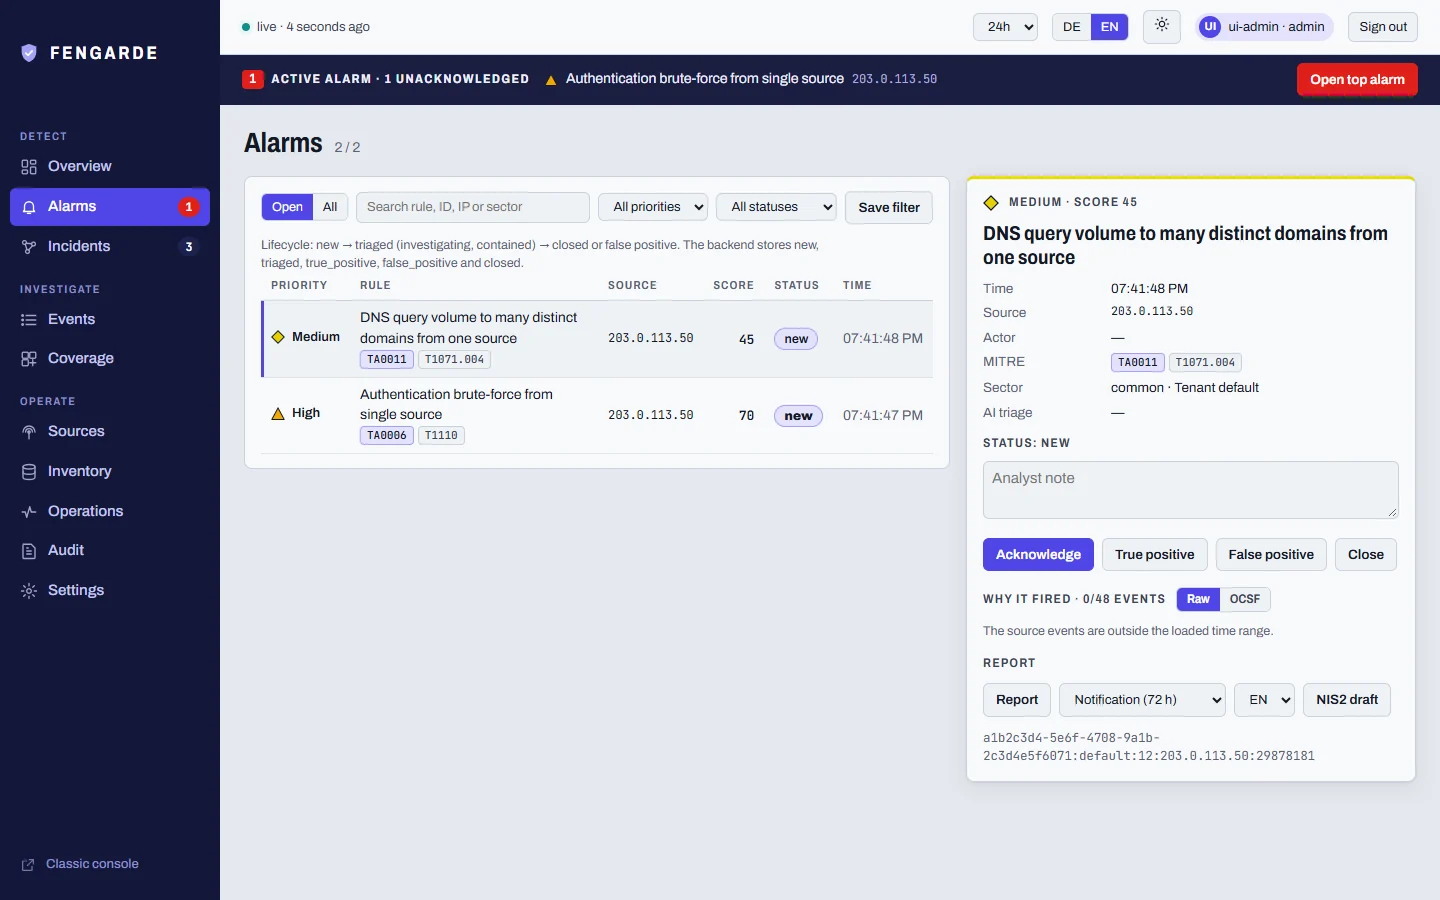 supermhel/fengarde
Open-source, self-hosted security pipeline for IT, AI and OT. Logs in. Evidence out.: OCSF normalization, 46 detection rules…
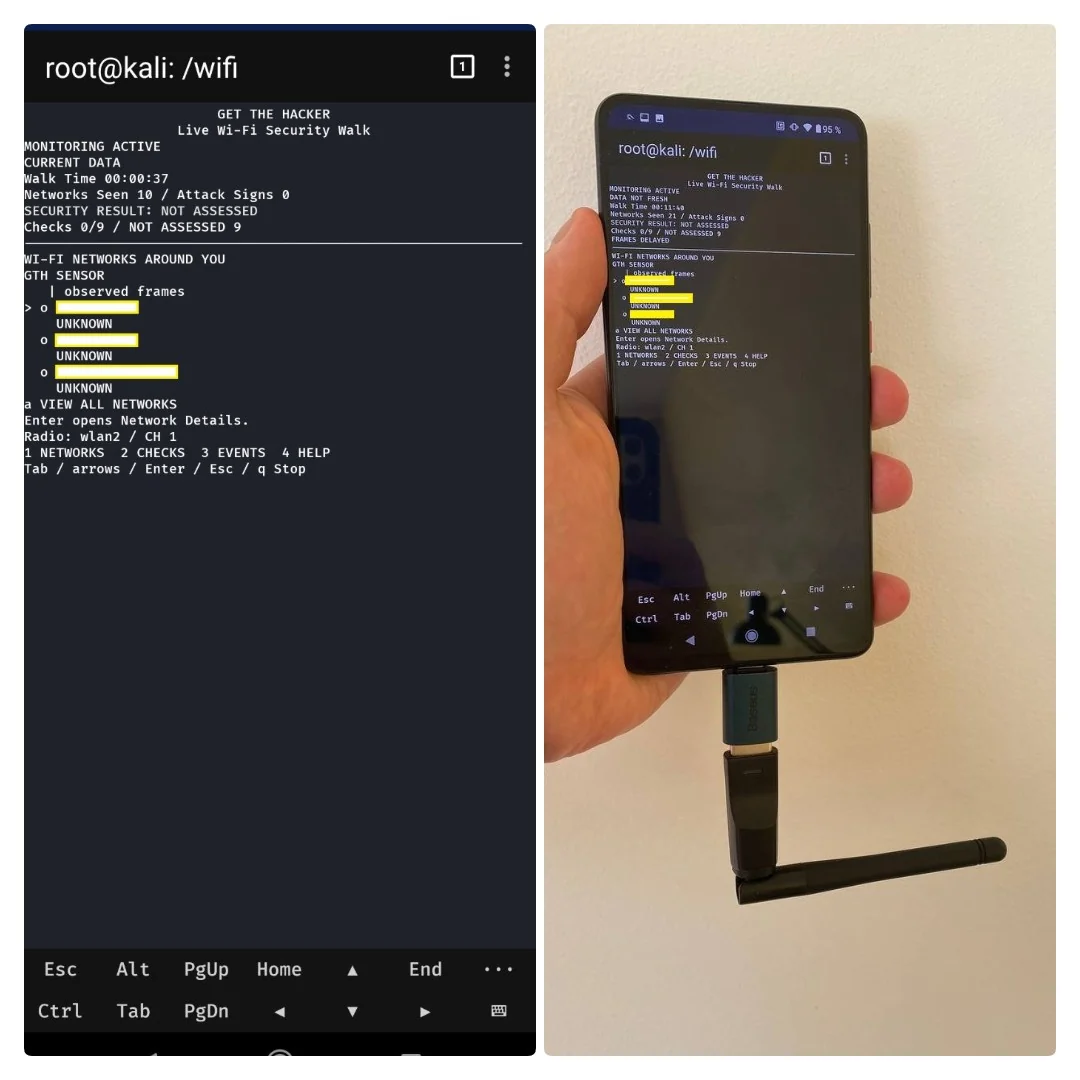 buybitart/get-the-hacker
Hunt WiFi threats silently. Catch the hackers.
 dshield-isc/dshield
Installs and configures a DShield honeypot sensor on Raspberry Pi or Ubuntu, running Cowrie SSH and HTTP honeypots and forwarding firewall logs to…
 0xajstrike/opcuatrap
High-interaction OPC UA honeypot for ICS/SCADA — multi-profile (oil & gas, water, power grid), live process simulation, per-session threat scoring,…
 aide/aide
File integrity monitoring tool that detects unauthorized changes to monitored files and directories using attribute checks, multiple hash algorithms,…
 jaksi/sshesame
An easy to set up and use SSH honeypot, a fake SSH server that lets anyone in and logs their activity
 0xmfbk/ebpf-container-escape-framework
Audit only eBPF EDR for Linux 5.15+ LTS: 14 kernel hooks, 15 actions (13 MITRE techniques), process lineage, SIEM export, K8s/Docker ready.
 perplexityai/numbat
Visibility into AI agent activity on endpoints, with on-device detection, optional pre-action blocking, and forensic reconstruction.
 cognis-digital/c2detect
C2 server fingerprinter — Cobalt Strike, Sliver, Mythic, Havoc, Brute Ratel
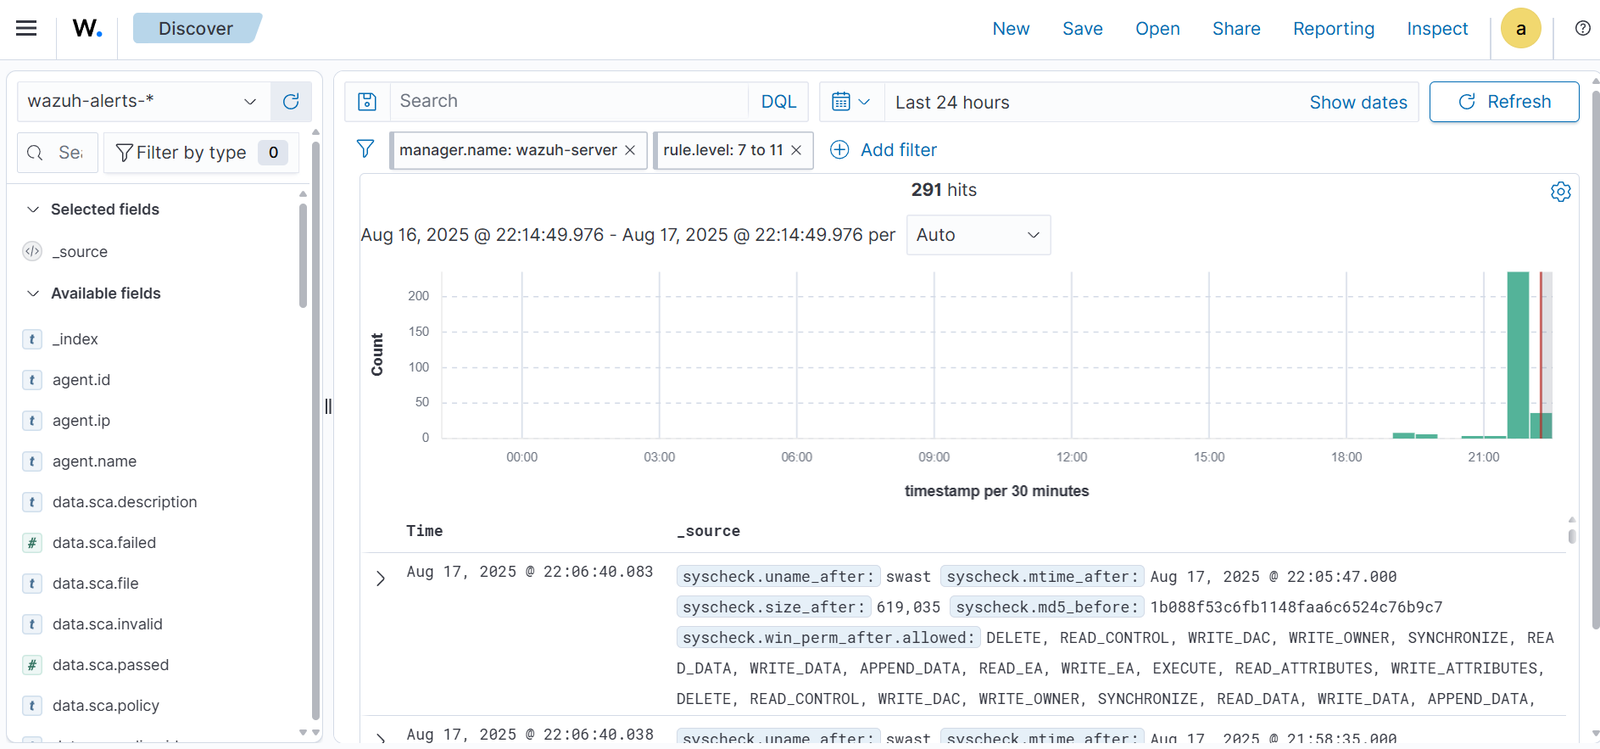 swastiksagar/wazuhlabproject
Hands-on Wazuh SIEM/XDR home lab covering OVA deployment, agent enrollment, file integrity monitoring, VirusTotal malware detection, and MITRE ATT&CK…