
openclaw-security-monitor
 adibirzu/openclaw-security-monitor
Proactive security monitoring for OpenClaw deployments. Detects ClawHavoc, AMOS stealer, CVE-2026-25253, memory poisoning, and supply chain attacks.
defensive-toolseducationforensics+9
48
adibirzu/openclaw-security-monitorProactive security monitoring for OpenClaw deployments. Detects ClawHavoc, AMOS stealer, CVE-2026-25253, memory poisoning, and supply chain attacks.
 mfthomps/labtainers
Labtainers: A Docker-based cyber lab framework
 prox0959/memguard
Zero-dependency Windows EDR utility that detects and mitigates unauthorized LSASS memory access, handle duplication, and LOLBin credential dumping in…
 hackspeak/cve-2026-23479
Redis UAF RCE PoC collection for CVE-2026-23479: safe version checker, exploit module, GDB-assisted PoC, and Sigma detection rules for authorized…
 tungduongnt/cve-2014-0160.
Docker-based lab environment for exploiting CVE-2014-0160 (Heartbleed) to leak sensitive memory from nginx web servers, with Snort IDS detection…
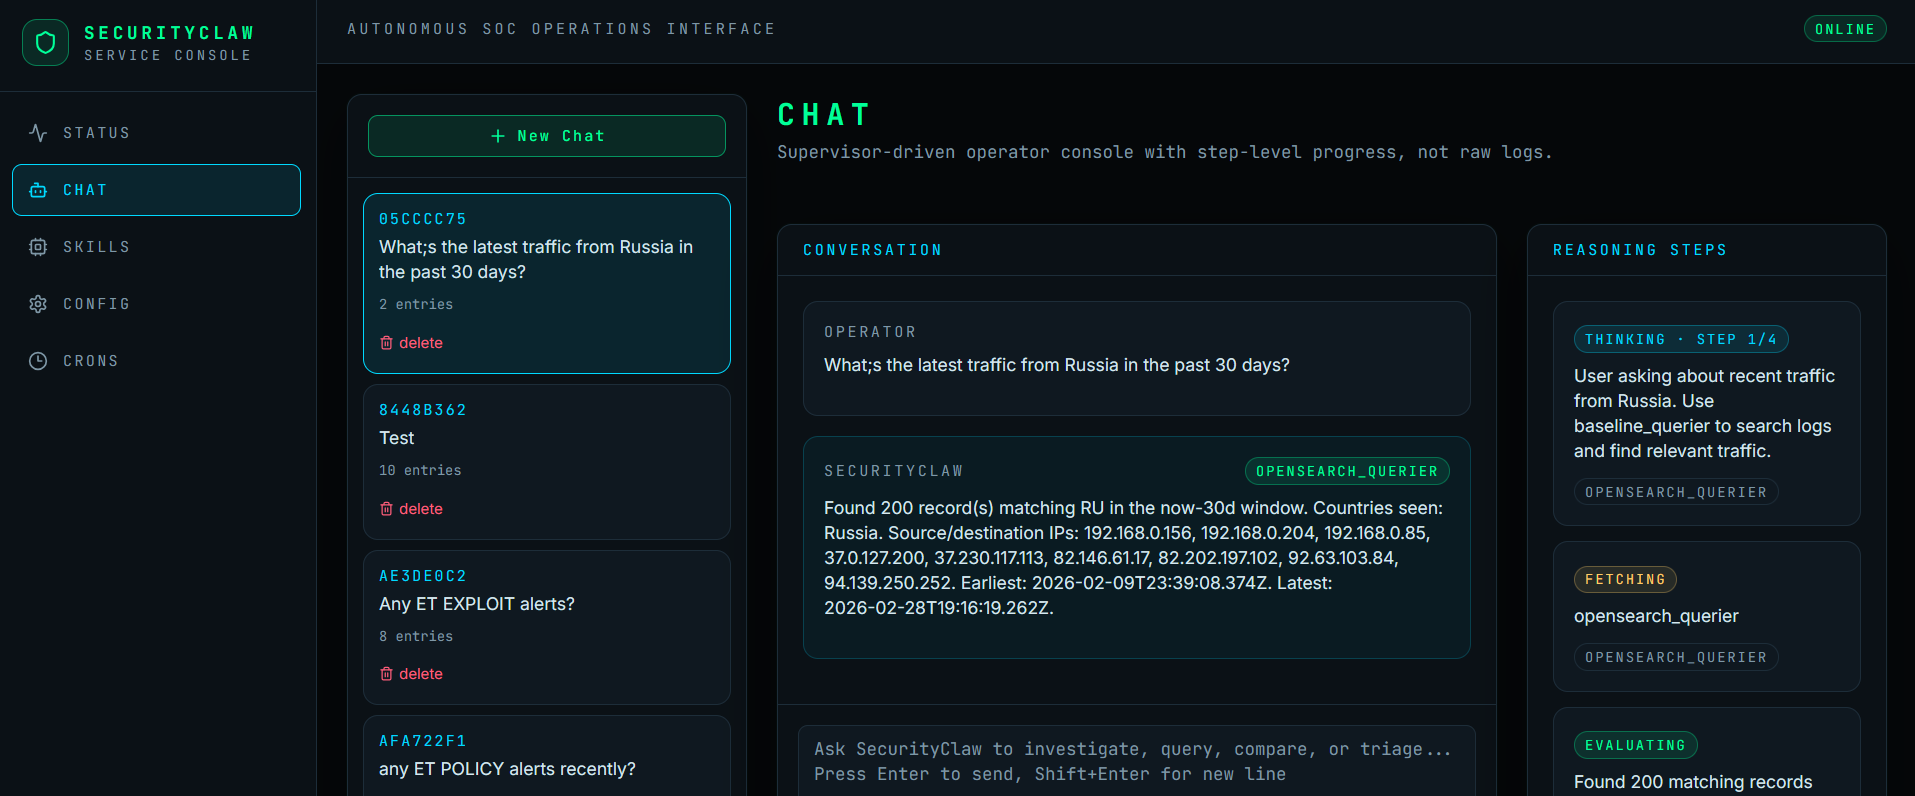 securityclaw/securityclaw
A modular, skill-based autonomous Security Operations Center (SOC) agent that monitors OpenSearch/Elasticsearch data, builds RAG-based behavioral…
 muhammednihalmp/google-chrome-zero-day
CVE-2025-6554
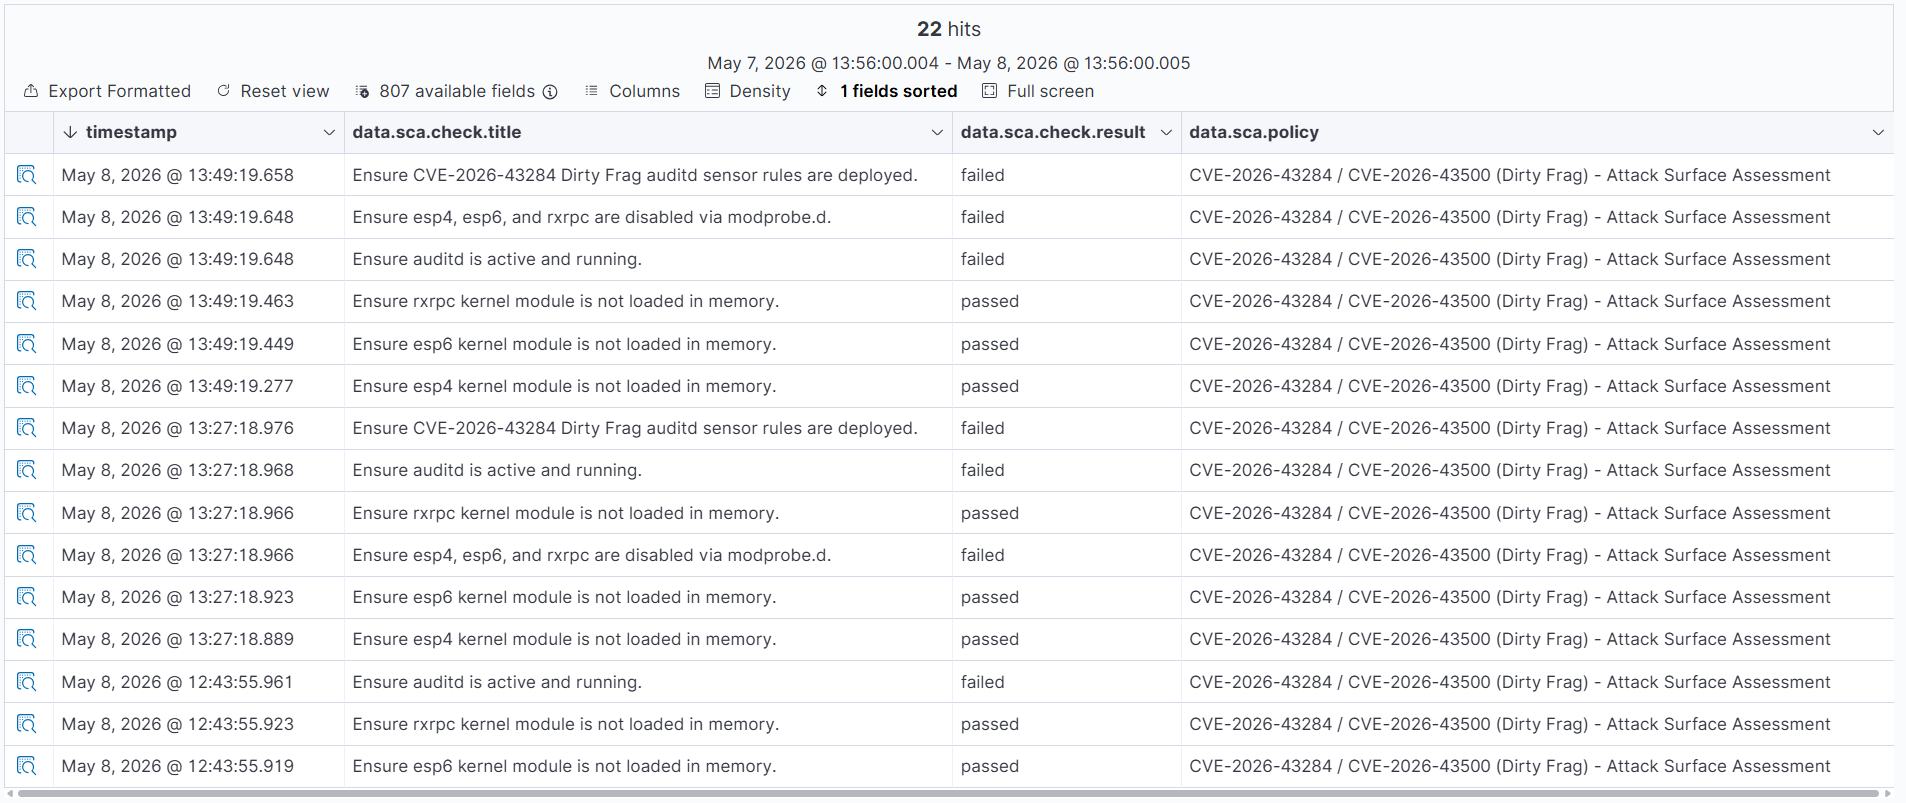 mym0us3r/dirty-frag-detection-with-wazuh-4.14.4
Wazuh 4.14.4 detection rules for CVE-2026-43284 / CVE-2026-43500 (Dirty Frag) - Linux Local Privilege Escalation via page cache write
 g0thamrabb1t/cve-2026-43284-dirtyfrag-detection
Lab validation report and detection artifacts for CVE-2026-43284 (DirtyFrag) Linux LPE. Provides auditd telemetry, event correlation rules, and…
 rvazarkar/antipwny
A host based IDS written in C# Targetted at Metasploit
 rickgeex/cve-2025-5777-citrixbleed
CitrixBleed-2 (CVE-2025-5777) – proof-of-concept exploit for NetScaler ADC/Gateway “memory bleed”
 22imer/cve-2014-0160
Dockerized training lab for exploiting Heartbleed (CVE-2014-0160) via TLS heartbeat to leak nginx memory, plus Snort rule to detect attacks.