
network-attack-detection
 lucadibello/network-attack-detection
Advanced detection of port scanning, DoS and malware attacks using Machine Learning techniques
anomaly-detectioneducationinformation-gathering+5
13
lucadibello/network-attack-detectionAdvanced detection of port scanning, DoS and malware attacks using Machine Learning techniques
 umidguluzada/cyberdefense-lab
A complete Blue Team Cybersecurity Lab featuring pfSense, Suricata, and ELK Stack for network monitoring and threat detection.
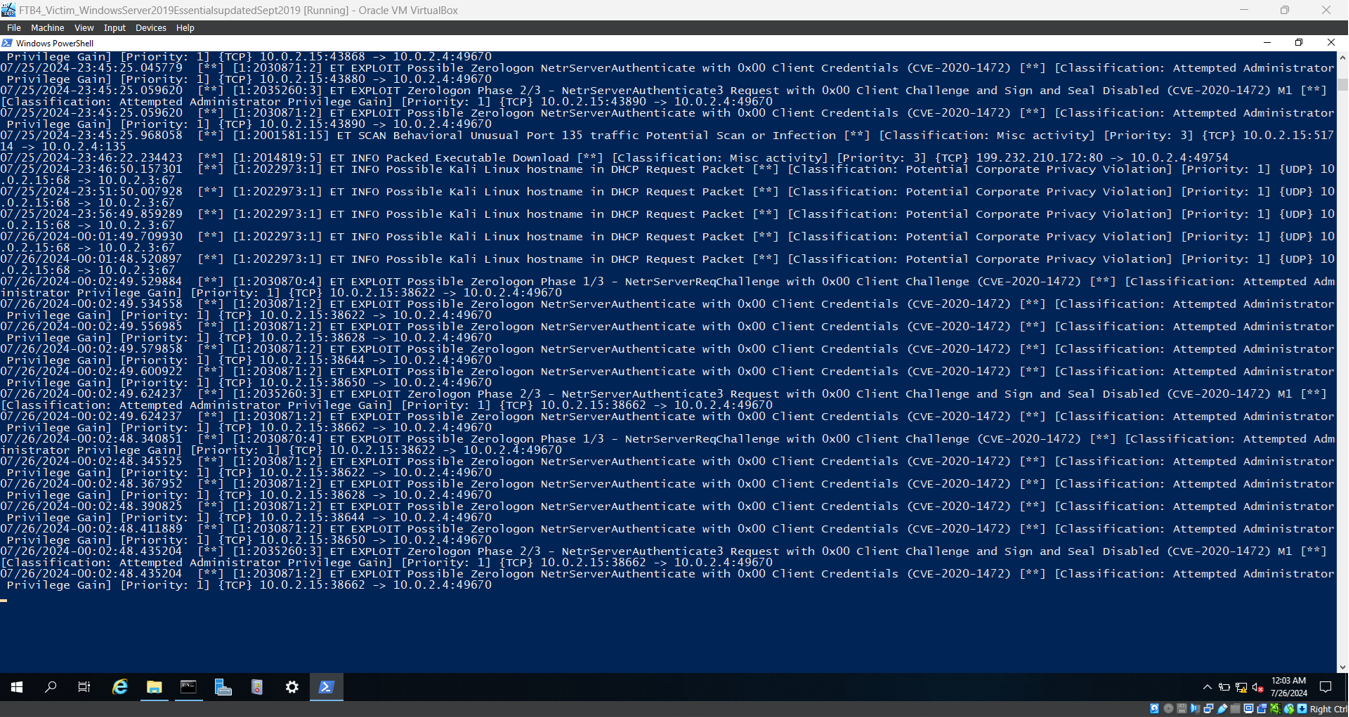 tdevworks/cve-2020-1472-zerologon-demo-detection-mitigation
Educational demo of CVE-2020-1472 (ZeroLogon) detection using Windows Event Logs and Suricata IDS, plus mitigation via Windows Updates. Includes…
 hpfeeds/hpfeeds
Honeynet Project generic authenticated datafeed protocol
 owasp/honeypot-project
Deploy web honeypots to capture emerging attack data, analyze ModSecurity audit logs via ELK, and share threat intelligence with MISP for…
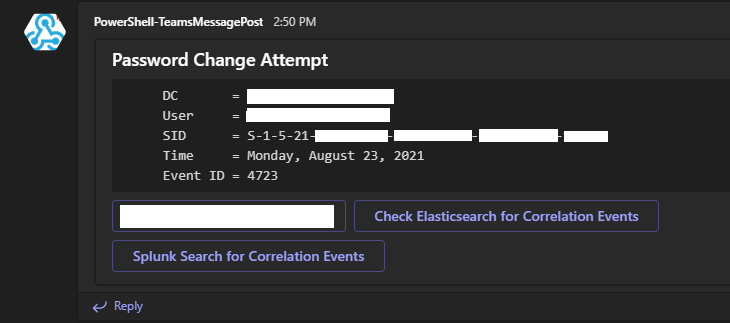 osbornepro/btps-secpack
PowerShell-based security toolkit for small-to-medium enterprises, providing automated alerts, Active Directory hardening, Windows Event Forwarding,…
 v1d1an/s1em
This project is a SIEM with SIRP and Threat Intel, all in one.
 efforg/rayhunter
Rust tool to detect cell site simulators on an orbic mobile hotspot
 spanwich/sel4-ics-gateway-demo
Defensive security demo: seL4 microkernel gateway protecting vulnerable ICS from CVE-2019-14462
 harshiys/cve-2007-2447-exploitation-siem-detection-lab
Isolated AD/Linux attack lab: exploited CVE-2007-2447 via Metasploit, detected with Wazuh SIEM mapped to MITRE ATT&CK (T1190, T1059)
 salo-404/firewall
🔒 Spring4Shell Firewall Defense — Cybersecurity Incident Simulation This project is part of a Cybersecurity Job Simulation I completed in August…
 owasp/securetea-project
The OWASP SecureTea Project provides a one-stop security solution for various devices (personal computers / servers / IoT devices)

 itzmeshervin/siem-dashboard
A lightweight, real-time Security Information and Event Management (SIEM) dashboard built using Streamlit. It collects system logs, detects USB and…
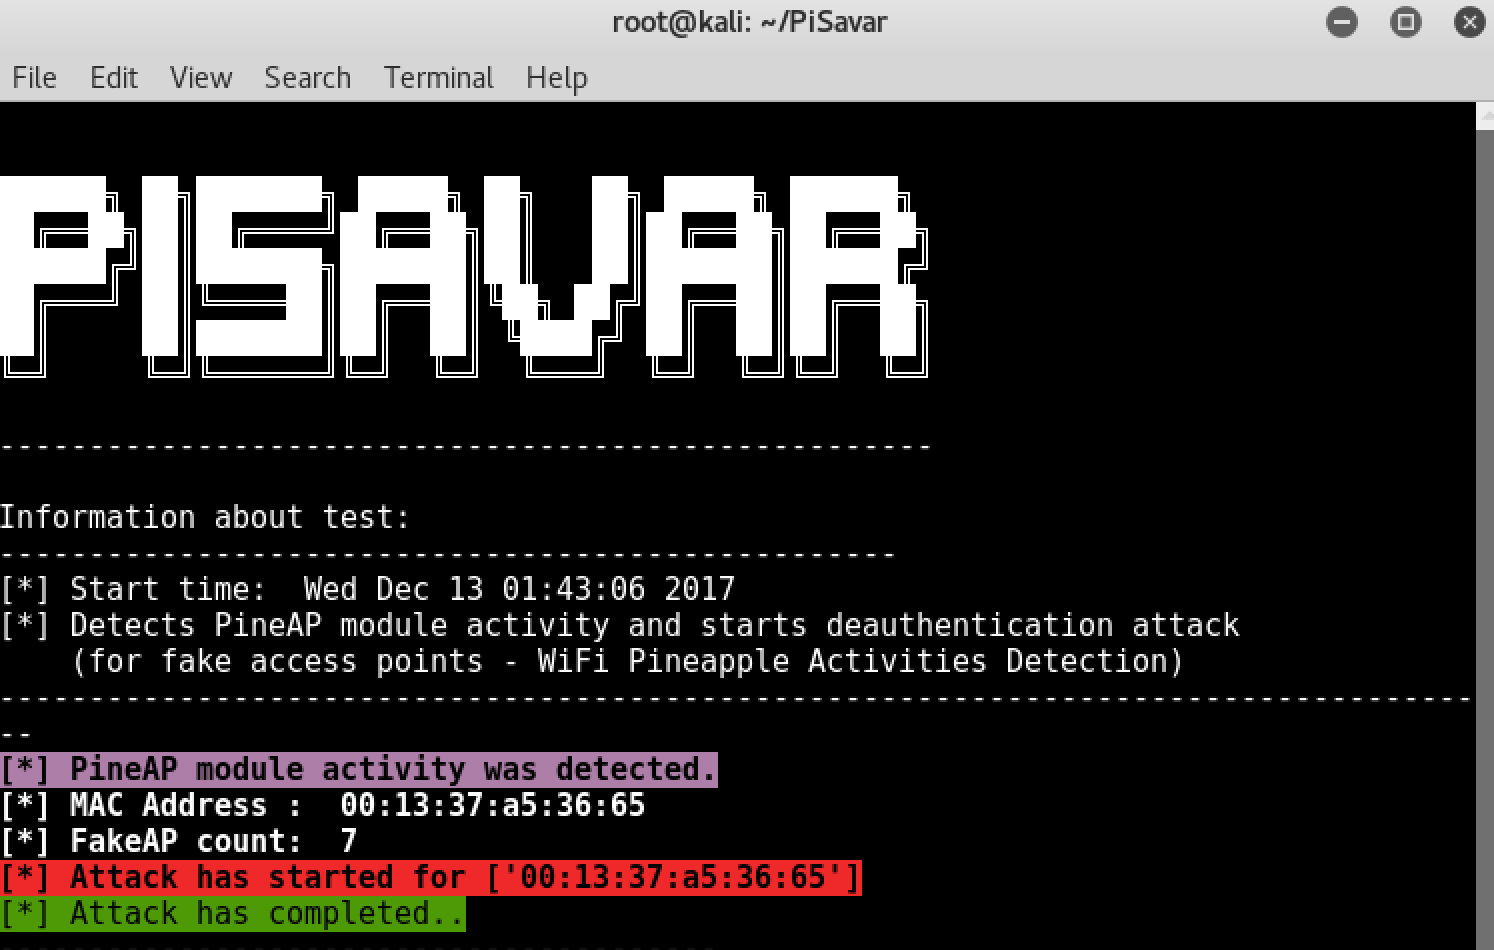 wipi-hunter/pisavar
📡 🍍Detects activities of PineAP module and starts deauthentication attack (for fake access points - WiFi Pineapple Activities Detection)
 alloysecuregroup/phantomfs
Windows honeypot using ProjFS to project decoy files that trigger Event Log and desktop alerts when accessed, with SMB remote session logging for…
 spiderlabs/owasp-modsecurity-crs
OWASP ModSecurity Core Rule Set (CRS) Project (Official Repository)
 theflink/hunt-weird-imageloads
Small tool to play with IOCs caused by Imageload events
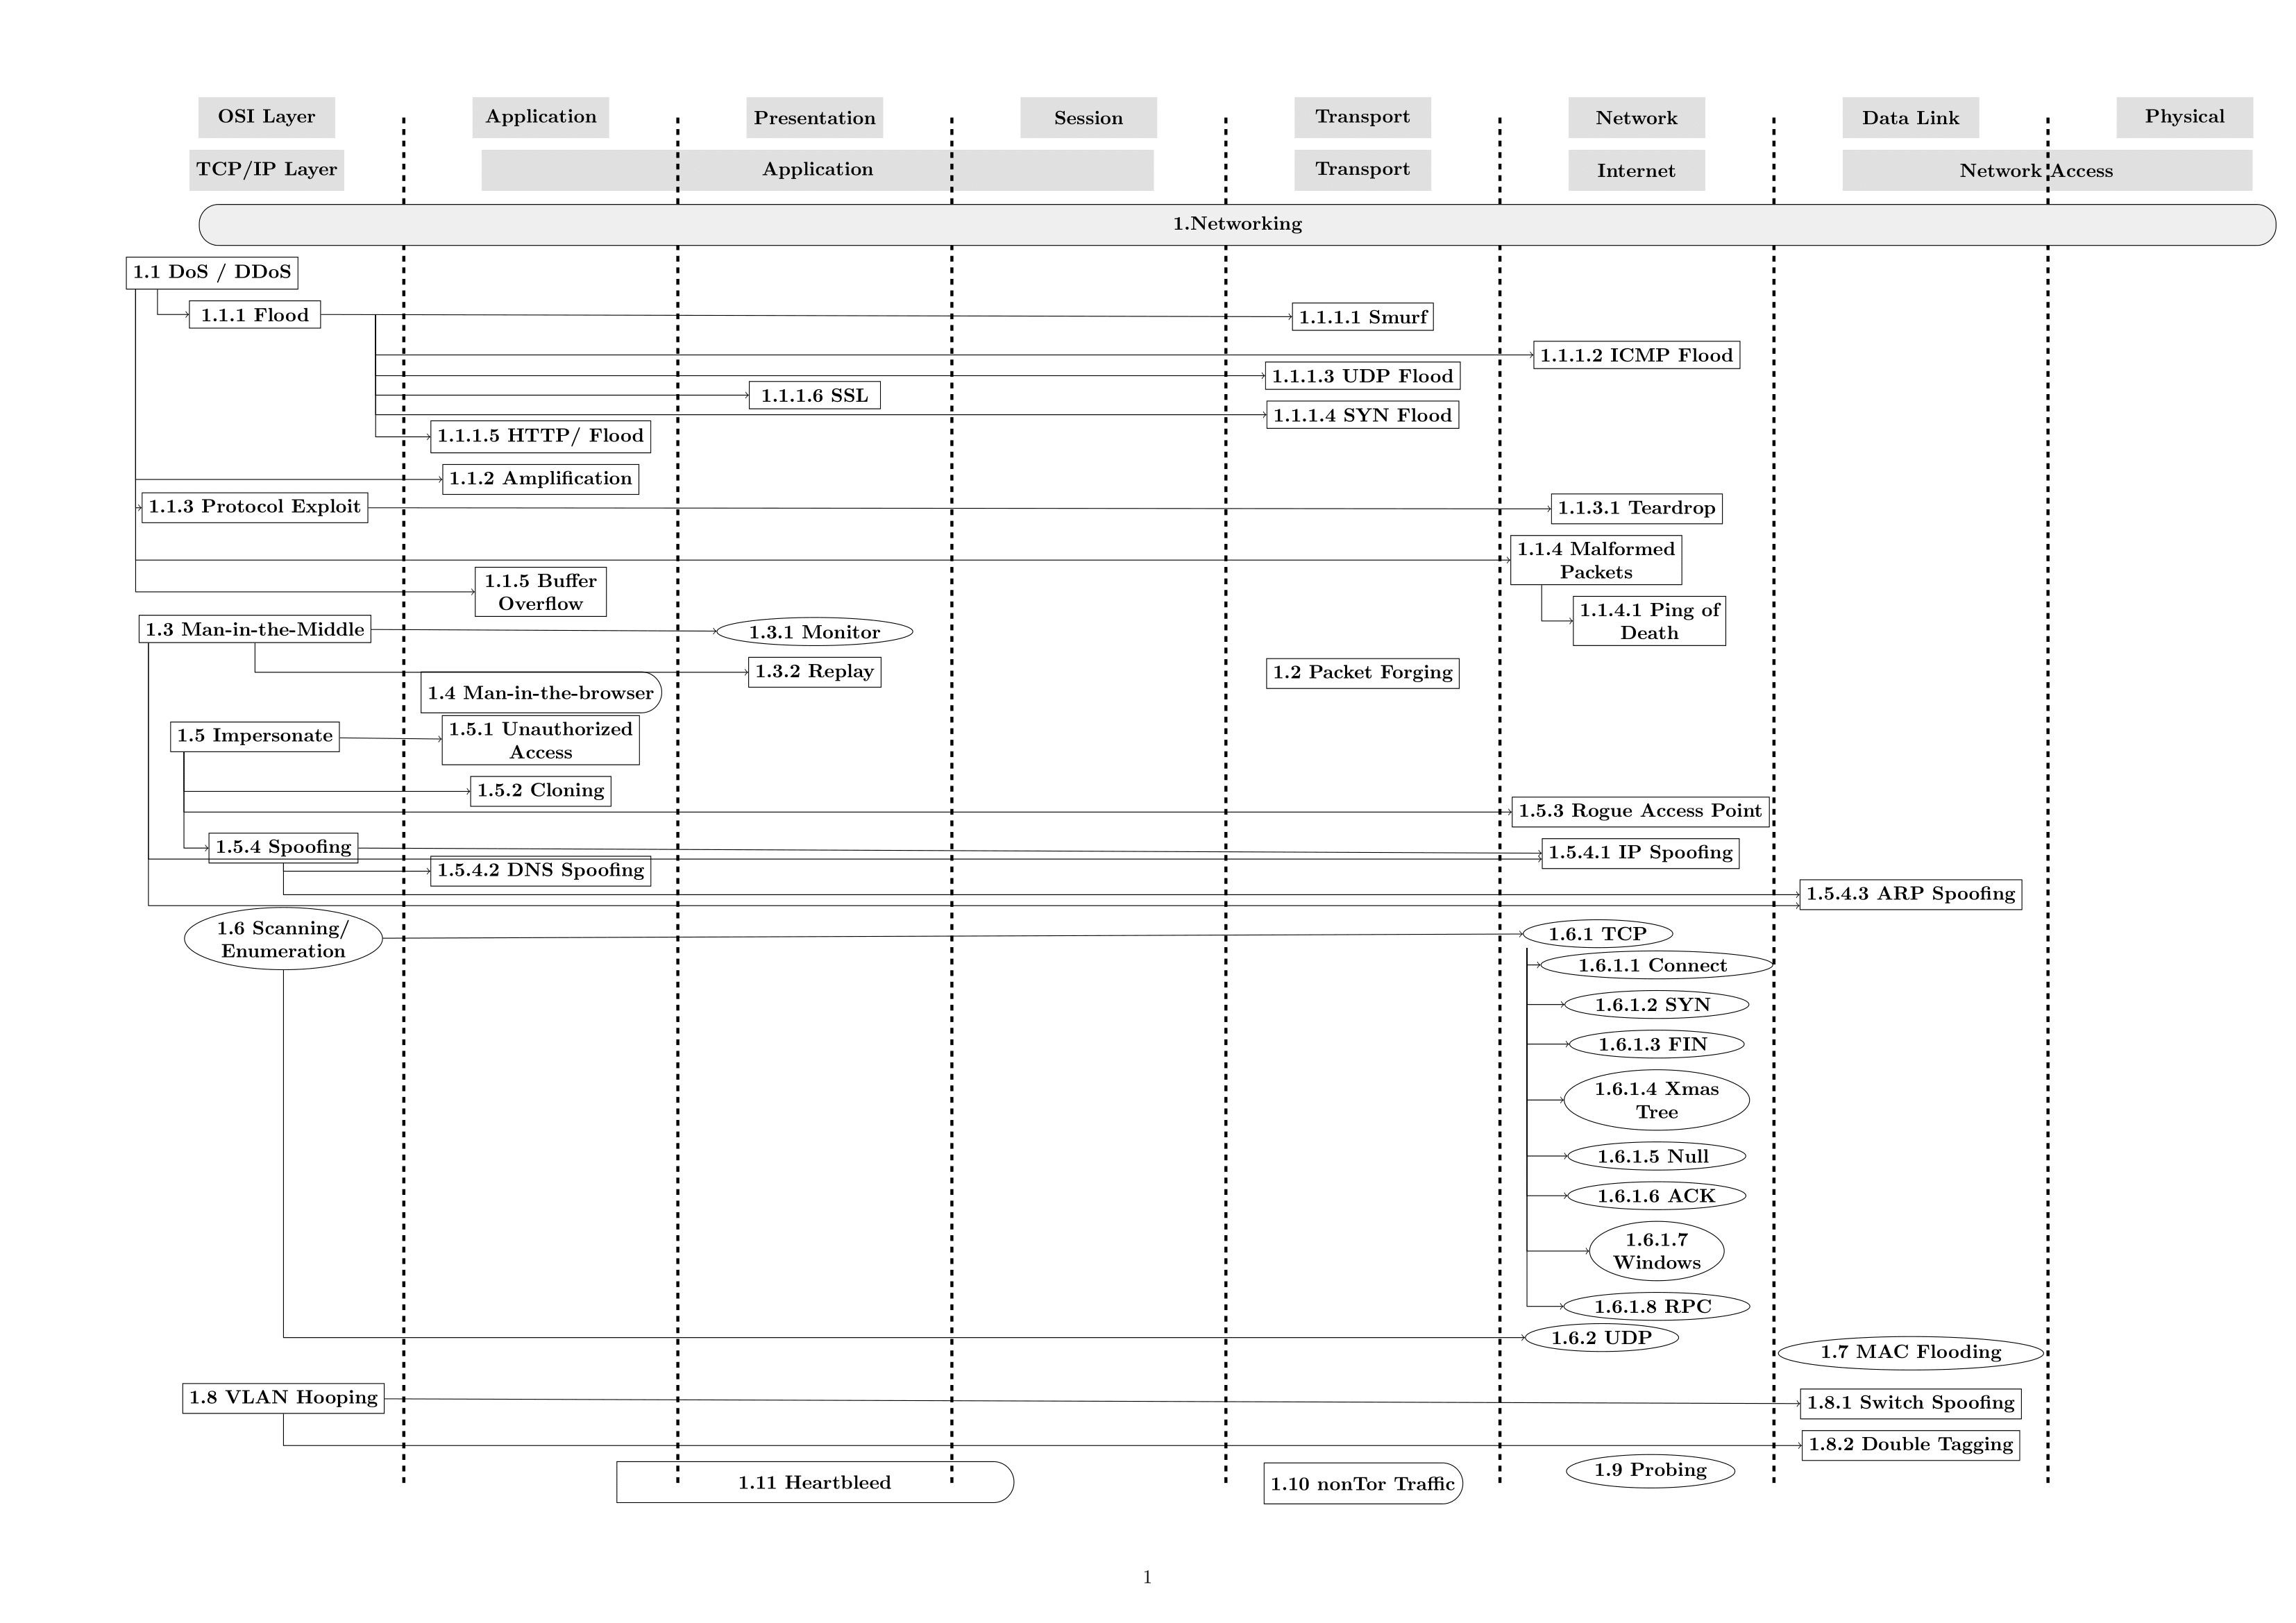 abertaymachinelearninggroup/network-threats-taxonomy
Machine Learning based Intrusion Detection Systems are difficult to evaluate due to a shortage of datasets representing accurately network traffic…