

wazuh
 wazuh/wazuh
Open-source XDR and SIEM platform for threat detection, log analysis, file integrity monitoring, vulnerability assessment, and compliance management…
anomaly-detectionanti-botcloud-security+12
wazuh/wazuhOpen-source XDR and SIEM platform for threat detection, log analysis, file integrity monitoring, vulnerability assessment, and compliance management…
 security-onion-solutions/securityonion
Open-source security monitoring platform for threat hunting, intrusion detection, log management, incident response, and endpoint visibility with…
 thinkst/opencanary
Low-resource honeypot that emulates common network services to detect post-breach attacker activity, with extensible protocol modules and…
 d3vhex/sentora
An open-source, self-hosted AI-powered SIEM, EDR and SOAR platform for modern security operations.
 duggytuxy/syswarden
Host-local Linux security orchestrator enforcing nftables policy with HIDS/HIPS telemetry, bounded threat-intelligence feeds, out-of-band WAAP log…
 dougburks/so-crates
SO-CRATES: Security Onion Containerized Rapid Analysis of Threats, Evil, and Sus!
 digitalruby/ipban
Automated IP ban service that detects failed login attempts from event logs and files, blocking attackers on Windows and Linux via firewall…
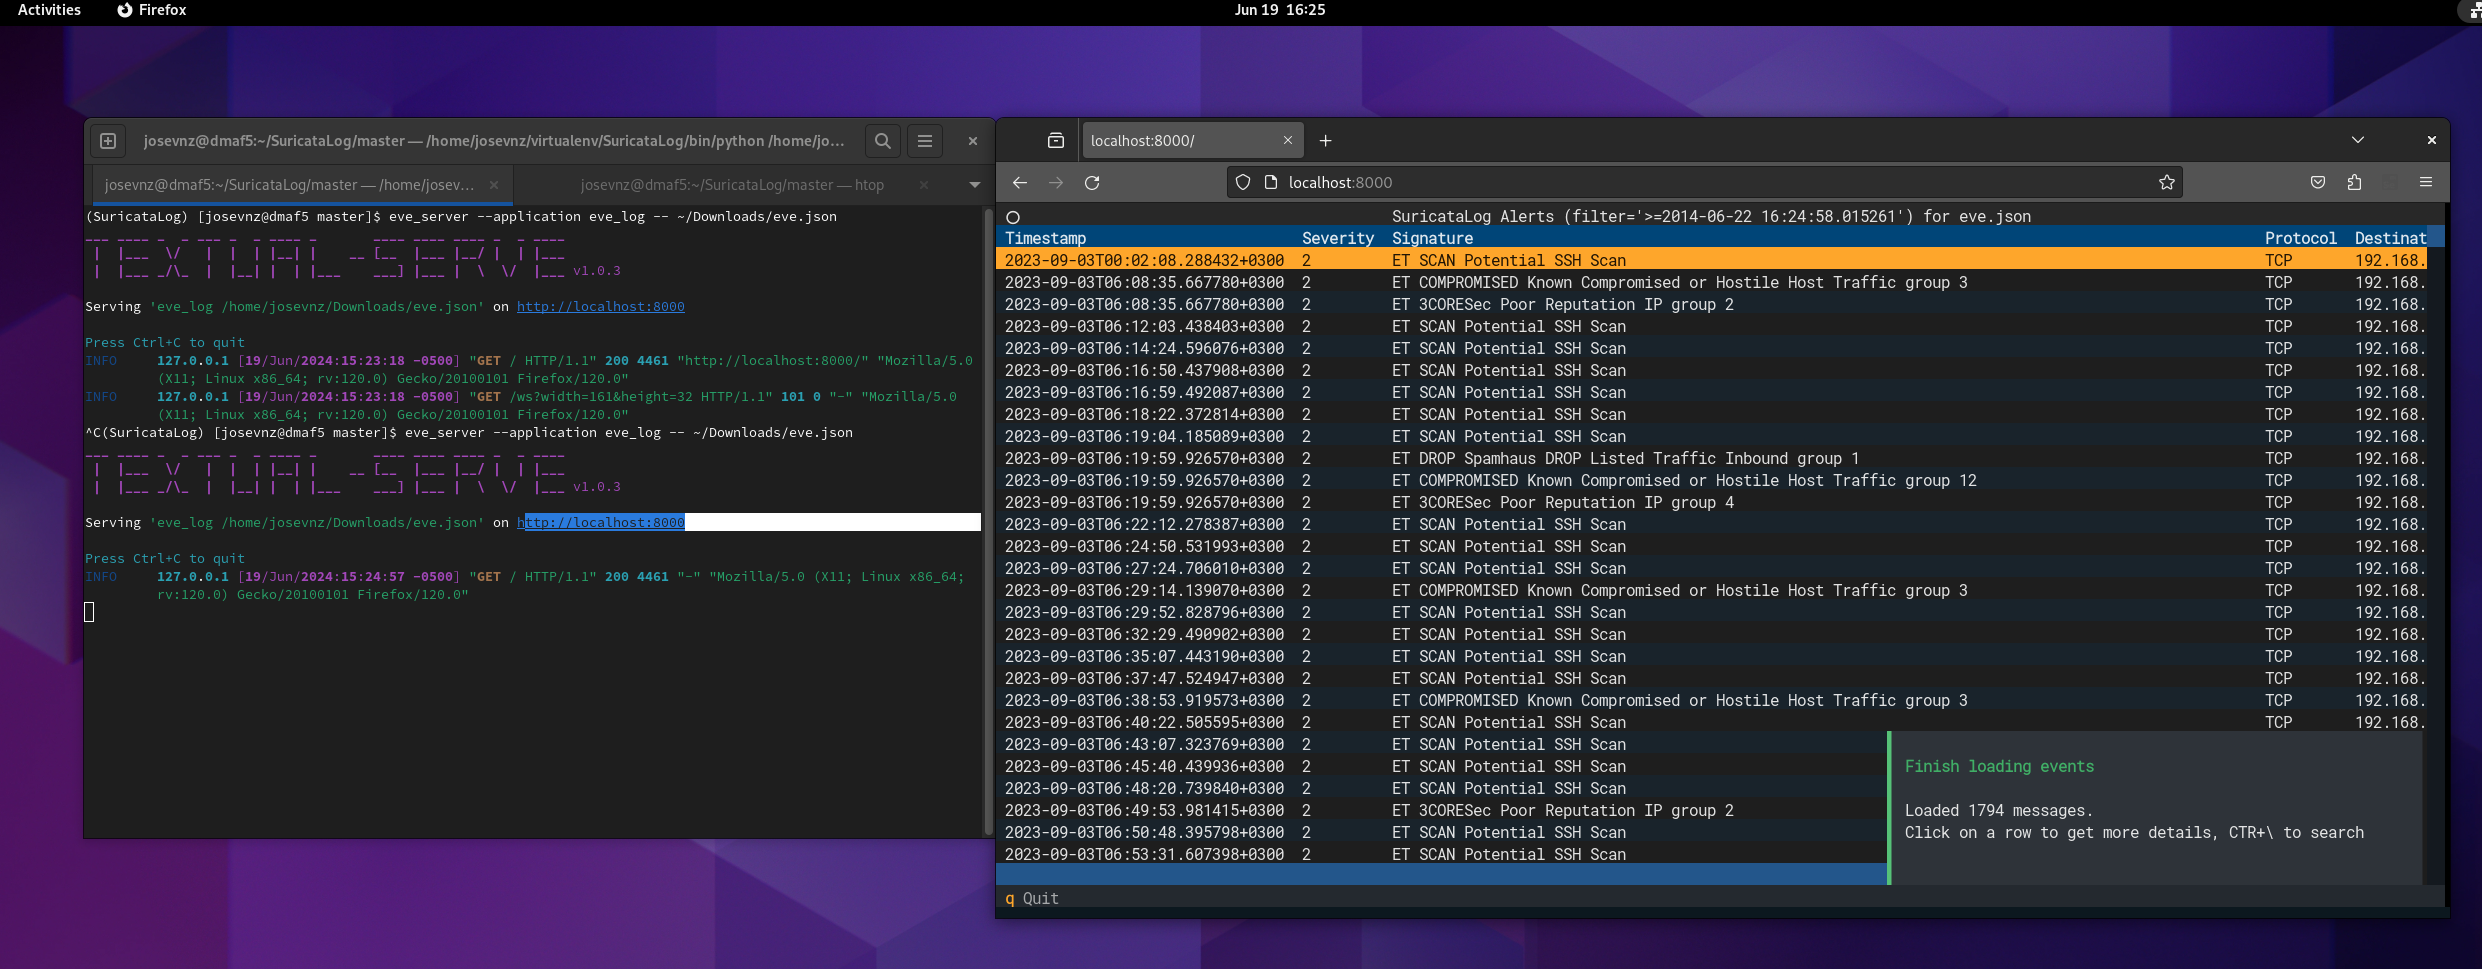 josevnz/suricatalog
Parse, filter, and visualize Suricata eve.json logs with CLI tools for alerts, flows, DNS, and payloads. Includes a tutorial for learning Suricata…
 sonitbahl/sshintel
Self-contained SSH honeypot for capturing attacker interactions and turning them into structured security intelligence.
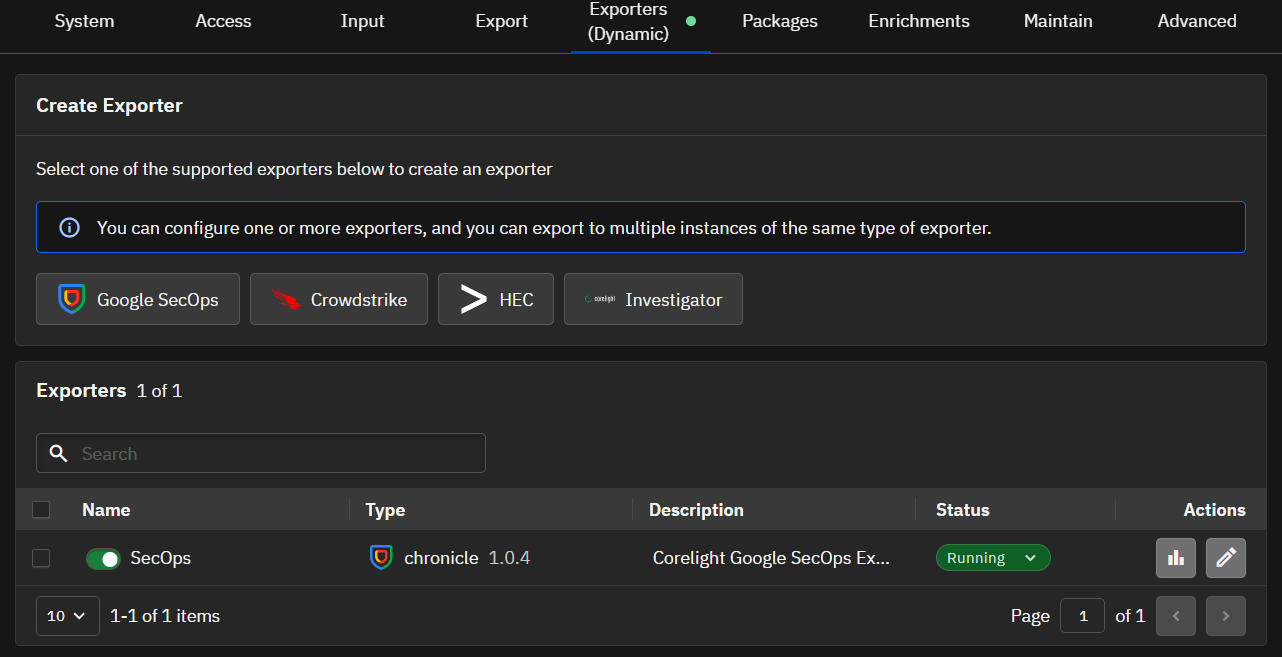 corelight/corelightforsecops
Chronicle parser for CORELIGHT and related information.
 0x4d31/awesome-threat-detection
Curated list of threat detection and hunting resources: detection rules, SIEM and log analysis tools, endpoint/network monitoring, datasets,…
 pisut4152/sigma-rule-for-cve-2021-22005-scanning-activity
Sigma rule for detecting scanning activity targeting CVE-2021-22005, enabling threat detection and log-based intrusion analysis.

 graylog2/graylog2-server
Centralized log management platform for collecting, indexing, and analyzing streaming logs, with alerting and event correlation for security…
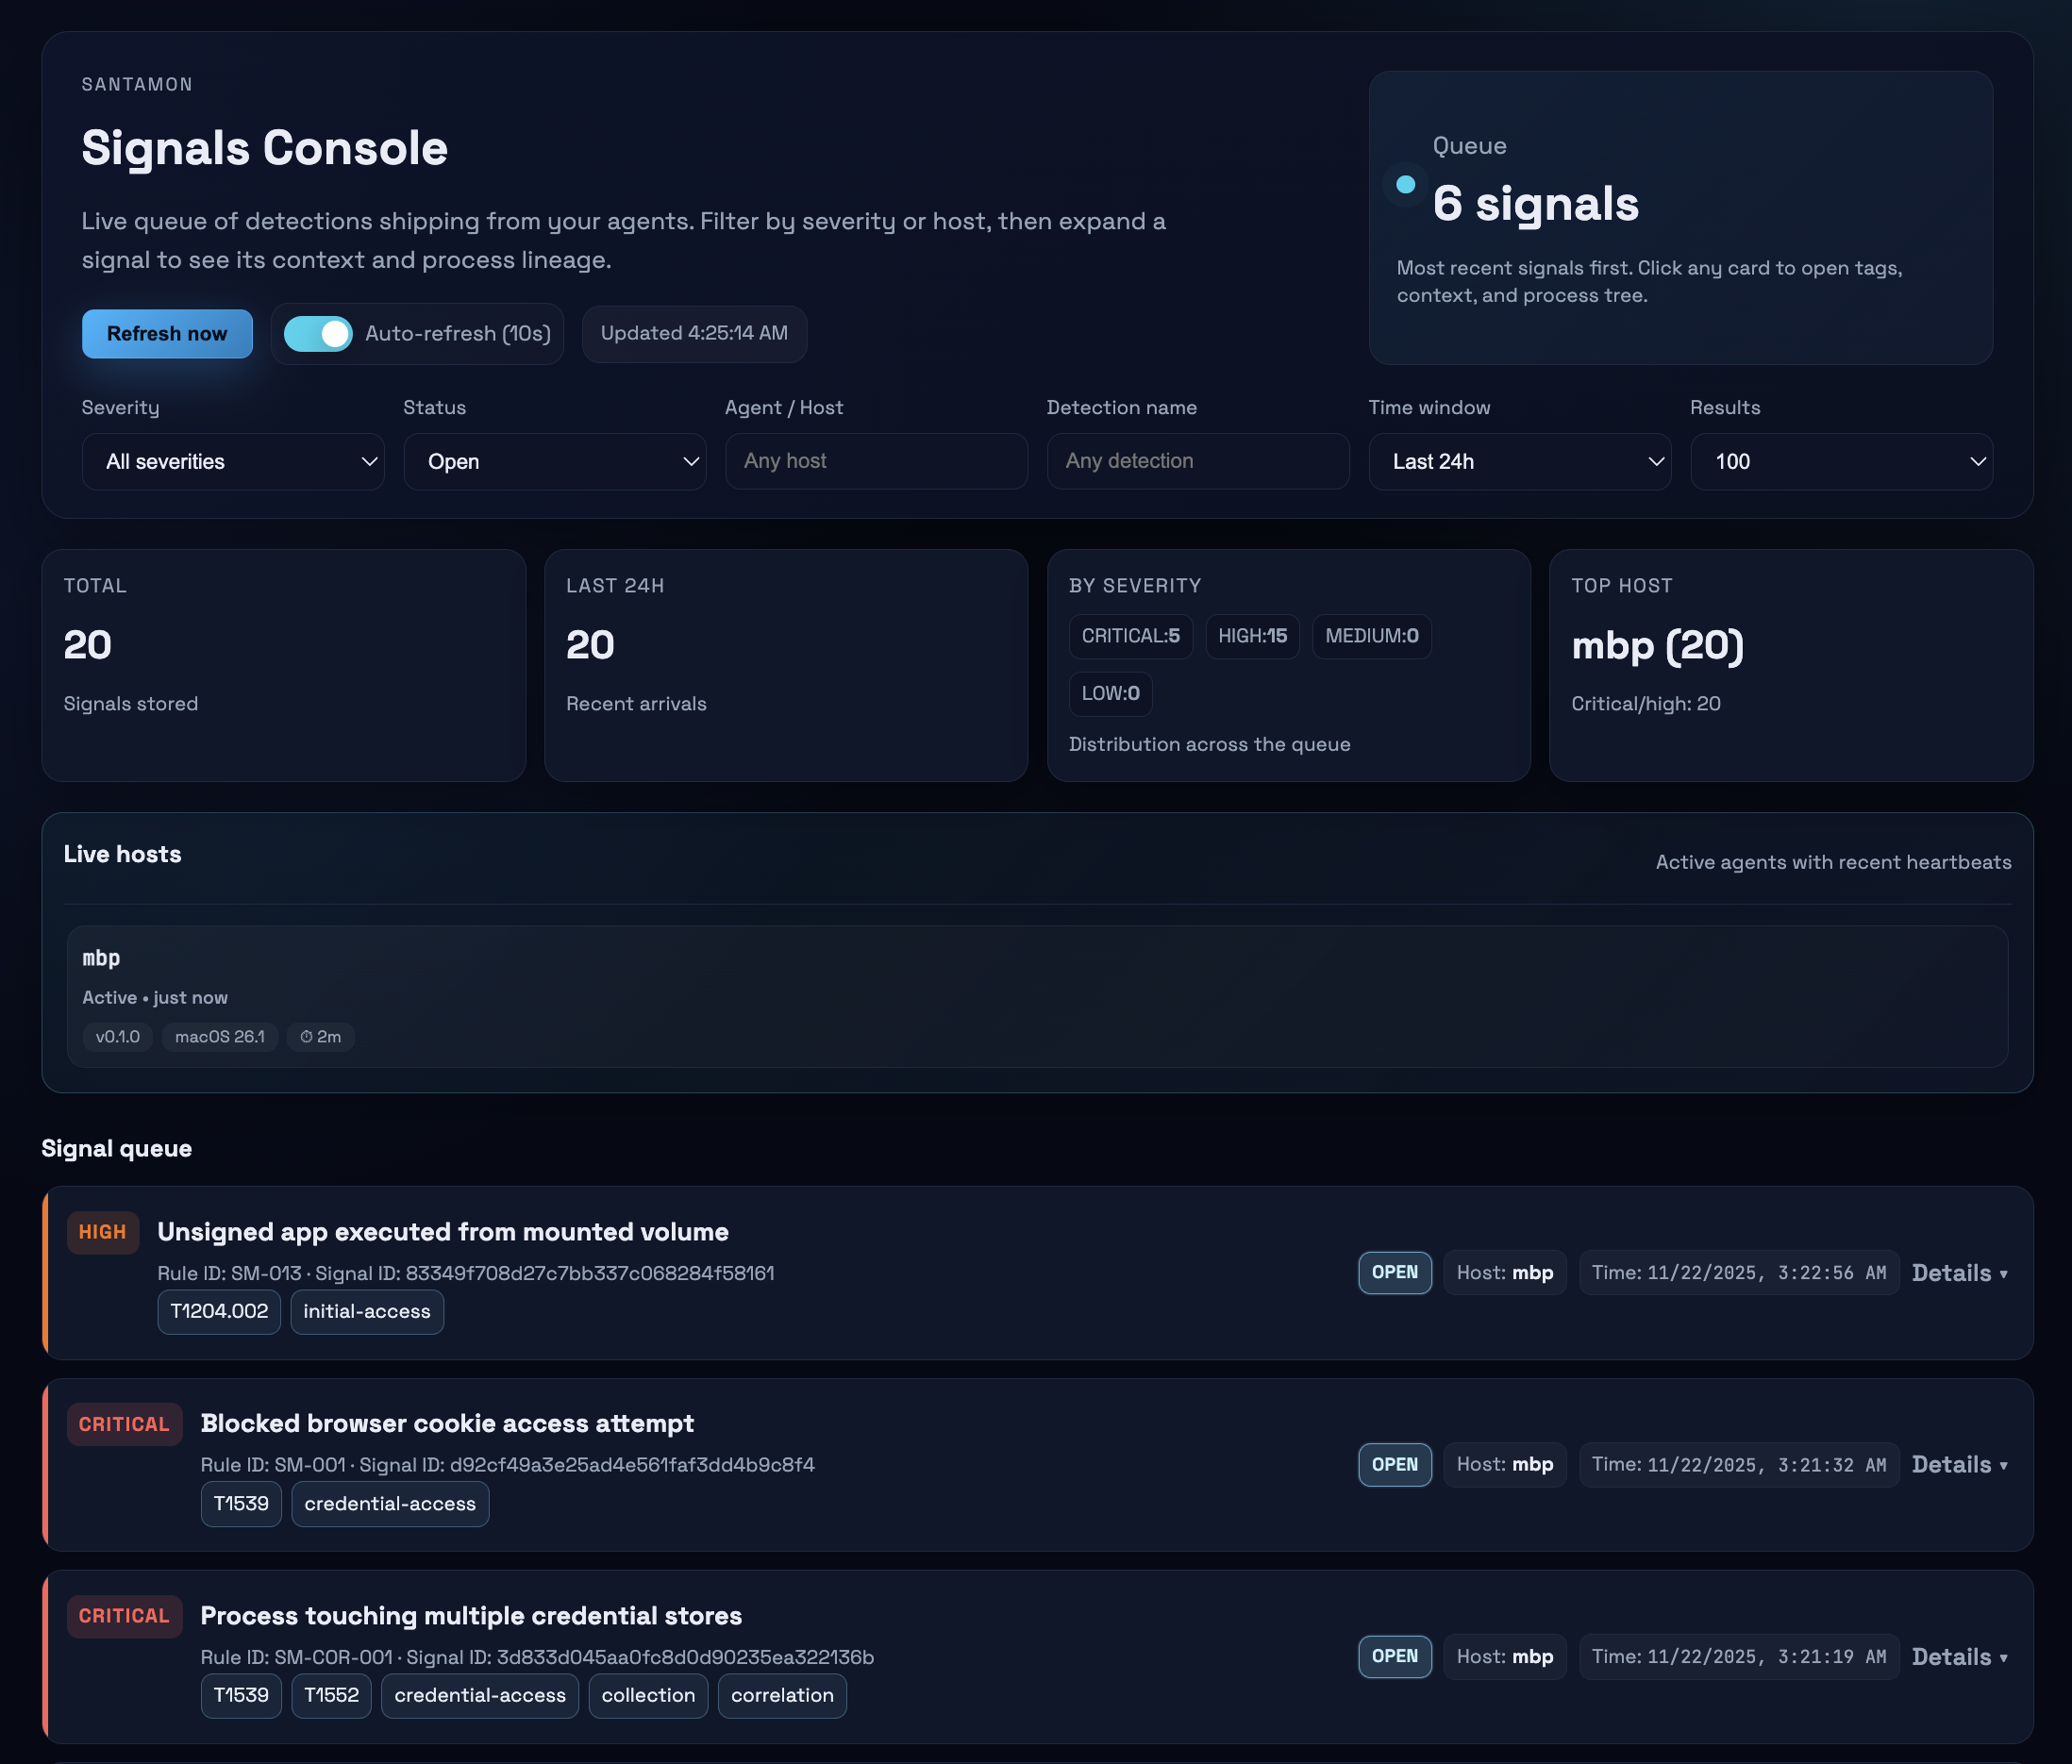 0x4d31/santamon
Lightweight macOS detection agent built on Santa’s Endpoint Security telemetry.
 linux-audit/audit-kernel
GitHub mirror of the Linux Kernel's audit repository
 mthbernardes/artlas
Apache Real Time Logs Analyzer System
 rabobank-cdc/dettect
Detect Tactics, Techniques & Combat Threats