
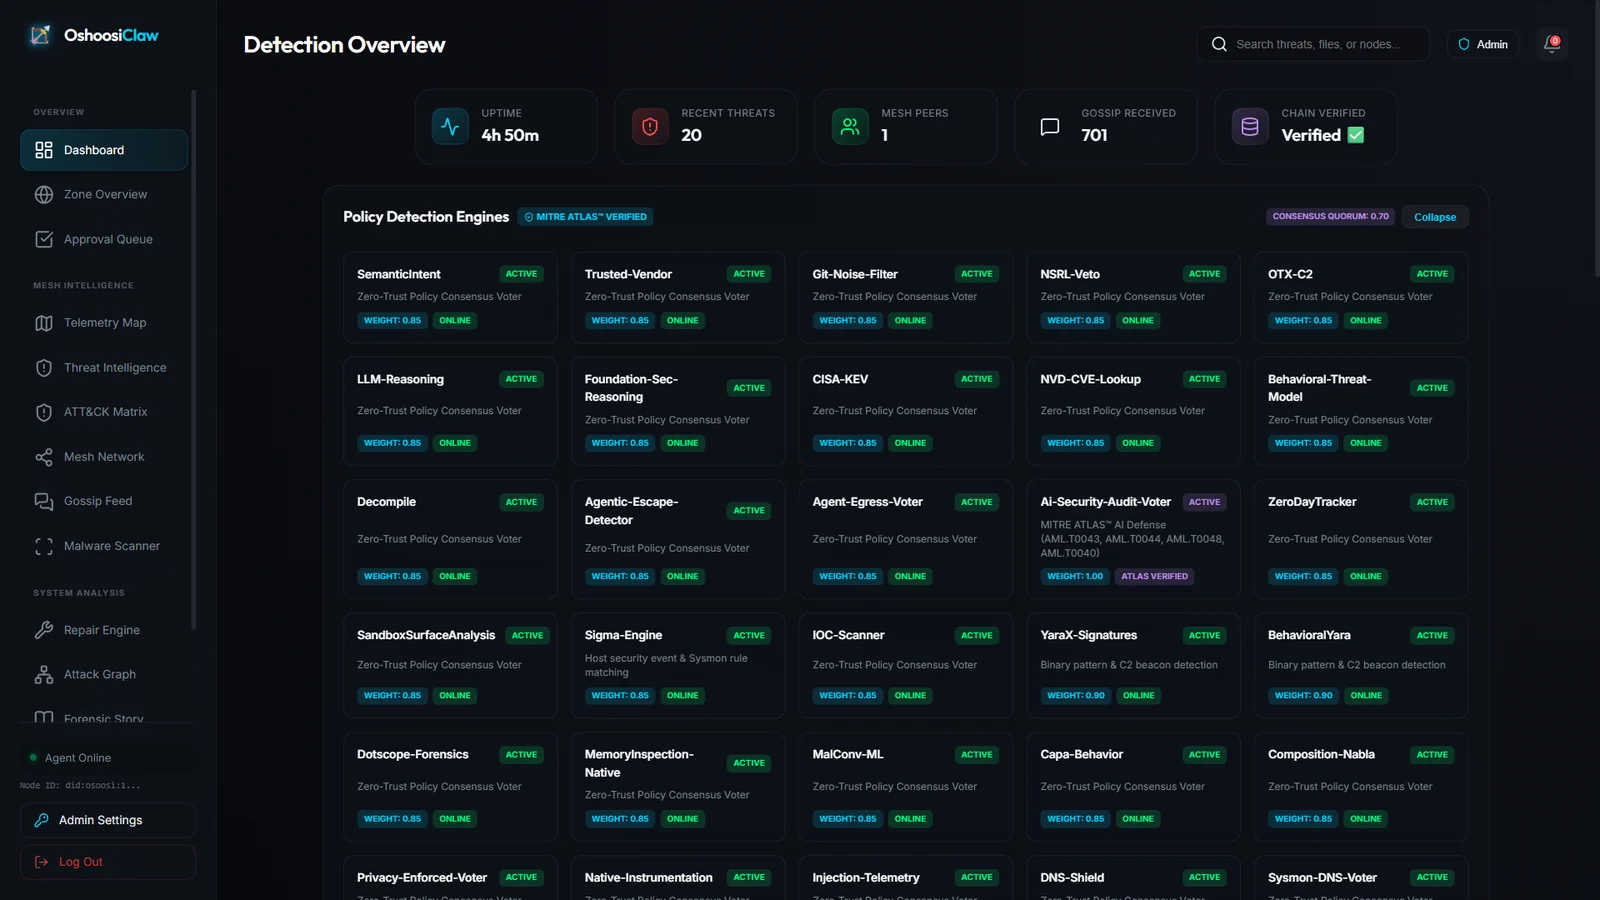
OshoosiClaw
 oyesanyf/oshoosiclaw
Autonomous Rust endpoint security agent combining Ring-0 Windows driver and Linux eBPF pre-execution blocking, YARA detection, MITRE ATT&CK mapping,…
ai-securityanomaly-detectioncommand-and-control+8
6
oyesanyf/oshoosiclawAutonomous Rust endpoint security agent combining Ring-0 Windows driver and Linux eBPF pre-execution blocking, YARA detection, MITRE ATT&CK mapping,…
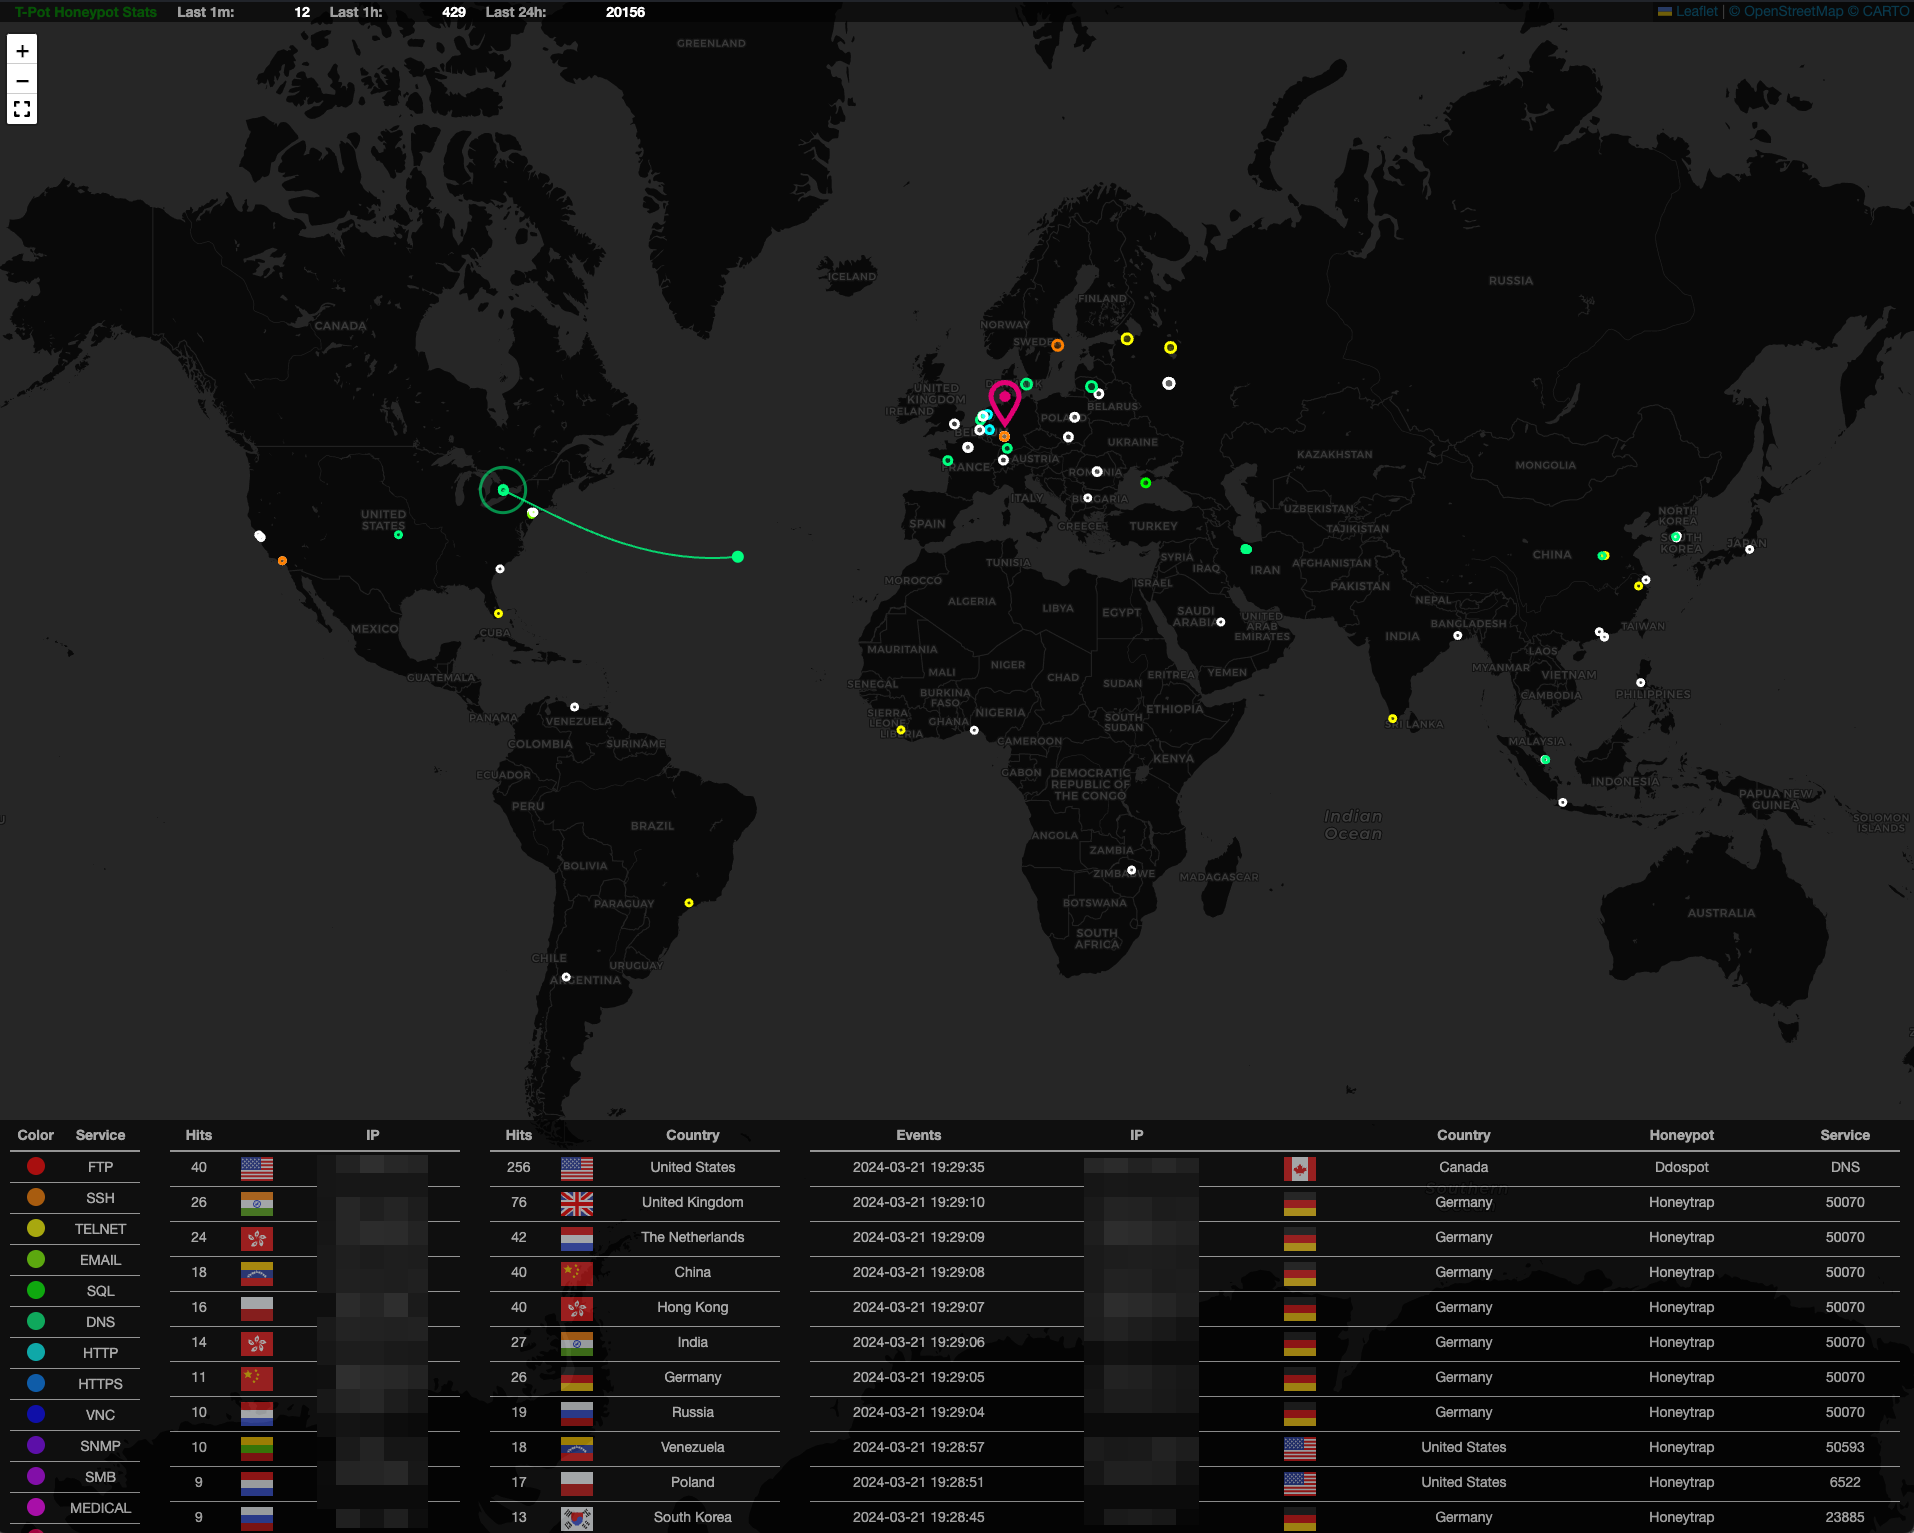 telekom-security/tpotce
🍯 T-Pot - The All In One Multi Honeypot Platform 🐝
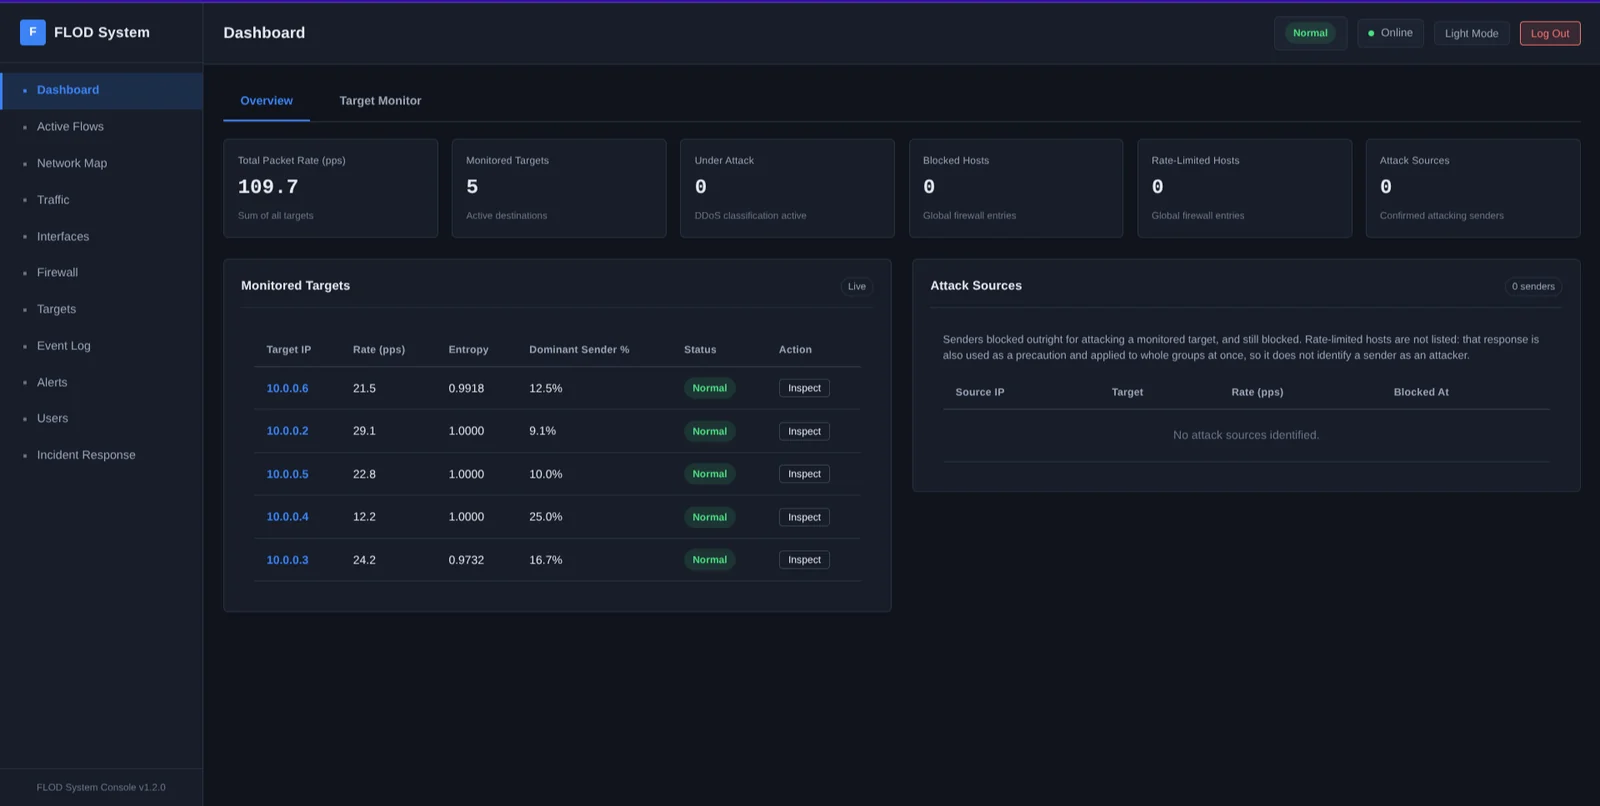 devinblack001/ddos-reduction-system
Adaptive two-stage Layer 4 DDoS mitigation gateway using behavioral traffic analysis, Random Forest classification, and kernel-level ipset/iptables…
 foxio-llc/ja4
JA4+ is a suite of network fingerprinting standards
 neo23x0/loki
IOC and YARA-based scanner for detecting indicators of compromise via file name regex, YARA signatures, hash matching, and C2 back-connect checks on…
 joseluispino/hardstop
Reference implementation for "Hard Stop: Kernel-Level Preemption and Containment for Rogue Agentic Execution". Out-of-band Epistemic Andon Cord,…
 microlaser/dns_watchdog_windows2
PowerShell script that monitors Windows DNS traffic via pktmon to detect poisoning, spoofing, rogue resolver responses, and gateway MAC changes,…
 digitalruby/ipban
Automated IP ban service that detects failed login attempts from event logs and files, blocking attackers on Windows and Linux via firewall…
 alphasoc/flightsim
A utility to safely generate malicious network traffic patterns and evaluate controls.
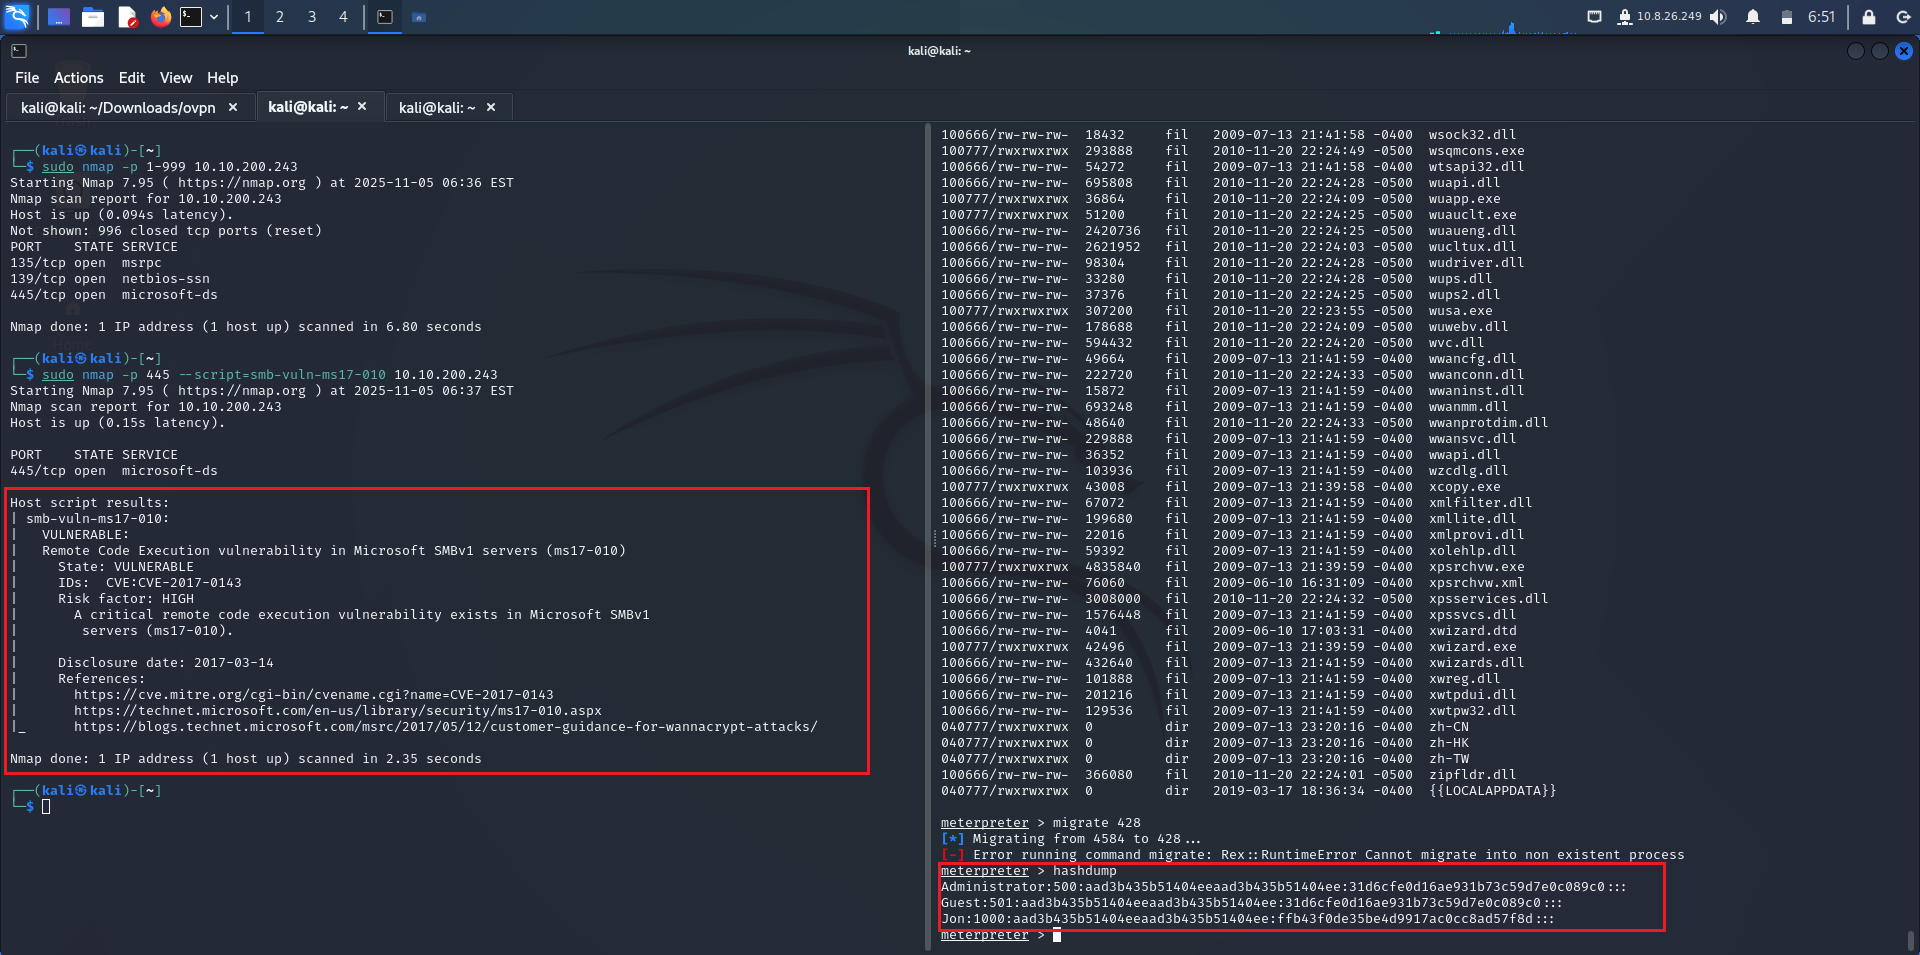 firetemple/blackash-cve-2017-0144
CVE-2017-0144
 wattocyber/detection-defense-library
Detection-engineering reference mapping Windows, cloud, container, identity, and ICS attack classes to Sigma rules, trust-boundary models, BYOVD…
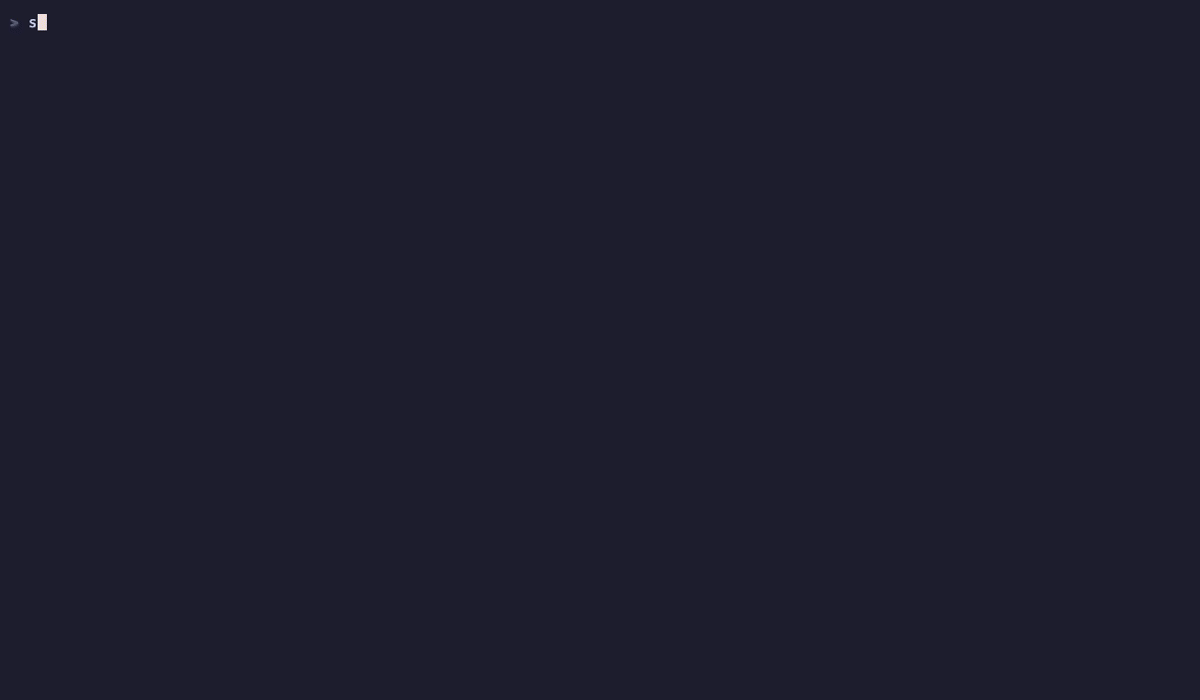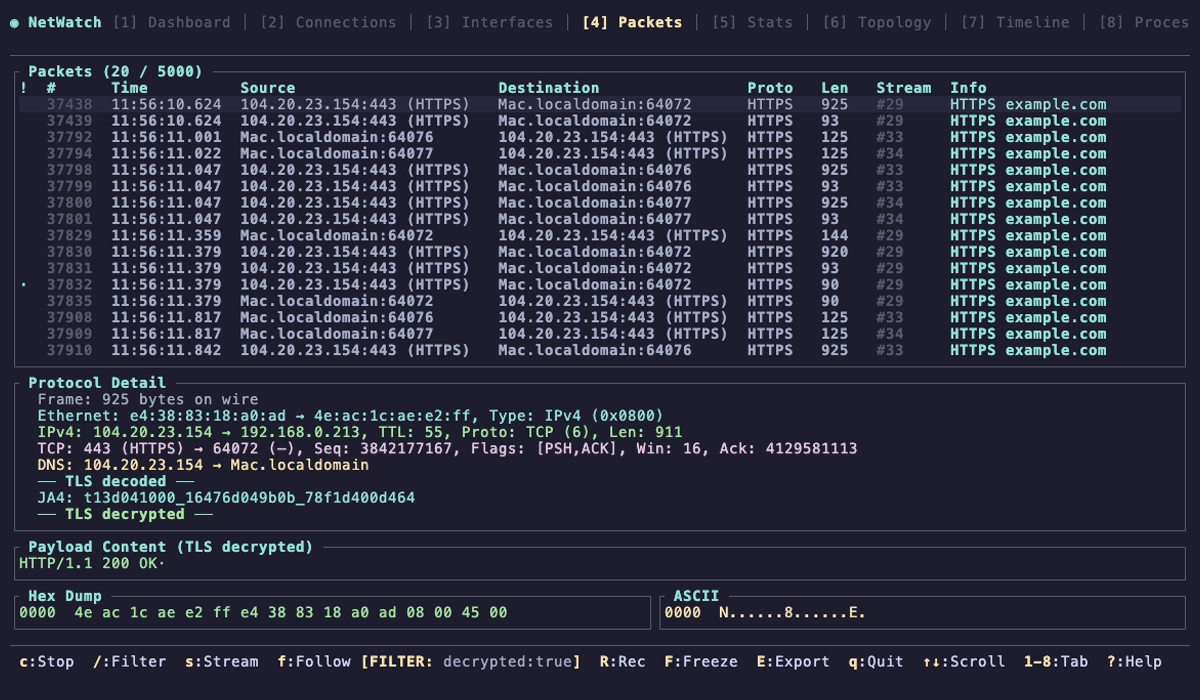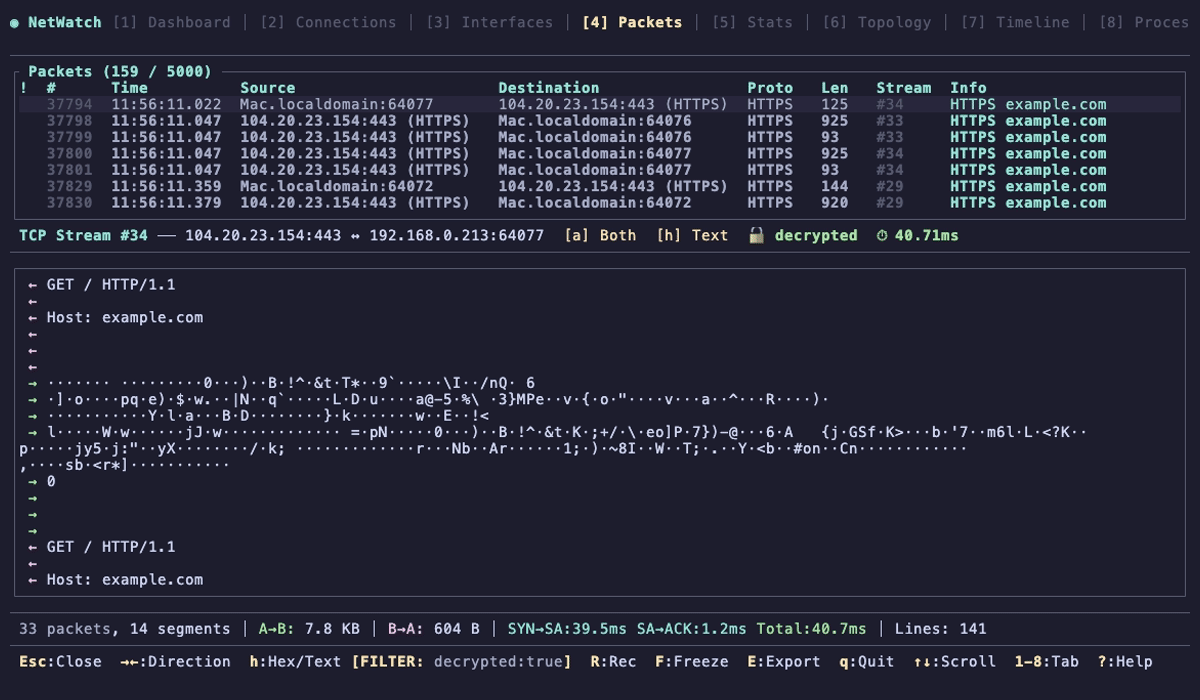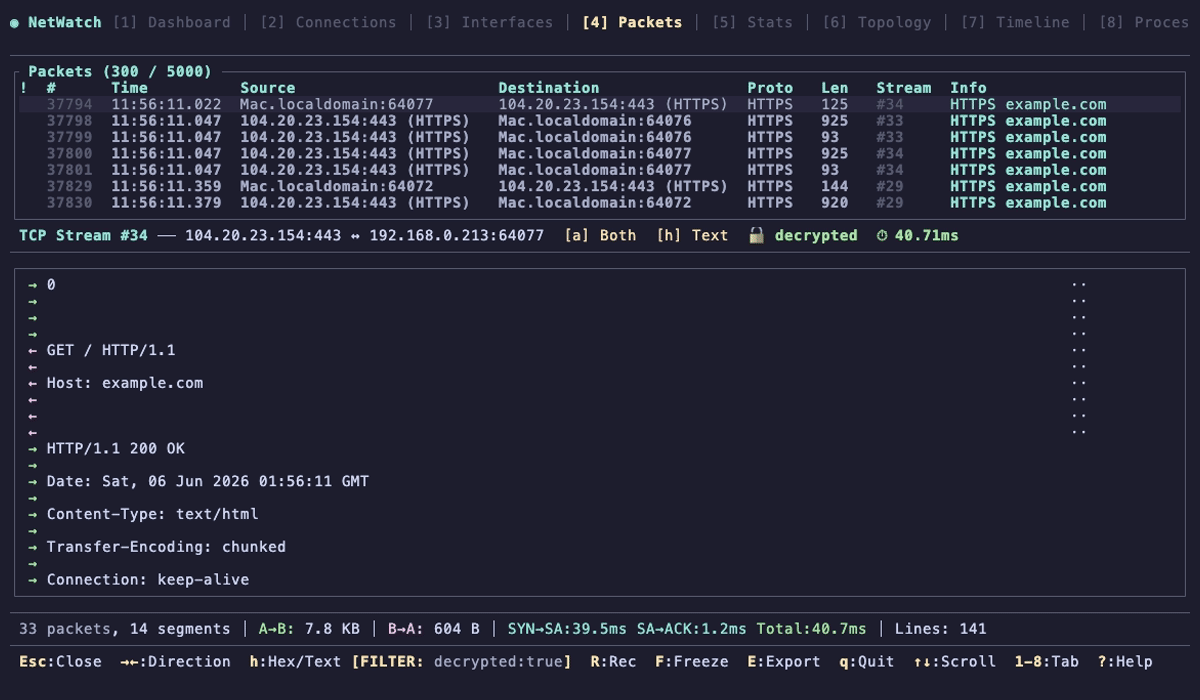 matthart1983/netwatch
Real-time network diagnostics in your terminal. One command, zero config, instant visibility.
 osquery/osquery
SQL powered operating system instrumentation, monitoring, and analytics.
 a2awais/threat-hunting
Curated collection of threat hunting and detection queries for CrowdStrike Falcon (CQL) and Microsoft Defender XDR (KQL), mapped to MITRE ATT&CK…
 0x4d31/awesome-threat-detection
Curated list of threat detection and hunting resources: detection rules, SIEM and log analysis tools, endpoint/network monitoring, datasets,…
 cyberdefenders/detectionlabelk
DetectionLabELK is a fork from DetectionLab with ELK stack instead of Splunk.
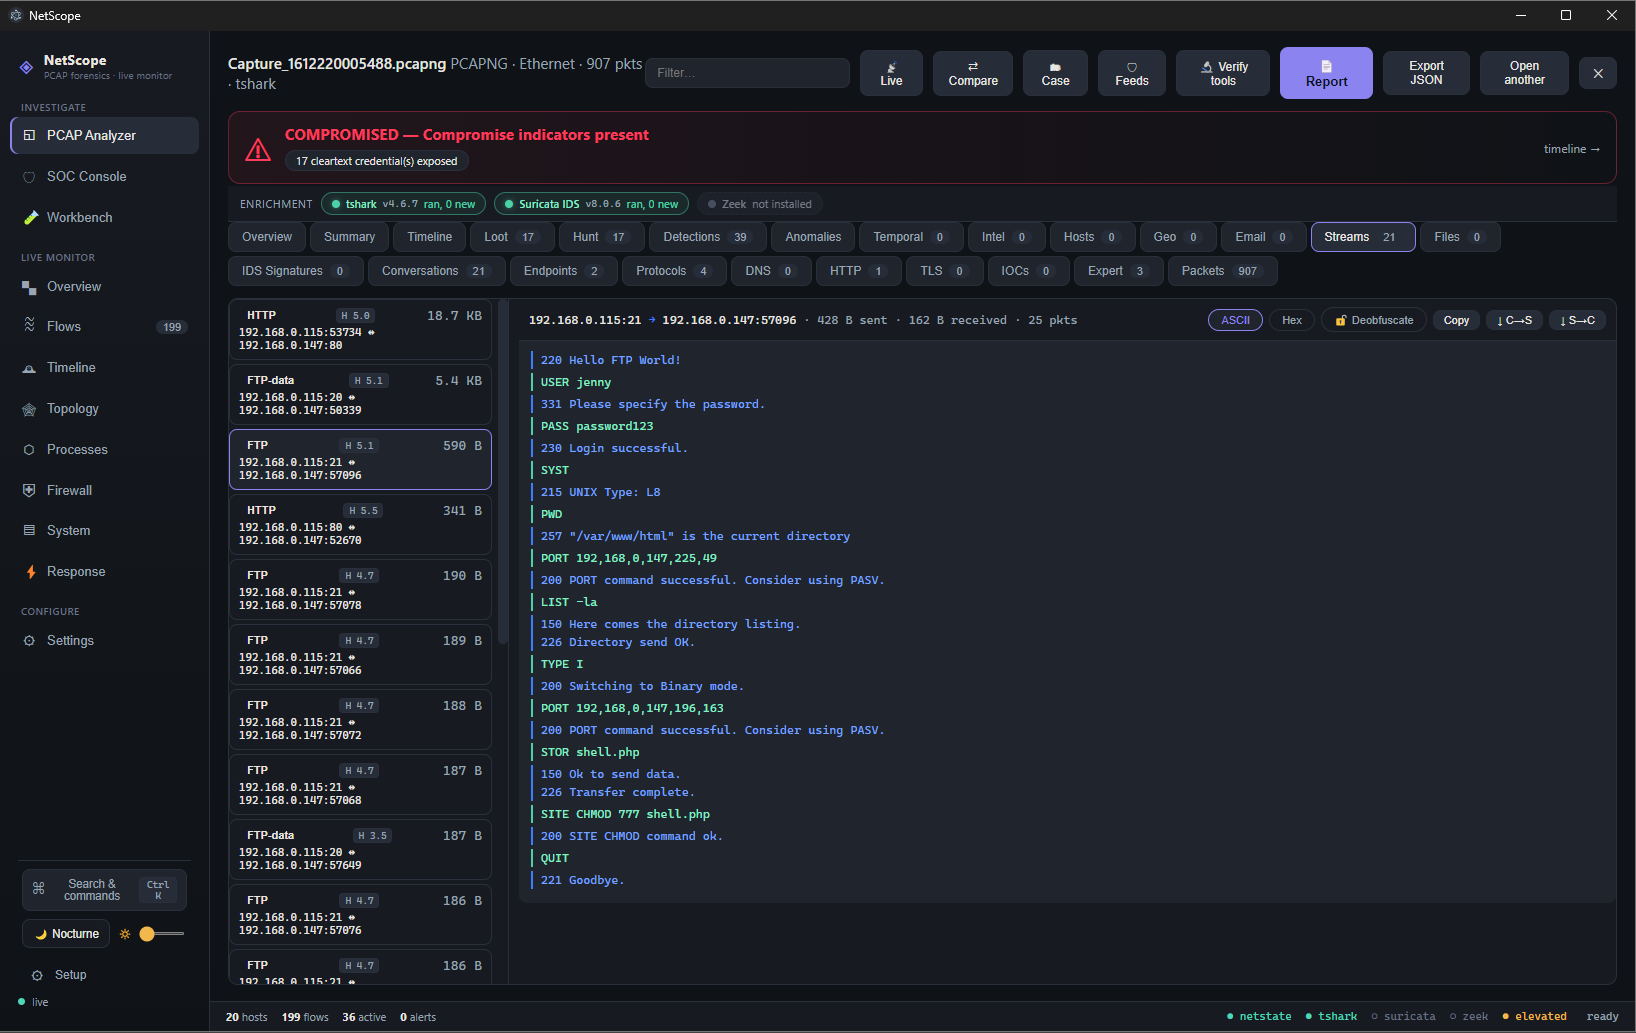 spectralzero/netscope
Offline-first network investigation and response platform for Windows. Turns a pcap or live capture into a full forensic verdict — attack story,…
 ntop/ntopng
Web-based Traffic and Cybersecurity Network Traffic Monitoring