

c2detect
 cognis-digital/c2detect
C2 server fingerprinter — Cobalt Strike, Sliver, Mythic, Havoc, Brute Ratel
command-and-controldefensive-toolsfingerprint-spoofing+8
cognis-digital/c2detectC2 server fingerprinter — Cobalt Strike, Sliver, Mythic, Havoc, Brute Ratel
 yaklang/yakit
All-in-one penetration testing platform with MITM proxy, web fuzzer, reverse connection handler, and plugin system for automated security testing and…
 pennyw0rth/netexec
Post-exploitation framework for automated network authentication testing, credential harvesting, and lateral movement across Windows/AD environments…
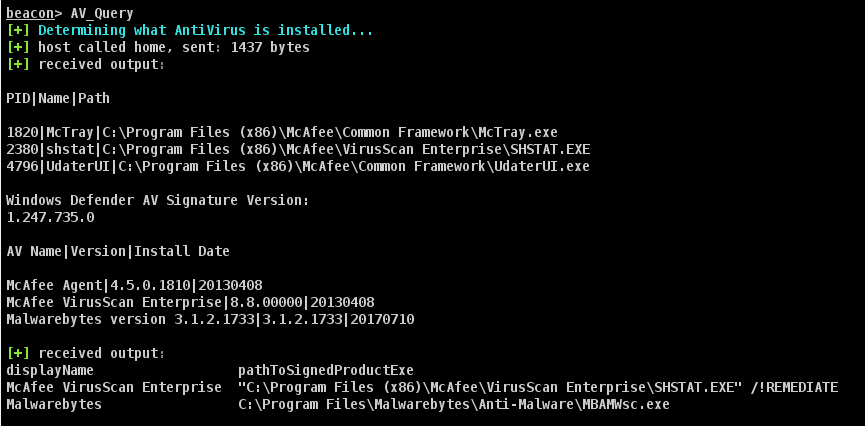 harleyqu1nn/aggressorscripts
Collection of Aggressor scripts for Cobalt Strike 3.0+ pulled from multiple sources
 r00ts3c/ddos-rootsec
Explore RootSec's DDOS Archive, featuring top-tier scanners, powerful botnets (Mirai & QBot) and other variants, high-impact exploits, advanced…
 outflanknl/c2-tool-collection
A collection of tools which integrate with Cobalt Strike (and possibly other C2 frameworks) through BOF and reflective DLL loading techniques.
 rvrsh3ll/bof_collection
Various Cobalt Strike BOFs
 nccgroup/steppingstones
Web-based red team activity logging, reporting, and situational awareness tool with Cobalt Strike and BloodHound integration.
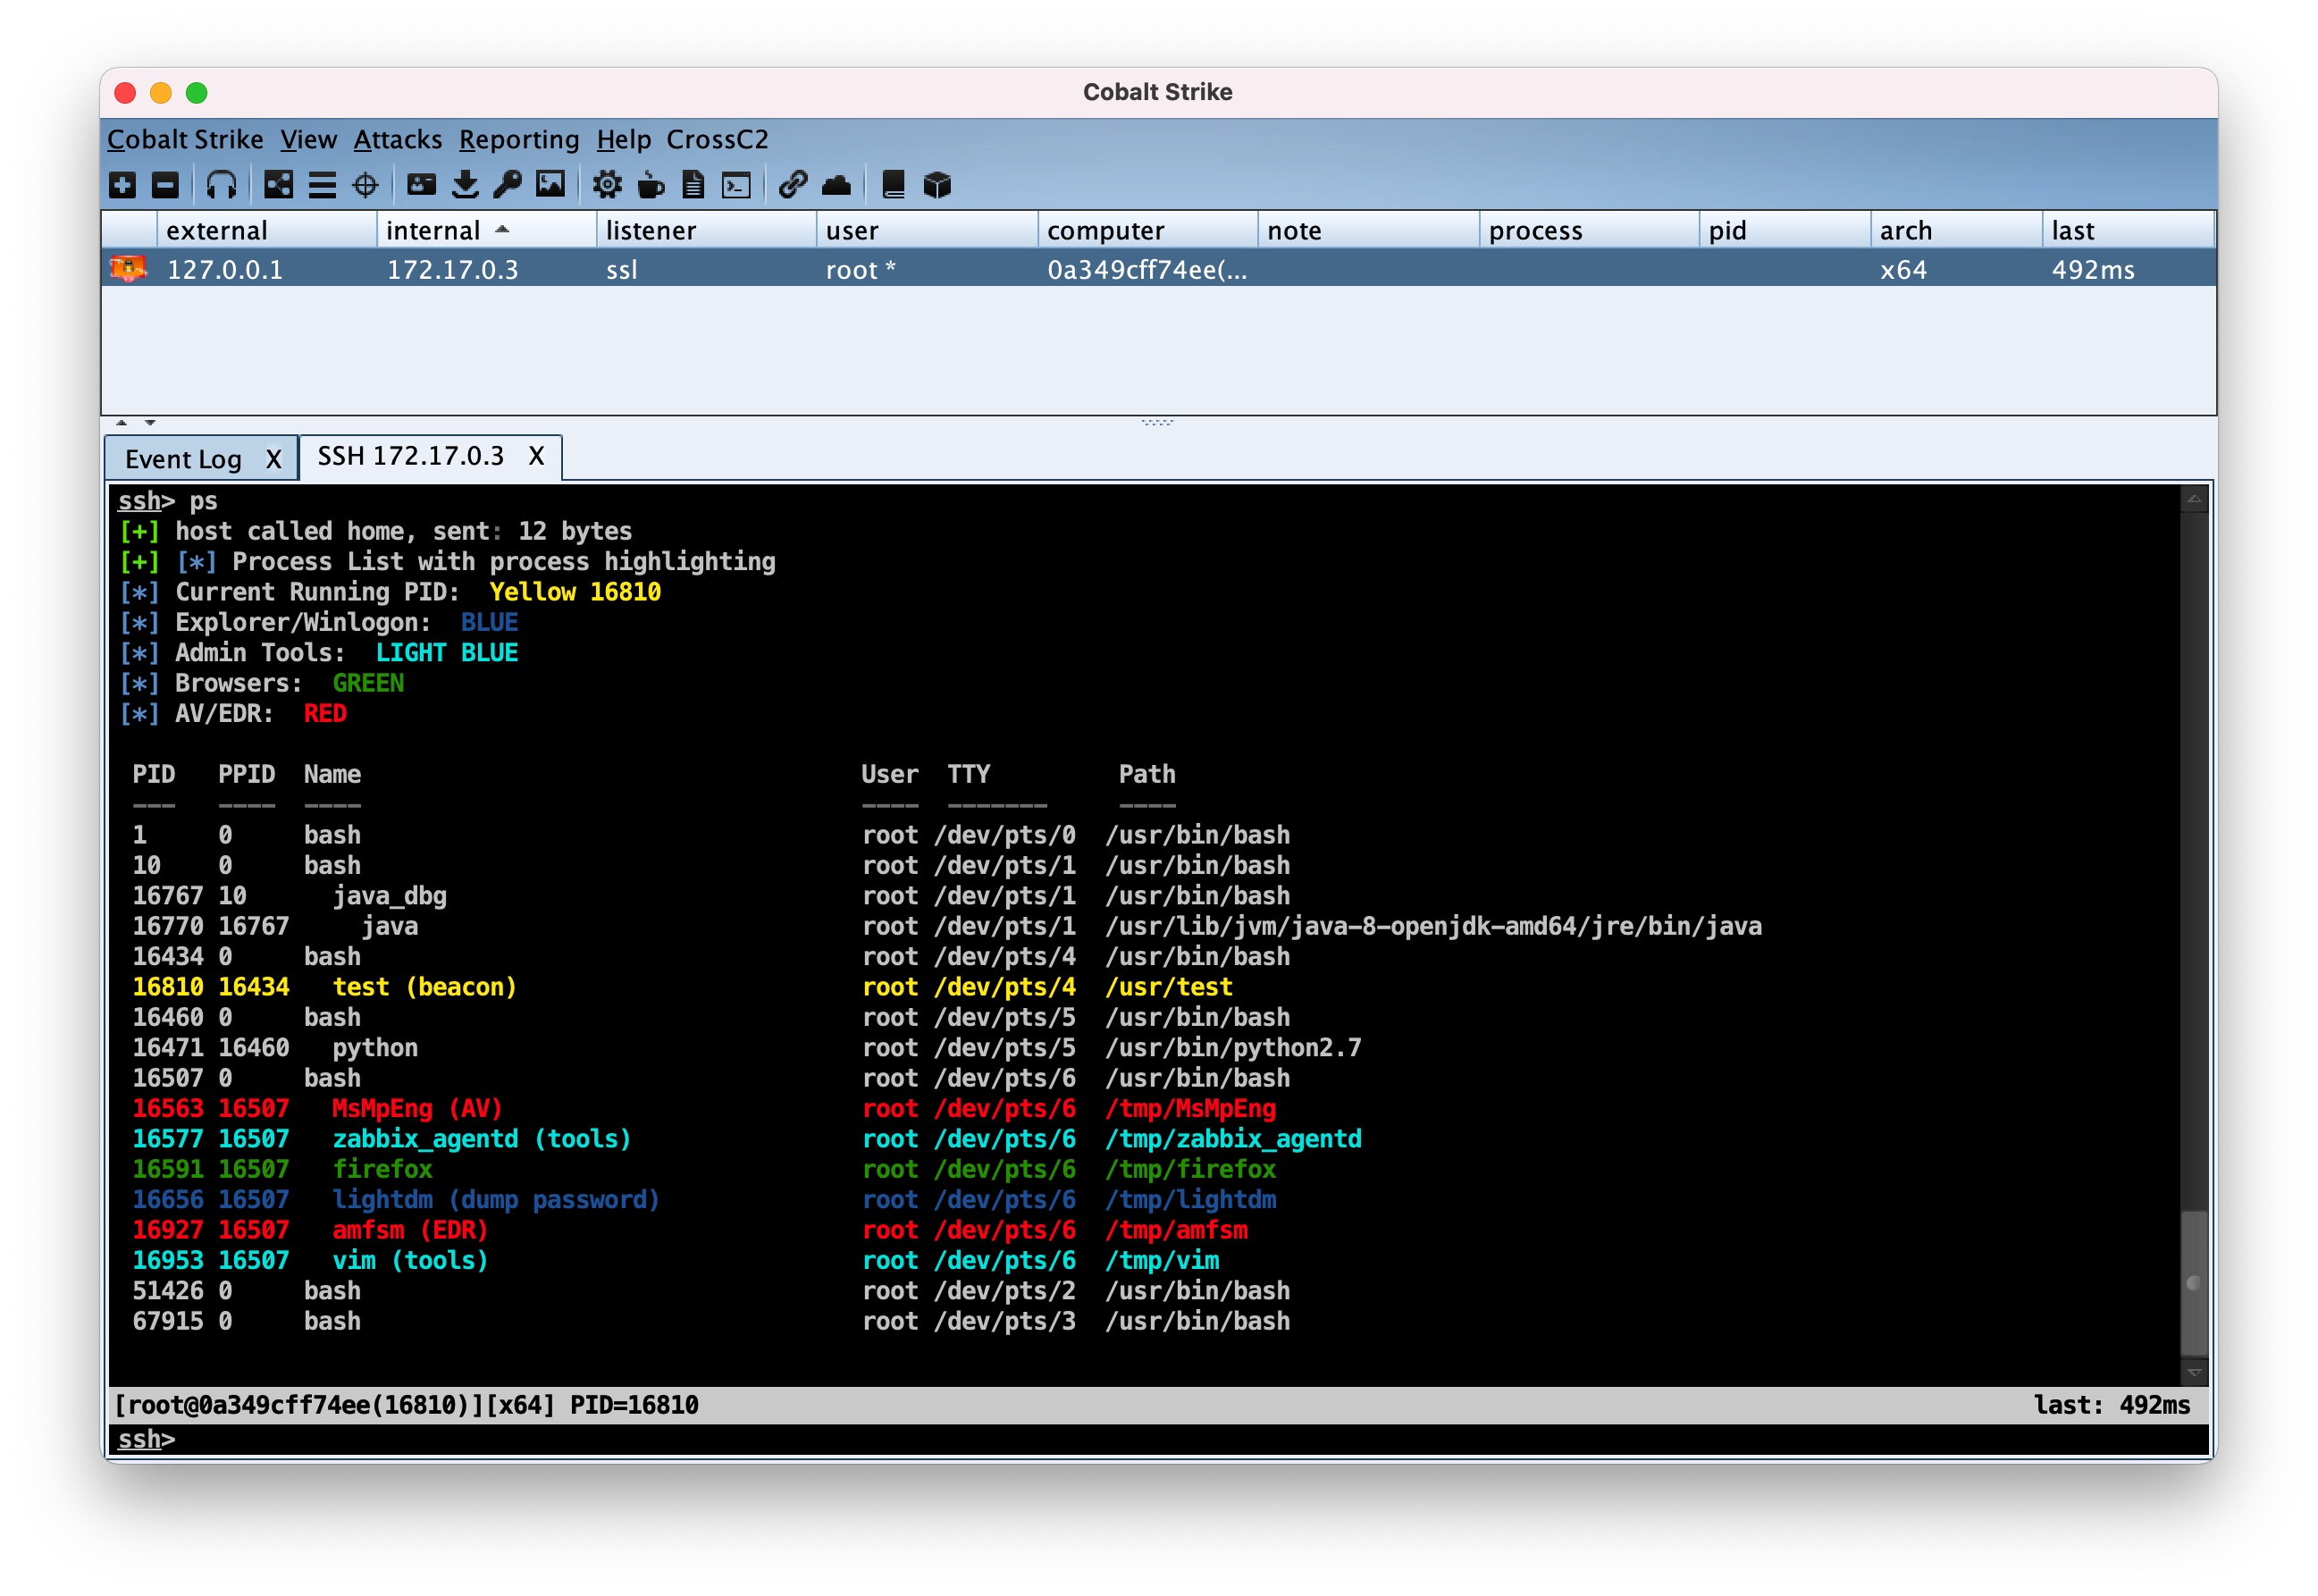 crossc2/crossc2kit
CrossC2 developed based on the Cobalt Strike framework can be used for other cross-platform system control. CrossC2Kit provides some interfaces for…
 karmanya03/overthrone
All-Rust Active Directory exploitation framework: LDAP/SMB/Kerberos enumeration, attack-graph pathfinding, Kerberoasting, NTLM relay, ticket forging,…
 01rabbit/pakuri-thon
PAKURI-THON is a tool that supports pentesters with various pentesting tools and C4 server (command & control and chat & communication server).…

 vqkro/ultrasploiter
A single binary that folds a port scanner, the full Exploit-DB index (47k entries) and runnable exploit modules into one tool. Written in Rust, runs…
 ash1996x/cve-2025-50154-aggressor-script
Cobalt Strike Aggressor script that weaponizes LNK and Library-MS files to trigger SMB NTLMv2 hash disclosure, including CVE-2025-24054 bypass, for…
 mgeeky/redwarden
Cobalt Strike C2 Reverse proxy that fends off Blue Teams, AVs, EDRs, scanners through packet inspection and malleable profile correlation
 markoarmitage/metasploit-framework
app turn nil publics and privates into blanks 3 months ago config Use bundler/setup for more graceful bundler related failures 11 days ago data…
 splunk/melting-cobalt
A Cobalt Strike Scanner that retrieves detected Team Server beacons into a JSON object
 nullarray/autosploit
Automated Mass Exploiter
 guardicore/monkey
Infection Monkey - An open-source adversary emulation platform