
pict
 thomasareed/pict
Modular incident response toolkit for collecting forensic data from potentially infected macOS endpoints, capturing browser artifacts, persistence…
digital-forensicsforensicsincident-response+2
95
thomasareed/pictModular incident response toolkit for collecting forensic data from potentially infected macOS endpoints, capturing browser artifacts, persistence…
 litneet64/etherblob-explorer
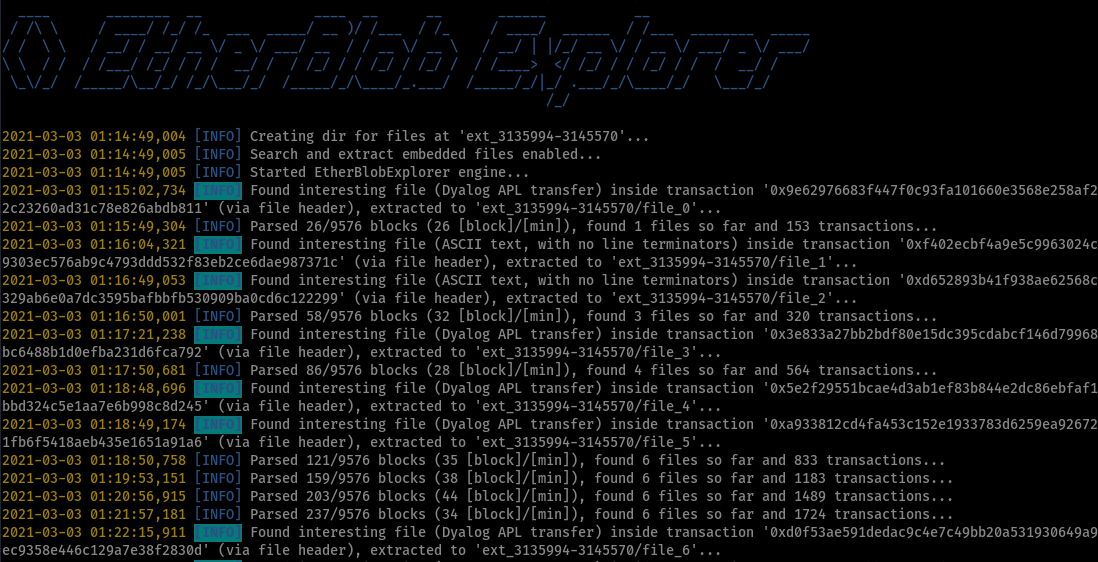
Search and extract blob files on the Ethereum Blockchain network

 simsong/bulk_extractor
This is the development tree. Production downloads are at:
 juanceresa/sift-kg
Turn any collection of documents into a knowledge graph. Extract entities and relationships via LLM, deduplicate with your approval. Map domains,…
 kvasirsecurity/kvasir
Kvasir: Penetration Test Data Management
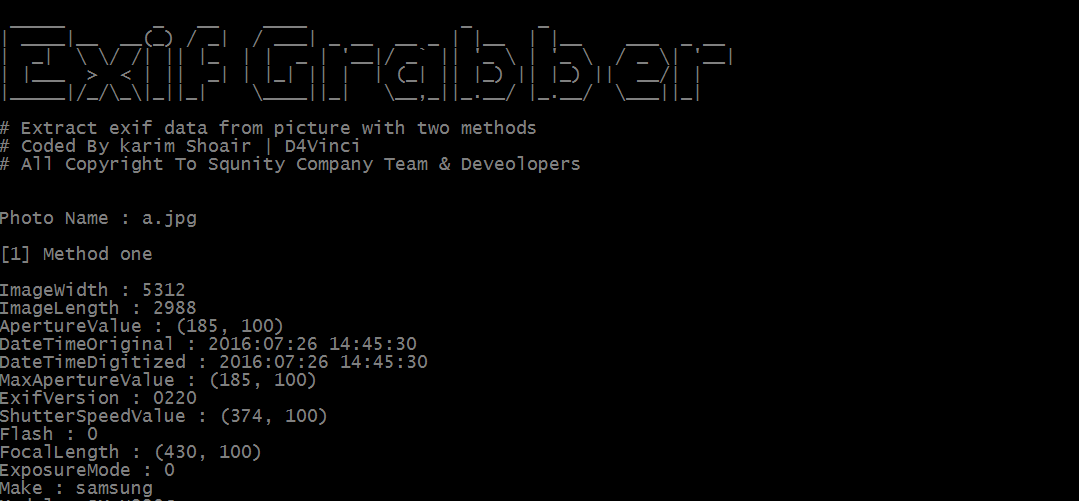 d4vinci/exif-grabber
A python tool that will extract exif data from picture with two methods
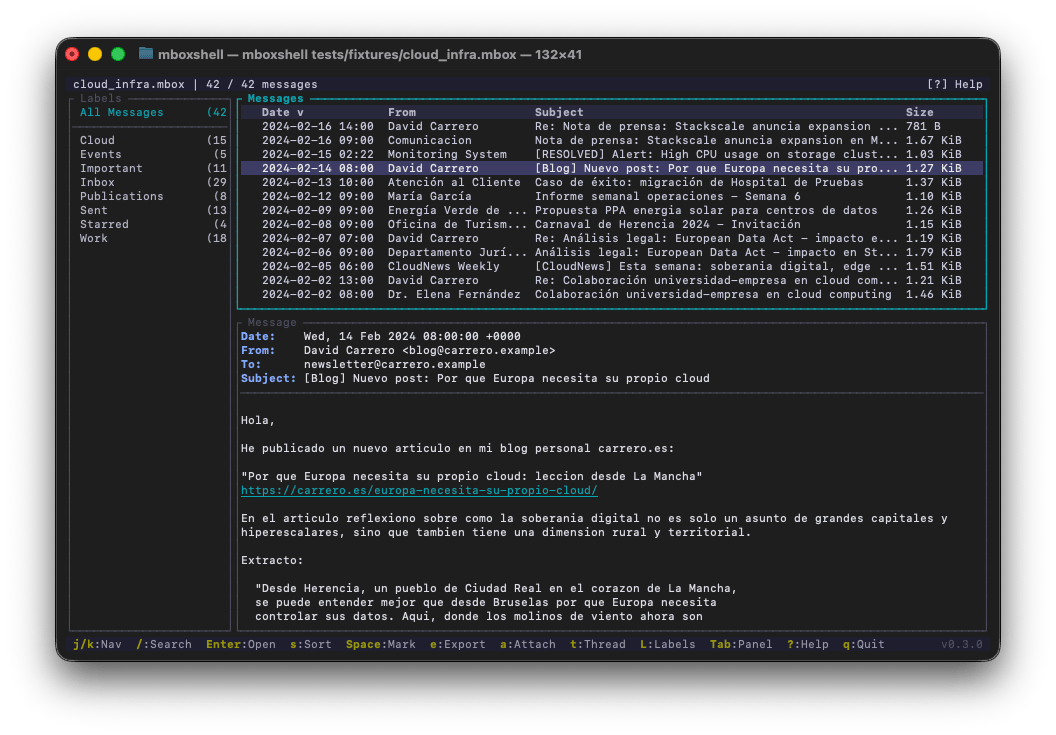 dcarrero/mboxshell
mboxShell. Fast terminal viewer for MBOX files of any size. Open, search and export emails from Gmail Takeout backups (50GB+) without loading them…
 xchwarze/magic-extractor
Universal Windows extraction tool that detects unknown files and routes them to the right bundled extractor.
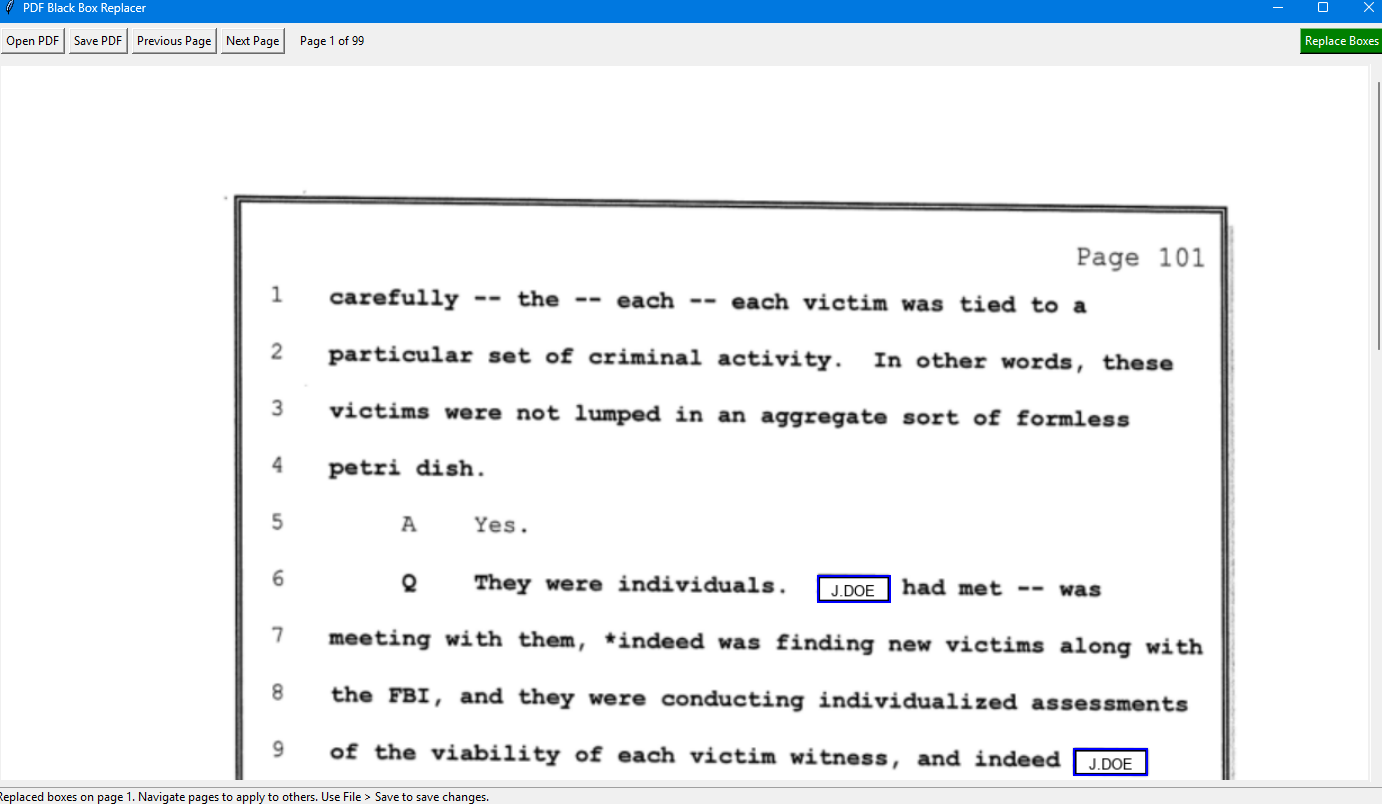
 emrekybs/osintcase
An OSINT investigation case mapping tool for organizing entities, relationships, evidence, and intelligence.
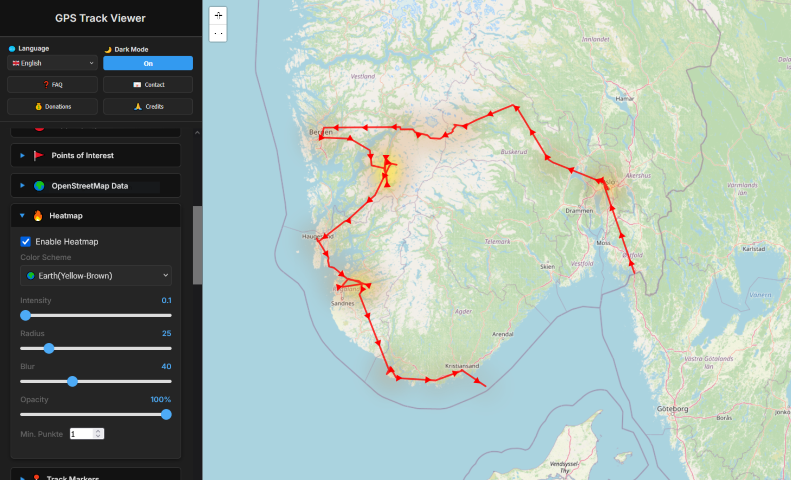 lukawe/localexifgeomap
A powerful, privacy-focused, browser-based tool to visualize and analyze GPS data from your photos. Simply drag and drop images to generate…
 mebus/cupp
Interactive password profiler that generates targeted wordlists by gathering personal details about a user, used for penetration testing and forensic…
 b16f00t/whapa
Graphical forensic toolkit for parsing, decrypting, and extracting WhatsApp data from Android and iOS devices, including Google Drive and iCloud…
 tclahr/uac
Portable, dependency-free incident response tool that automates forensic artifact collection from Unix-like systems, including memory acquisition,…
 soxoj/telegram-bot-dumper
🔪 Dumper & ripper for Telegram bots by token. Forensic CLI tool with web interface
 nightbringer21/fridump
Cross-platform memory dumper using Frida to extract accessible memory from iOS, Android, and Windows applications for forensic analysis and…
 biggiesmallsag/nighthawkresponse
Incident Response Forensic Framework