PowerShell-Suite
 fuzzysecurity/powershell-suite
My musings with PowerShell
binary-analysisdebuggersforensics+5
fuzzysecurity/powershell-suiteMy musings with PowerShell
 mandiant/goresym
Parses Go binaries to recover symbols, function metadata, types, file paths, and embedded strings, including stripped or UPX-packed samples, with IDA…
 isecpartners/introspy-ios
Security profiling for blackbox iOS
 payloadsecurity/sandbox_scryer
Parses public sandbox detonation reports to produce threat hunting intelligence, organizes findings via MITRE ATT&CK, assembles IOCs, and generates…
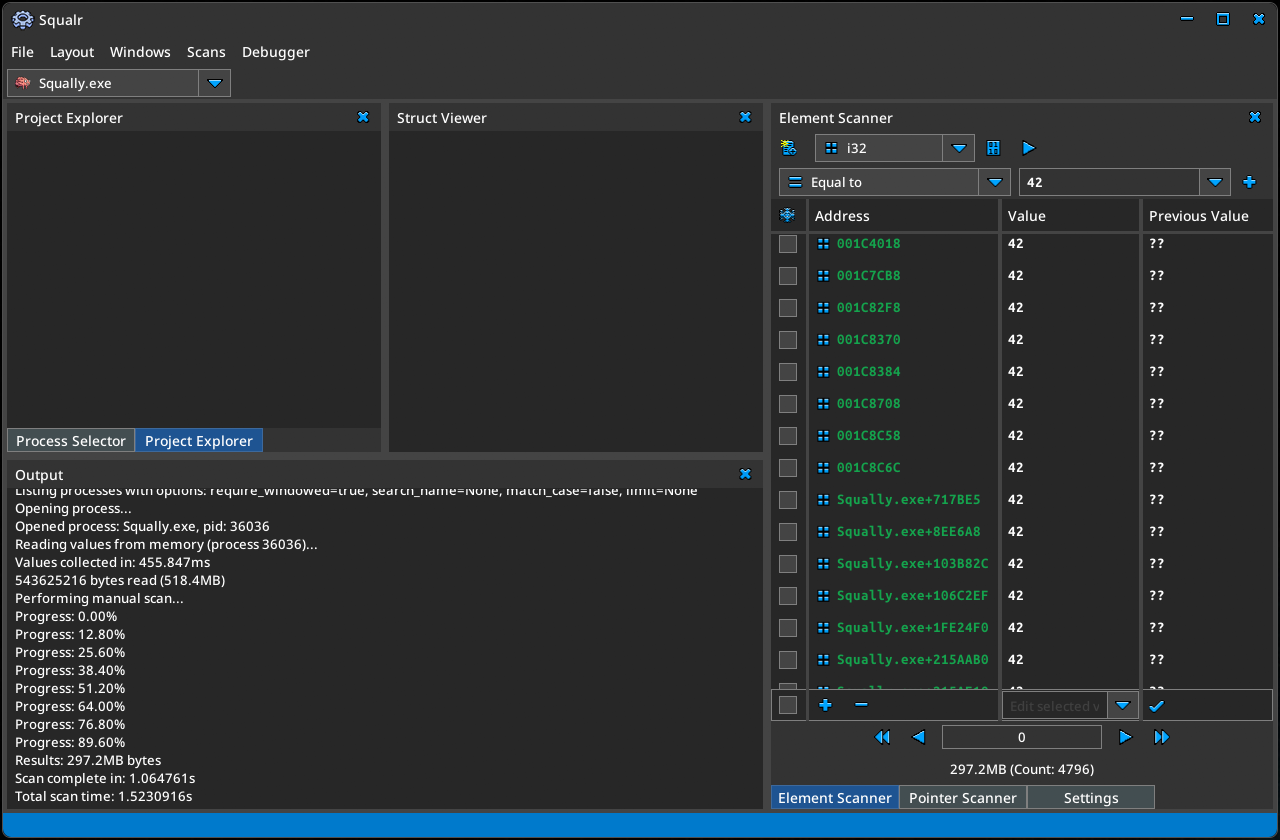 squalr/squalr
A generic game/software hacking tool written from the ground up in Rust.
 dougwithseismic/dezlock-dump
Runtime schema + RTTI extraction tool for Deadlock, CS2, Dota, and others (Source 2). No source2gen required.
 yeet-src/usbsnoop
Live, system-wide USB transfer sniffer in eBPF — decodes USB traffic inline (control SETUP, SCSI, HID) from two universal URB hooks. No usbmon, no…
 jstrosch/subparse
Modular malware analysis artifact collection and correlation framework
 nccgroup/mnemosyne
A Generic Windows Memory Scraping Tool
 kartoffelpflanze/odis-project-explorer
Python dumper/explorer for MCD Runtime Projects used by ODIS
 hackinglz/svg_phishing_tools
SVG Analysis and generation tools for commonly seen SVG attachment phishing
 gilnett/wstrace
Standalone zero-driver Windows system and API monitor in Rust
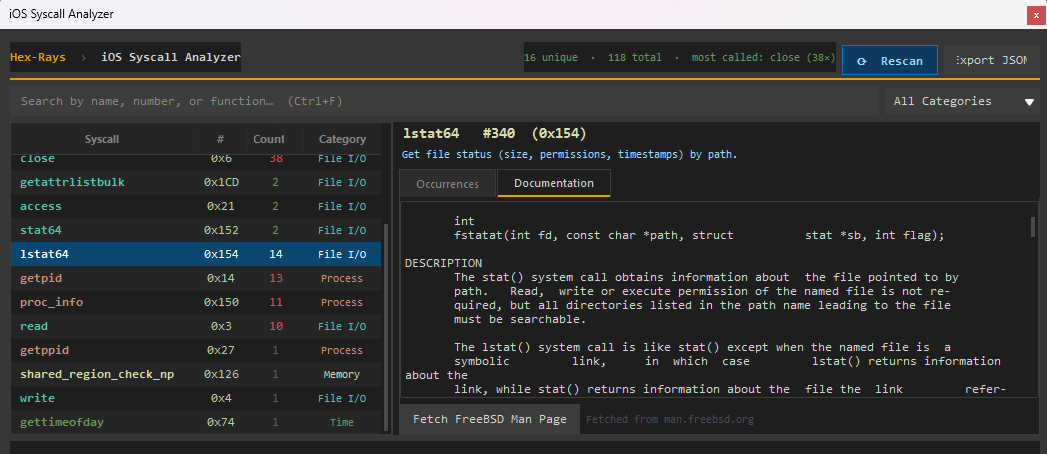 stolevchristian/sylvia
iOS Syscall Explorer for IDA 9.X
 rakutentech/jndi-ldap-test-server
A minimalistic LDAP server that is meant for test vulnerability to JNDI+LDAP injection attacks in Java, especially CVE-2021-44228.
 sunghoojung/reverse-engineering-browser
Local-first macOS research browser built on a custom Brave build that captures network traffic, fingerprints, scripts, and runtime evidence for…
 kaandemir993/formbook-payload-extraction-xor-decryption-net-assembly-analysis
Reverse engineering analysis of Formbook, an info-stealer that uses .NET assembly manipulation and XOR decryption. Full payload extracted via x32dbg,…
 kaandemir993/amadey-loader-multi-stage-malware-with-keylogging-clipboard-hijack-privilege-escalation-analysis
Reverse engineering Amadey Loader with x64dbg: dynamic API resolution, token privilege escalation, keylogger hooks, clipboard capture, and…