
htb-ctf-walkthroughs
 rootsecnz/htb-ctf-walkthroughs
Walkthroughs for Capture the Flag challenges on the HTB Cybersecurity Platform.
ctfeducationexploitation+6
rootsecnz/htb-ctf-walkthroughsWalkthroughs for Capture the Flag challenges on the HTB Cybersecurity Platform.
 shenril/sitadel
Web Application Security Scanner
 foxvr-sudo/bug-bounty-arsenal-v.3
Full-stack platform for authorized web application security scanning with a detector-based engine, async Celery workers, and a React dashboard for…
 taksec/google-dorks-bug-bounty
A list of Google Dorks for Bug Bounty, Web Application Security, and Pentesting
 spinkham/skipfish
Web application security scanner created by lcamtuf for google - Unofficial Mirror
 yunemse48/403bypasser
Automates HTTP 403 access control bypass techniques using header manipulation, path obfuscation, and HTTP method conversion for web application…
 0xdekster/reconnote
Web Application Security Automation Framework which recons the target for various assets to maximize the attack surface for security professionals &…
 capture0x/lfi-space
Automated Local File Inclusion (LFI) vulnerability scanner with Google Dork search and targeted URL scan modes for web application security testing.
 matrix07ksa/hackerinfo
Hackerinfo infromations Web Application Security
 sobri3195/pegasus-pentest-arsenal
A comprehensive web application security testing toolkit that combines 10 powerful penetration testing features into one tool.
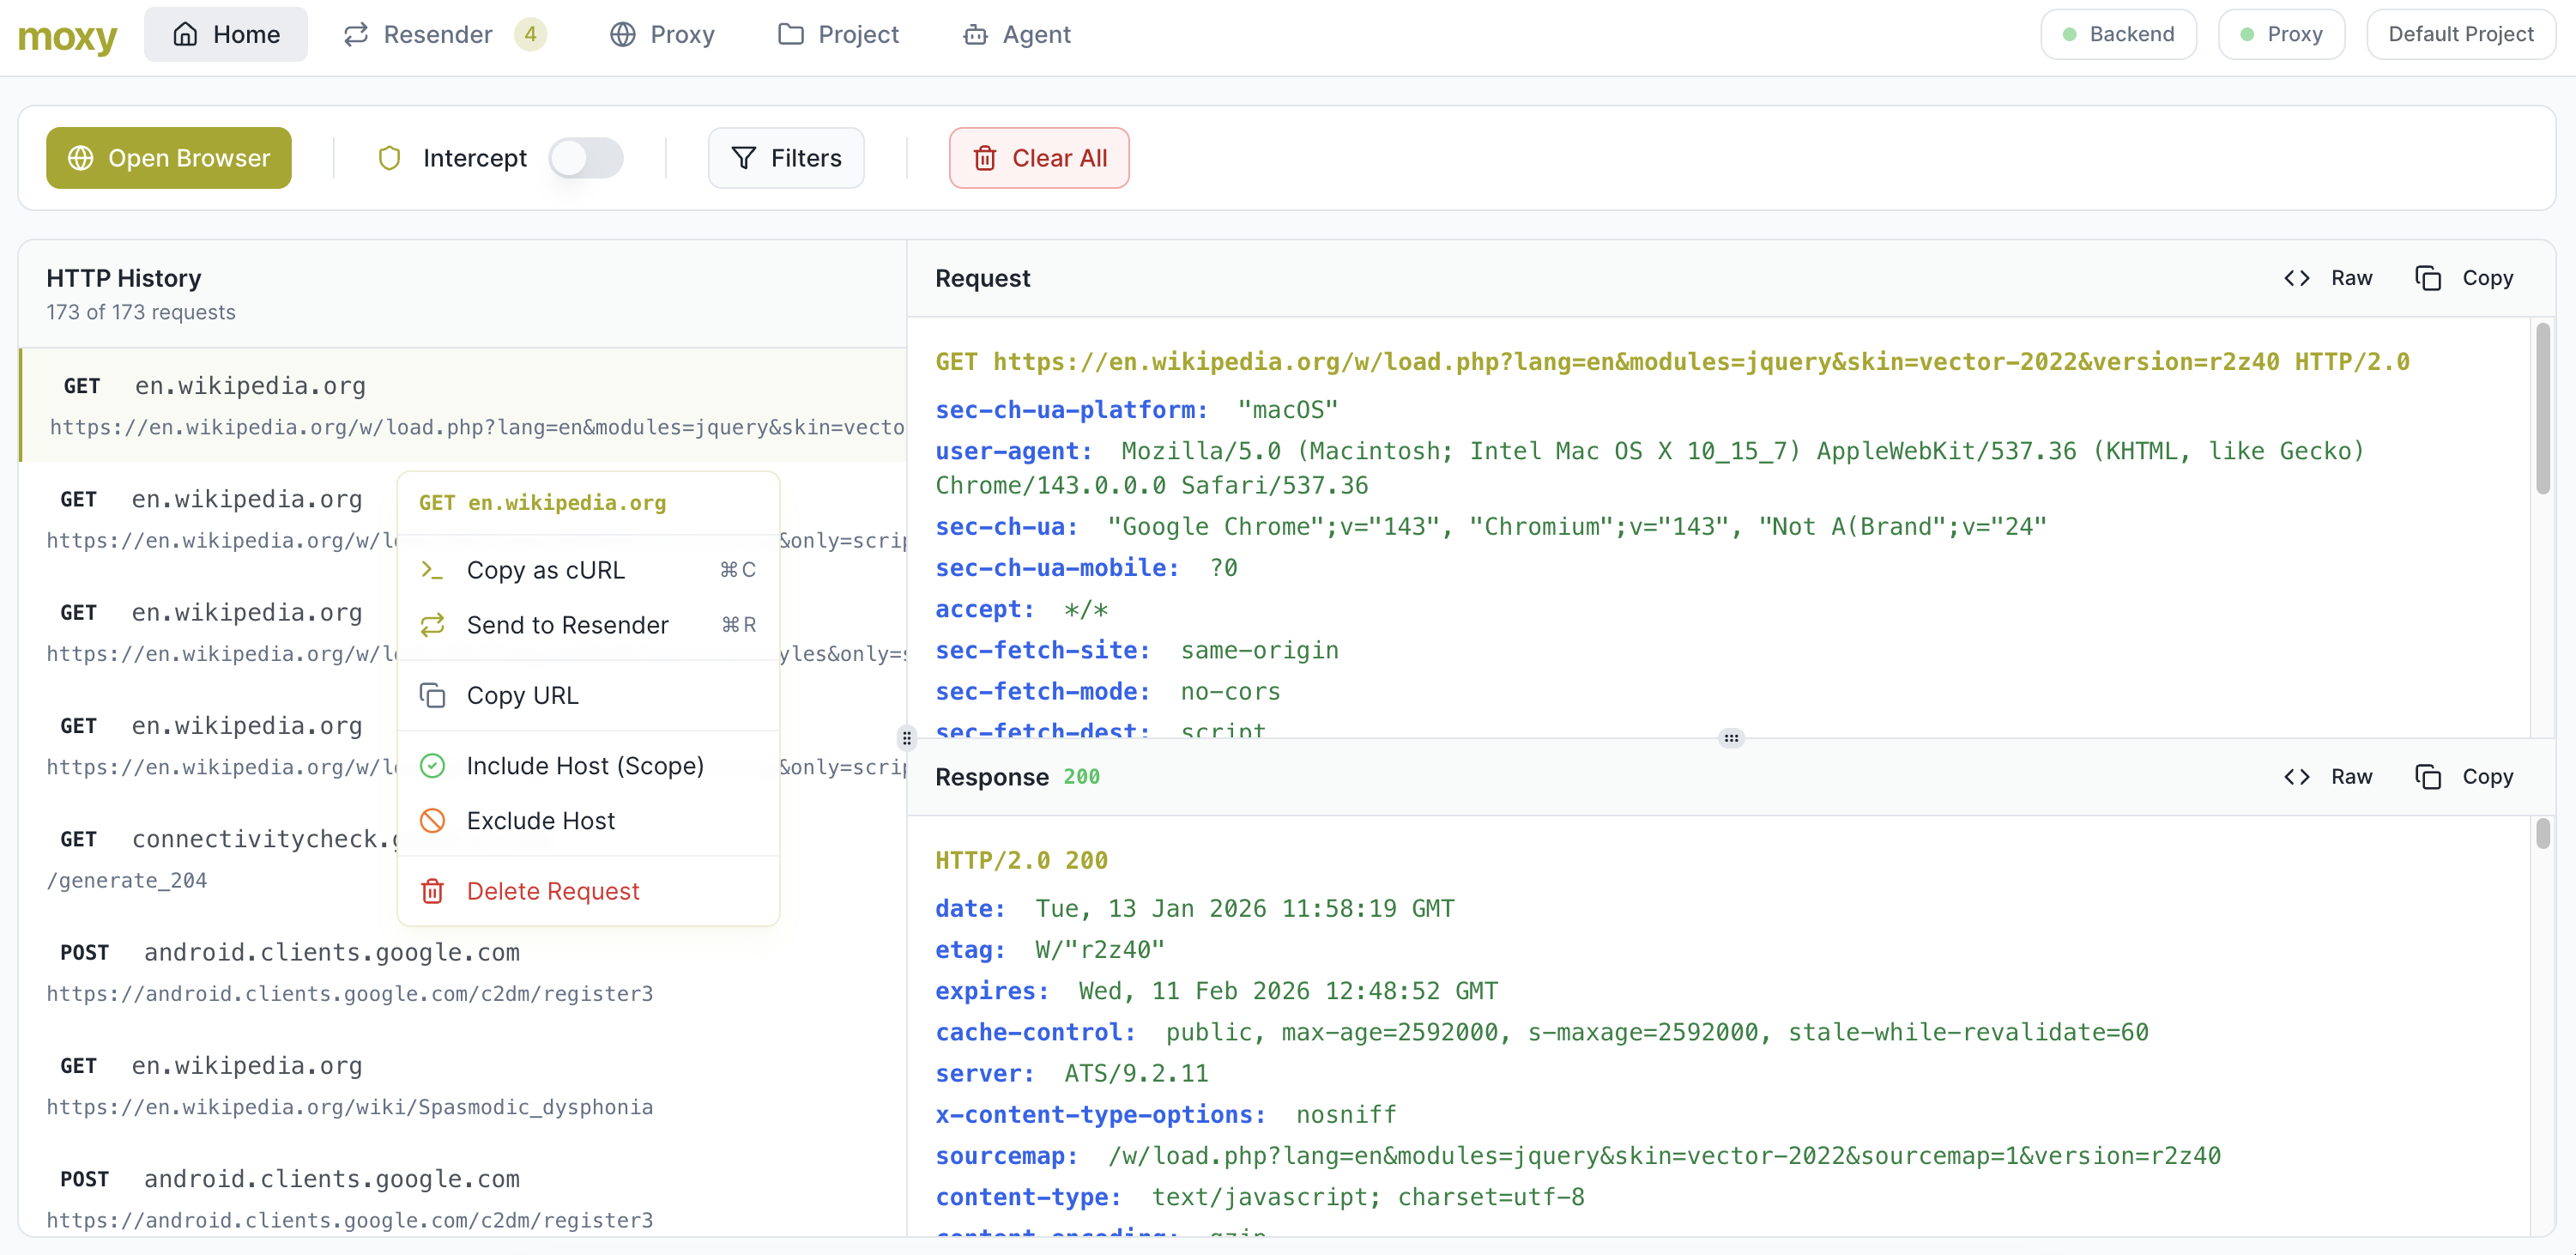 matank001/moxy
Moxy is an open-source DAST tool designed for modern web application security testing. It provides an easy-to-use interface with agentic capabilities…
 jas502n/burpsuite_pro_v1.7.37
Comprehensive web application security testing platform featuring advanced scanning engine, intercepting proxy, and automated vulnerability detection…
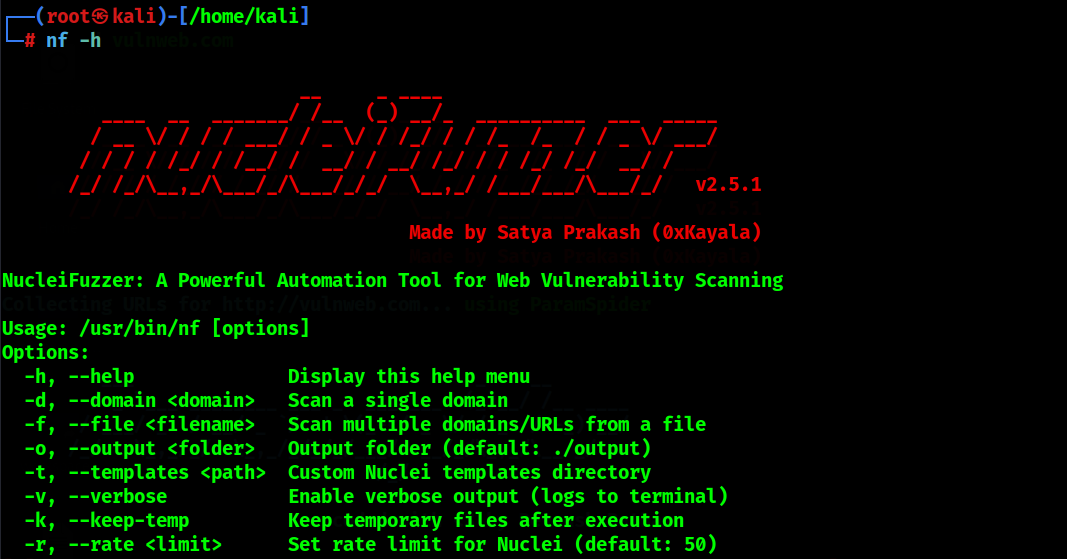 0xkayala/nucleifuzzer
Automated web vulnerability scanner combining URL discovery tools (ParamSpider, waybackurls, gauplus, hakrawler, katana) with Nuclei fuzzing…
 delvelabs/tachyon
Fast http dead file finder.
 rwincey/cve-2021-27198
Proof-of-concept exploit for CVE-2021-27198, demonstrating a specific vulnerability in a web application for security testing and validation.
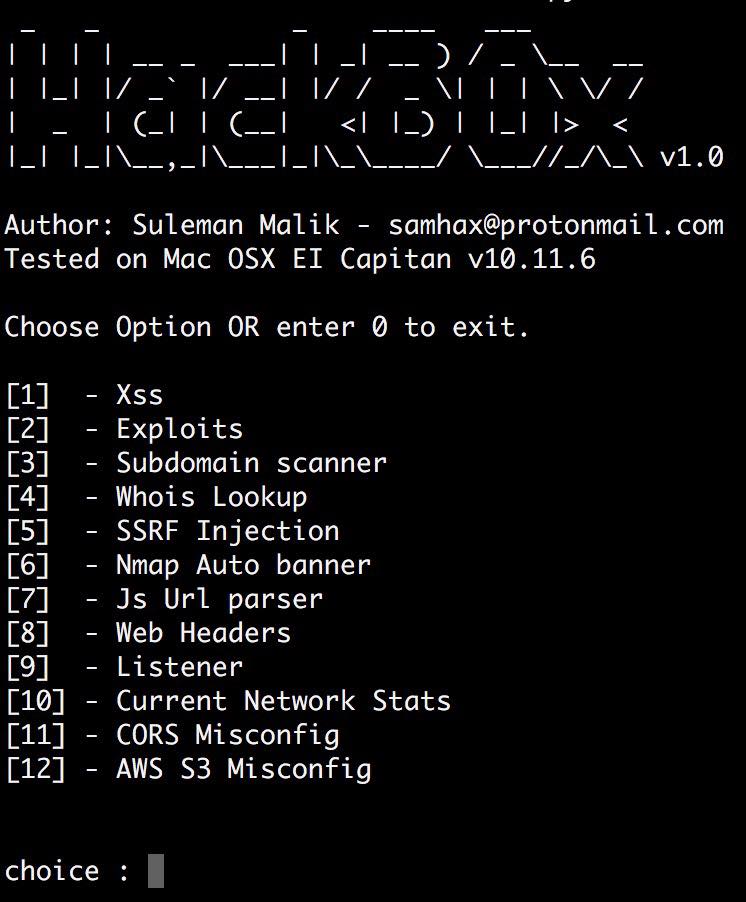 samhaxr/hackbox
HackBox is a powerful and comprehensive tool that combines a variety of techniques for web application and network security assessments, including…
 pudding2/cve-2018-14083
Proof-of-concept exploit for CVE-2018-14083, demonstrating a specific web application vulnerability for security testing and validation.
 michelin/chopchop
YAML-driven CLI scanner that detects exposed services, files, and folders on web endpoints. Designed for developers to integrate security checks into…