
 algosecure/pollenisator
Collaborative pentest tool with highly customizable tools
 franccesco/getaltname
Extract subdomains from SSL certificates in HTTPS sites.
 christophetd/cloudflair
🔎 Find origin servers of websites behind CloudFlare by using Internet-wide scan data from Censys.
 laluka/bypass-url-parser
Tests hundreds of URL bypass techniques against 40X protected pages using raw curl requests, with multi-mode scanning, header spoofing, and JSON/HTML…
 stefanoj3/dirstalk
Modern alternative to dirbuster/dirb
 trhhubsd/artex
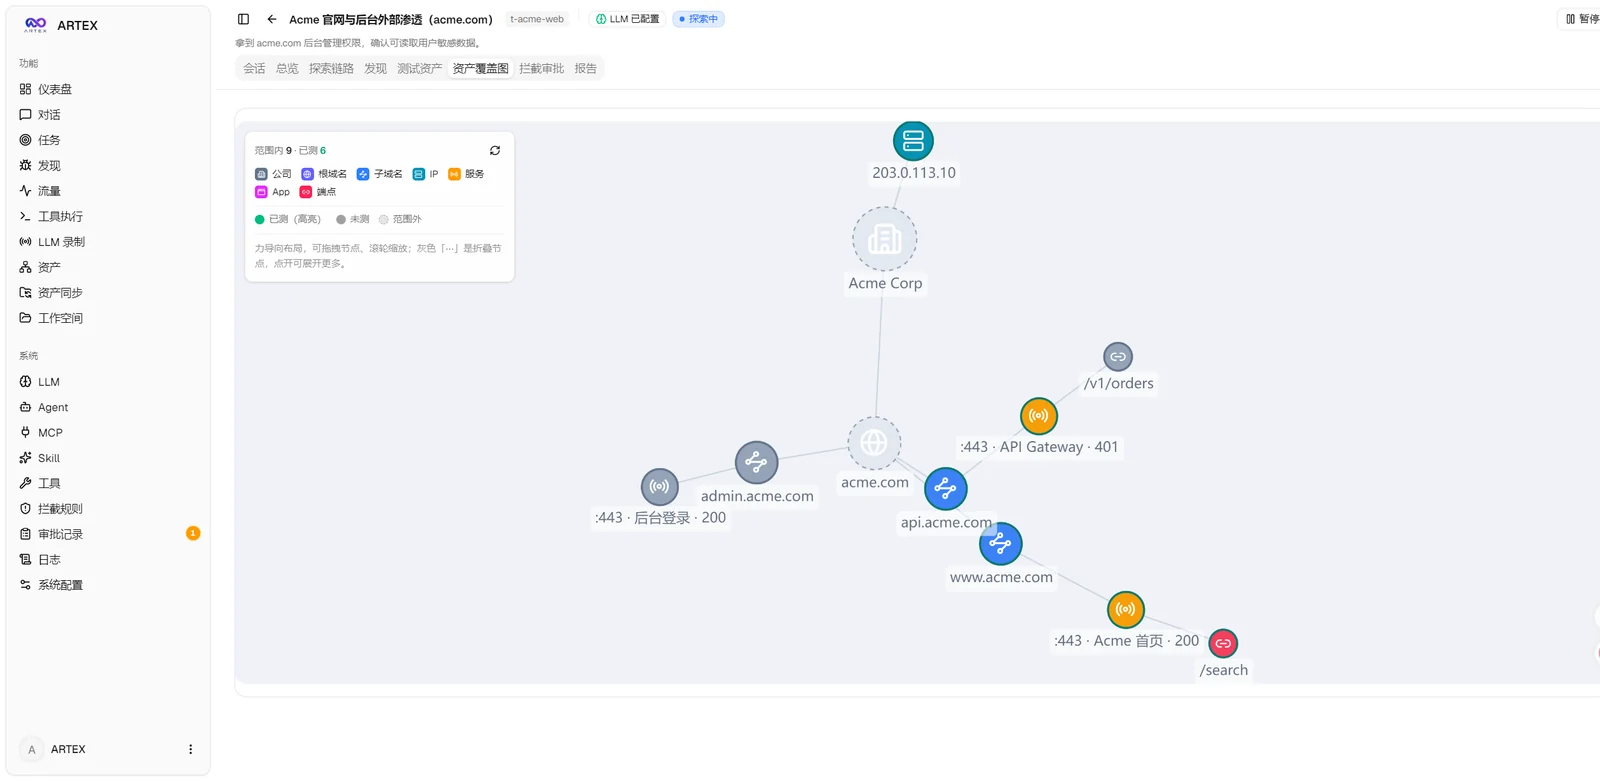
Multi-agent LLM system for autonomous penetration testing in isolated labs: planner/worker agents share asset and exploration graphs, with MITM…
 g0h4n/rusthound-ce
Active Directory data ingestor for BloodHound Community Edition written in Rust. 🦀
 nh-red-team/rusthound
Active Directory data ingestor for BloodHound Legacy written in Rust. 🦀
 evkir/phantom-grid
Free Burp Collaborator alternative- OOB interaction capture (HTTP/HTTPS/DNS) with SQLite & exfil reassembly
 initstring/cloud_enum
Multi-cloud OSINT tool. Enumerate public resources in AWS, Azure, and Google Cloud.

 invuls/pentest-projects/pcf
Opensource, cross-platform and portable toolkit for automating routine processes when carrying out various works for testing!
 lefayjey/linwinpwn
Bash script wrapping Active Directory tools for automated enumeration, vulnerability checks, exploitation, and password dumping via LDAP, RPC,…
 koutto/jok3r
Jok3r v3 BETA 2 - Network and Web Pentest Automation Framework
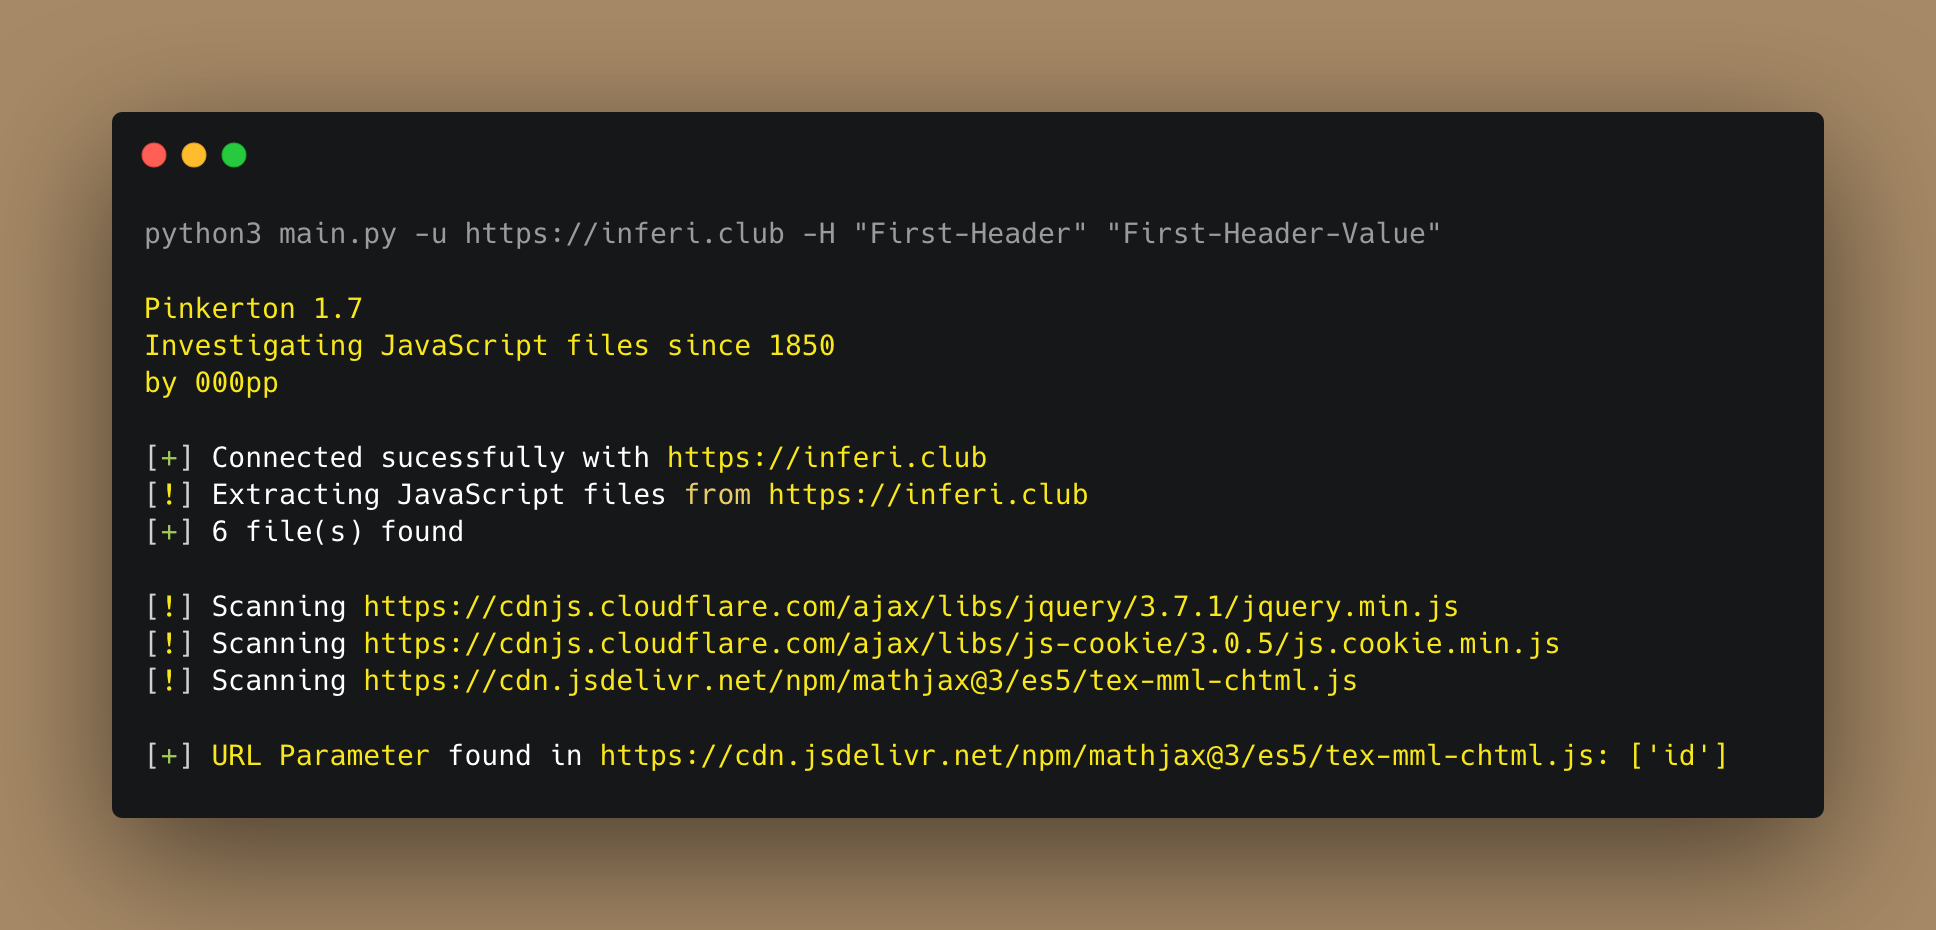 0xdsm/pinkerton
🕵️ Python project to crawl for JavaScript files and search for secrets like API keys, authorization tokens, hardcoded credentials, etc.
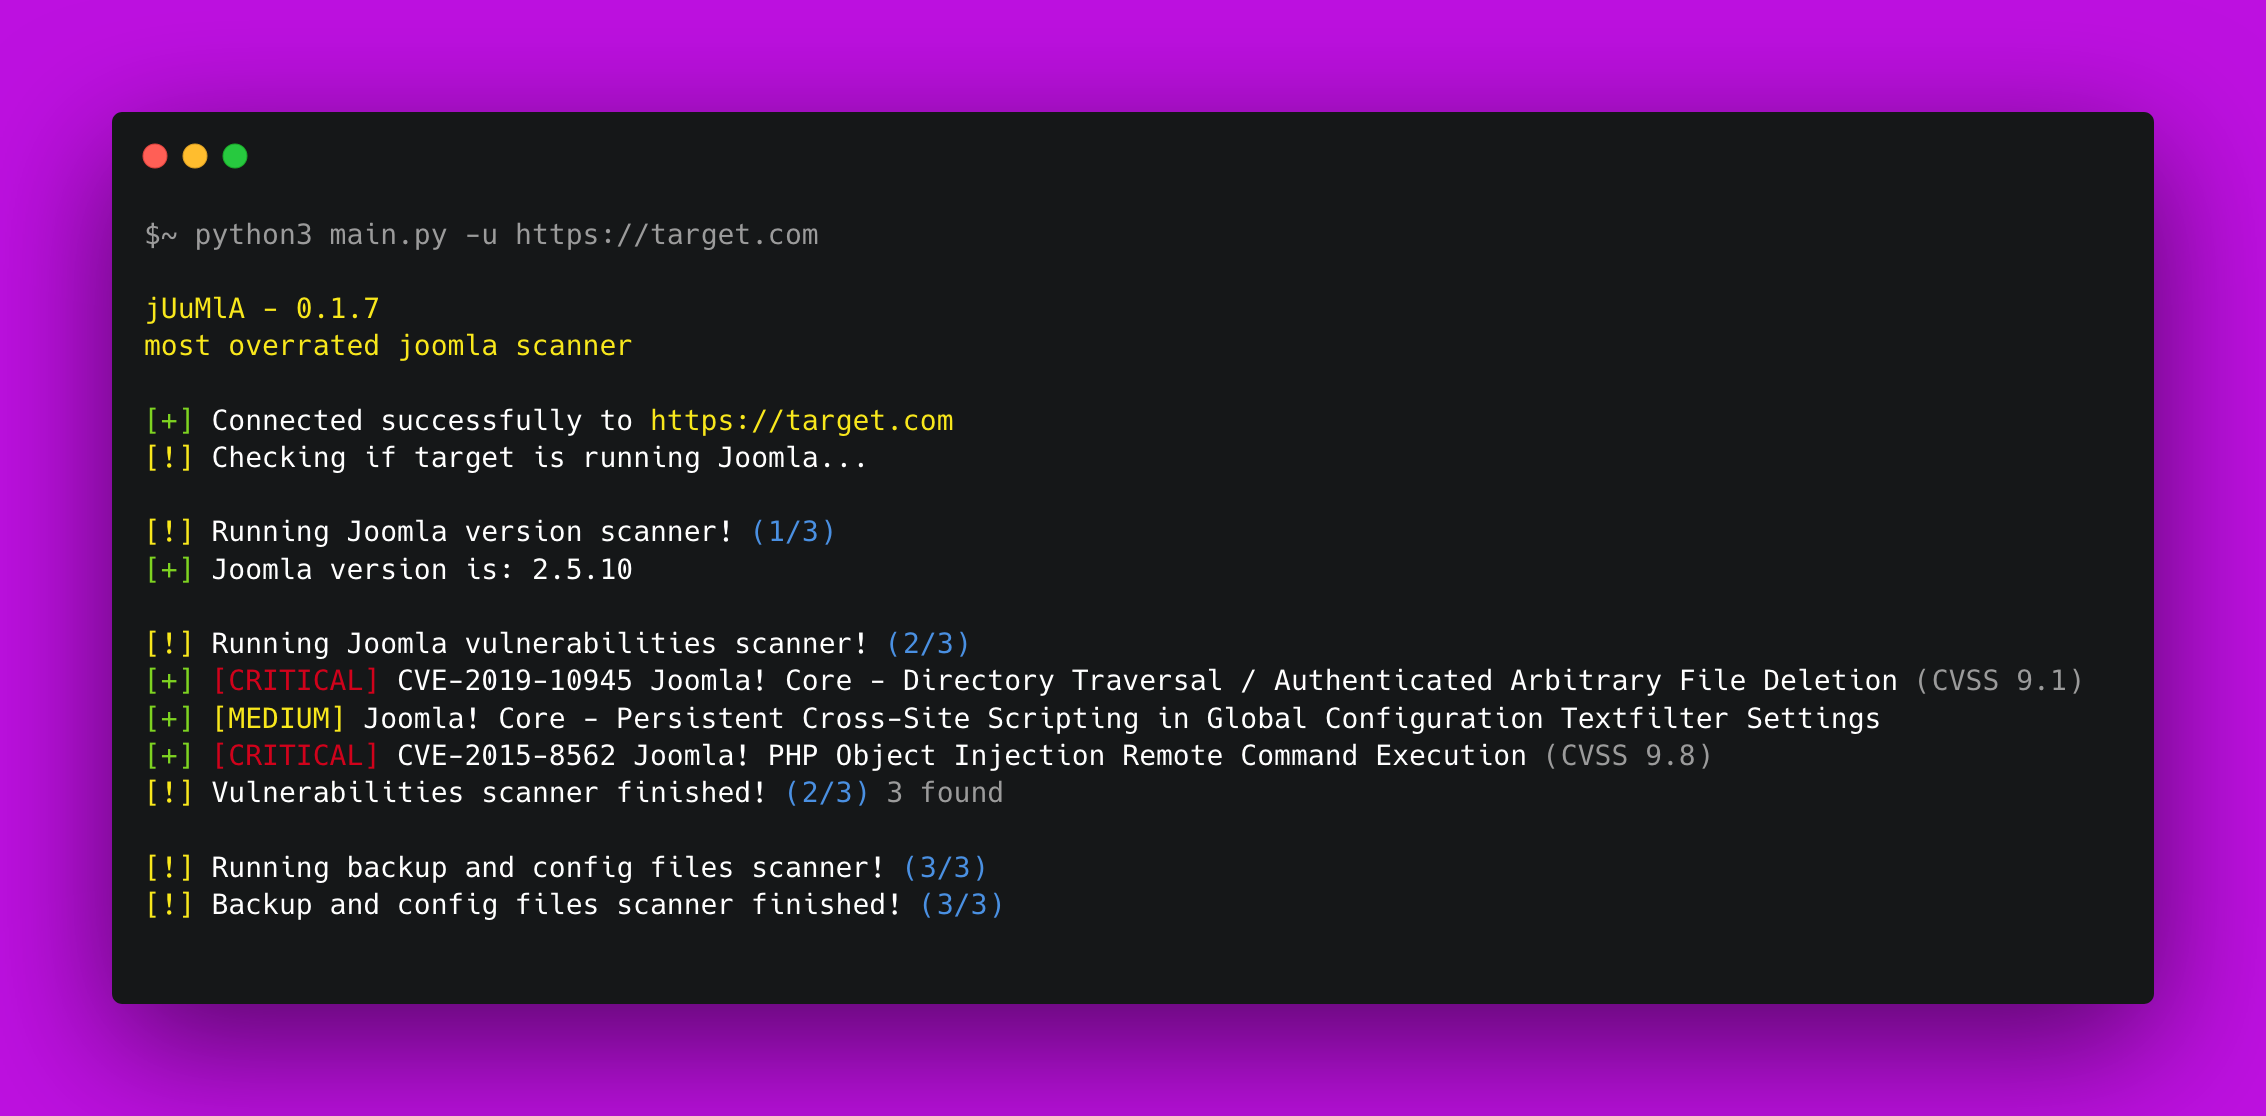 0xdsm/juumla
🦁 Python project to identify and scan for vulnerabilities related to the Joomla CMS project. It scans for common misconfigurations and public…