

CVE-2025-61148
 sharma19d/cve-2025-61148
The vulnerability exists in the Student Payment API. The application fails to properly validate whether the user requesting a receipt is authorized…
api-security-testingeducationinformation-gathering+3
sharma19d/cve-2025-61148The vulnerability exists in the Student Payment API. The application fails to properly validate whether the user requesting a receipt is authorized…
 adelittle/cve-2021-4191_exploits
Exploit script for CVE-2021-4191 that enumerates GitLab users via the GraphQL API, useful for security assessments and validating exposure.
 d0rb/packetpirate
A headless , scriptable, command-line based MITM proxy designed for network traffic interception, analysis, and modification on Windows systems.
 secsys-fdu/cve-2025-51867
Demonstrates an Insecure Direct Object Reference (IDOR) vulnerability in Deepfiction AI's chat API, allowing attackers to consume other users'…
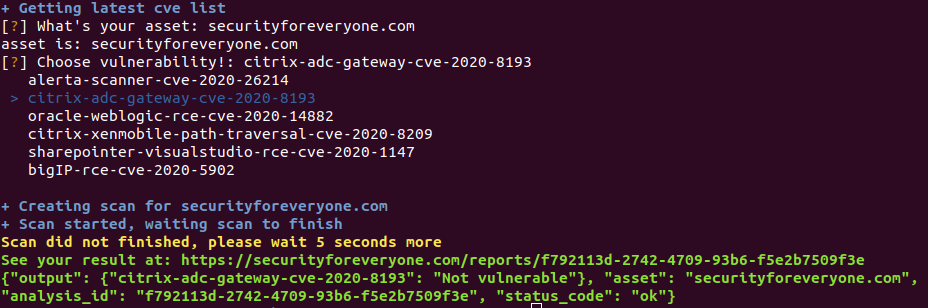 s4e-io-old-labs/s4e-cve-scanner
API-based scanner that retrieves and lists the latest Common Vulnerabilities and Exposures (CVEs) for automated security assessment and vulnerability…
 cetinpy/cve-2024-50633
Proof-of-concept exploit for CVE-2024-50633, a Broken Object Level Authorization (BOLA) vulnerability in Indico v3.2.9–v3.3.2, enabling unauthorized…
 randomrobbiebf/cve-2023-6289
Swift Performance Lite <= 2.3.6.14 - Missing Authorization to Unauthenticated Settings Export
 thoropass-public/area51
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
 hahwul/gori
A fast, keyboard-driven HTTP intercepting proxy and hacking & pentesting toolkit for the terminal.
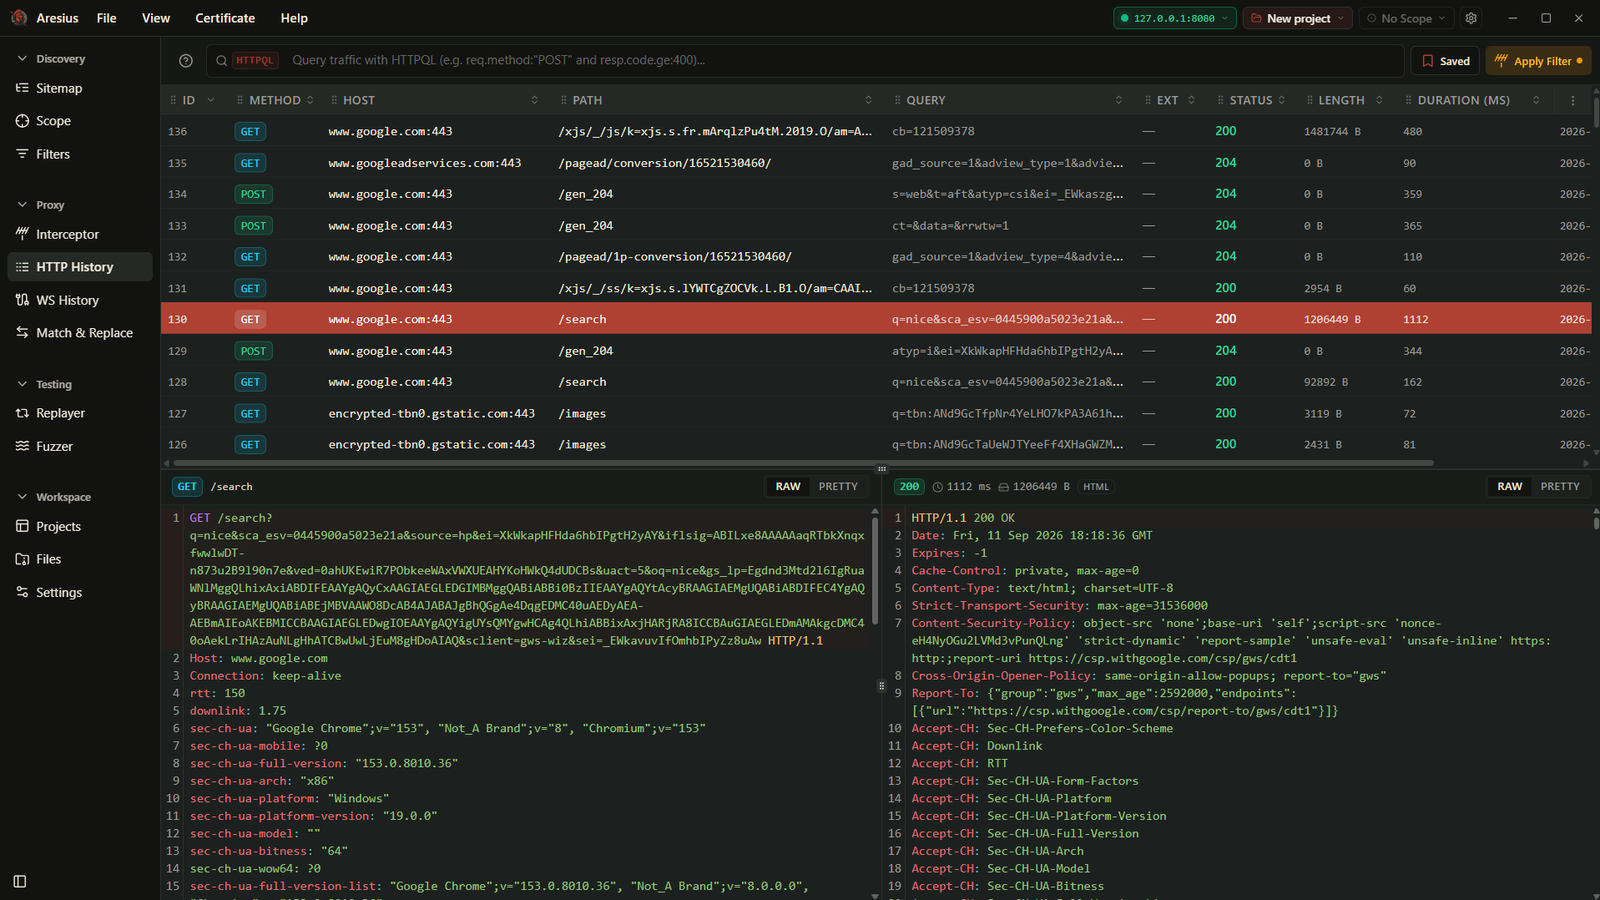 0xmarik/aresius
Native HTTP/HTTPS interception proxy for penetration testers and bug bounty hunters with live request tampering, request replay, high-speed fuzzing,…
 wkeeling/selenium-wire
Extends Selenium's Python bindings to give you the ability to inspect requests made by the browser.
 gsmith257-cyber/graphcrawler
GraphQL automated security testing toolkit
 elmasy-com/columbus-server
API-first subdomain discovery service using Certificate Transparency logs for fast, passive enumeration of subdomains via a REST API with JSON or…