
CVE-2026-26012
 diegobaelen/cve-2026-26012
Proof-of-concept exploit for CVE-2026-26012, demonstrating an authenticated organization collection permissions bypass and cipher enumeration in…
api-security-testingexploitationinformation-gathering+3
diegobaelen/cve-2026-26012Proof-of-concept exploit for CVE-2026-26012, demonstrating an authenticated organization collection permissions bypass and cipher enumeration in…
 sharma19d/cve-2025-61148
The vulnerability exists in the Student Payment API. The application fails to properly validate whether the user requesting a receipt is authorized…
 jfriedli/cve-2025-6792
Proof-of-concept exploit for CVE-2025-6792 demonstrating unauthorized Pusher channel subscription and event eavesdropping in a WordPress plugin via…
 adelittle/cve-2021-4191_exploits
Exploit script for CVE-2021-4191 that enumerates GitLab users via the GraphQL API, useful for security assessments and validating exposure.
 d0rb/packetpirate
A headless , scriptable, command-line based MITM proxy designed for network traffic interception, analysis, and modification on Windows systems.
 secsys-fdu/cve-2025-51867
Demonstrates an Insecure Direct Object Reference (IDOR) vulnerability in Deepfiction AI's chat API, allowing attackers to consume other users'…
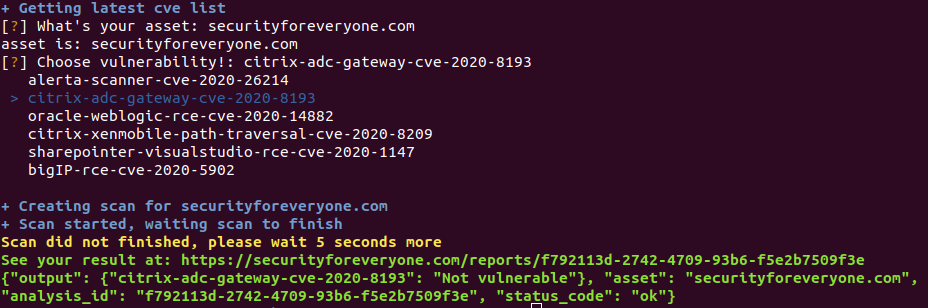 s4e-io-old-labs/s4e-cve-scanner
API-based scanner that retrieves and lists the latest Common Vulnerabilities and Exposures (CVEs) for automated security assessment and vulnerability…
 cetinpy/cve-2024-50633
Proof-of-concept exploit for CVE-2024-50633, a Broken Object Level Authorization (BOLA) vulnerability in Indico v3.2.9–v3.3.2, enabling unauthorized…
 randomrobbiebf/cve-2023-6289
Swift Performance Lite <= 2.3.6.14 - Missing Authorization to Unauthenticated Settings Export
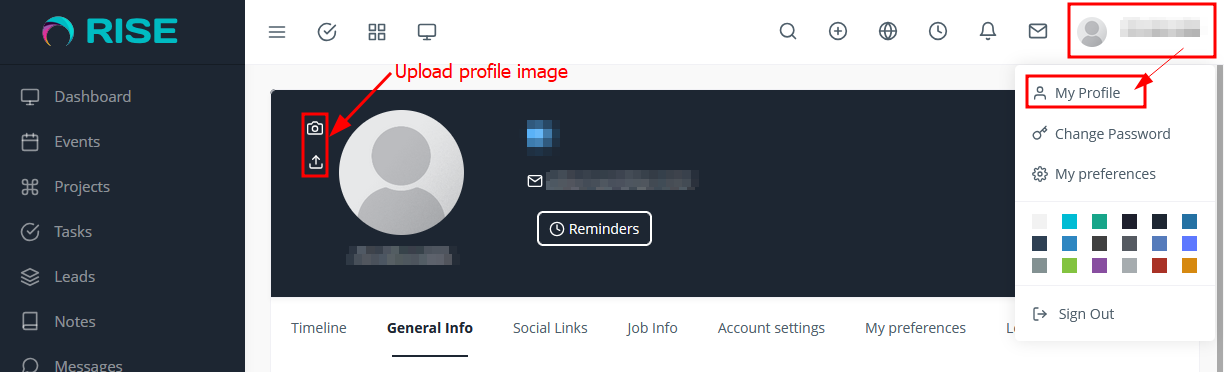 l4zyfox/rise-ultimate_project_manager_e_crm
CVE-2025-3855 - RISE Ultimate Project Manager - IDOR
 kamalx06/xxeripper
Black-box XXE scanner detecting in-band, error-based, and blind out-of-band injection via statistical baselining, parser fingerprinting, and OOB…
 wkeeling/selenium-wire
Extends Selenium's Python bindings to give you the ability to inspect requests made by the browser.
 gsmith257-cyber/graphcrawler
GraphQL automated security testing toolkit
 elmasy-com/columbus-server
API-first subdomain discovery service using Certificate Transparency logs for fast, passive enumeration of subdomains via a REST API with JSON or…