
CVE-2026-64849.yaml
 zavisco/cve-2026-64849.yaml
Detects unauthenticated MLflow webhook SSRF (CVE-2026-64849) that accesses internal or cloud metadata services and leaks response details via…
api-security-testingcloud-securityexploitation+3
zavisco/cve-2026-64849.yamlDetects unauthenticated MLflow webhook SSRF (CVE-2026-64849) that accesses internal or cloud metadata services and leaks response details via…
 nel-droid/cve-2026-71203-poc
PoC: changedetection.io unauthenticated OpenAPI schema disclosure (CVE-2026-71203, Medium 5.3)
 saboor-hakimi/cve-2023-23752
CVE-2023-23752 nuclei template
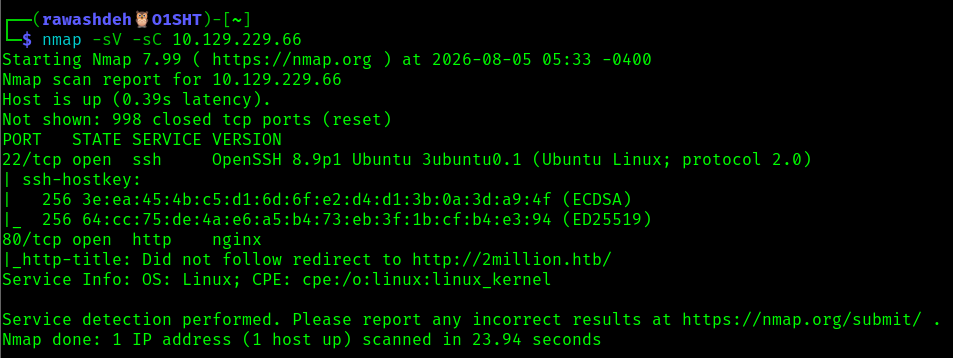 abedallarawashdeh/htb-twomillion-machine
Hack The Box TwoMillion machine writeup — JWT/invite-code bypass, IDOR, command injection, and CVE-2023-0386 privilege escalation.
 razureink/arisu
Scans public code repositories and code snippet platforms to extract and validate AI service API keys with real-time dashboard and multi-format…
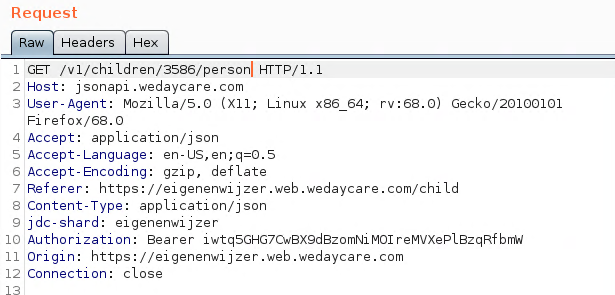 fopje/cve-2022-36539
Insecure Permissions WeDayCare
 cve-2023-49954/cve-2023-49954.github.io
SQL Injection in 3CX CRM Integration
 renzi25031469/cve-2026-19478
Detects CVE-2026-19478 in GitLab CE/EE with a non-destructive Nuclei template that triggers the GraphQL fallback-field method invocation via touch…
 aquibpro/reconix
Advanced recon engine that finds real secrets, validates them live, and builds exploit paths from client-side intelligence.
 cropnet/ni8mare
Comprehensive vulnerability detection tool for n8n workflow automation instances. Detects the critical CVE-2026-21858 vulnerability (CVSS 10.0)…
 perufitlife/directus-security
Keyless active-probe security auditor for Directus CMS. Proves public-role data exposure, user enumeration, unauthenticated version/schema leaks,…
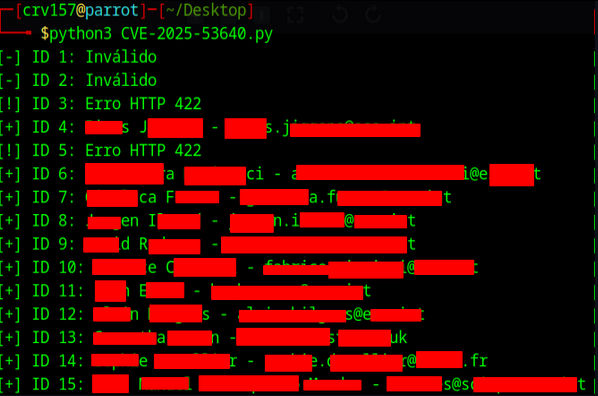 rafaelcorvino1/cve-2025-53640
Broken Object Level Authorization (BOLA) in CERN's Indico leads to authenticated user enumeration.
 randomrobbiebf/cve-2024-51665
Magical Addons For Elementor <= 1.2.1 - Authenticated (Subscriber+) Server-Side Request Forgery
 alt3kx/cve-2018-7690
The SSC REST API contains Insecure Direct Object Reference (IDOR) vulnerabilities in Fortify Software Security Center (SSC) 17.10, 17.20 & 18.10
 alt3kx/cve-2018-7691
The SSC REST API contains Insecure Direct Object Reference (IDOR) vulnerabilities in Fortify Software Security Center (SSC) 17.10, 17.20 & 18.10
 jfriedli/cve-2025-6792
Proof-of-concept exploit for CVE-2025-6792 demonstrating unauthorized Pusher channel subscription and event eavesdropping in a WordPress plugin via…
 adelittle/cve-2021-4191_exploits
Exploit script for CVE-2021-4191 that enumerates GitLab users via the GraphQL API, useful for security assessments and validating exposure.
 secsys-fdu/cve-2025-51867
Demonstrates an Insecure Direct Object Reference (IDOR) vulnerability in Deepfiction AI's chat API, allowing attackers to consume other users'…