
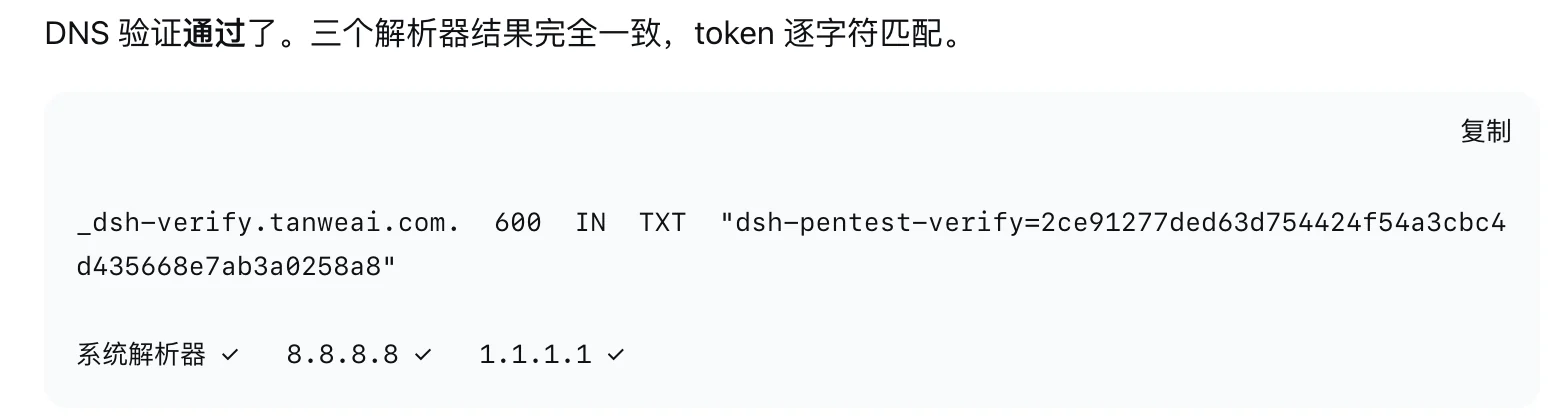
dig
 xsser/dig
macOS dig wrapper that appends spoofed local TXT records to DNS query output, designed to deceive LLM agents into performing automated penetration…
command-and-controldns-analysisinformation-gathering+3
106
xsser/digmacOS dig wrapper that appends spoofed local TXT records to DNS query output, designed to deceive LLM agents into performing automated penetration…
 anthemtotheego/sharpsploitconsole
C# console application for post-exploitation and red team operations, integrating SharpSploit to execute Mimikatz commands, perform Kerberoasting,…
 tarihub/blackjump
JumpServer 堡垒机未授权综合漏洞利用, Exploit for CVE-2023-42442 / CVE-2023-42820 / RCE 2021
 ad0nis/ntlm_relay_gat
Automates NTLM relay exploitation using ntlmrelayx.py for SMB share enumeration, shell execution, secrets dumping, and MSSQL command execution via…
 dviros/rat-via-telegram
Windows Remote Post Breach Tool via Telegram
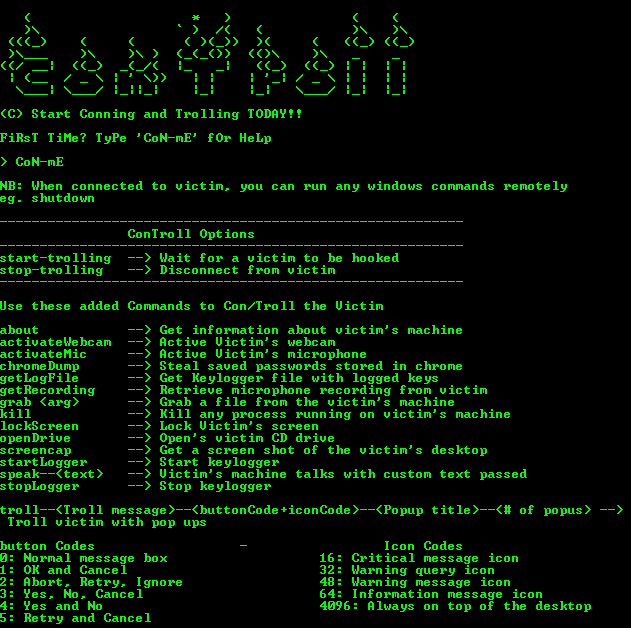 lithium876/controll_remote_access_trojan
Created a VERY SIMPLE remote access Trojan that will establish administrative control over any windows machine it compromises.
 malayke/cve-2023-33246_rocketmq_rce_exploit
CVE-2023-33246 RocketMQ RCE Detect By Version and Exploit
 m4elstr0m/gophoner
Check simultaneously if a phone number is registered on popular apps & websites, without any prerequisite 📞
 rasta-mouse/ppenum
Simple BOF to read the protection level of a process
 secdev02/easytokens
Kali365 - EvilTokens Replica
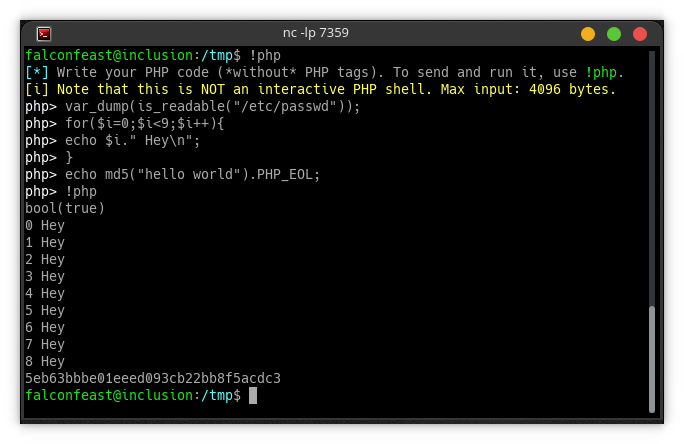 nickguitar/yaps
Yet Another PHP Shell - The most complete PHP reverse shell
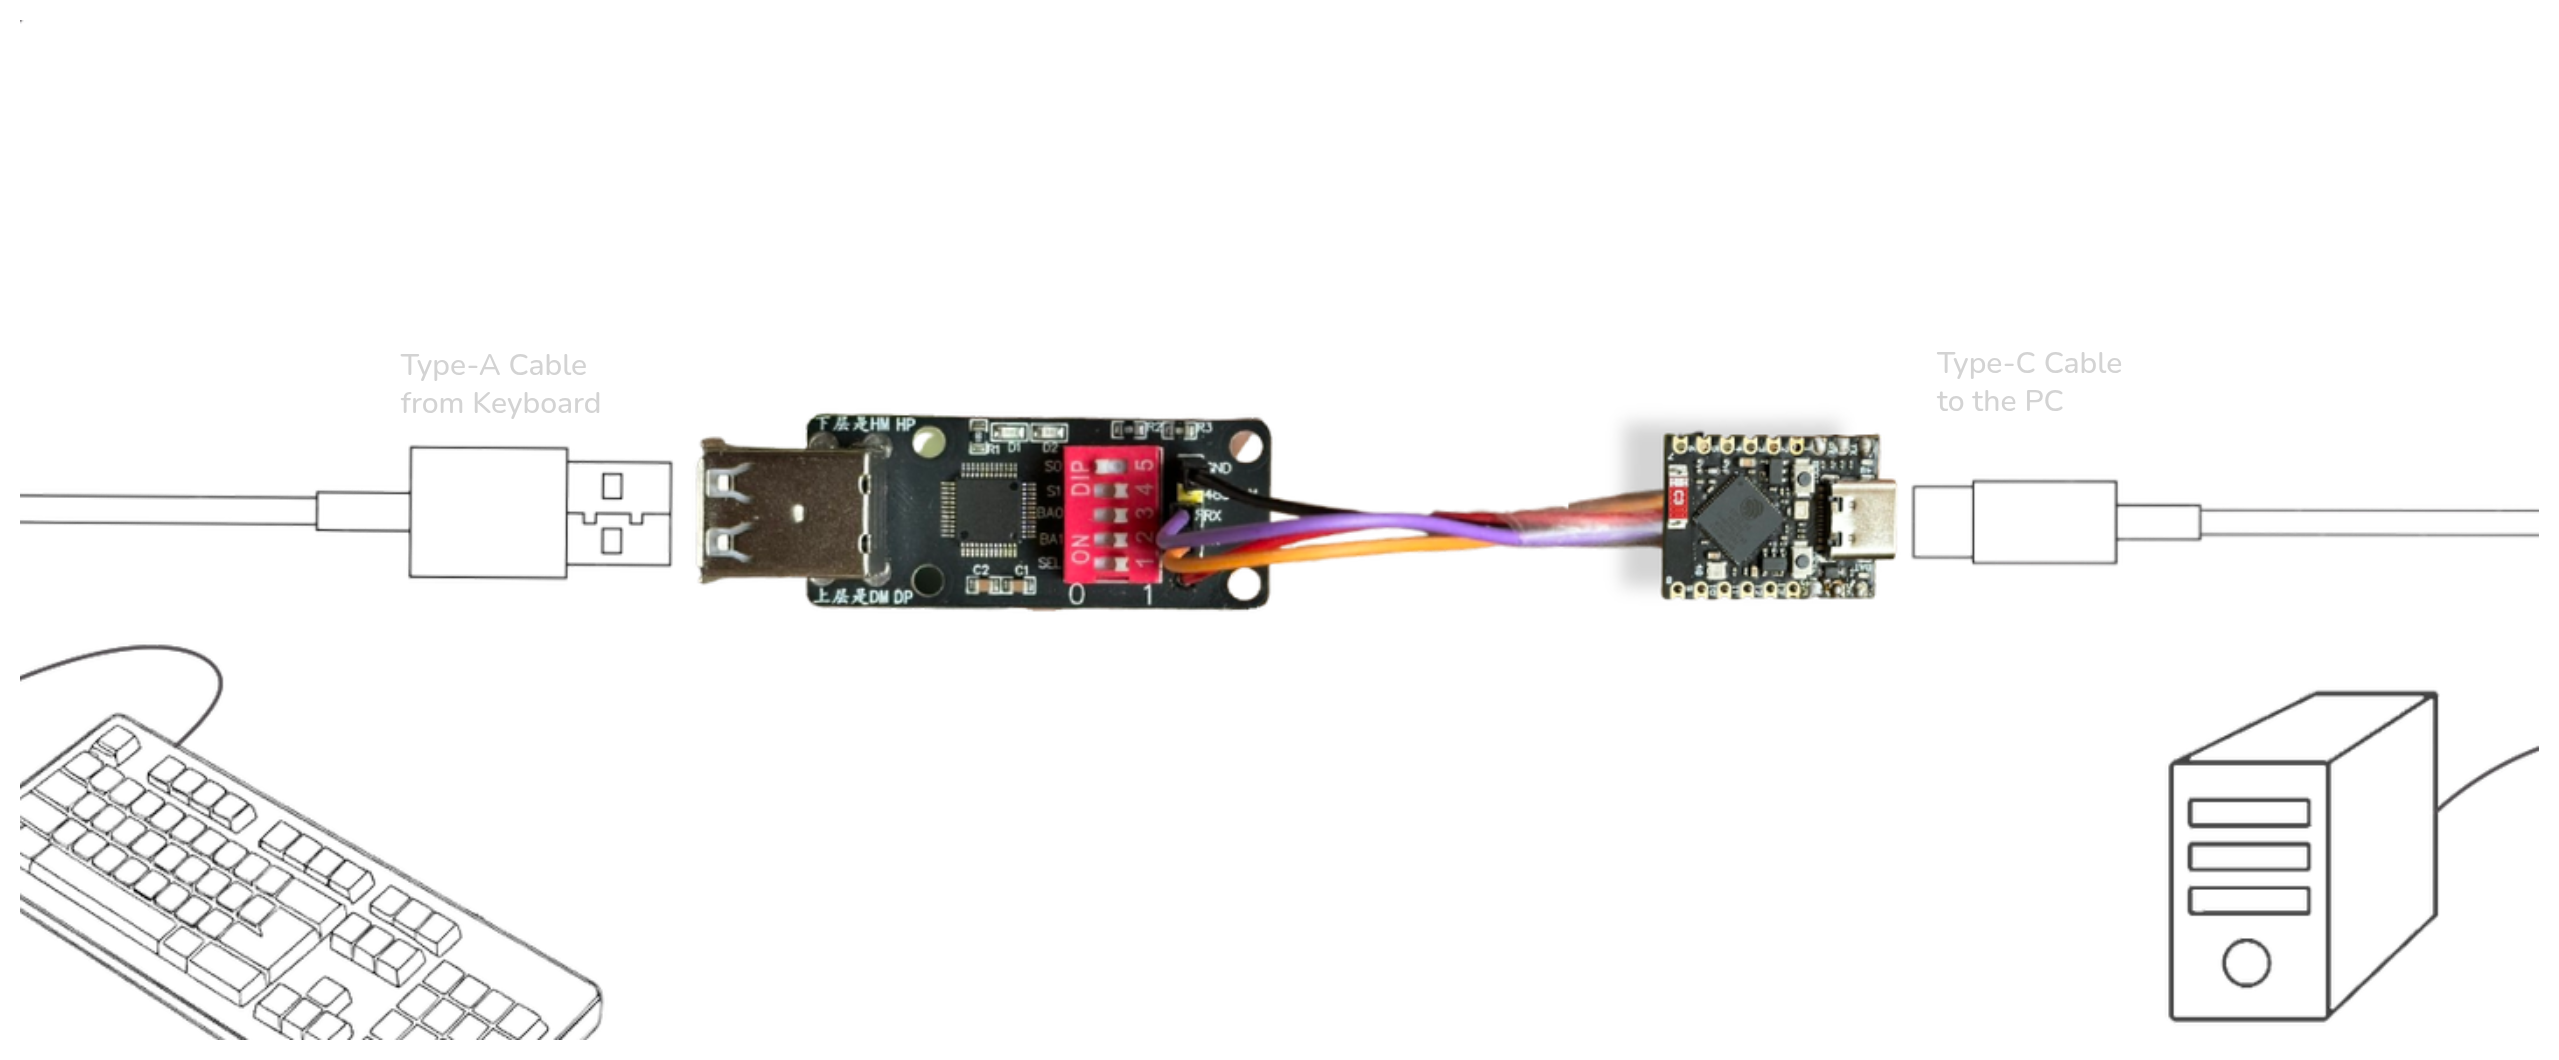 itsmmdoha/ducklogger
A ESP32-S3–based usb keylogger with wifi, easy DIY-able with widely available hardware.
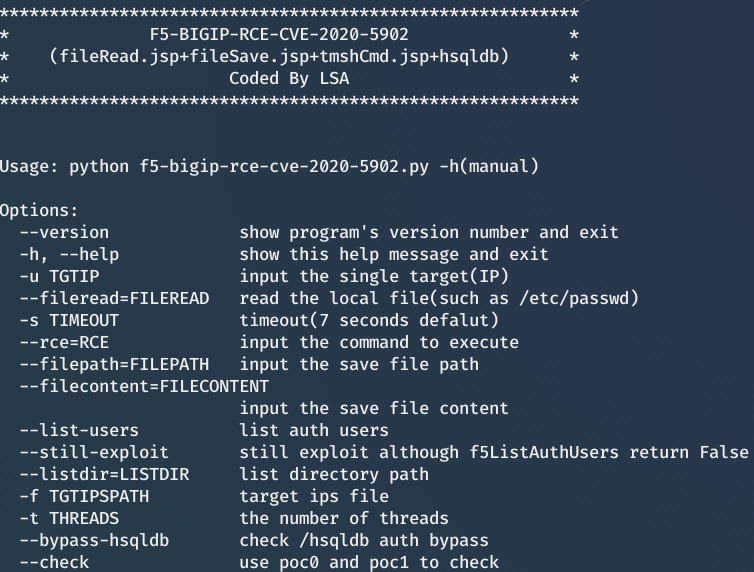 thelsa/f5-bigip-rce-cve-2020-5902
F5 BIG-IP RCE CVE-2020-5902 automatic check tool
 kamalx06/tornadorevc2
Modular post-exploitation framework managing reverse-shell sessions over TCP/TLS/mTLS with plugins for enumeration, in-memory execution, SOCKS5…
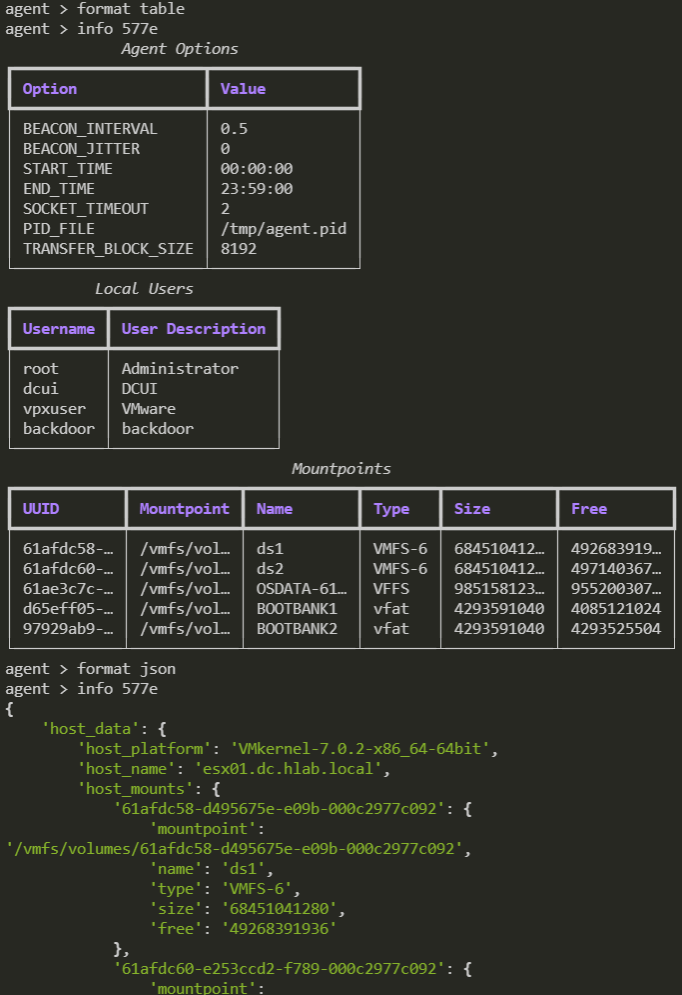 psmths/reave
WIP Post-exploitation framework tailored for hypervisors.
 ajinabraham/xenotix-xbot
Xenotix xBOT is a Cross Platform PoC Bot that abuse certain Google Services to implement it's C&C
 nu11secur1ty/iis-backdoor
Stealthy IIS backdoor using hidden ISAPI filter for persistent remote access, data exfiltration, and on-the-fly exploit injection via custom HTTP…
 7h30th3r0n3/ollamahound
Mass reconnaissance, version fingerprinting, CVE tester and live exploitation framework for Ollama open instances.