Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
68 results
CVE-2020-1938_Ghostcat-PoC preview

CVE-2020-1938_Ghostcat-PoC

GitHubabrewer251/cve-2020-1938_ghostcat-poc

Apache Tomcat AJP Ghostcat (CVE-2020-1938) exploit tool for file disclosure with multi-target scanning, custom wordlists, and upload point detection…

exploitationinformation-gatheringpayload-generation+3
9 months ago
CVE-2025-53770-Vulnerable-Scanner preview

CVE-2025-53770-Vulnerable-Scanner

GitHubimbas007/cve-2025-53770-vulnerable-scanner

Python script to scan SharePoint hosts for CVE-2025-53770 using custom payloads, with optional Burp Suite proxy interception for traffic analysis and…

exploitationinformation-gatheringpenetration-testing+3
11 year ago
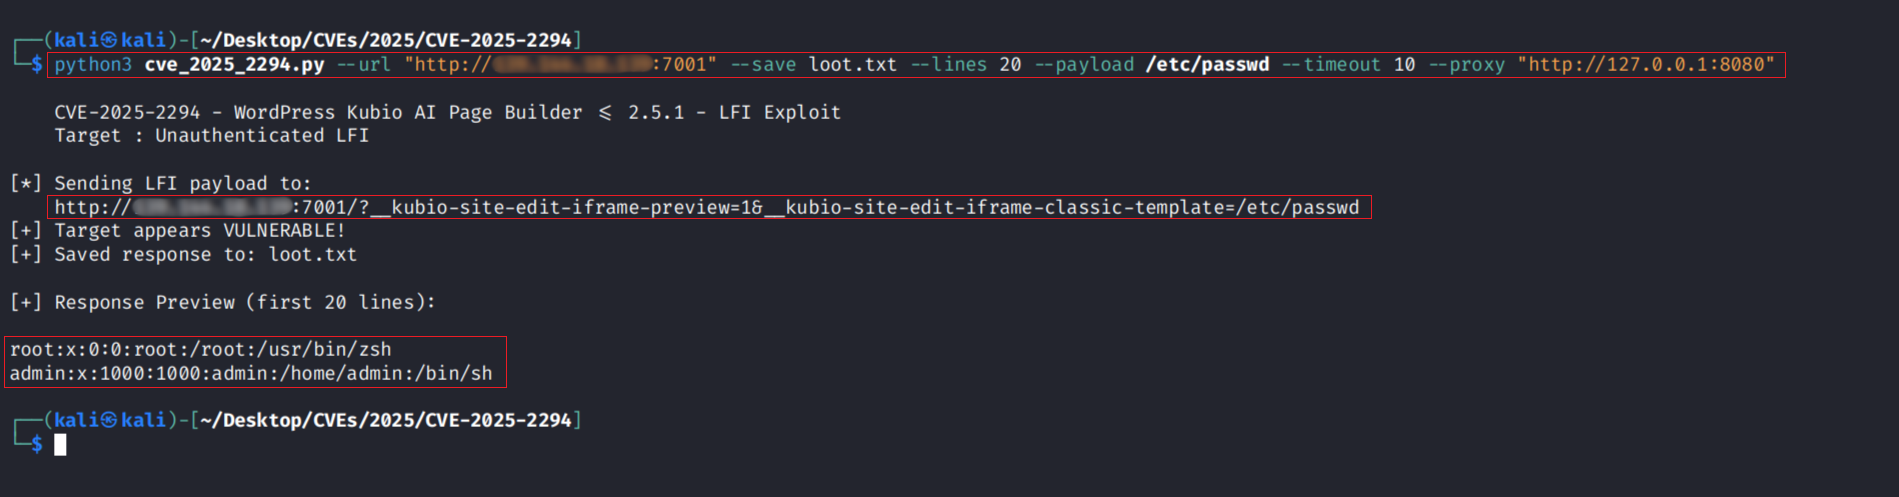
CVE-2025-2294 preview

CVE-2025-2294

GitHubr0otk3r/cve-2025-2294

Python exploit script for CVE-2025-2294, an unauthenticated Local File Inclusion vulnerability in WordPress Kubio AI Page Builder ≤ 2.5.1. Supports…

code-analysisexploitationinformation-gathering+3
1 year ago
CVE-2024-27954 preview

CVE-2024-27954

GitHubr0otk3r/cve-2024-27954

Python-based scanner for CVE-2024-27954, a Local File Inclusion vulnerability in the WordPress wp-automatic plugin. Supports multithreaded scanning,…

educationexploitationinformation-gathering+3
1 year ago
SIGINT_THROUGH_BROTHER_PRINTERS preview

SIGINT_THROUGH_BROTHER_PRINTERS

GitHubspiralbl0ck/sigint_through_brother_printers

Exploit vulnerable Brother printers via CVE-2017-7588, collect data, and develop custom firmware implants for attack simulation.

embedded-systems-securityexploitationfirmware-analysis+6
2 years ago
CVE-2015-1635 preview

CVE-2015-1635

GitHubh3x0v3rl0rd/cve-2015-1635

Python exploit for CVE-2015-1635 (MS15-034) targeting HTTP.sys remote code execution vulnerability in IIS servers. Supports custom arguments for…

exploitationinformation-gatheringpenetration-testing+2
5 years ago
CVE-2025-2294 preview

CVE-2025-2294

GitHubmrrivaldo/cve-2025-2294

Unauthenticated Local File Inclusion (LFI) exploit for Kubio Page Builder WordPress plugin (CVE-2025-2294). Supports single target, bulk scanning,…

exploitationinformation-gatheringpenetration-testing+3
1 year ago
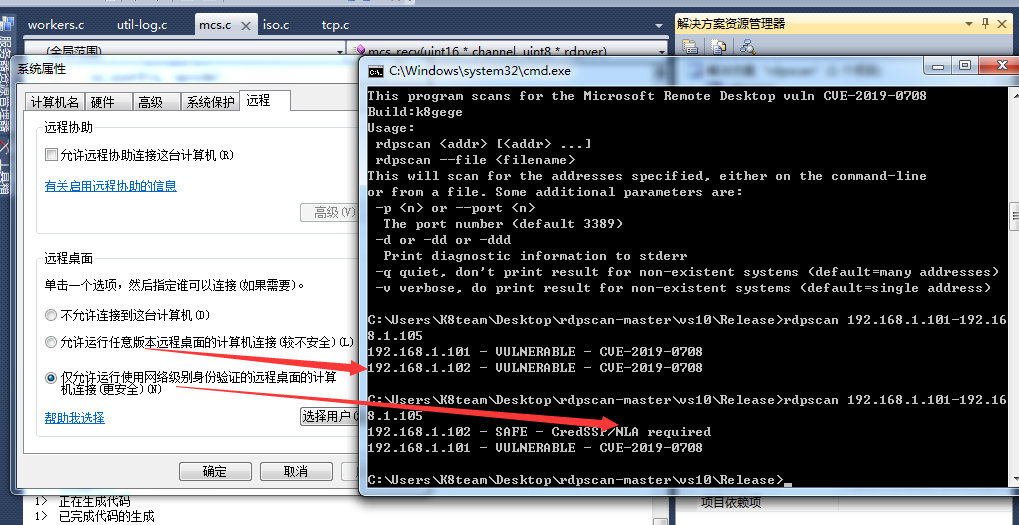
CVE-2019-0708-scan preview

CVE-2019-0708-scan

GitHublisinan988/cve-2019-0708-scan

Batch scanner for CVE-2019-0708 (BlueKeep) RDP vulnerability with Windows and Linux support, using rdpscan and custom Cscan for mass IP range…

exploitationinformation-gatheringnetwork-security+3
4 years ago
CVE-2025-30208-PoC preview

CVE-2025-30208-PoC

GitHubisee857/cve-2025-30208-poc

Multi-threaded Python scanner for CVE-2025-30208 Vite path traversal vulnerability with custom payload support, batch scanning, and proxy debugging.

exploitationinformation-gatheringpenetration-testing+3
1 year ago
WordList preview

WordList

GitHubrix4uni/wordlist

Curated collection of custom wordlists for fuzzing, DNS enumeration, parameter discovery, and default credentials, plus a Go generator for nuclei…

dns-subdomain-enumerationfuzzinginformation-gathering+6
1533 months ago
reverse-engineering-browser preview

reverse-engineering-browser

GitHubsunghoojung/reverse-engineering-browser

Local-first macOS research browser built on a custom Brave build that captures network traffic, fingerprints, scripts, and runtime evidence for…

code-analysisdebuggersdynamic-analysis-sandboxing+9
53 days ago
melody preview
Archived

melody

GitHubma111e/melody

Melody is a transparent internet sensor built for threat intelligence. Supports custom tagging rules and vulnerable application simulation.

information-gatheringintrusion-detectionnetwork-security+5
1391 year ago
pulsar preview
Archived

pulsar

GitHub0x0fb0/pulsar

Network footprint scanner platform. Discover domains and run your custom checks periodically.

cloud-securitydns-subdomain-enumerationinformation-gathering+6
4294 years ago
icannTLD preview

icannTLD

GitHubcorelight/icanntld

Zeek script using the official ICANN Top-Level Domain (TLD) list with the Input Framework to extract the relevant information from a DNS query and…

dns-analysisinformation-gatheringintrusion-detection+3
81 year ago
nmap preview

nmap

GitHubnmap/nmap

High-performance network discovery and security auditing tool with advanced port scanning, OS detection, service version detection, and scriptable…

bluetooth-securitydatabase-securitydata-exfiltration+18
13.7k22h 28m ago
scan4all preview

scan4all

GitHubghosttroops/scan4all

Official repository vuls Scan: 15000+PoCs; 23 kinds of application password crack; 7000+Web fingerprints; 146 protocols and 90000+ rules Port…

dns-subdomain-enumerationexploit-frameworksfuzzing+9
6.2k2 years ago
S3Scanner preview

S3Scanner

GitHubsa7mon/s3scanner

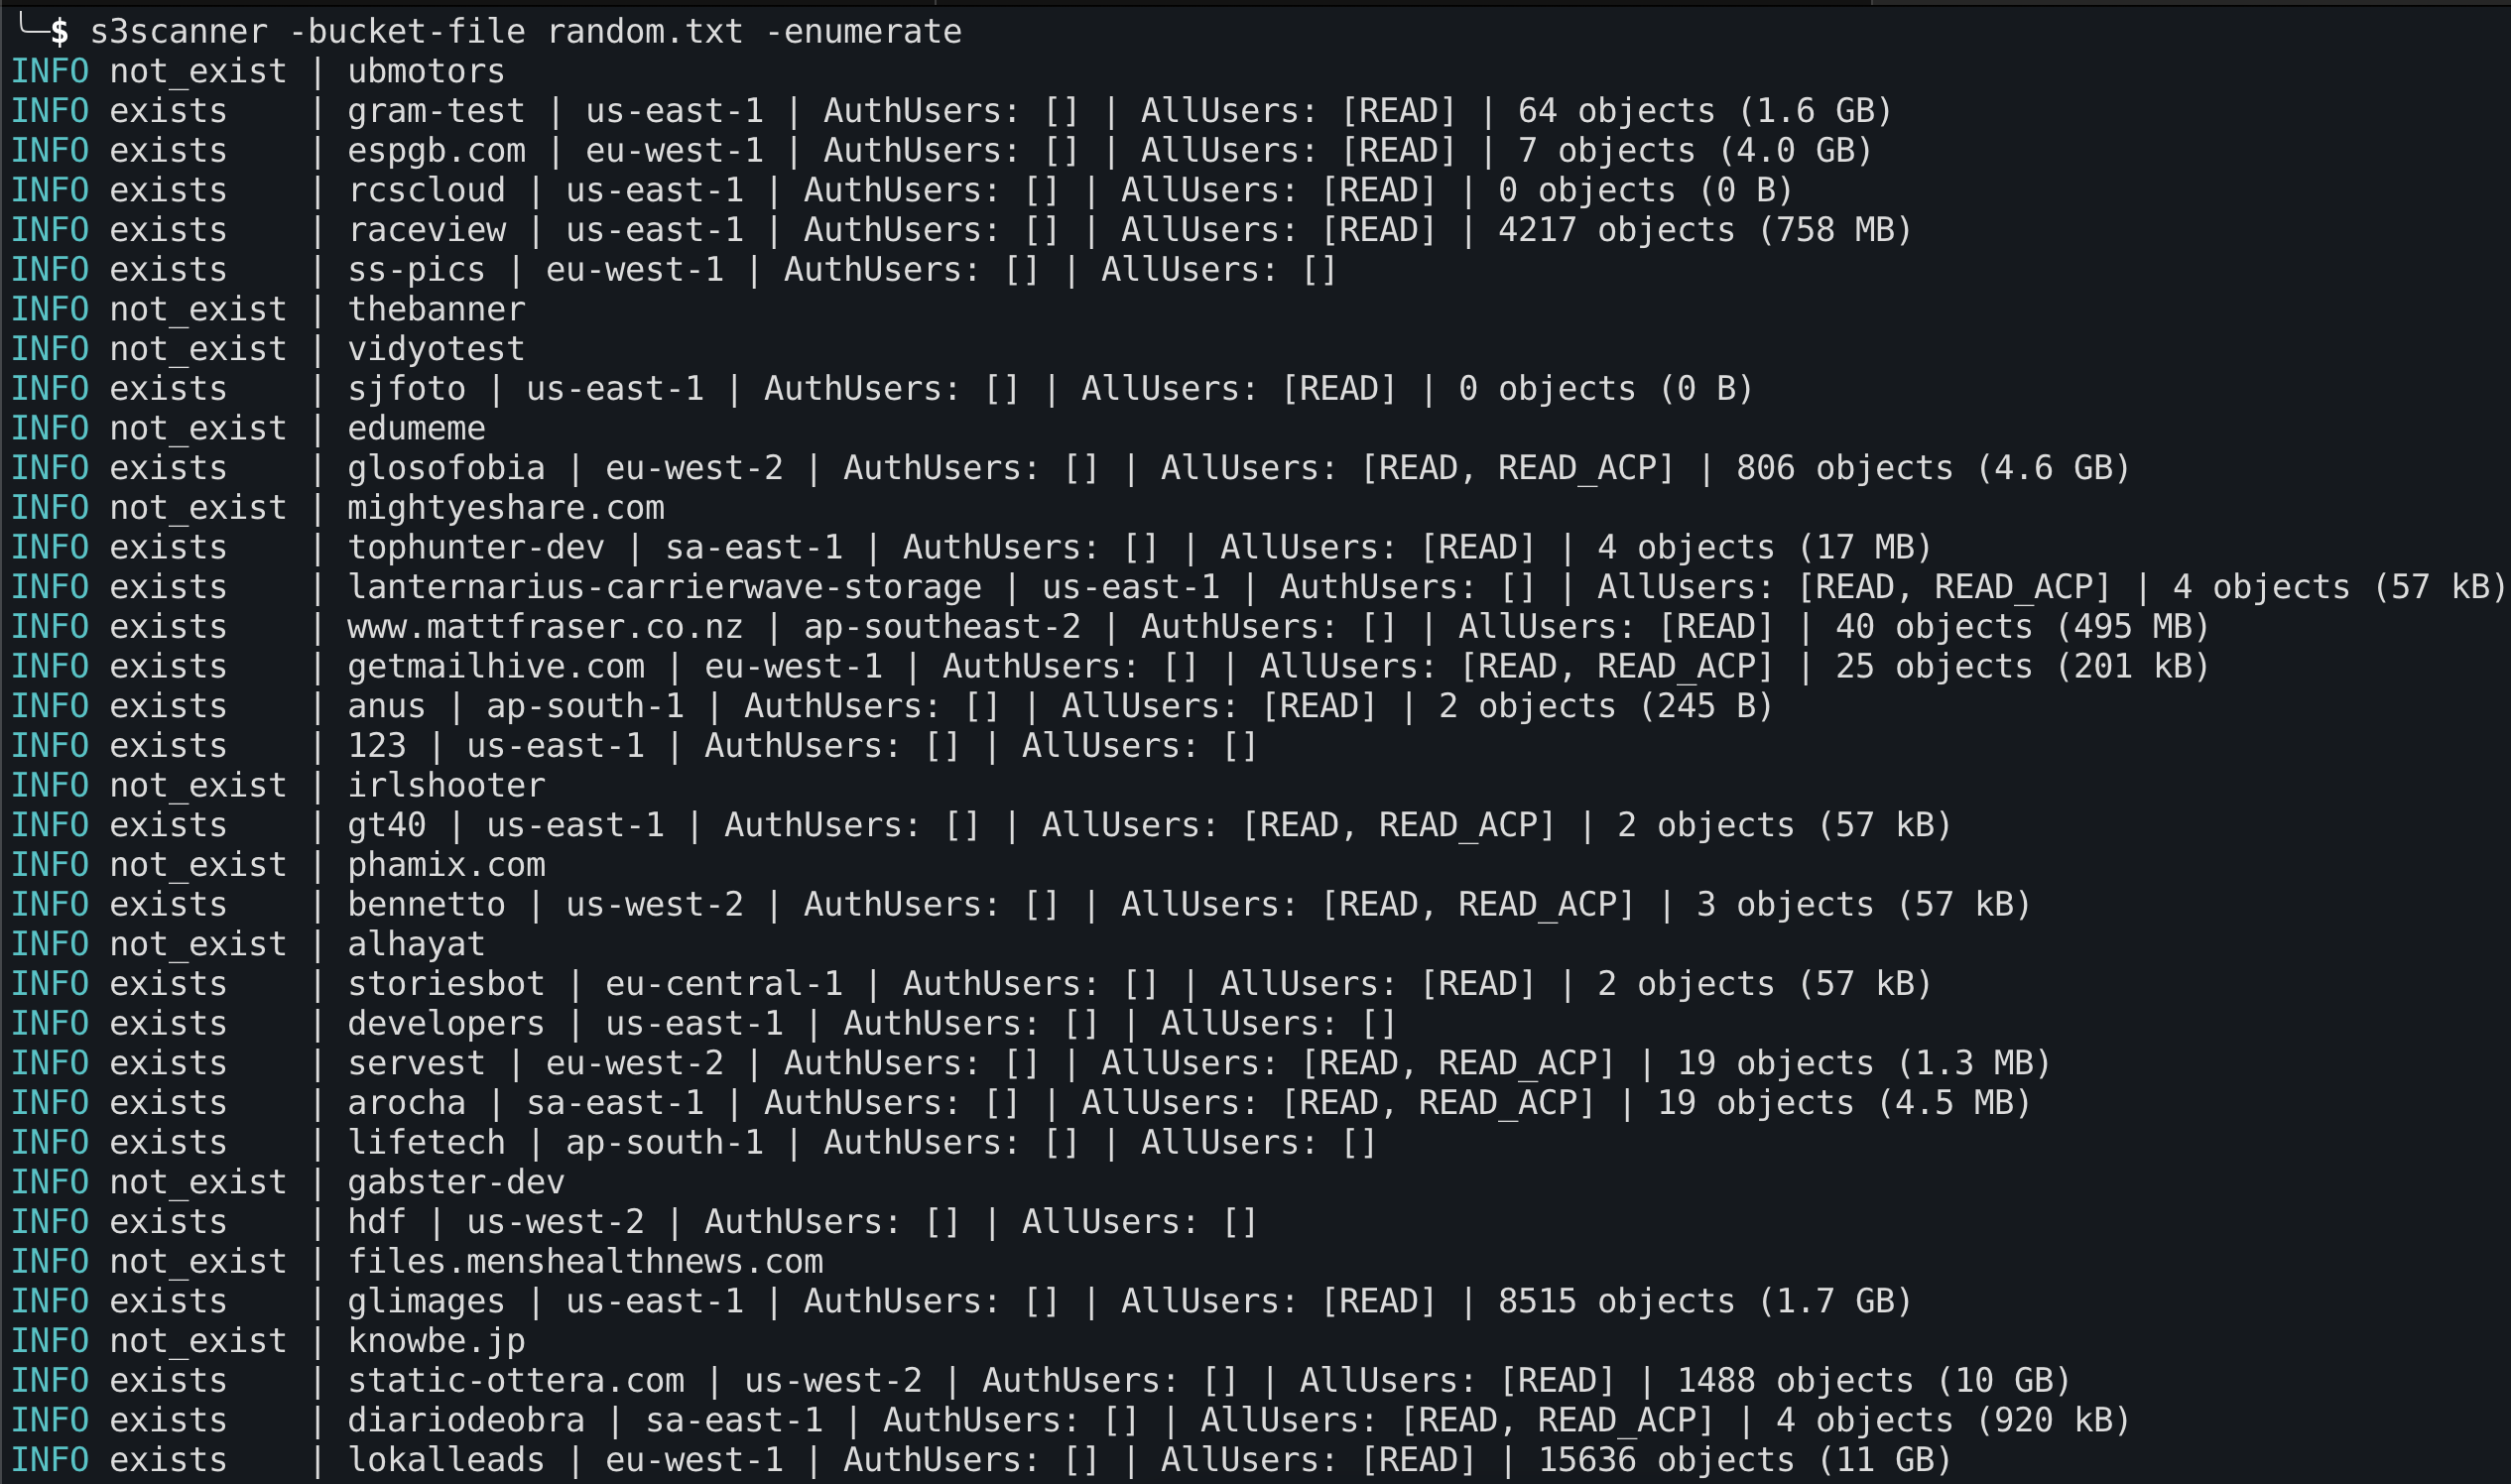
Scan for misconfigured S3 buckets across S3-compatible APIs!

cloud-securityinformation-gatheringmisconfiguration+1
3.2k2 months ago
singularity preview

singularity

GitHubnccgroup/singularity

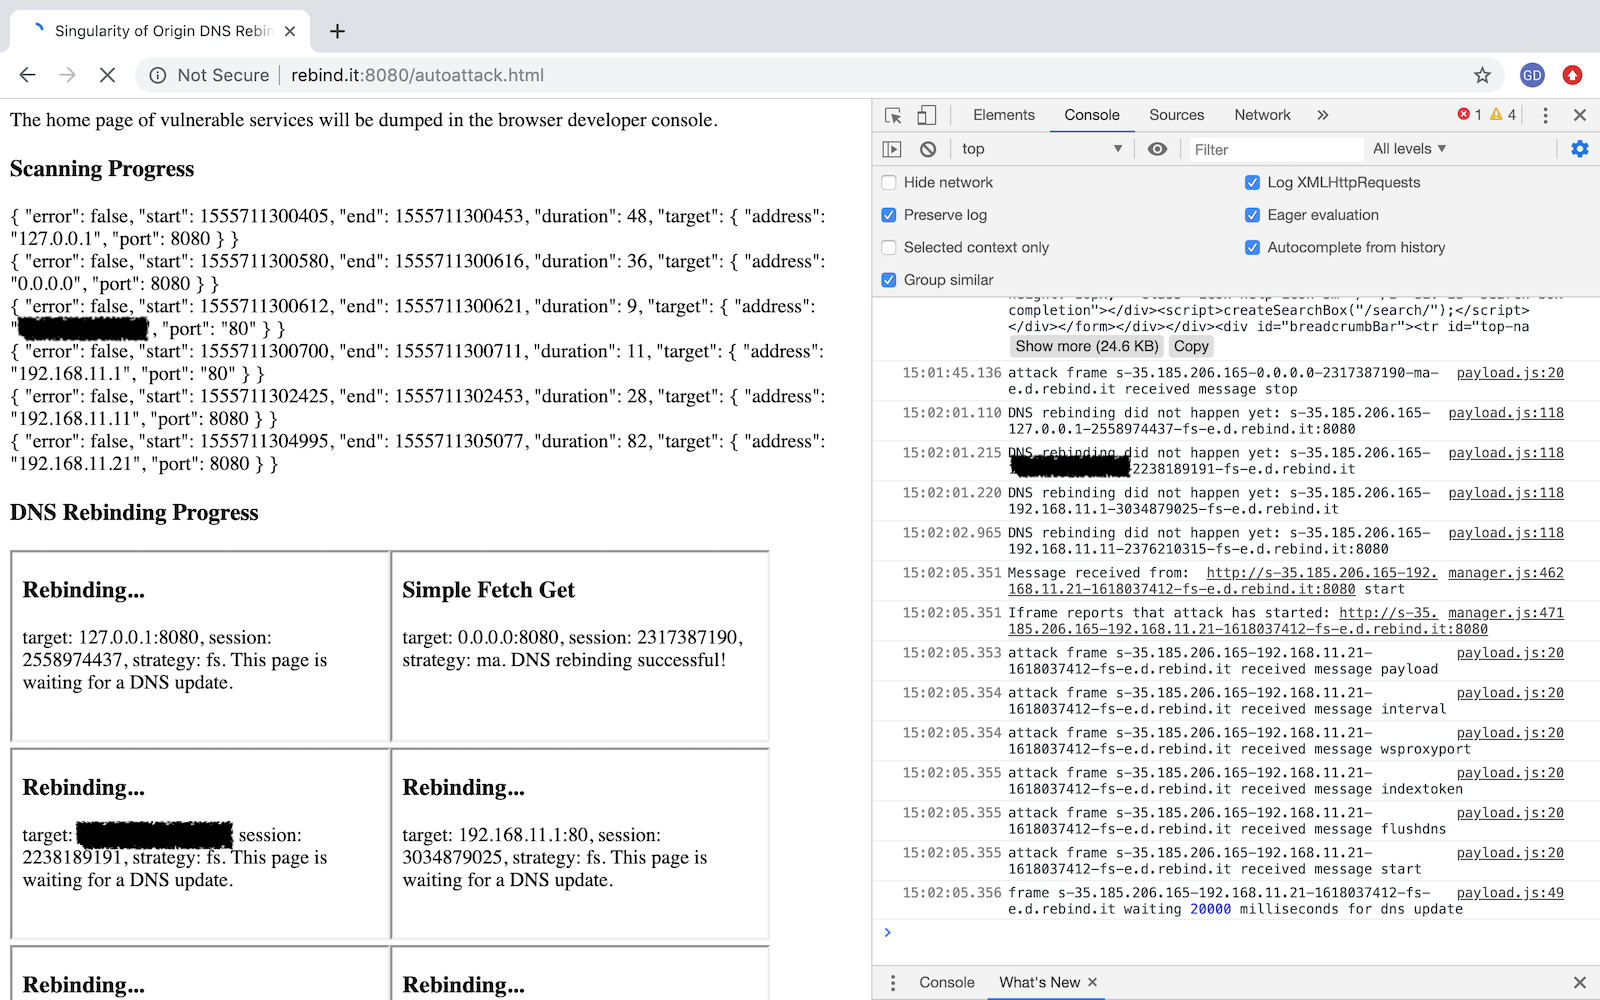
A DNS rebinding attack framework.

dns-analysisexploitationinformation-gathering+6
1.3k2 months ago
Previous1234Next