
udpx
 nullt3r/udpx
Single-packet UDP scanner in Go for fast discovery of 45+ services across networks, supporting custom probes, CIDR scanning, and JSONL output.
information-gatheringnetwork-securityport-scanning+2
238
nullt3r/udpxSingle-packet UDP scanner in Go for fast discovery of 45+ services across networks, supporting custom probes, CIDR scanning, and JSONL output.
 mrcl0wnlab/scanner-inurlbr
Advanced search in search engines, enables analysis provided to exploit GET / POST capturing emails & urls, with an internal custom validation…
 smiegles/mass3
Multi-threaded DNS-based enumeration tool for discovering AWS S3 buckets using pre-compiled wordlists and custom DNS resolvers, with optional Docker…
 anof-cyber/paraforge
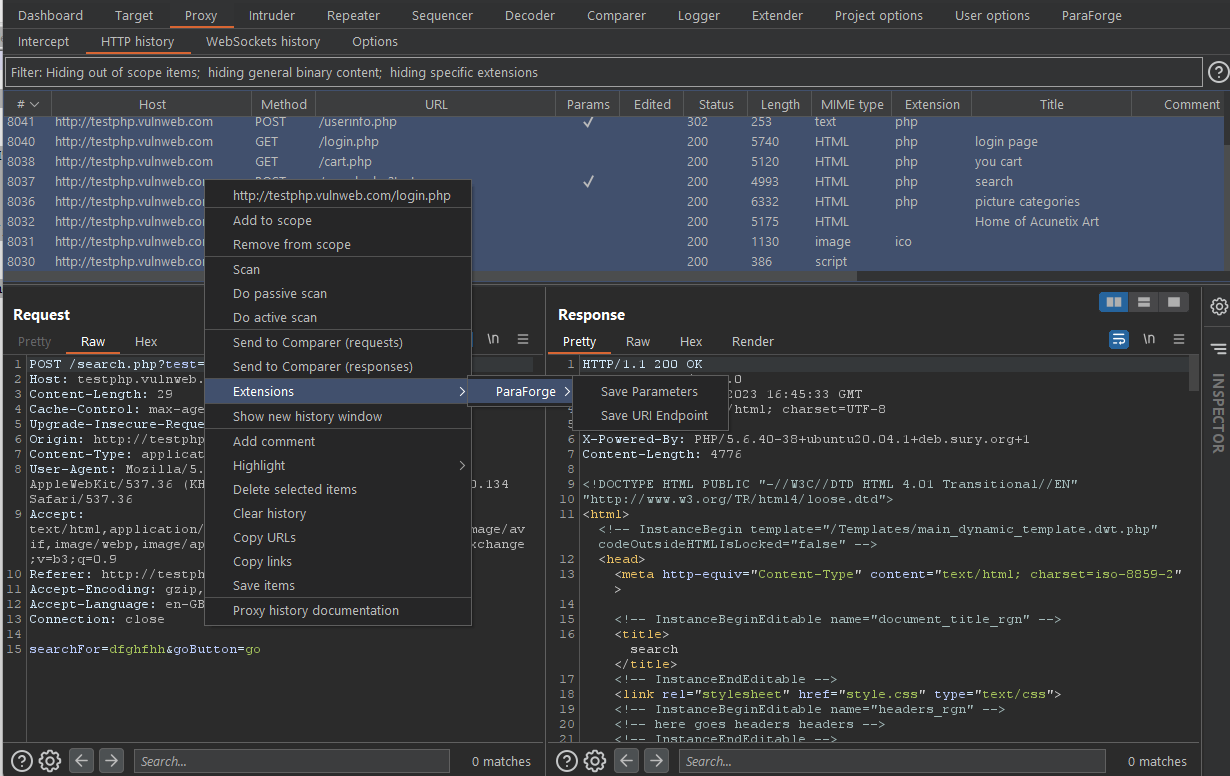
A BurpSuite extension to create a custom word-list of endpoint and parameters for enumeration and fuzzing
 h43z/dns-rebinding-tool
dns rebind tool with custom scripts
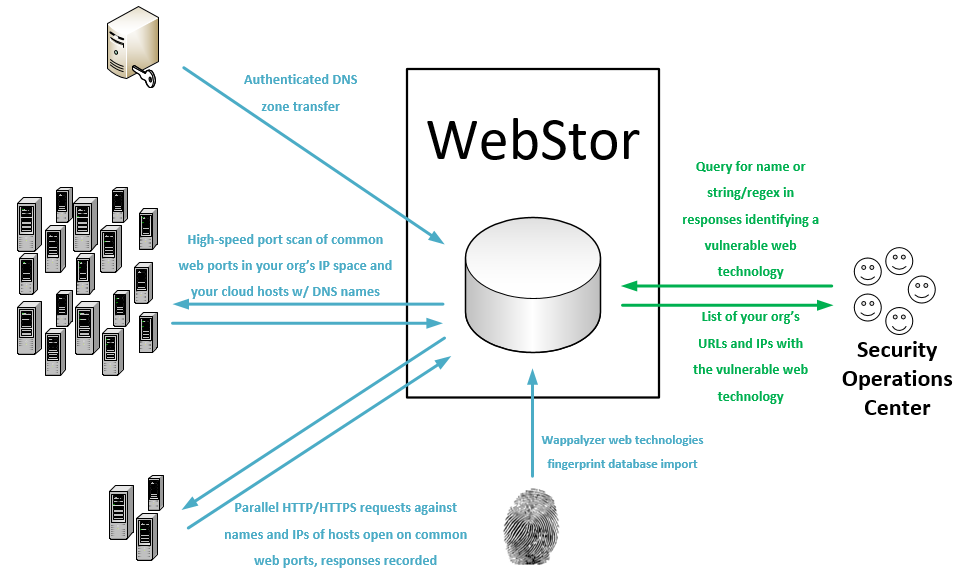 rossgeerlings/webstor
Enumerates all websites across an organization's networks via DNS zone transfers and masscan, stores responses, and enables querying for known…
 nu11secur1ty/iis-backdoor
Stealthy IIS backdoor using hidden ISAPI filter for persistent remote access, data exfiltration, and on-the-fly exploit injection via custom HTTP…
 iamagarre/badexclusionsnwbo
BadExclusionsNWBO is an evolution from BadExclusions to identify folder custom or undocumented exclusions on AV/EDR
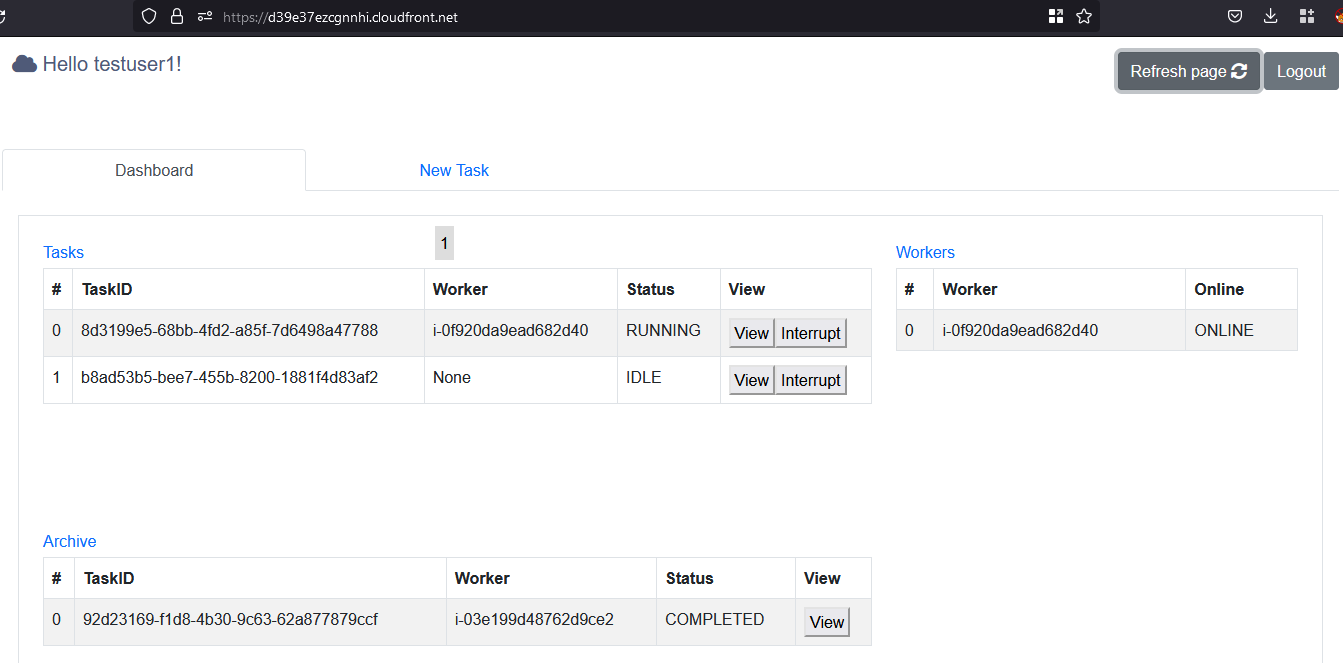 nccgroup/cowcloud
Serverless AWS solution for distributing recon and vulnerability scanning workloads. Submit tasks via web UI; EC2 workers execute custom Python…
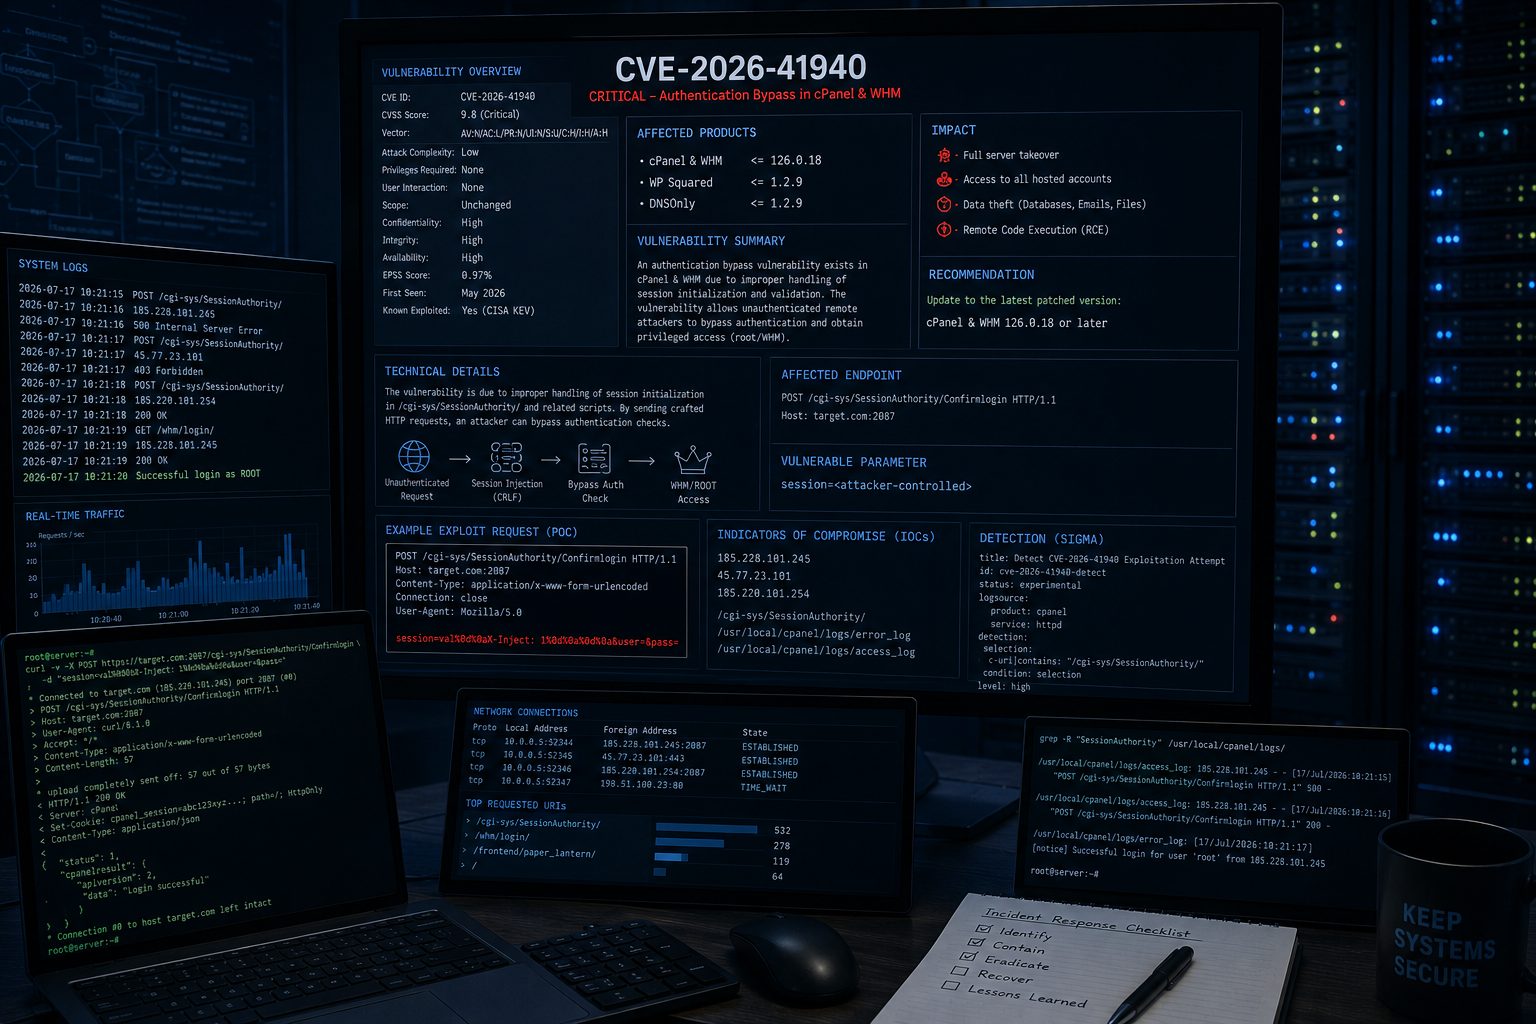 tc4dy/cve-2026-41940-poc-exploit
🚀 CVE-2026-41940 cPanel/WHM Auth Bypass Exploit - Best Flow 💥 CRLF injection leads to auth bypass, session hijacking & account leak. ✅ Proxy,…
 ht0ruial/cve-2019-0708poc-batchscanning
Batch scanning tool for CVE-2019-0708 (BlueKeep) vulnerability detection on Windows systems, supporting single and multi-IP scanning with custom IP…
 joshuavanderpoll/cve-2026-49772
Blind SQL injection exploit for CVE-2026-49772 targeting The Events Calendar WordPress plugin. Extracts database contents via boolean/time-based…
 tc4dy/cve-2026-29000-poc-exploit
CVE-2026-29000 – pac4j-jwt Authentication Bypass (🔥 CVSS 10.0). One-click admin forge via public key JWE wrapping. Leaks configs, users, secrets.…
 cyberthreatanalysis/esxi-ransomware-scanner-mi
ESXi EZ - A custom scanner that takes list of IPs either in JSON, CSV or individually and checks for infection CVE-2021-21974
 jenderal92/fofa-api-threaded-searcher
Multi‑threaded Python tool to query FOFA API, extract custom fields (IP, port, cert, TLS, etc.), deduplicate results, and resume interrupted searches.
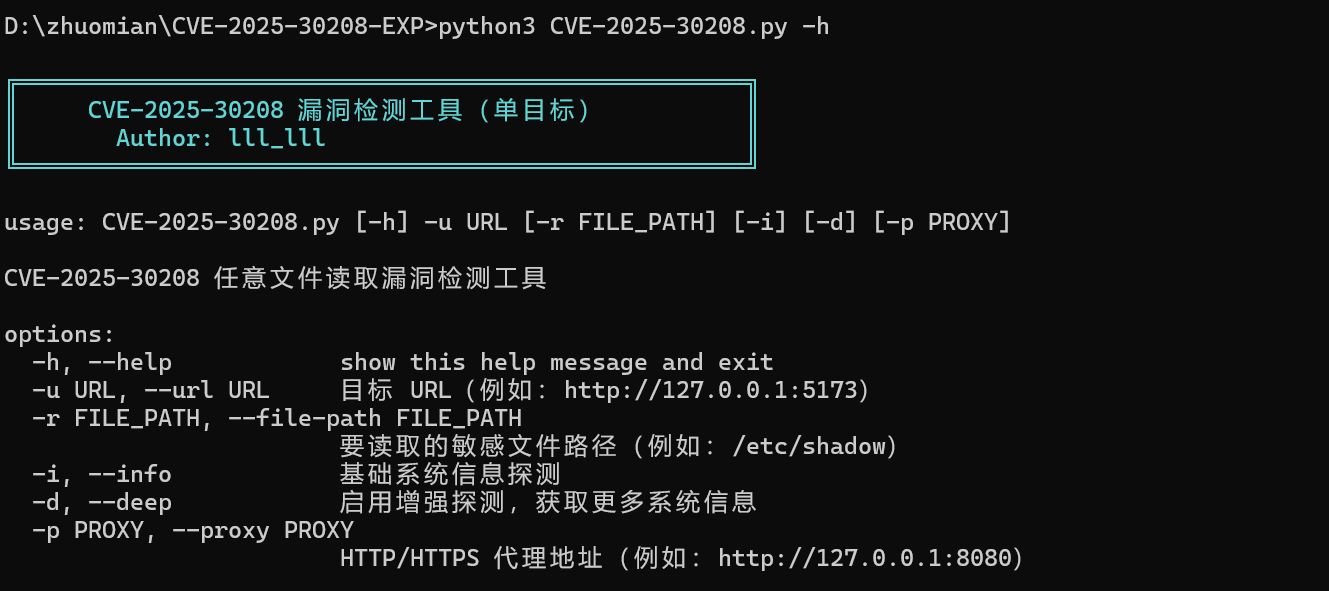 lilil3333/vite-cve-2025-30208-exp
Python-based exploit for CVE-2025-30208 targeting Vite dev server arbitrary file read. Supports single-target detection, custom file paths, system…
 goomdan/cve-2016-6210-exploit
Custom exploit written for enumerating usernames as per CVE-2016-6210
 fernandobortotti/cve-2024-24919
Automated exploit for CVE-2024-24919 with API-based vulnerable IP discovery and LFI brute-force using custom wordlists. Designed for educational…