
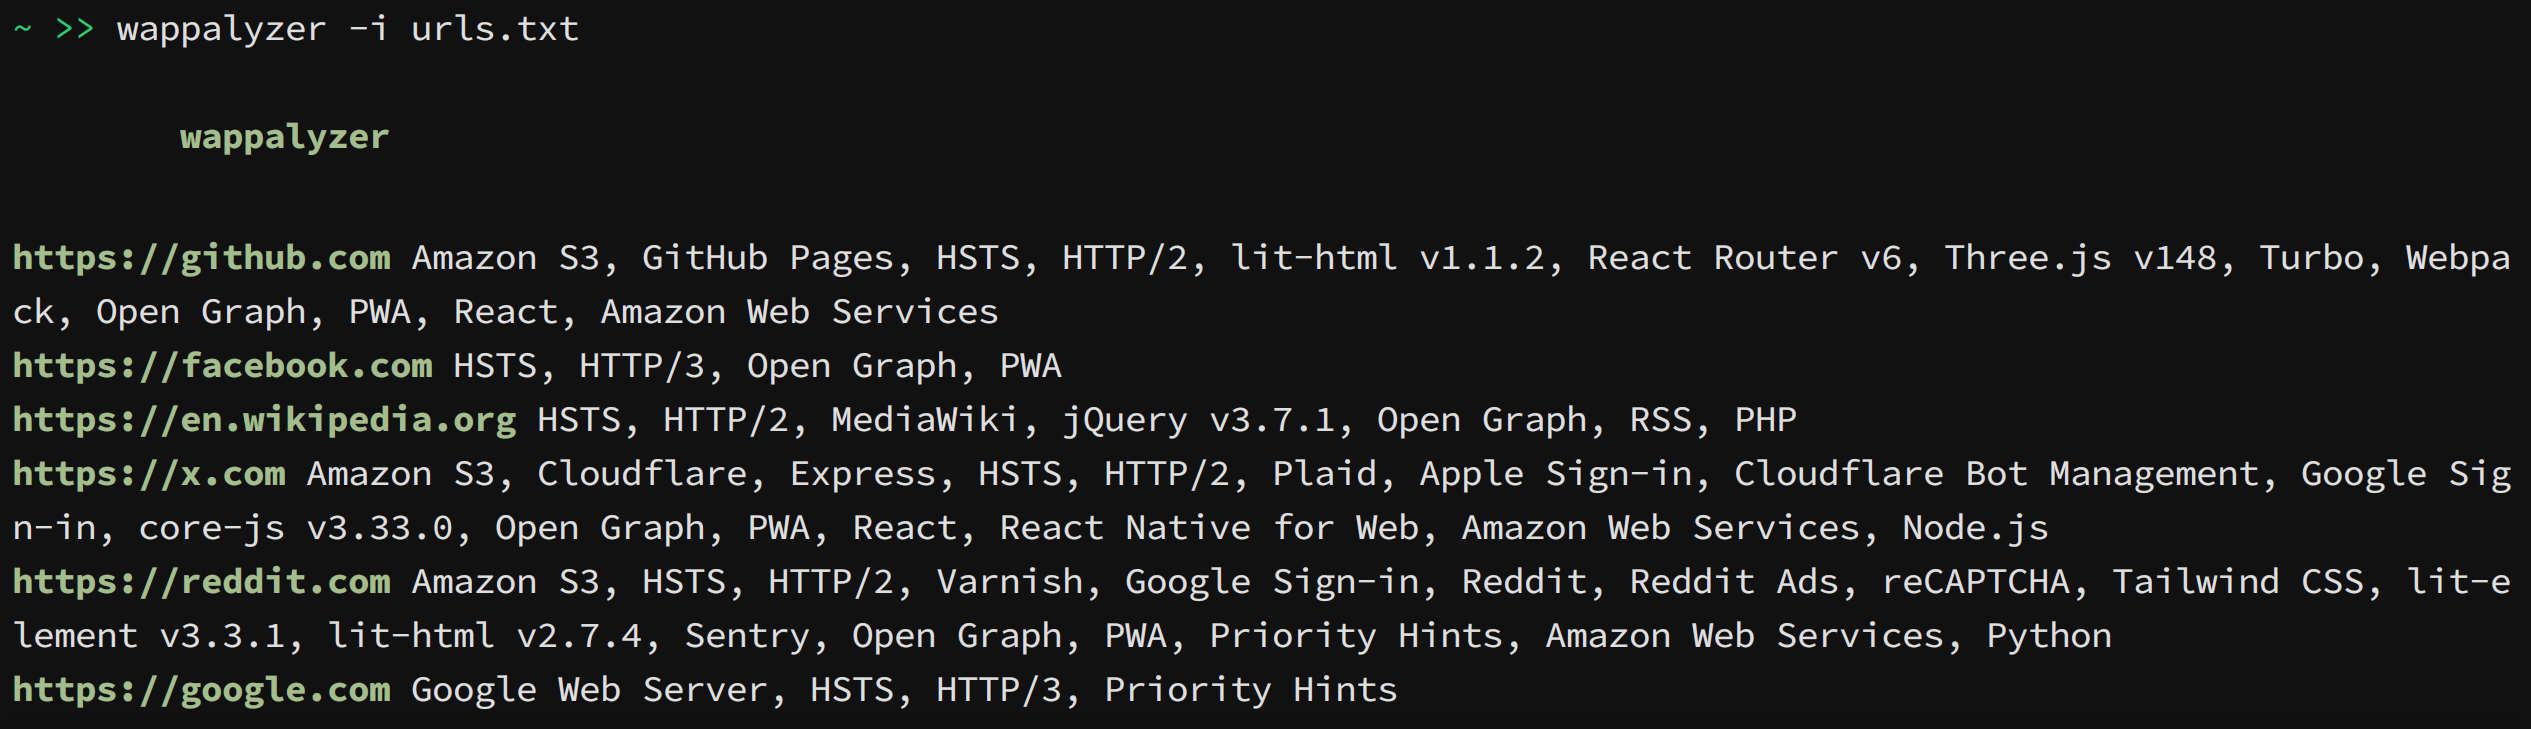
wappalyzer-next
 s0md3v/wappalyzer-next
detect technologies with wappalyzer alternative
crawlerinformation-gatheringreconnaissance+1
s0md3v/wappalyzer-nextdetect technologies with wappalyzer alternative
 wkovacs64/pwned
CLI tool to query the Have I Been Pwned API for breached accounts, pastes, and password exposure, enabling rapid security assessment of compromised…
 majd/ipatool
Command-line tool that allows you to search for iOS, iPadOS, tvOS, visionOS, and macOS apps on the App Store, and download .ipa or macOS .pkg app…
 sec-dan/wp2shell-scanner
Read-only CLI to check whether a WordPress site is exposed to WP2Shell (CVE-2026-63030 / CVE-2026-60137)
 exdev994/cve-2026-4631-cockpit-rce
Unauthenticated Remote Code Execution via SSH Command-Line Argument Injection Cockpit versions 327 – 359 | CVSS 9.8 Critical | CWE-78
 rix4uni/cve-2025-55182
A command-line tool for detecting CVE-2025-55182 and CVE-2025-66478 in Next.js applications using React Server Components.
 s_r_e_e_r_a_j/ftpbuster
FTPBuster is a powerful command-line brute-forcing tool designed to brute-force FTP, SFTP, and explicit FTPS servers by performing dictionary-based…
 reverseclabs/azuredevops-enum
Read-only Azure DevOps enumeration tool that queries the REST API to surface projects, repositories, service connections, builds, pipeline secrets,…
 dominicbreuker/pspy
Monitor linux processes without root permissions
 rapiddns/rapiddns-cli
A powerful command-line interface for interacting with the [RapidDNS API](https://rapiddns.io/help/api). This tool allows you to perform DNS…
 hueristiq/xsubfind3r
Passive subdomain discovery tool that aggregates results from multiple online sources via CLI, supporting stdin/stdout, JSONL output, and API key…
 hueristiq/xurlfind3r
Passive URL discovery tool that collects domain-associated URLs from multiple public sources via command-line, supporting stdin/stdout and JSONL…
 byt3hx/jsleak
Concurrent CLI tool for discovering secrets, API keys, and links in JavaScript files during web reconnaissance, with custom regex pattern support and…
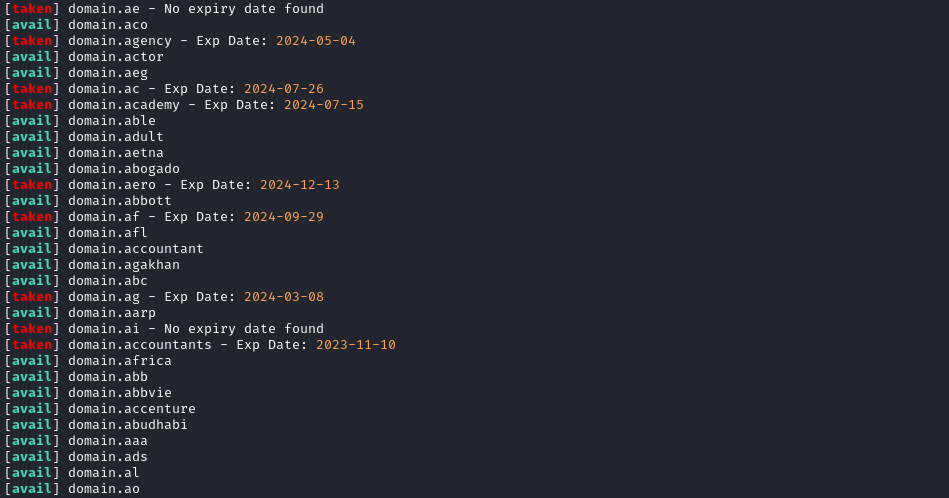 yuyudhn/tldhunt
Bash-based domain availability checker that scans WHOIS records across multiple TLDs to find unregistered domains for red teaming and phishing…
 anonkryptiquz/nextsploit
NextSploit is a command-line tool designed to detect and exploit CVE-2025-29927, a security flaw in Next.js
 pixilated730/nextjs-exploit-
CVE-2025-29927
 cappricio-securities/crlfi
This is a tool used by several security researchers to find Carriage Return Line Feed Injection Bug
 0zer0d4y/fuegotest
A CLI tool for detecting CVE-2023-20048 vulnerability in Cisco Firepower Management Center.