
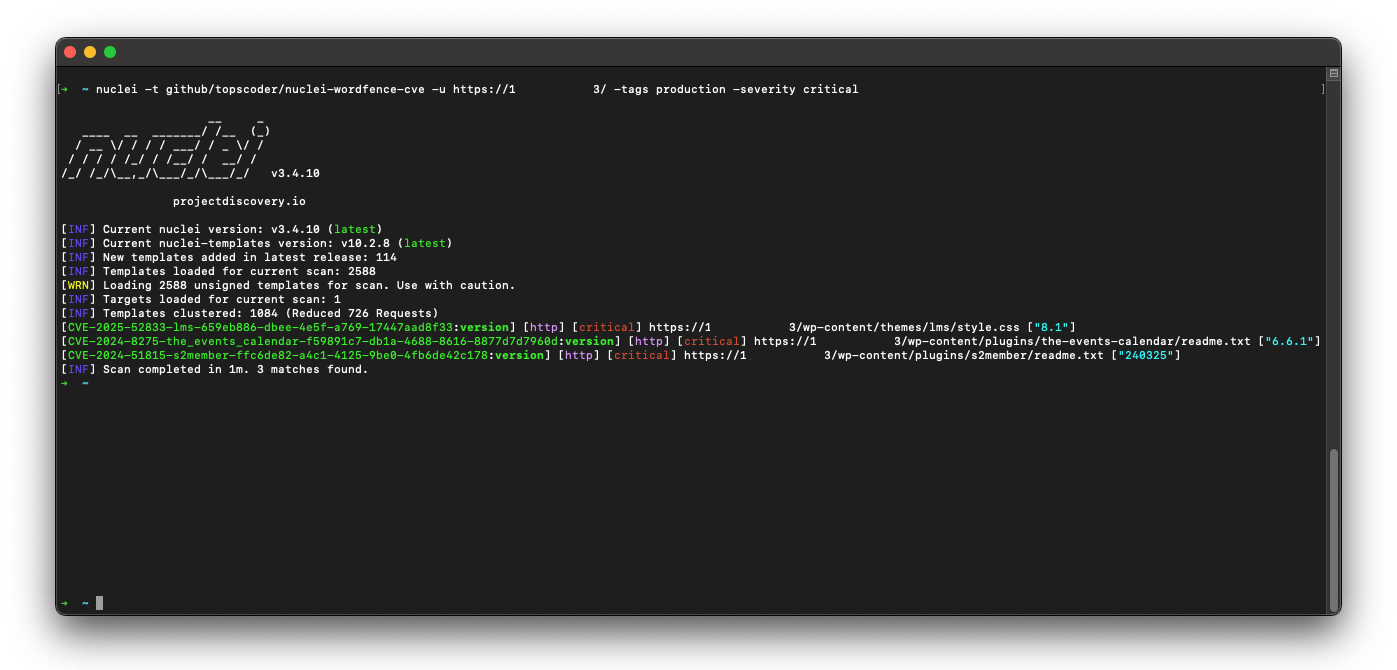
nuclei-wordfence-cve
 topscoder/nuclei-wordfence-cve
80k+ WordPress Nuclei templates, updated daily from Wordfence intel—filter by severity/tags/CVE and scan in one line. 🚀🔒
crawlerexploitationinformation-gathering+3
1.3k
topscoder/nuclei-wordfence-cve80k+ WordPress Nuclei templates, updated daily from Wordfence intel—filter by severity/tags/CVE and scan in one line. 🚀🔒
 cisagov/vulnrichment
A repo to conduct vulnerability enrichment.
 0xmarcio/pocindex
Search public CVE proof-of-concept exploits from GitHub, Nuclei, ExploitDB, Metasploit and Vulhub, with CVSS, EPSS and CISA KEV context.
 edoardottt/awesome-hacker-search-engines
A curated list of awesome search engines useful during Penetration testing, Vulnerability assessments, Red/Blue Team operations, Bug Bounty and more
 nomi-sec/poc-in-github
📡 PoC auto collect from GitHub. ⚠️ Be careful Malware.
 berylliumsec/nebula
AI-powered penetration testing assistant that automates reconnaissance, vulnerability analysis, and note-taking via integrated LLMs and CLI tool…
 projectdiscovery/vulnx
Modern CLI for exploring vulnerability data with powerful search, filtering, and analysis capabilities.
 xalgorix/xalgorix
Autonomous AI pentesting agents — real-time reconnaissance, vulnerability detection, and exploitation orchestration. Go + TypeScript.
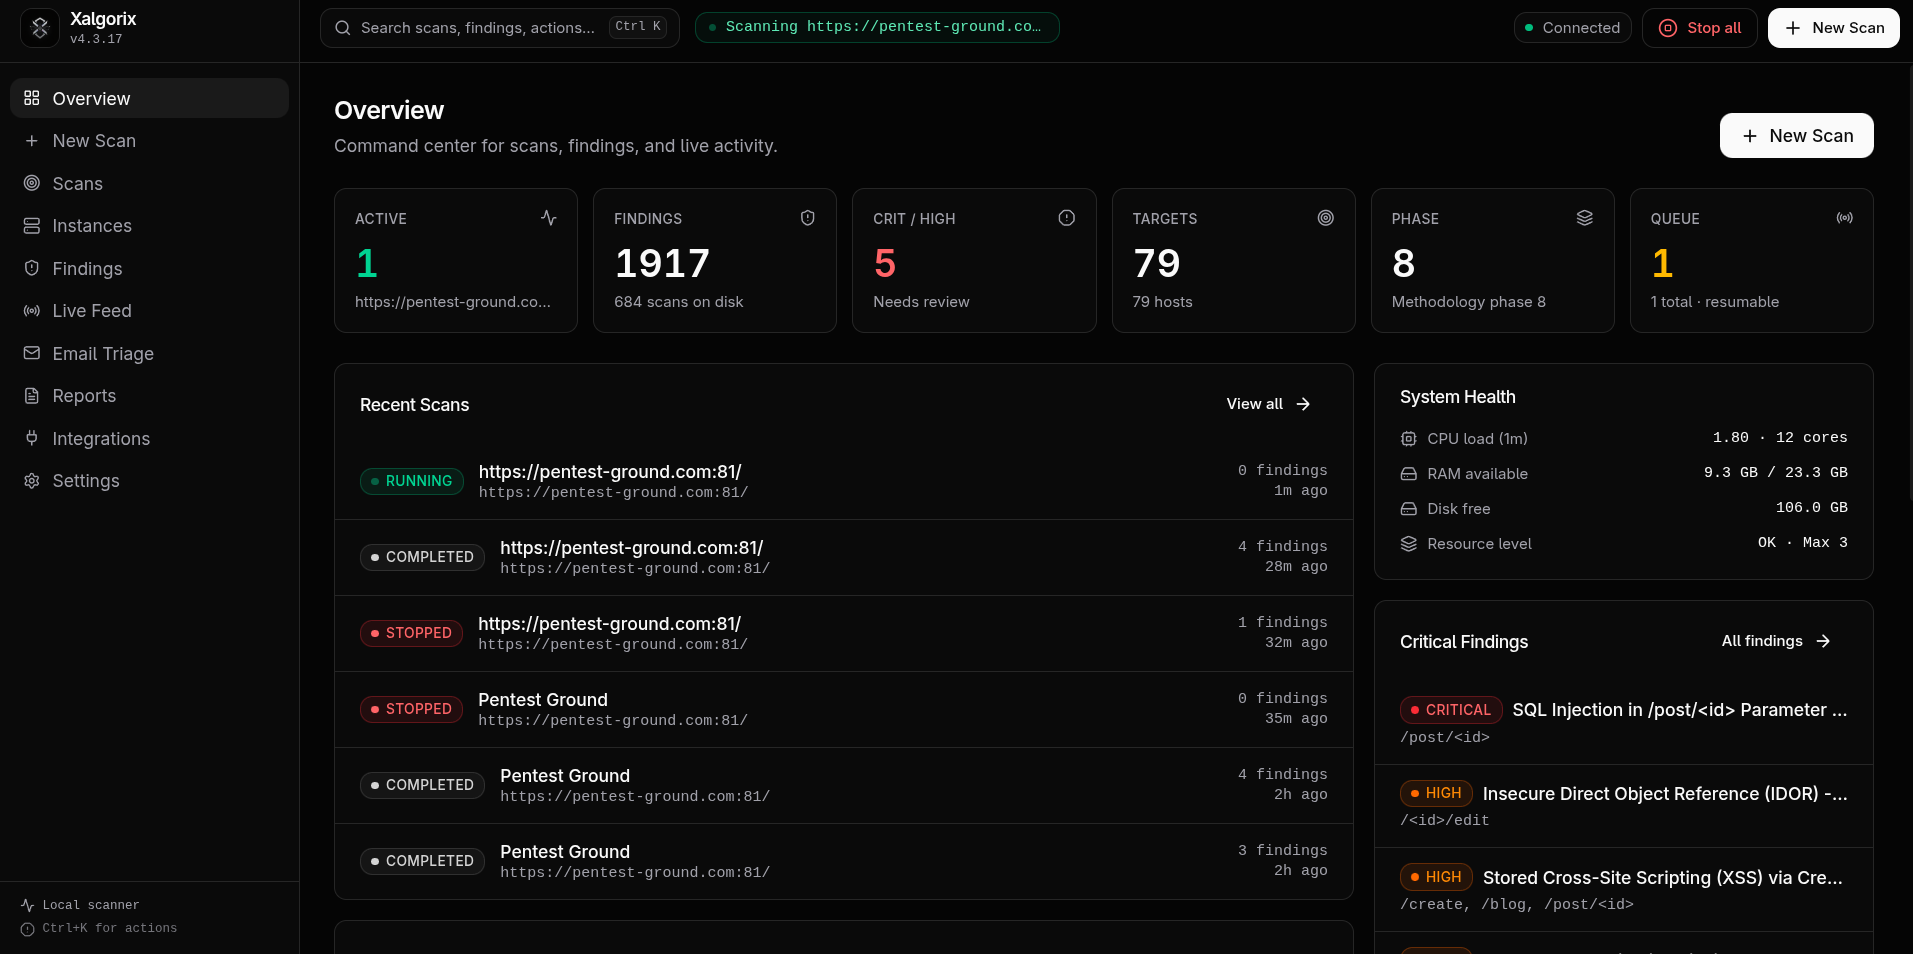 xalgord/xalgorix
Autonomous AI pentesting agents — real-time reconnaissance, vulnerability detection, and exploitation orchestration. Go + TypeScript.
 nomi-sec/nvd-exploit-list-ja
🔍NVD exploit & JVN(Japan Vulnerability Notes) easy description
 j0lt-github/react2shell-burp
Burp Suite extension for detecting CVE-2025-55182 (React2Shell) unsafe deserialization vulnerability. Features safe digest check, PoC redirect mode,…
 tridents10/vader-pro-vdr
AI-assisted Vulnerability Detection & Remediation platform featuring a Go endpoint agent, centralized dashboard, and vulnerability intelligence…
 trickest/cve
Gather and update all available and newest CVEs with their PoC.
 rafabd1/vectorfreed
Documents the VectorFreed librsvg use-after-free RCE chain (CVE-2026-96889) with an SVG generator PoC and remediation guidance for librsvg, Next.js,…
 0xblackash/cve-2025-14847
CVE-2025-14847
 trustedsec/spoonmap
Python wrapper around masscan and nmap for large-scale port discovery, host discovery, banner grabbing, and NSE-based vulnerability scanning across…
 xewdy444/netgrave
A tool for retrieving login credentials from Netwave IP cameras using a memory dump vulnerability (CVE-2018-17240)
 tc4dy/cve-2026-29000-poc-exploit
CVE-2026-29000 – pac4j-jwt Authentication Bypass (CVSS 10.0). One-click admin forge via public key JWE wrapping. Leaks configs, users, secrets.…