
mimicry
 chaitin/mimicry
Active deception tool that transparently migrates attackers from real targets to honeypots during exploitation and post-exploitation, supporting…
defensive-toolsincident-responsered-teaming+1
62
chaitin/mimicryActive deception tool that transparently migrates attackers from real targets to honeypots during exploitation and post-exploitation, supporting…
 adityabhatt3010/cve-2025-49706-sharepoint-spoofing-vulnerability-under-active-exploitation
A deep dive into CVE-2025-49706 — the SharePoint spoofing flaw now exploited in the wild for stealthy web shell deployment and privilege escalation.
 michaael01/letsdefend--soc-342-cve-2025-53770-sharepoint-exploit-toolshell
Detailed walkthrough of CVE-2025-53770 (ToolShell) SharePoint zero-day exploitation, including RCE analysis, MachineKey exfiltration, payload…
 cyprianatsyor/toolshell-cve-2025-53770-sharepoint-exploit-lab-letsdefend
Step-by-step walkthrough of exploiting CVE-2025-53770 (ToolShell) in a LetsDefend lab, covering RCE, web shell deployment, and incident response…
 canyonroad/agentsh
Execution-Layer Security (ELS) for AI agents — policy-enforced shell with audit.
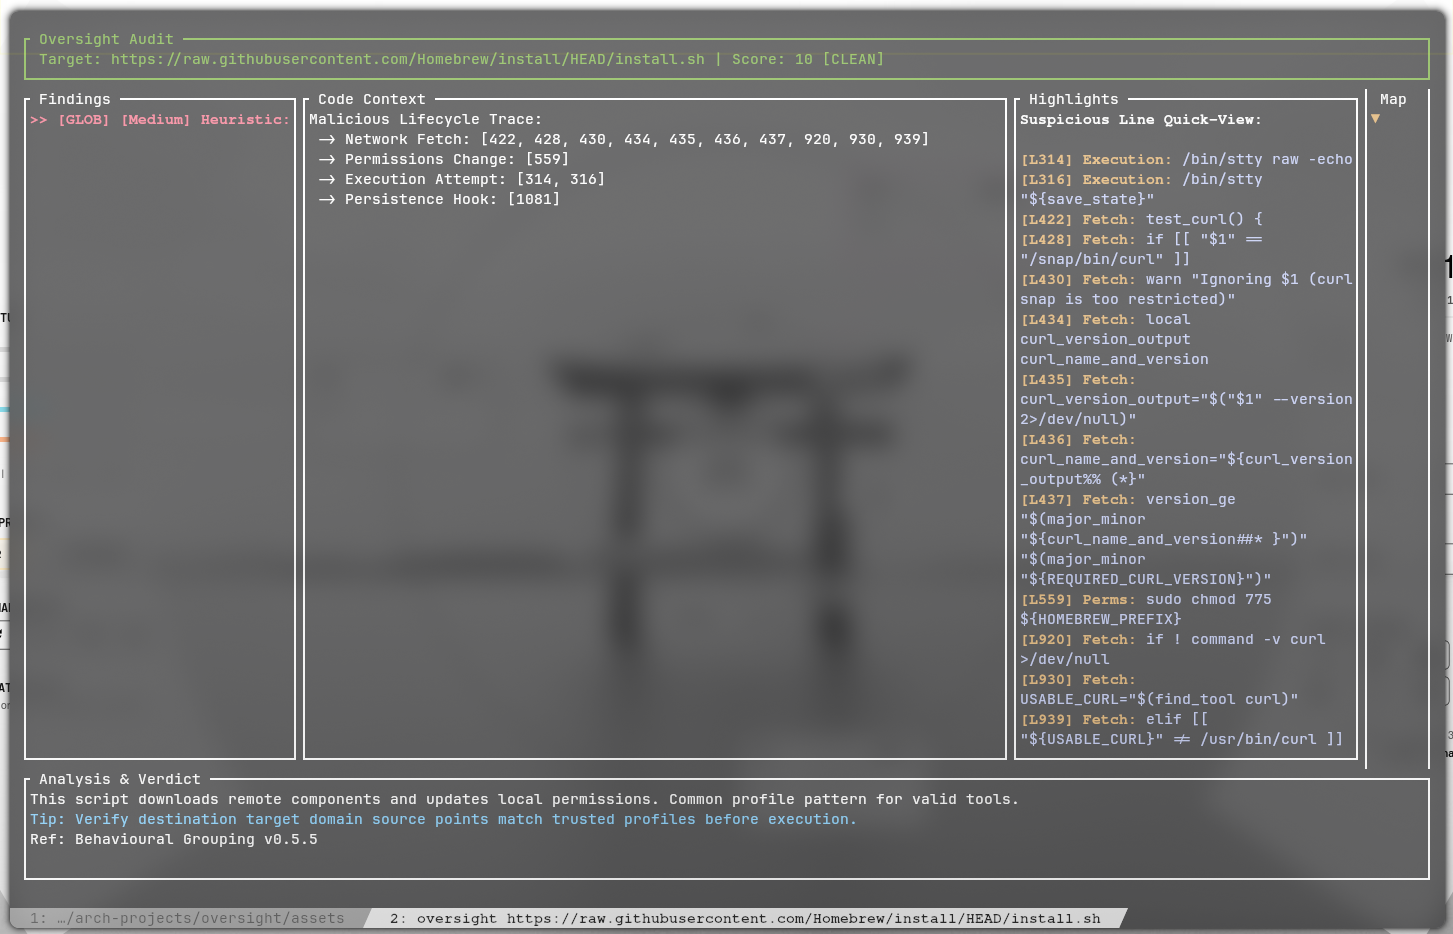 rakosn1cek/oversight
A lightweight security auditor and sandbox for shell scripts. Oversight combines a Static Analysis engine (Rust) with Dynamic Enforcement (Linux…
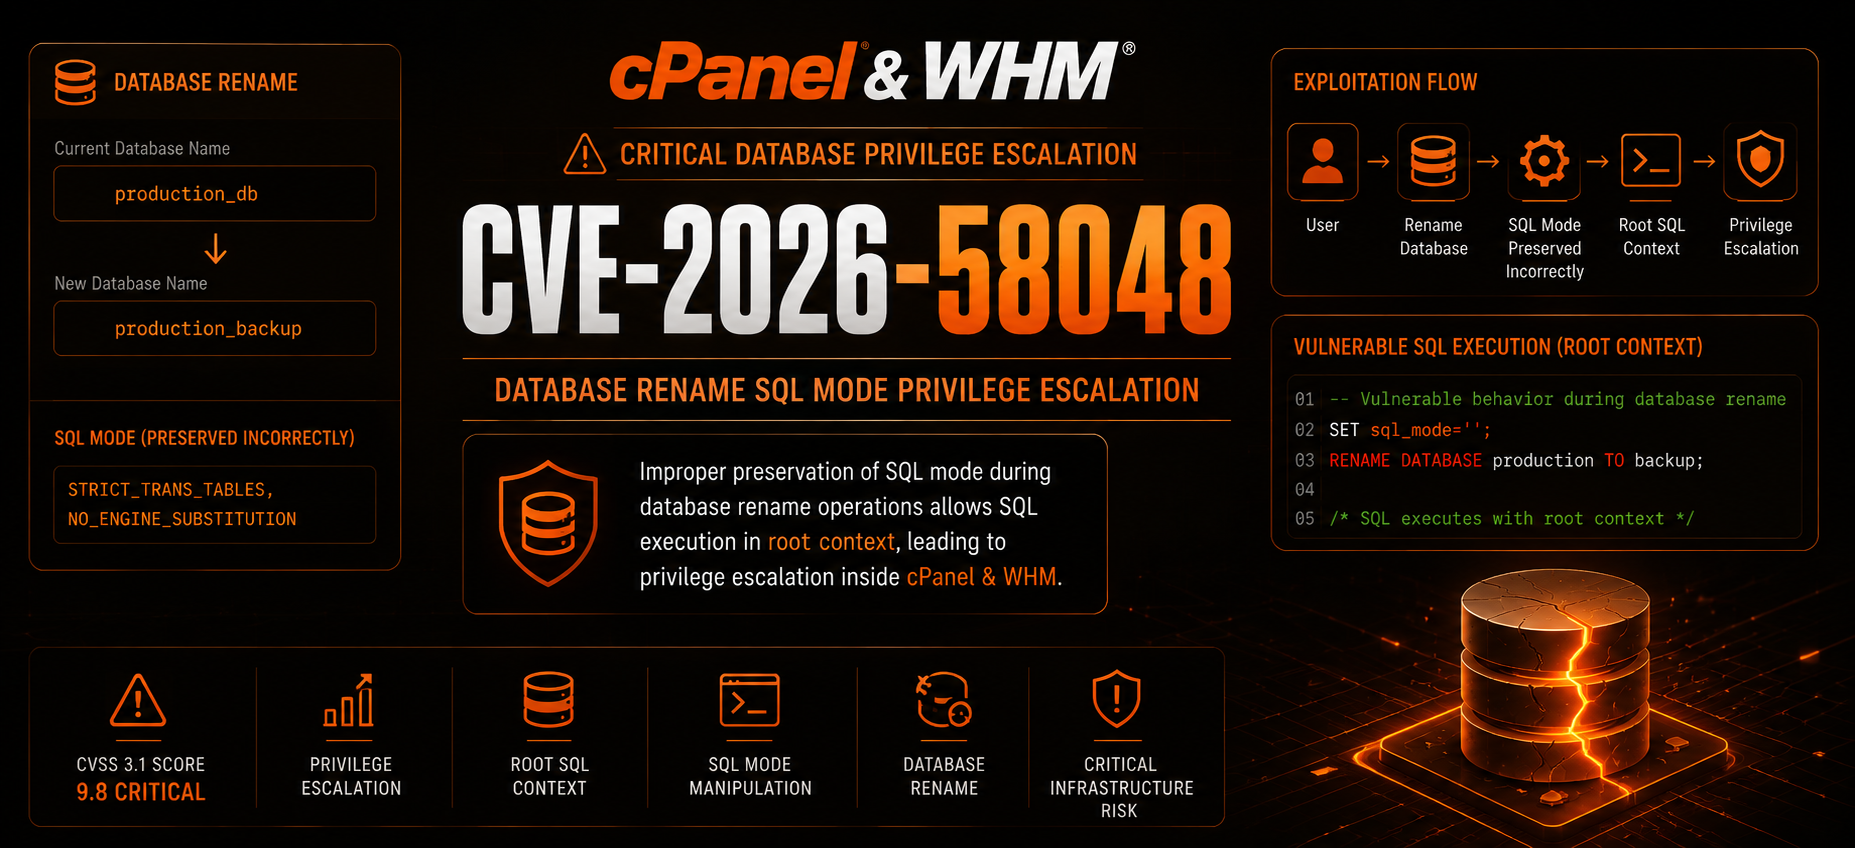 tc4dy/cve-2026-58048-poc-exploit
👾 CVE-2026-58048 – cPanel Root SQL Execution Toolkit (CVSS 9.4) | Full Red/Blue Team Toolkit suite for unpatched cPanel & WHM 11.x. 2 tools: Safe…
 mightysai1997/cve-2024-3094
Shell scripts to detect CVE-2024-3094 backdoor in liblzma5 across Kubernetes pods and Docker containers, with SBOM generation via Trivy for…
 cowrie/cowrie
Cowrie SSH/Telnet Honeypot https://docs.cowrie.org/
 johnng007/live-forensicator
Cross-platform incident response and live forensics toolkit with built-in detection, structured analysis, and report generation — designed for fast,…
 ngvcanh/cve-2025-55182-attack-analysis
Real-world attack analysis of CVE-2025-55182 (React2Shell) - React Server Components RCE vulnerability