
regipy
 mkorman90/regipy
Regipy is an os independent python library for parsing offline registry hives
digital-forensicsforensicsincident-response+1
mkorman90/regipyRegipy is an os independent python library for parsing offline registry hives
 gagaltotal/cve-2026-43284-cve-2026-43500-scan
Automated SSH-based scanner and patcher for Linux kernel LPE vulnerabilities CVE-2026-43284 and CVE-2026-43500, with multi-host discovery, privilege…
 puppetlabs-toy-chest/puppetlabs-cve20113872
Puppet Module to help fix and migrate a Puppet deployment (CVE-2011-3872)
 codesource/copyfail-check
Shell script to detect CVE-2026-31431 (Copy Fail) exposure and mitigations on Linux systems: kernel check, module state, boot params, AF_ALG…
 mrowkoob/copy-fail-mitigate-no-reboot
No-reboot mitigation script for the Copy Fail kernel bug (CVE-2026-31431). Disables the vulnerable algif_aead module and evicts page cache for setuid…
 whereisxuezugi/cplhf
Modular Bash toolkit that hardens Debian/Ubuntu systems for CyberPatriot competitions, automating account, firewall, SSH, PAM, and service hardening…
 vasyapokemon/cve-2026-31431
Research and detection toolkit for Linux kernel LPE CVE-2026-31431, including exploit analysis, YARA rules, auditd/Falco detection, patching guide,…
 rippsec/cve-2026-31431-copy-fail
Comprehensive analysis of CVE-2026-31431, a Linux kernel LPE, including exploit methodology, detection scripts, YARA rules, auditd and Falco…
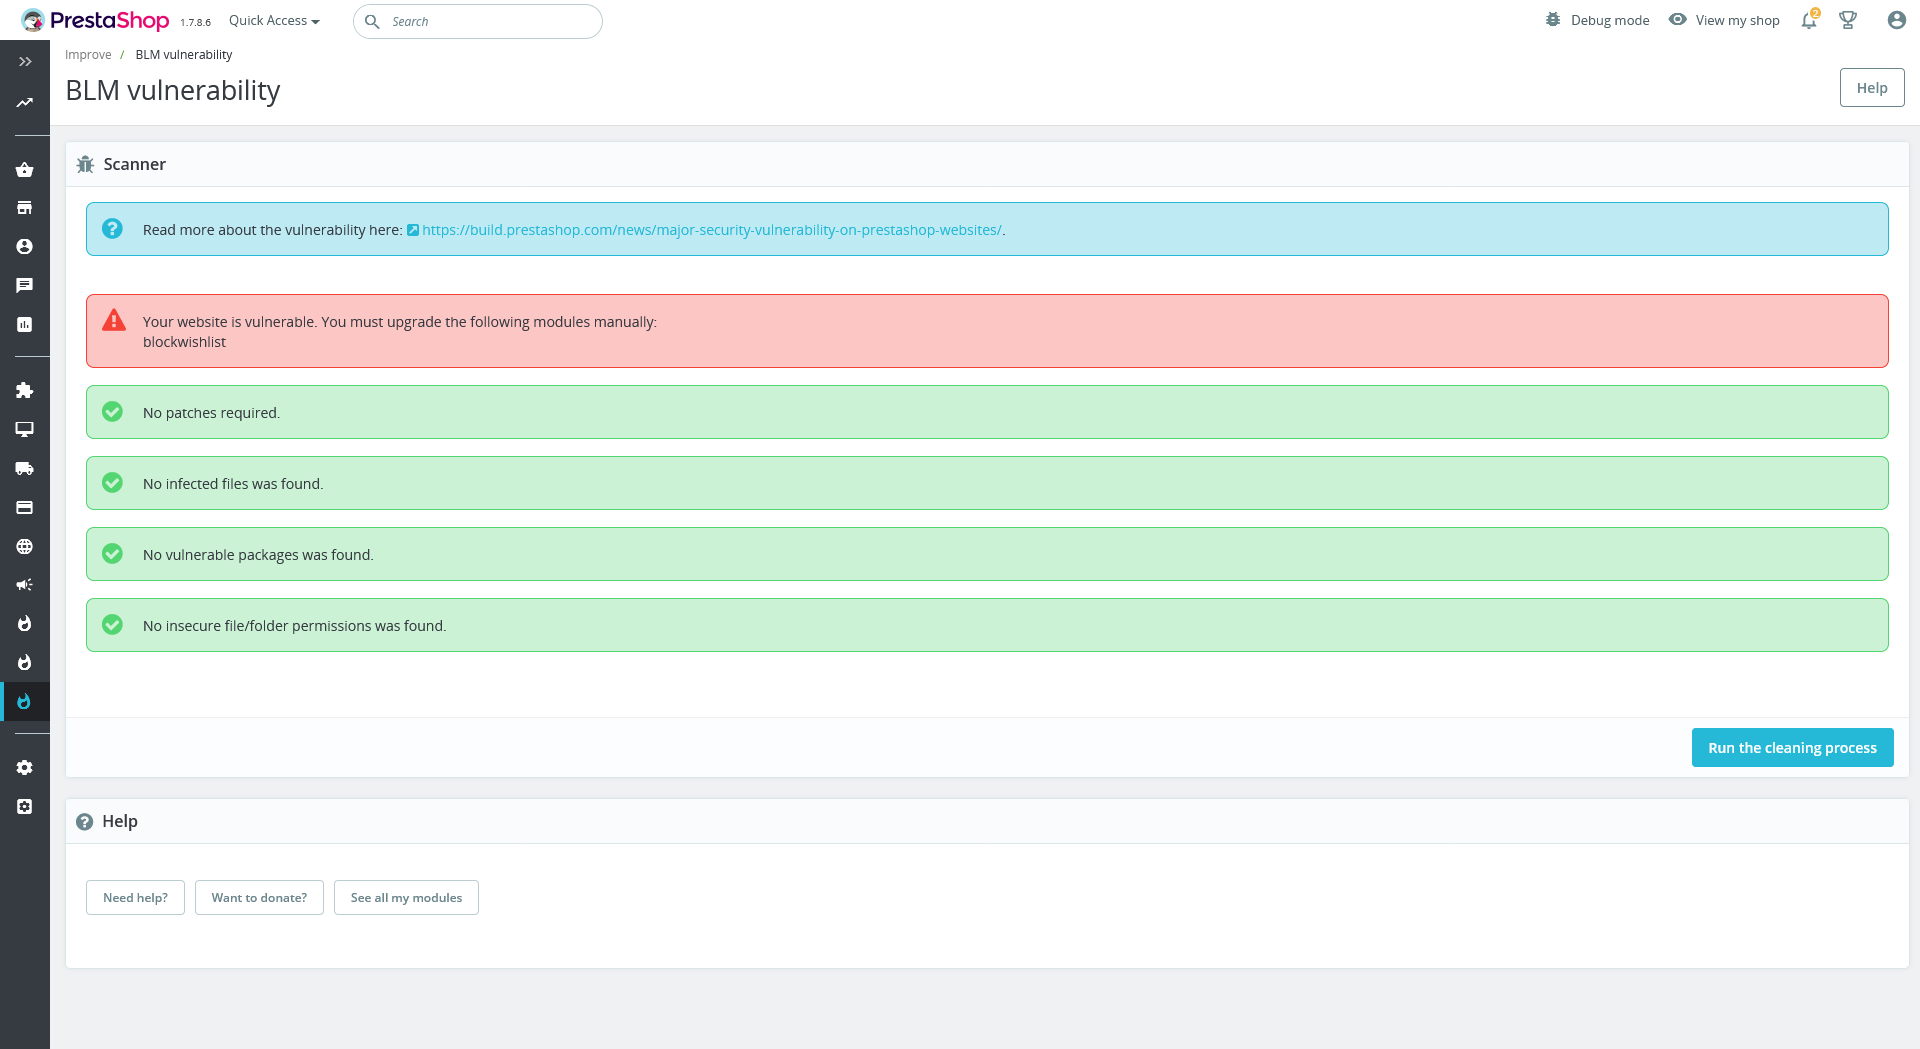 mathiasreker/blmvuln
Major Security Vulnerability on PrestaShop Websites - CVE-2022-31101
 jtsylve/lime
Kernel module for volatile memory acquisition from Linux and Android devices, producing forensically sound captures to disk or over the network.
 last-byte/persistencesniper
Powershell module that can be used by Blue Teams, Incident Responders and System Administrators to hunt persistences implanted in Windows machines.…
 invictus-ir/microsoft-extractor-suite
A PowerShell module for acquisition of data from Microsoft 365 and Azure for Incident Response and Cyber Security purposes.
 theflink/hunt-sleeping-beacons
Callstack scanner that identifies IOCs of unpacked or injected C2 agents by analyzing thread idle behavior, unbacked memory, module stomping, APCs,…
 darkquasar/azurehunter
A Cloud Forensics Powershell module to run threat hunting playbooks on data from Azure and O365
 anssi-fr/dfir-o365rc
PowerShell module for Office 365 and Azure log collection
 anssi-fr/dfir4vsphere
Powershell module for VMWare vSphere forensics
 joe-desimone/patriot
In-memory stealth detection tool that identifies process hollowing, module stomping, unbacked executable regions, and anomalous CONTEXT structures…
 jbnetwork-git/copy-fail-check
Interactive bash helper to check exposure to CVE-2026-31431 (Copy Fail) and apply temporary mitigation by disabling algif_aead module on…