

mvt
 mvt-project/mvt
Forensic collection and analysis toolkit for Android and iOS devices to identify potential compromise by known spyware using public and private…
android-securitydigital-forensicsdisk-forensics+7
15.6k
mvt-project/mvtForensic collection and analysis toolkit for Android and iOS devices to identify potential compromise by known spyware using public and private…
 netalertx/netalertx
Centralized network visibility and continuous asset discovery. Monitor devices, detect change, and stay aware across distributed networks.
 jtsylve/lime
Kernel module for volatile memory acquisition from Linux and Android devices, producing forensically sound captures to disk or over the network.
 mvt-project/androidqf
androidqf (Android Quick Forensics) helps quickly gathering forensic evidence from Android devices, in order to identify potential traces of…
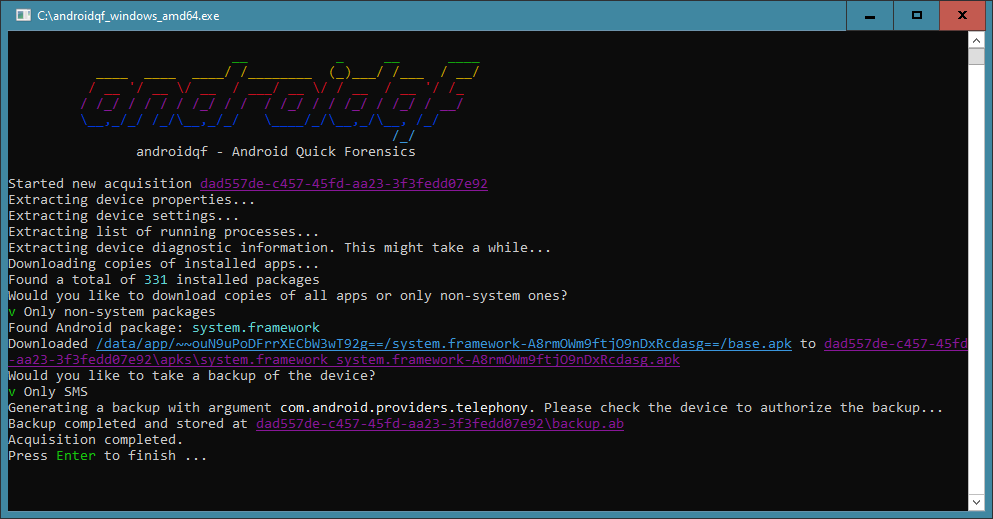 botherder/androidqf
Portable forensic acquisition tool for Android devices that collects relevant data via USB debugging to identify potential spyware or compromise…
 fox-it/citrix-netscaler-triage
Forensic triage toolkit for Citrix NetScaler devices, featuring a Dissect-based IOC scanner for webshells, timestomping, and suspicious binaries,…
 vulncheck-oss/cisco-ios-xe-implant-scanner
Go-based scanner that detects implanted Cisco IOS XE systems by sending crafted HTTP requests to identify compromised devices and vulnerable versions.
 nccgroup/mimikatz-detector-busylight
USB HID driver emulation with PID/VID (0x3bca/0x27bb) of Plenom A/S Busylight Alpha, that is supported by Mimikatz. When mimikatz is executed, a…
 corelight/cve-2020-5902-f5bigip
A network detection package for CVE-2020-5902, a CVE10.0 vulnerability affecting F5 Networks, Inc BIG-IP devices.
 k3rnix/portguard
USB port access control tool for Debian with whitelist management, automatic background scanning daemon, and CLI interface to block or allow USB…
 yami0x777/belsen_group-et-exploitation-de-la-cve-2022-40684
Analyzes a dark web leak of 15,000+ Fortinet devices compromised via CVE-2022-40684, providing IOCs, impacted versions, and a Python script to…
 digital-dev/log4j-cve-2021-44228-remediation
This powershell script is intended to be used by anyone looking to remediate the Log4j Vulnerability within their environment. It can target multiple…
 maikelnight/zerologon
Check for events that indicate non compatible devices -> CVE-2020-1472
 inverse-inc/packetfence
PacketFence is a fully supported, trusted, Free and Open Source network access control (NAC) solution. Boasting an impressive feature set including a…
 fleetdm/fleet
Open-source platform to secure and manage endpoints via MDM, patch management, software deployment, and osquery-powered visibility with compliance…
 johnng007/live-forensicator
Cross-platform incident response and live forensic artifact collector with built-in detection, structured analysis, and report generation — designed…
 bert-janp/incident-response-powershell
PowerShell-based incident response toolkit that collects 25+ forensic artifacts (processes, network connections, registry, browser history) and…
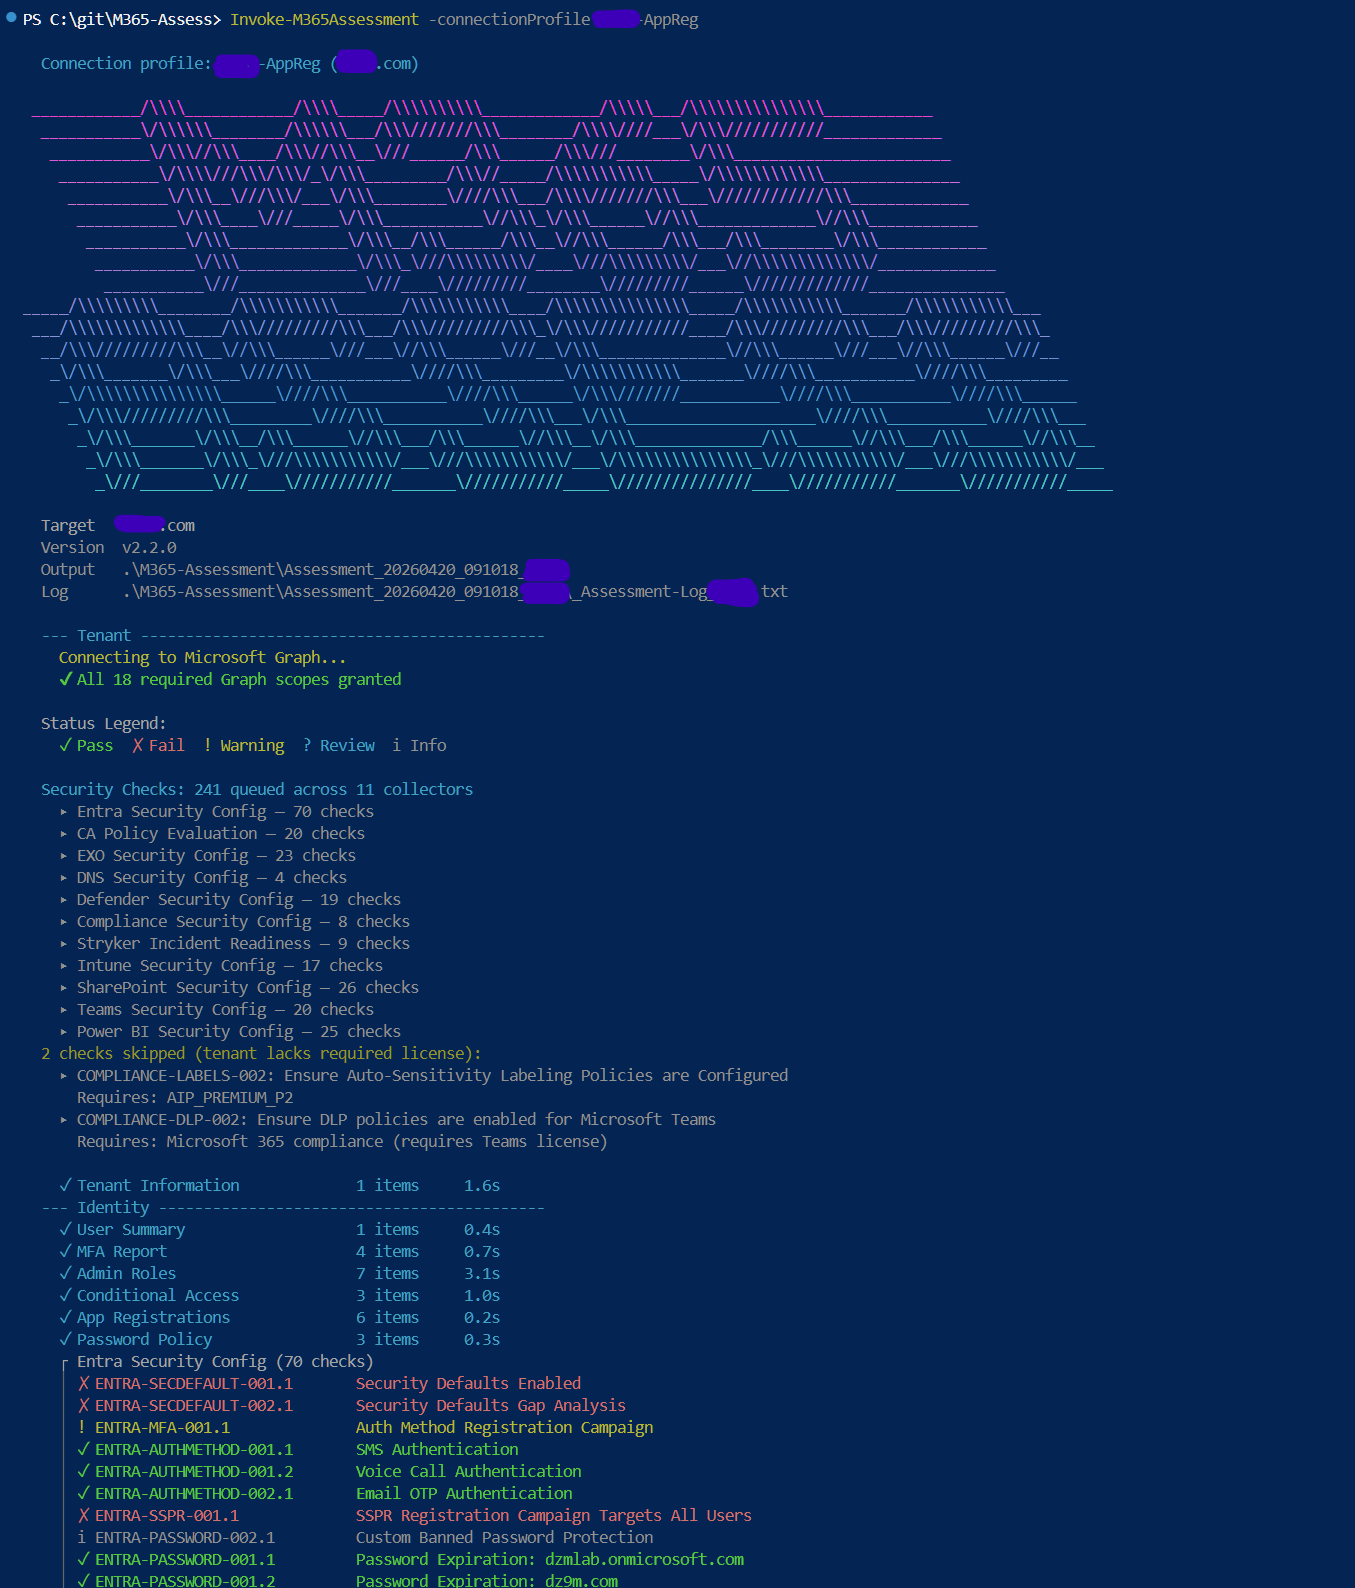 galvnyz/m365-assess
290+ Automated checks across 14 compliance frameworks, interactive HTML report, no data leaves your machine.