
mimicry
 chaitin/mimicry
Active deception tool that transparently migrates attackers from real targets to honeypots during exploitation and post-exploitation, supporting…
defensive-toolsincident-responsered-teaming+1
62
chaitin/mimicryActive deception tool that transparently migrates attackers from real targets to honeypots during exploitation and post-exploitation, supporting…
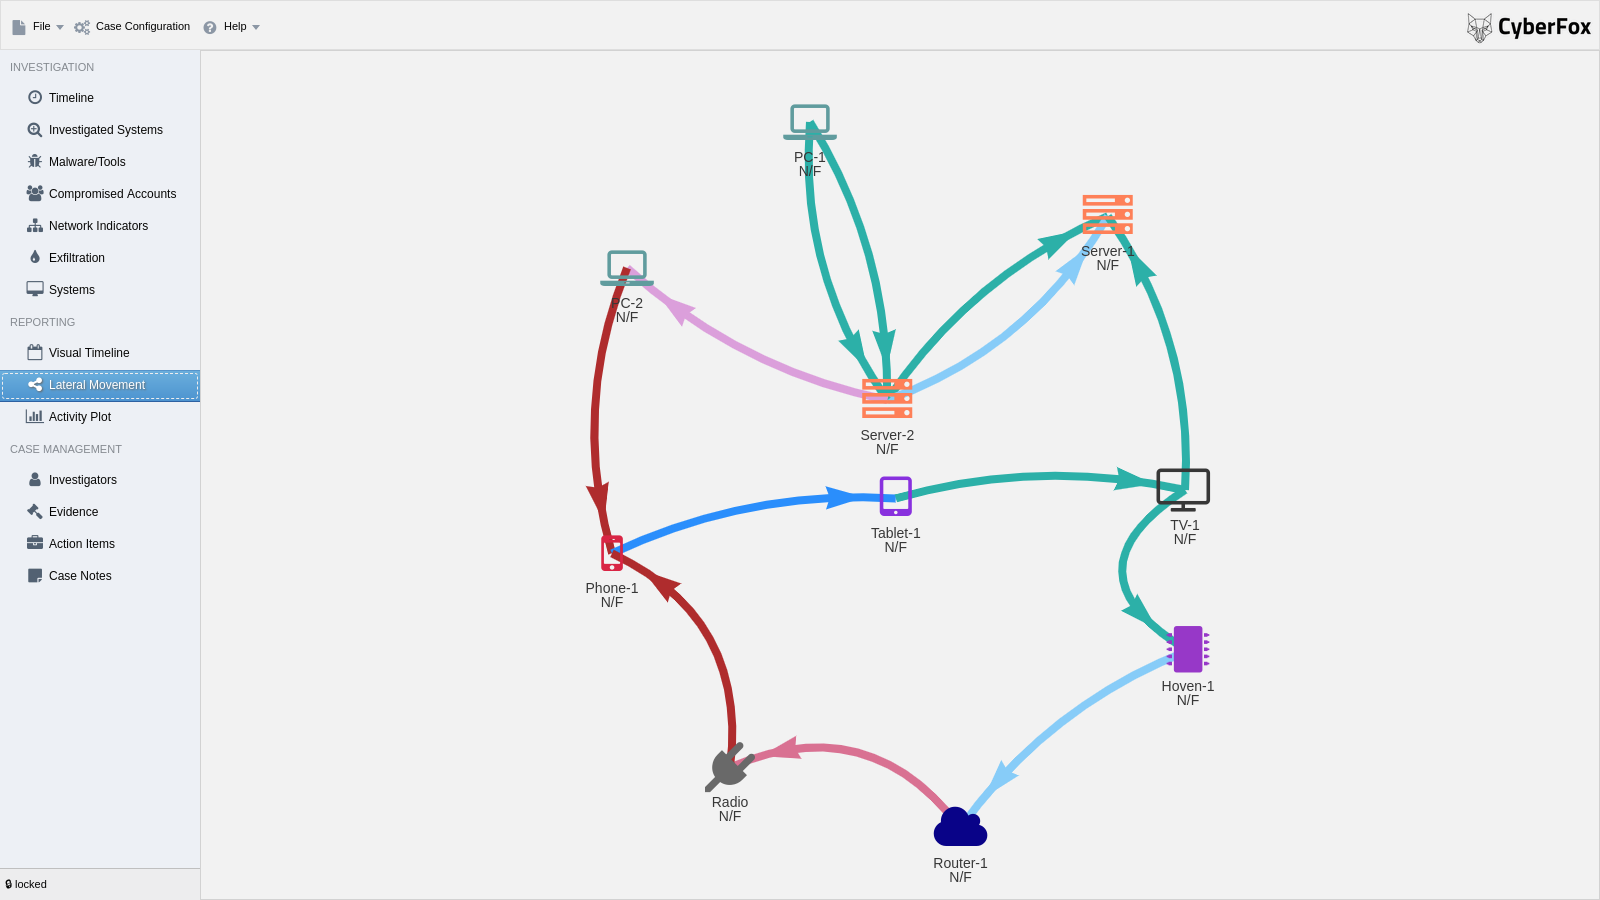 cyb3rfox/aurora-incident-response
Incident Response Documentation made easy. Developed by Incident Responders for Incident Responders
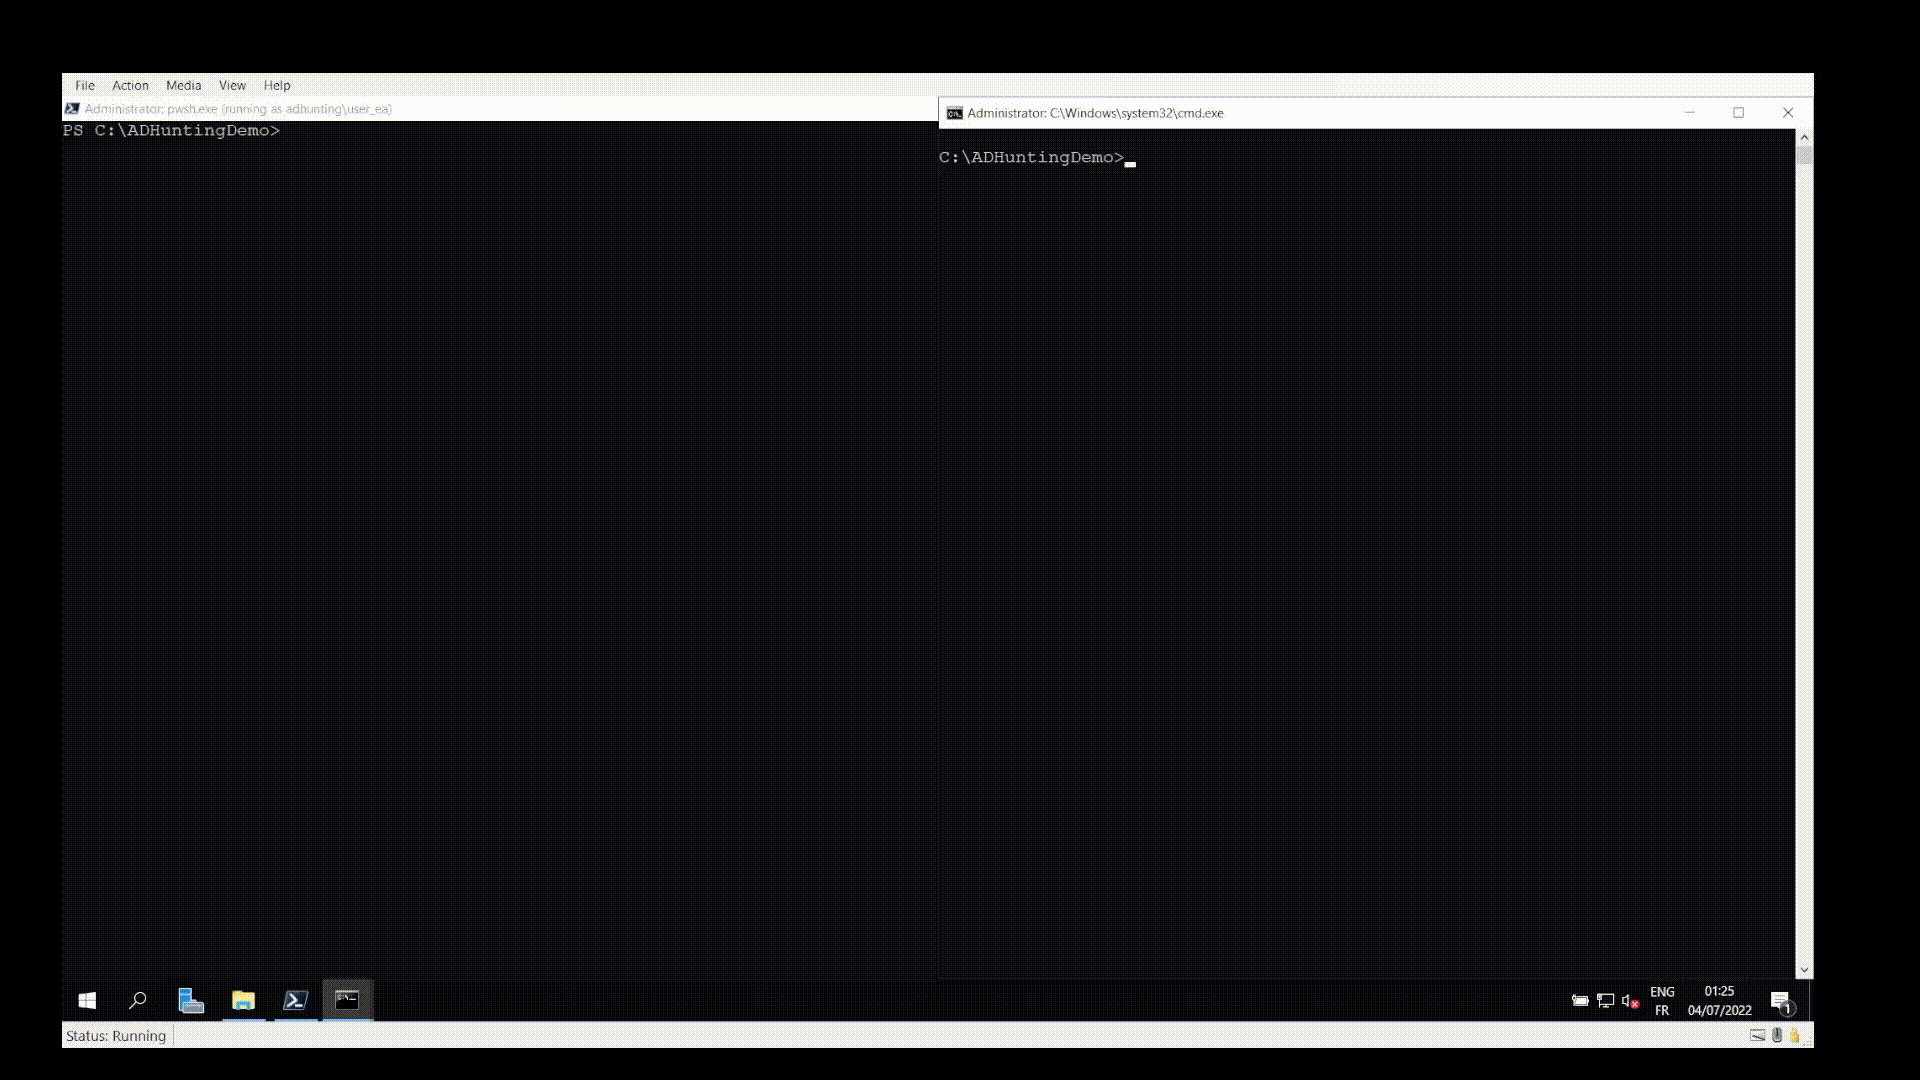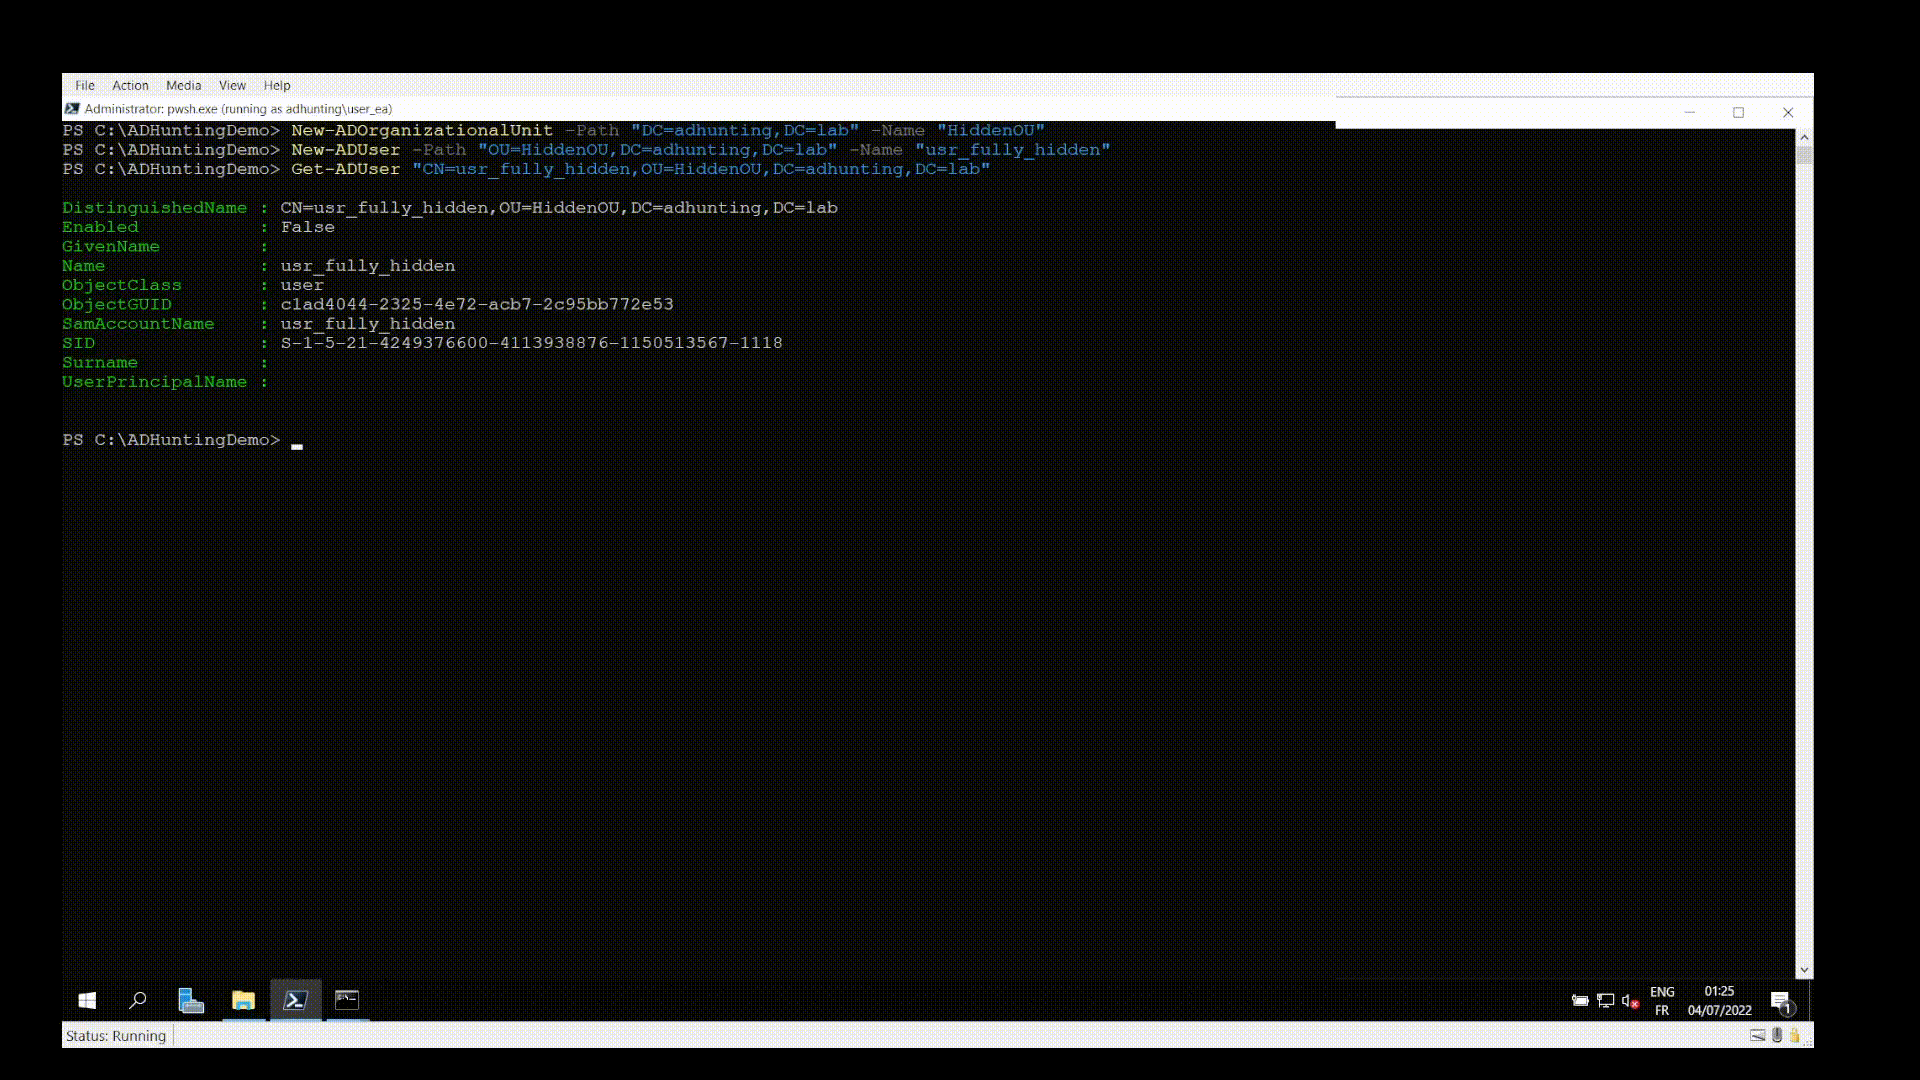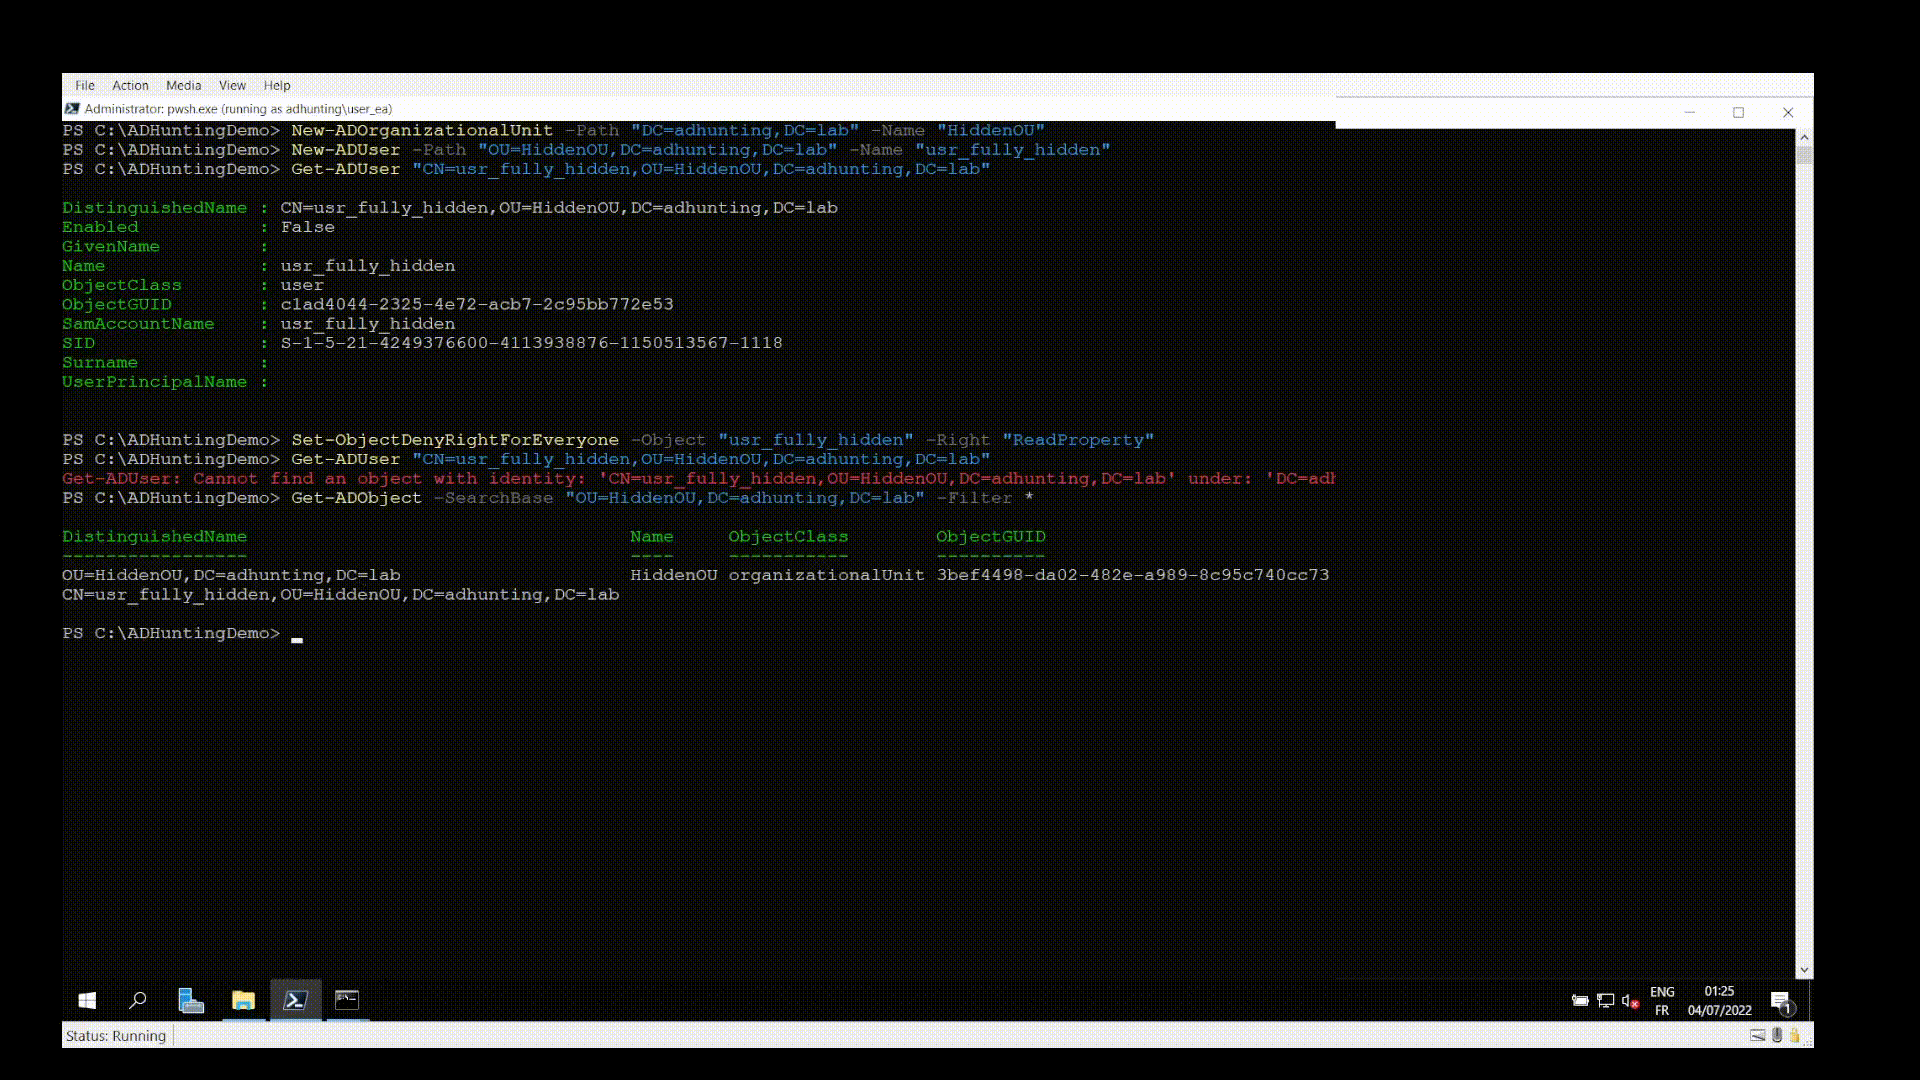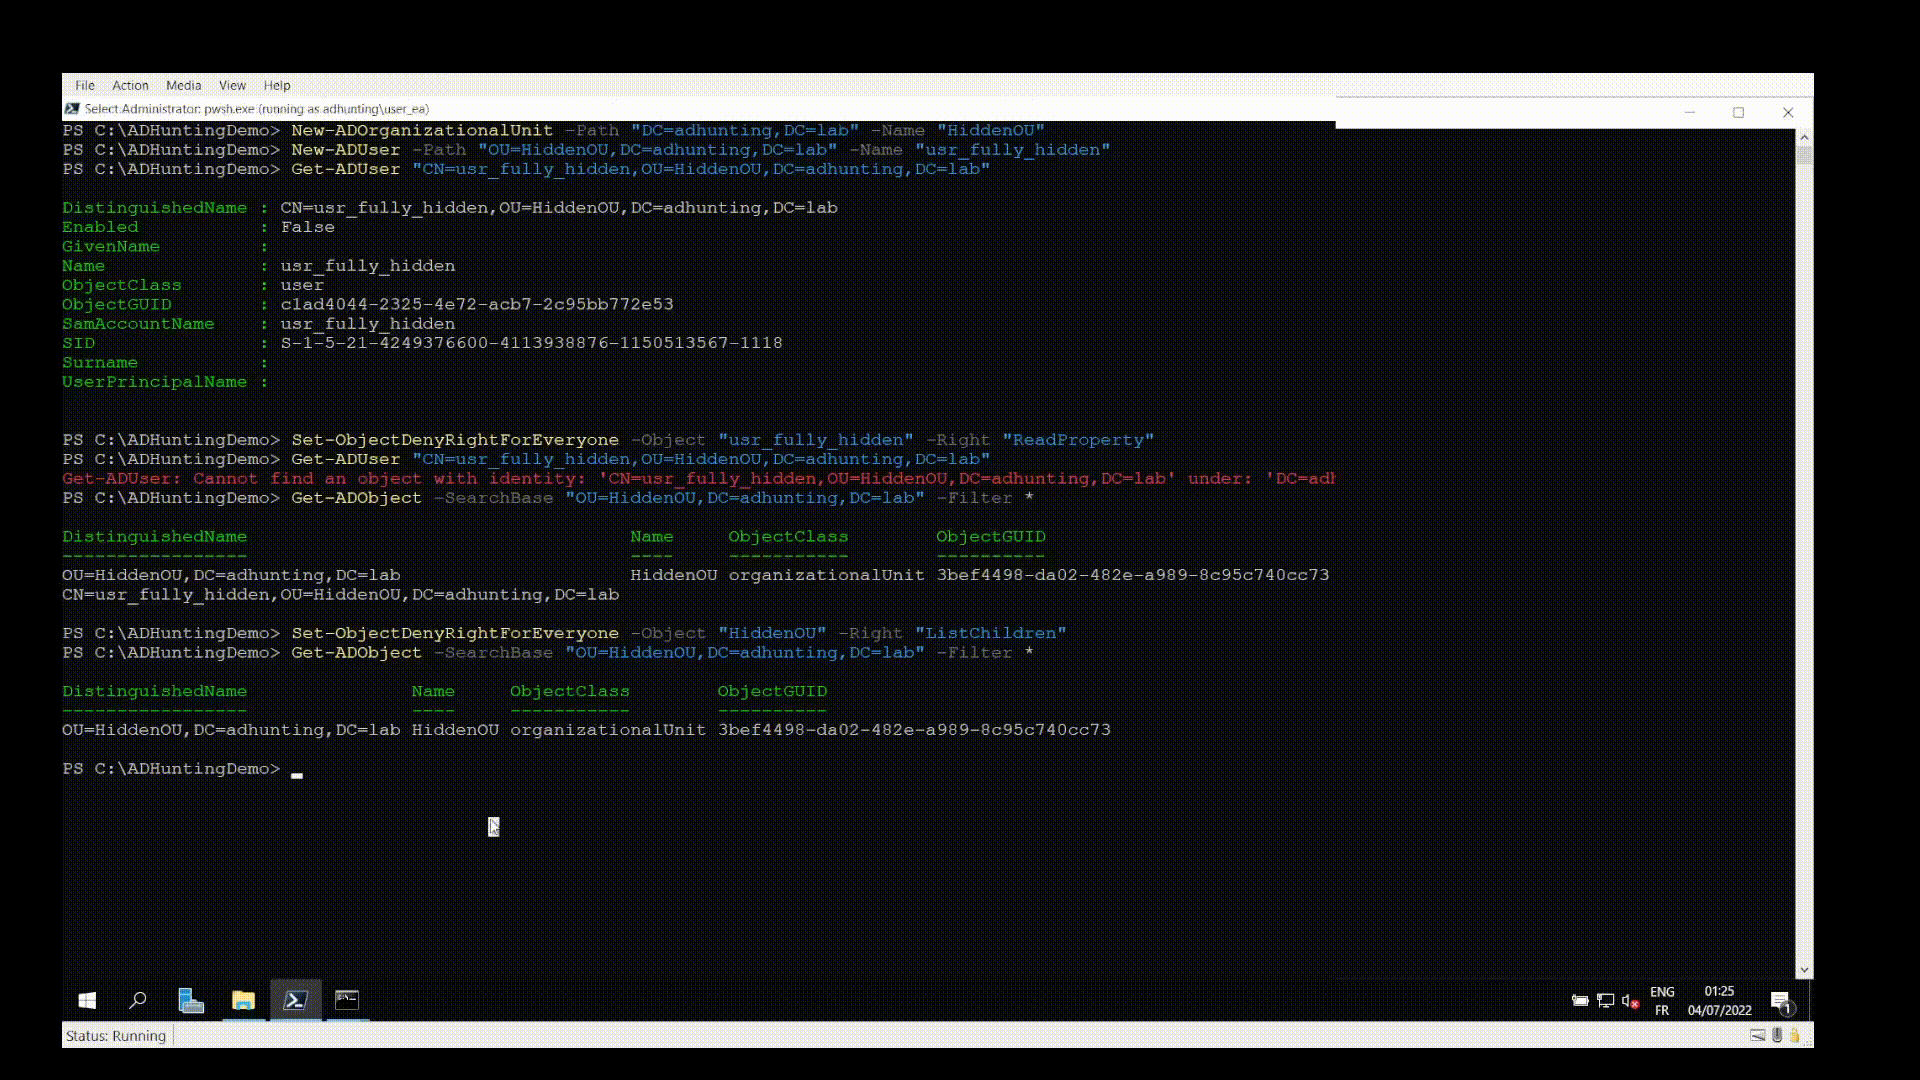 qazeer/farsightad
PowerShell script that aim to help uncovering (eventual) persistence mechanisms deployed by a threat actor following an Active Directory domain…
 josephgodwinkimani/cloudpanel-2.4.2-cve-2024-44765-recovery
How to "recover" a CloudPanel server affected by the CVE-2024-44765 vulnerability
 niklasmato/fortileak-01-2025-be
This repository contains informaion about the Fortigate firewall vulnerability (CVE-2022-40684) and affected data that were publicly disclosed by the…
 cowrie/cowrie
Cowrie SSH/Telnet Honeypot https://docs.cowrie.org/
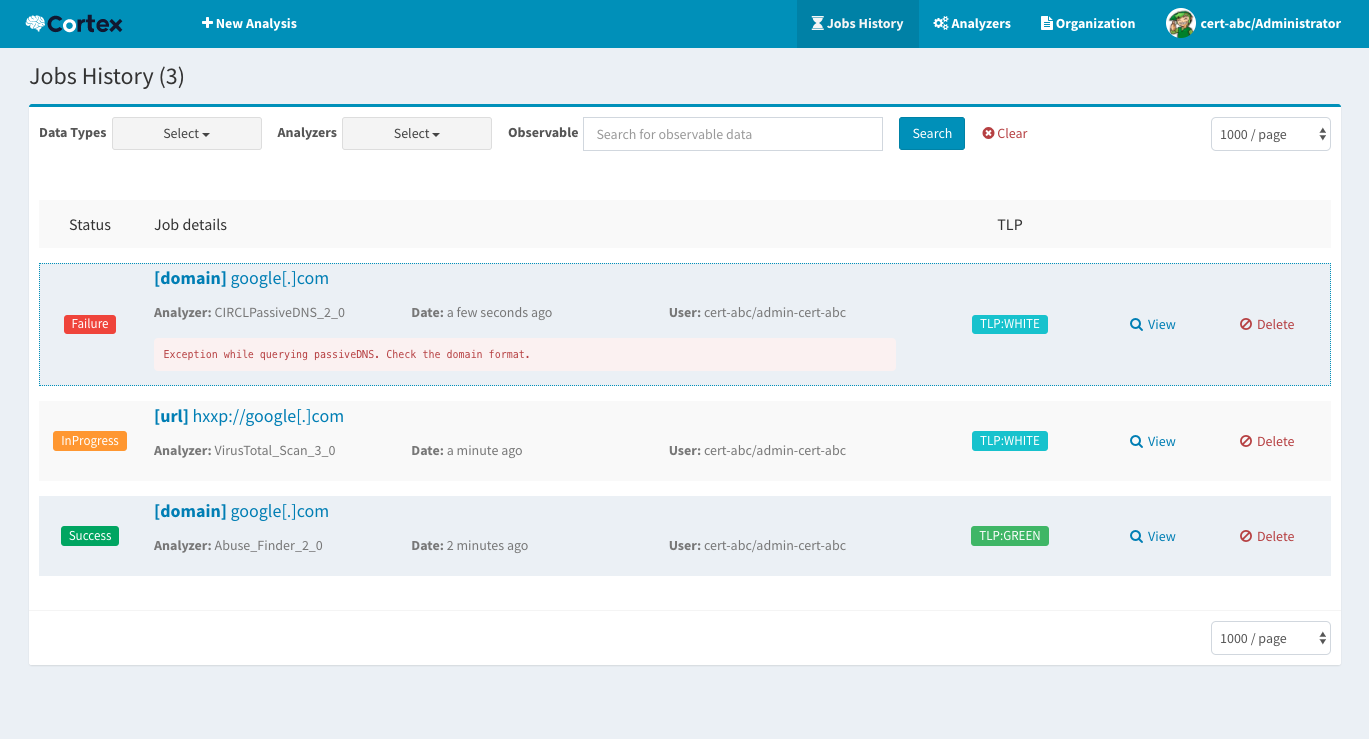 thehive-project/cortex
Cortex: a Powerful Observable Analysis and Active Response Engine
 pjlantz/hale
Botnet command & control monitor
 rushyo/vindicatetool
LLMNR/NBNS/mDNS Spoofing Detection Toolkit
 rootly-ai-labs/rootly-graphify-importer
Turn Rootly incidents, alerts, and teams into a queryable knowledge graph. Visualize service dependencies, on-call coverage gaps, and cross-incident…

 limo57640-crypto/wp-user-registration-vuln-checker
Read-only WordPress User Registration CVE-2026-1492 checker for hidden admins, plugin version, uploads PHP, cron, and compromise IOCs.
 g0tmi1k/kippo-g0tmi1k
Medium-interaction SSH honeypot that logs brute force attacks and full attacker shell interactions, with customization options to reduce…
 watchtowrlabs/citrix-netscaler-cve-2026-88771-iocs
Indicators of Compromise and hunting guidance for CVE-2026-88771, an unauthenticated command injection in Citrix NetScaler ADC and Gateway, covering…
 mvt-project/mvt
Forensic collection and analysis toolkit for Android and iOS devices to identify potential compromise by known spyware using public and private…
 kubeshark/kubeshark
eBPF-powered network observability for Kubernetes. Indexes L4/L7 traffic with full K8s context, decrypts TLS without keys. Queryable by AI agents via…
 sepinf-inc/iped
IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…
 jpcertcc/logontracer
Investigate malicious Windows logon by visualizing and analyzing Windows event log