
Configuration_extractors
 pandare9x/configuration_extractors
Configuration Extractors for Malware
digital-forensicsincident-responsemalware-analysis+3
128
pandare9x/configuration_extractorsConfiguration Extractors for Malware
 sjkim1127/reversecore_mcp
A security-first MCP server that empowers AI agents to perform automated reverse engineering, malware analysis, forensics, vulnerability research,…
 kaandemir993/vidar-stealer-reverse-engineering
"In-depth reverse engineering analysis of Vidar Stealer 2.0 covering Task Scheduler tampering (1999 timestamps), Explorer.exe process hollowing, and…
 perkins-fund/malware-bible
Free educational courses in cybersecurity, reverse engineering, malware analysis, and programming designed to expand access, build practical skills,…
 remnux/distro
Provides supplemental files and Debian package sources for a specialized Linux distro focused on malware analysis, reverse engineering, and digital…
 cristhiansm0/txdxcristhian_2023-cve-38831
CVE-2023-38831 WinRAR lab: detection with Sysmon/Wazuh, reverse engineering with Ghidra, patch analysis, and remediation.
 v-pun215/tourmaline
Reverse engineering notes, deobfuscated source, IOCs, and YARA rules for the Tourmaline ClickFix Python RAT, covering its DNS tunnel and blockchain…
 te0rwx/cve-2025-32433-detection
Custom YARA rule for detecting artifacts of CVE-2025-32433, an Erlang/OTP SSH pre-authentication RCE vulnerability. Validated against public PoCs and…
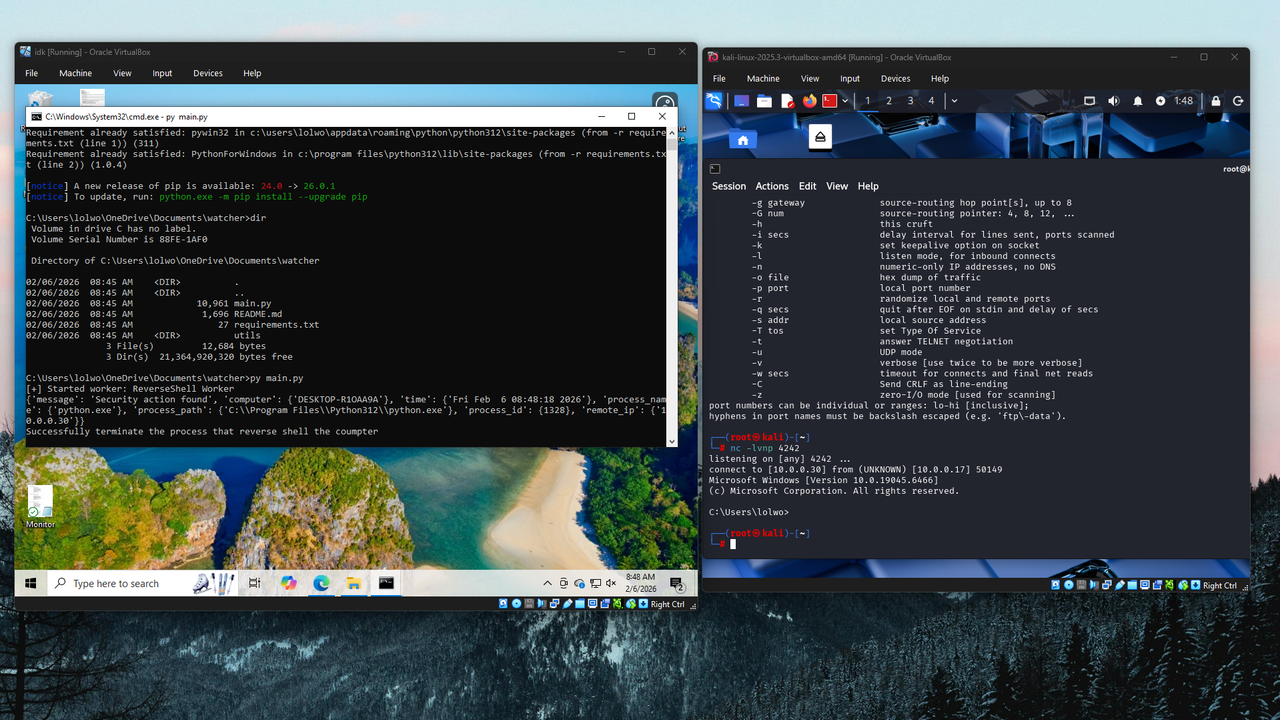 themoonsir/watcher
Detection reverse shell and kill it before trying shell.
 mvt-project/mvt
Forensic collection and analysis toolkit for Android and iOS devices to identify potential compromise by known spyware using public and private…
 mandiant/capa
Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…
 volatilityfoundation/volatility3
Advanced framework for extracting digital artifacts from volatile memory (RAM) samples, enabling deep forensic analysis of system runtime state…
 mandiant/flare-floss
FLARE Obfuscated String Solver - Automatically extract obfuscated strings from malware.
 freedomofpress/dangerzone
Take potentially dangerous PDFs, office documents, or images and convert them to safe PDFs
 rabbitstack/fibratus
Security sensor for realtime threat detection and protection
 withsecurelabs/doublepulsar-detection-script
A python2 script for sweeping a network to find windows systems compromised with the DOUBLEPULSAR implant.
 hasherezade/hollows_hunter
Scans all running processes. Recognizes and dumps a variety of potentially malicious implants (replaced/implanted PEs, shellcodes, hooks, in-memory…