
agentic-threat-hunting-framework
 nebulock-inc/agentic-threat-hunting-framework
ATHF is a framework for agentic threat hunting - building systems that can remember, learn, and act with increasing autonomy.
ai-securityeducationincident-response+7
384
nebulock-inc/agentic-threat-hunting-frameworkATHF is a framework for agentic threat hunting - building systems that can remember, learn, and act with increasing autonomy.
 trappsec-dev/trappsec
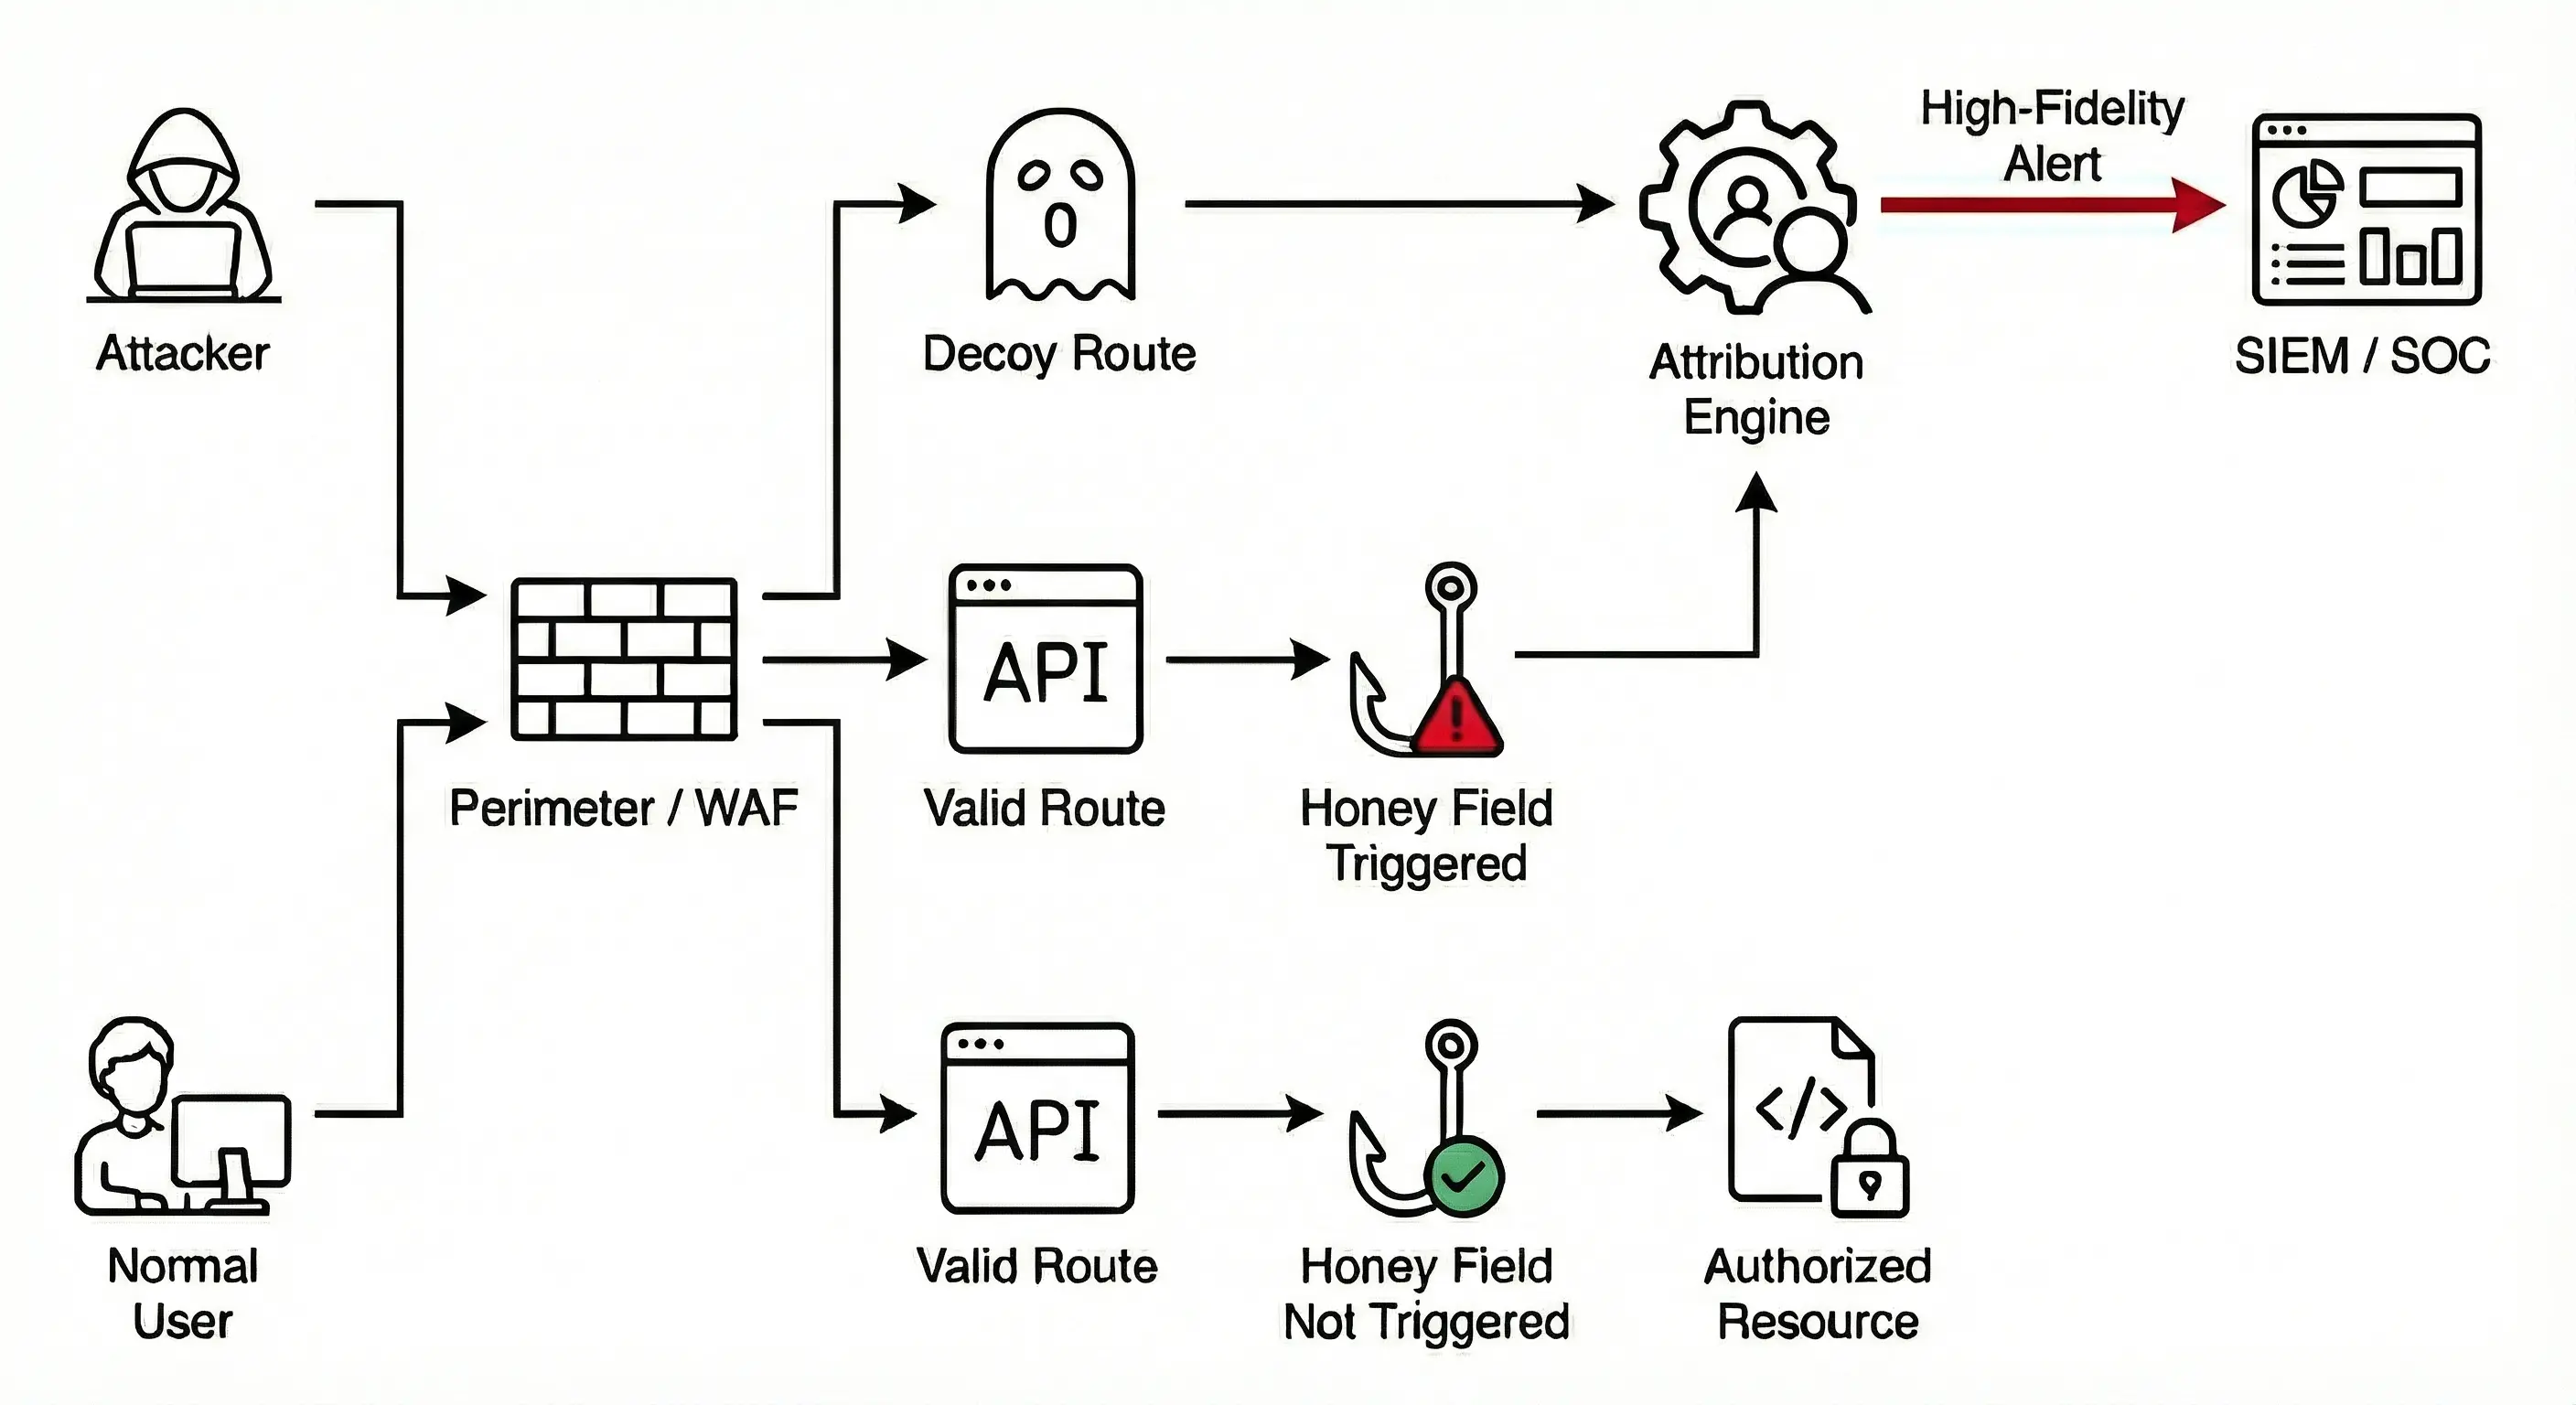
Open-source framework for embedding realistic decoy routes and honey fields into APIs to detect attackers probing business logic, converting…
 emrekybs/socmintelligence
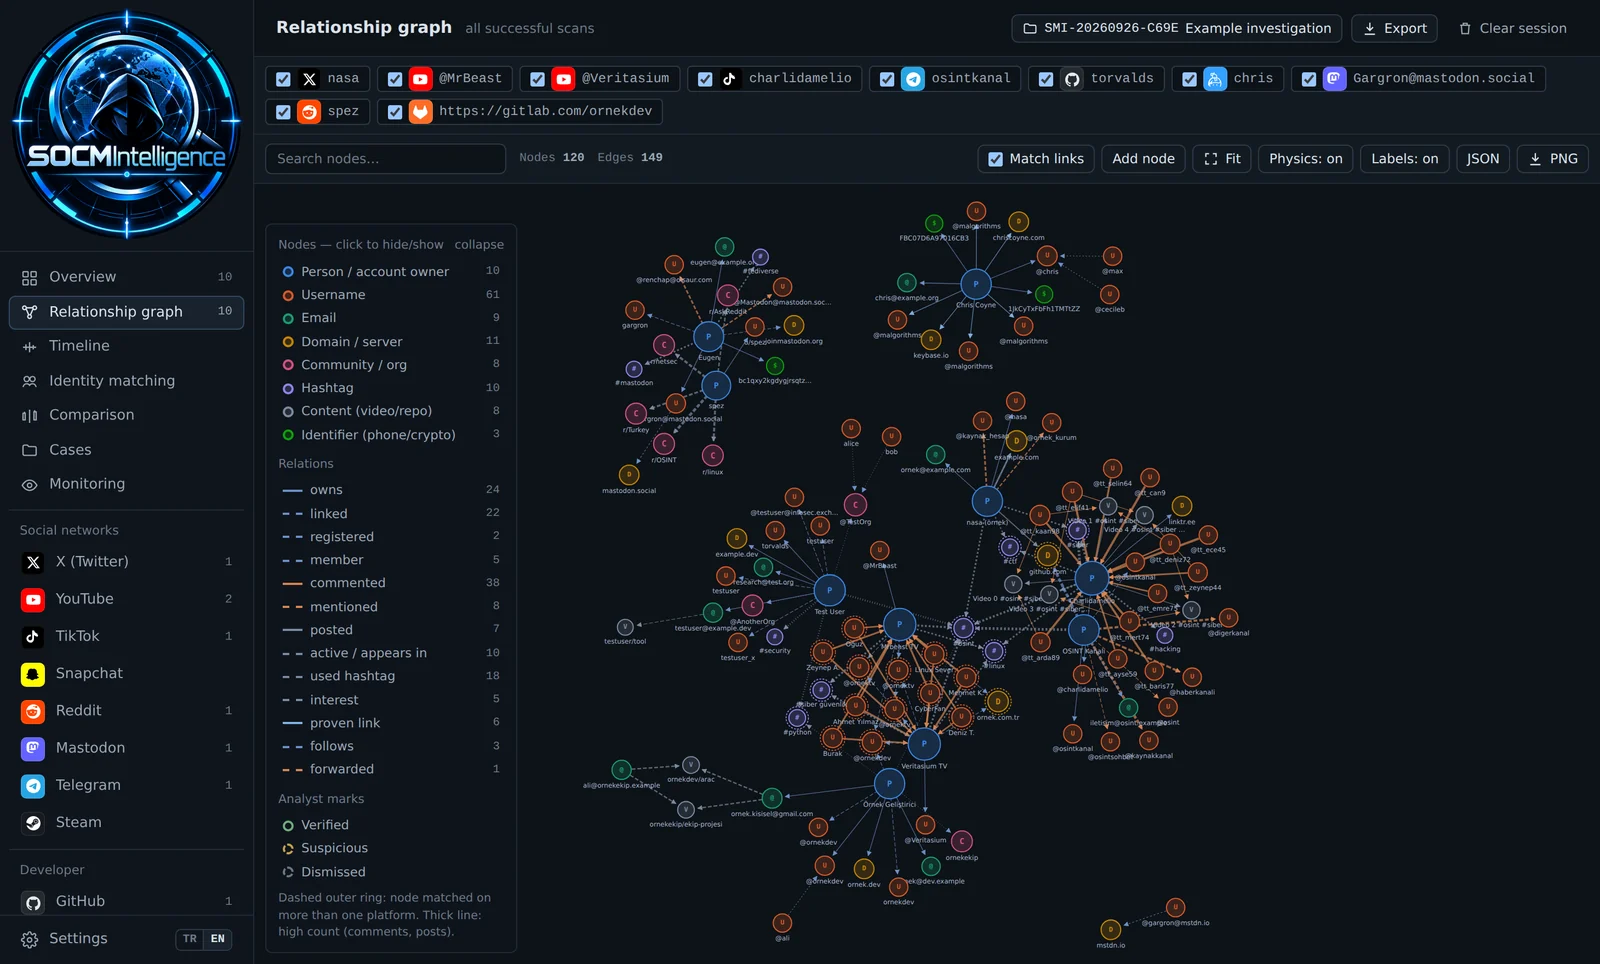
A modular OSINT & SOCMINT framework for social media intelligence, investigation, and public data analysis.
 osquery/osquery
SQL powered operating system instrumentation, monitoring, and analytics.
 adrecon/adrecon
PowerShell tool that extracts Active Directory artifacts via LDAP or ADWS and generates Excel reports for auditing, DFIR, and penetration testing.
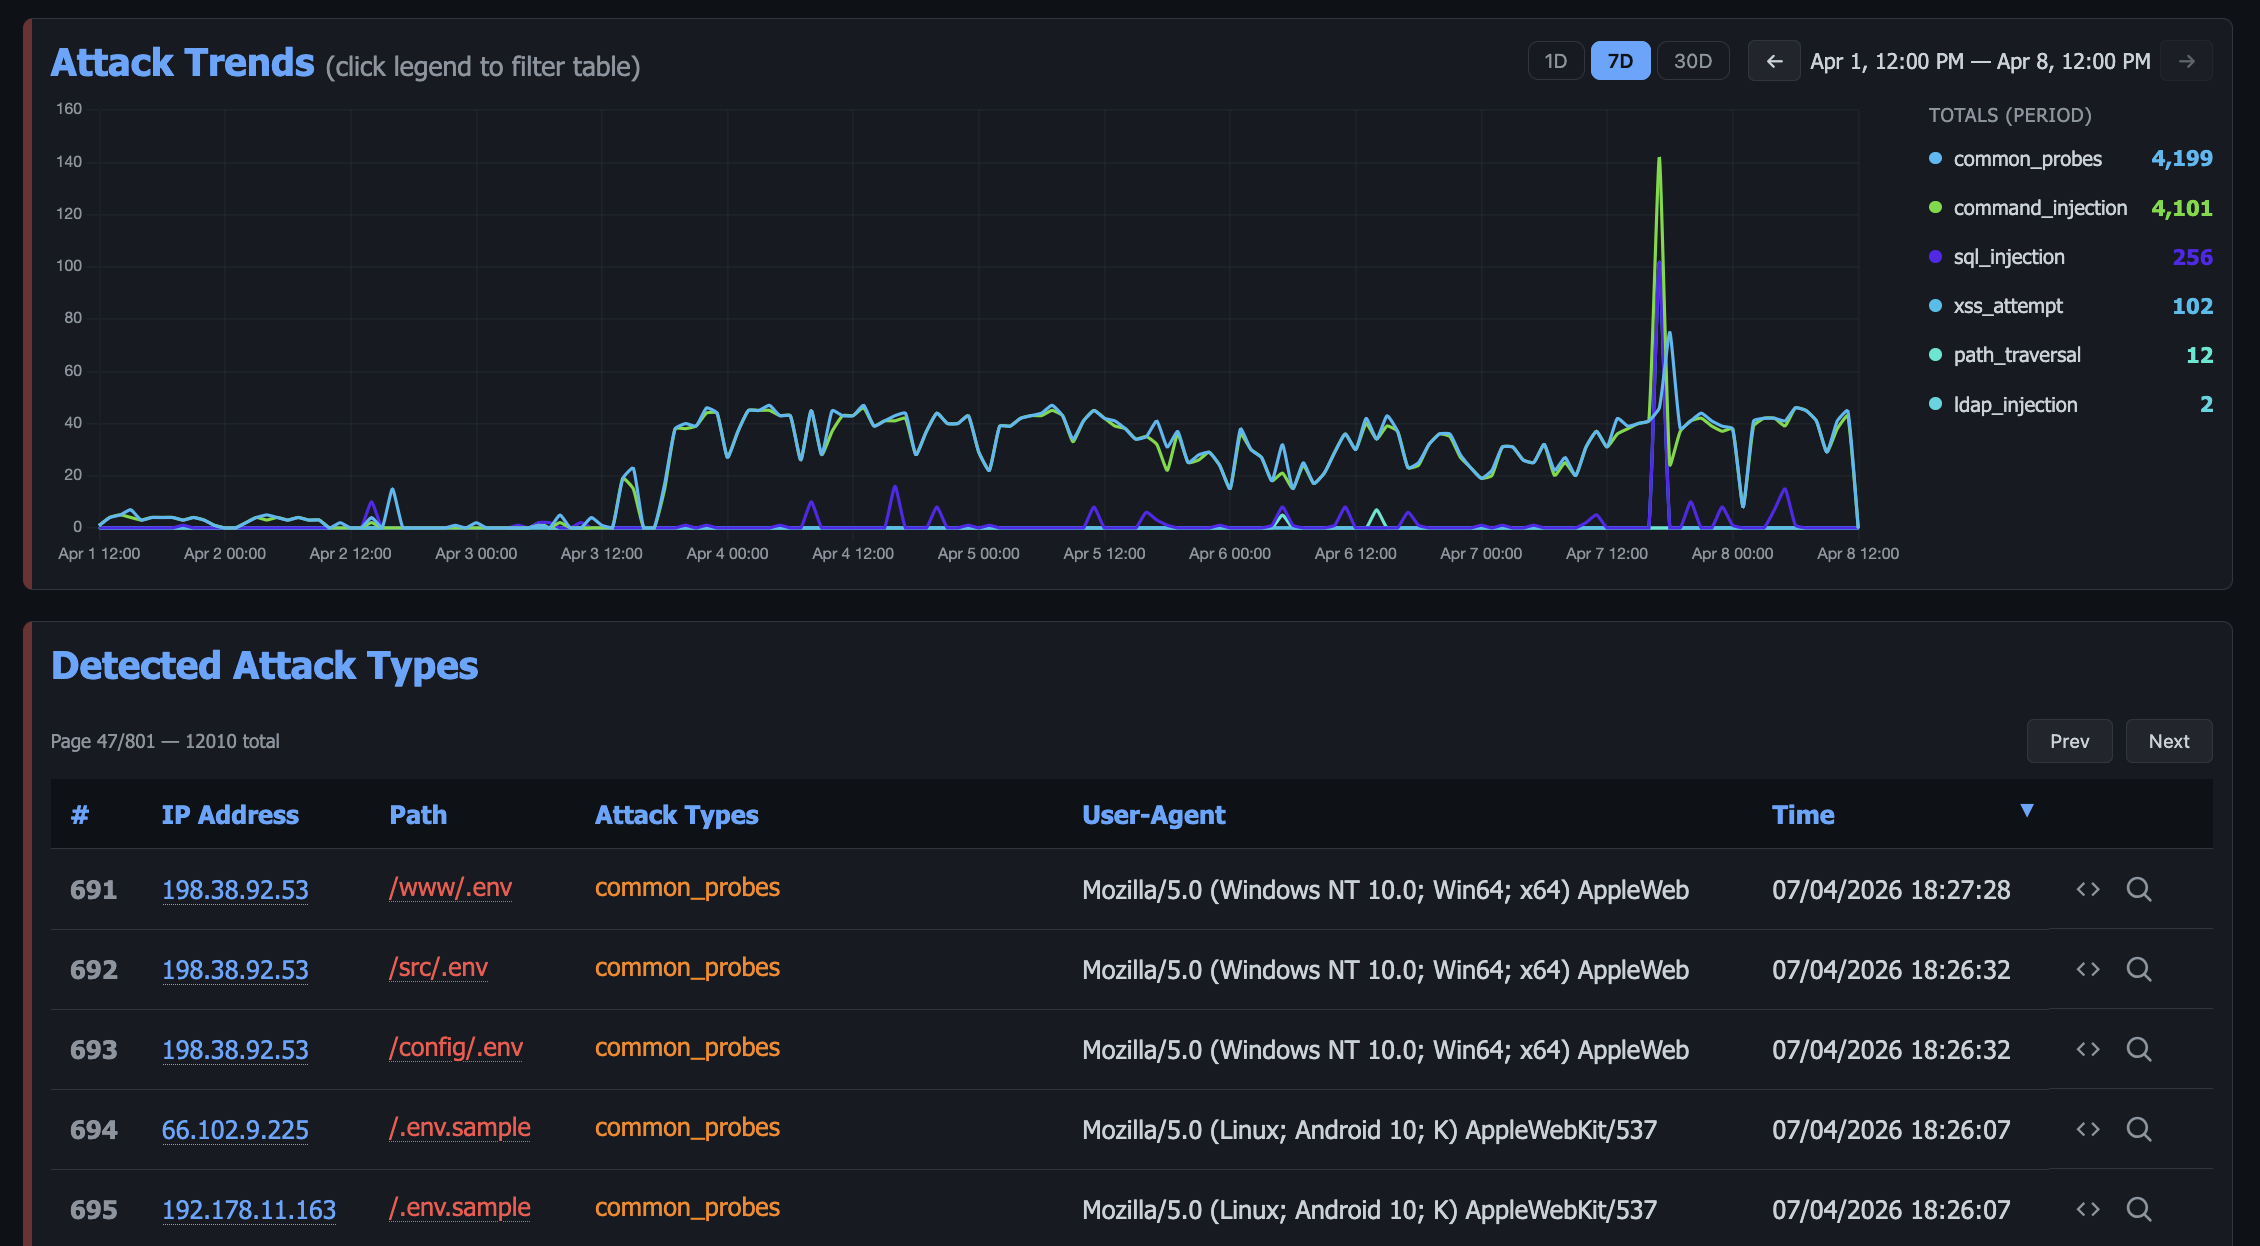 blessedrebus/krawl
Krawl is a customizable, lightweight, cloud-native web deception server and anti-crawler that creates fake web applications with low-hanging…
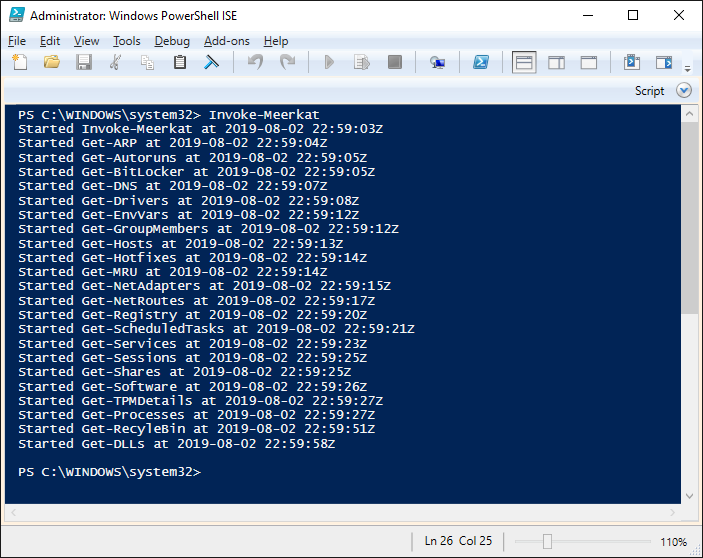 tonyphipps/meerkat
A collection of PowerShell modules designed for artifact gathering and reconnaisance of Windows-based endpoints.
 biggiesmallsag/nighthawkresponse
Incident Response Forensic Framework
 activecm/rita
Real Intelligence Threat Analytics (RITA) is a framework for detecting command and control communication through network traffic analysis.
 ctxis/snitchdns
Database Driven DNS Server with a Web UI
 owasp/honeypot-project
Deploy web honeypots to capture emerging attack data, analyze ModSecurity audit logs via ELK, and share threat intelligence with MISP for…

 viralmaniar/ddwpasterecon
DDWPasteRecon tool will help you identify code leak, sensitive files, plaintext passwords, password hashes. It also allow member of SOC & Blue Team…
 onapsis/cve-2020-6287_recon-scanner
Black-box vulnerability scanner and indicator-of-compromise analyzer for CVE-2020-6287 (RECON) in SAP NetWeaver Java applications, enabling rapid…
 infostealers-stats/credential-and-breach-monitoring
This repository provides a practical comparison of breach intelligence, dark web monitoring, and identity exposure services, with a focus on factors…
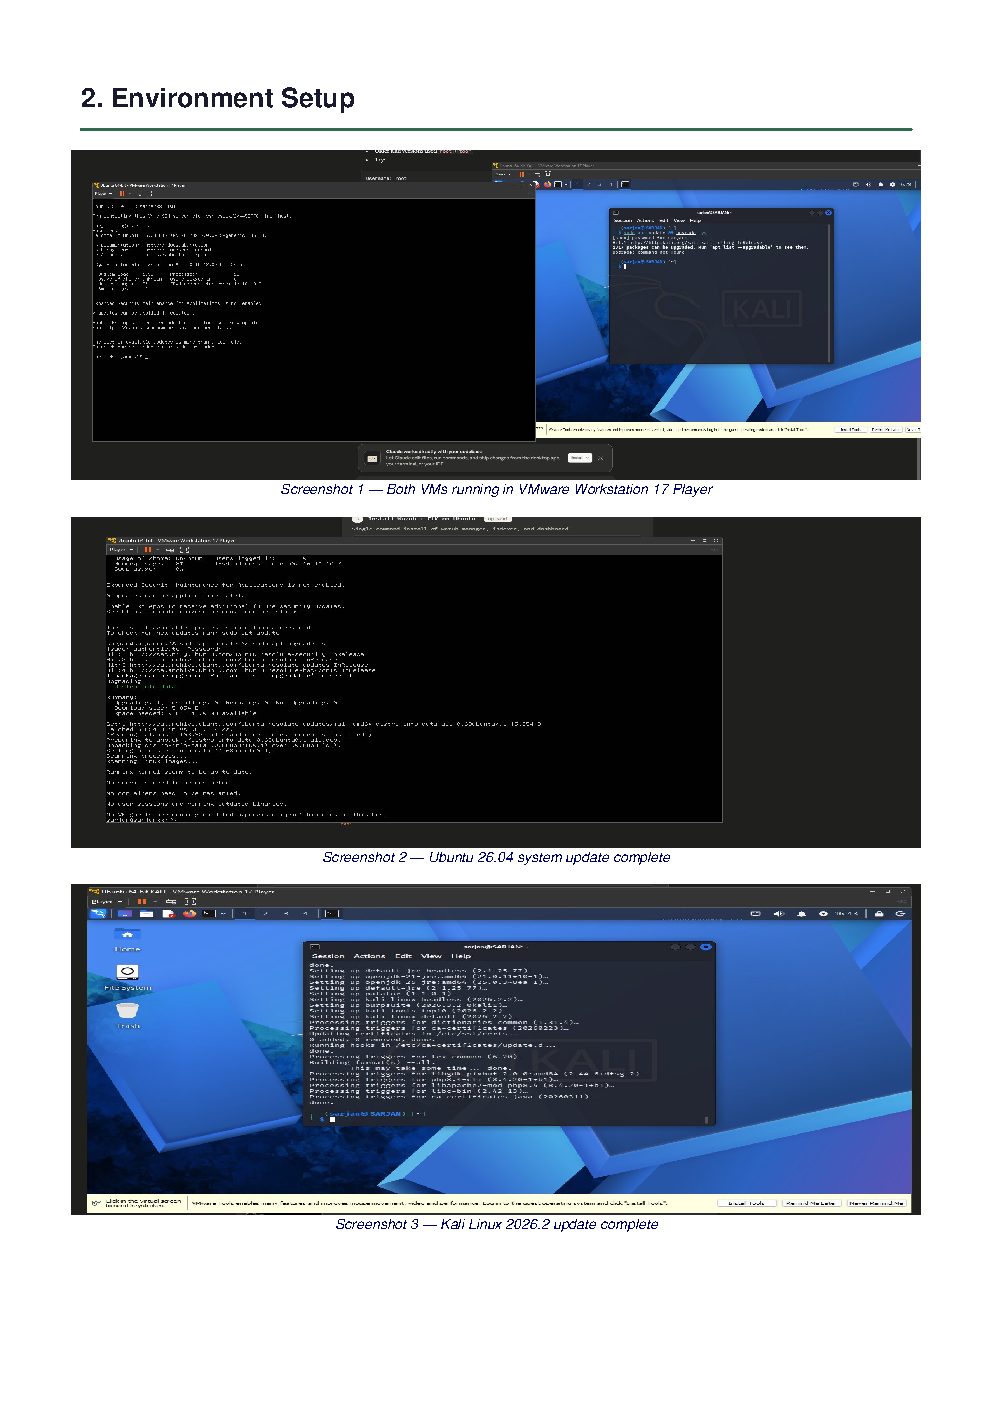 sarjanpatel22/siem-threat-detection-lab
Blue-team SIEM lab: Wazuh 4.7.5 detecting 7 simulated attacks (SSH brute force, Slowloris DoS / CVE-2007-6750, web attacks) with real-time MITRE…
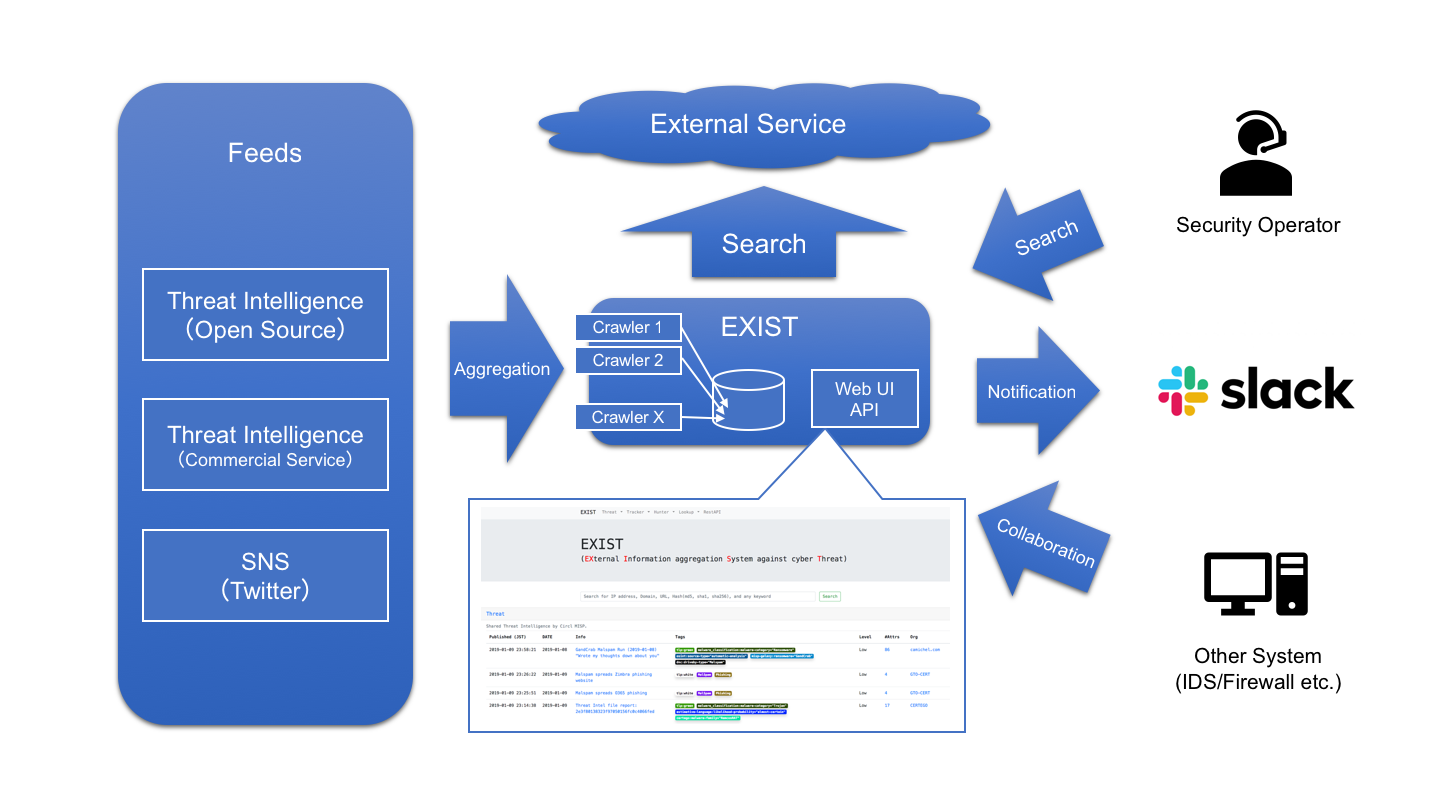 nict-csl/exist
EXIST is a web application for aggregating and analyzing cyber threat intelligence.
 duggytuxy/data-shield_ipv4_blocklist
Curated IPv4 blocklist of malicious addresses, refreshed every 6 hours for firewall and WAF ingestion, with split lists and CTI-ready formats for…