

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
94 results
androidqf preview

androidqf

GitHubmvt-project/androidqf

androidqf (Android Quick Forensics) helps quickly gathering forensic evidence from Android devices, in order to identify potential traces of…
android-securitydata-recoverydigital-forensics+4
325
7h 37m ago
OreNPMGuard preview

OreNPMGuard

GitHubrapticore/orenpmguard

Defense Against the Shai-Hulud Supply Chain Attack

code-analysisdevsecopseducation+6
139 months ago
mitmengine preview
Archived

mitmengine

GitHubcloudflare/mitmengine

A MITM (monster-in-the-middle) detection tool. Used to build MALCOLM:
defensive-toolsincident-responsenetwork-security+1
8122 years ago
Persistnux preview

Persistnux

GitHubgo-lanz/persistnux

Bash-based Linux persistence detection tool for DFIR investigations. Scans 15+ persistence mechanisms (systemd, cron, kernel modules, SSH,…

container-escapedigital-forensicseducation+7
32 months ago
IMDSpoof preview

IMDSpoof

GitHubgrahamhelton/imdspoof

IMDSPOOF is a cyber deception tool that spoofs the AWS IMDS service to return HoneyTokens that can be alerted on.
cloud-securitydefensive-toolsincident-response
1062 years ago
claude-code-guardrails preview

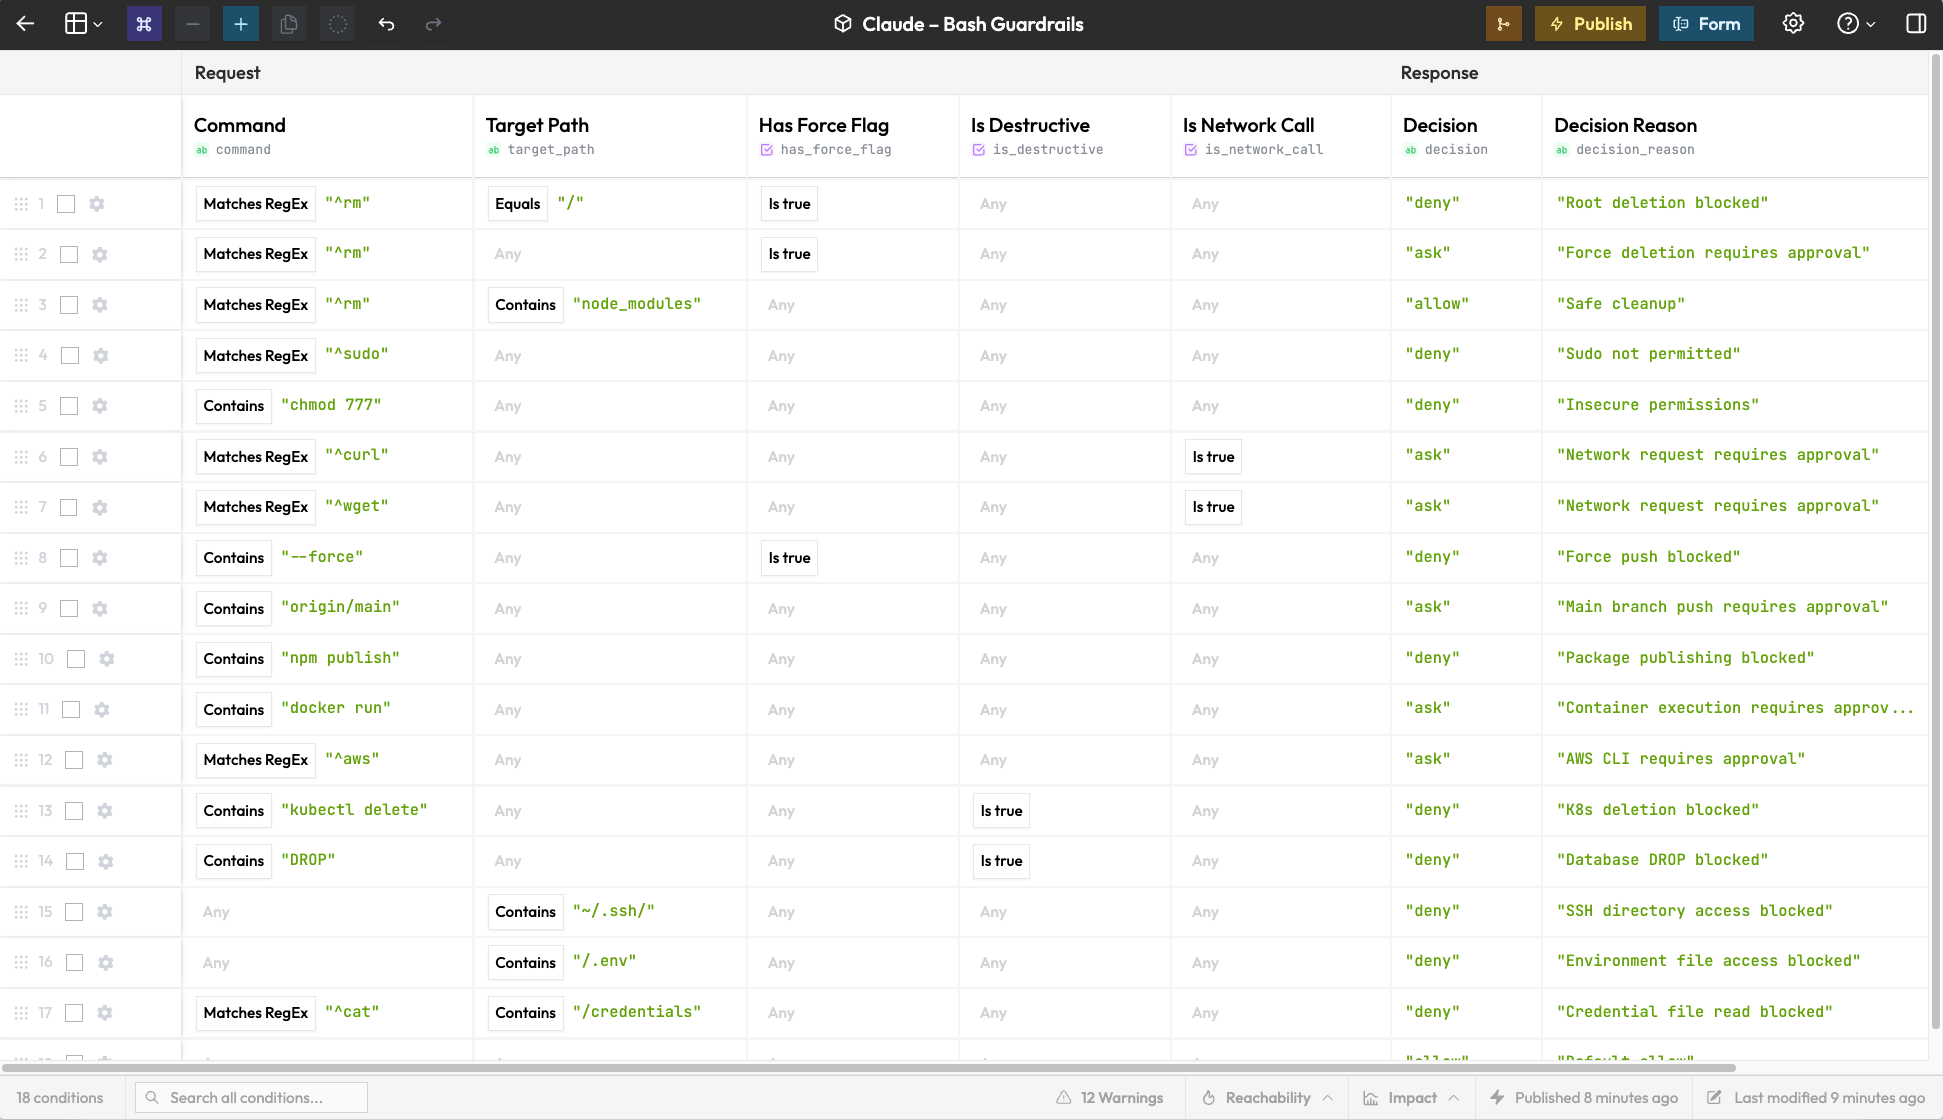
claude-code-guardrails

GitHubrulebricks/claude-code-guardrails

Real-time guardrails for Claude Code tool calls.

ai-securityapi-securityconfiguration-auditing+3
798 months ago
androidqf preview

androidqf

GitHubbotherder/androidqf

Portable forensic acquisition tool for Android devices that collects relevant data via USB debugging to identify potential spyware or compromise…
android-securitydigital-forensicsforensics+2
3118 months ago
Log4j-CVE-2021-44228-Remediation preview

Log4j-CVE-2021-44228-Remediation

GitHubdigital-dev/log4j-cve-2021-44228-remediation

This powershell script is intended to be used by anyone looking to remediate the Log4j Vulnerability within their environment. It can target multiple…
cloud-securitydefensive-toolsincident-response+3
2 years ago
reportly preview

reportly

GitHubsap8899/reportly

AzureAD/EntraID user activity reporter for blue teams. Input a suspicious user and time frame to receive a detailed report of user info, actions, and…

cloud-securityidentity-access-managementincident-response+2
963 years ago
Judge-Jury-and-Executable preview

Judge-Jury-and-Executable

GitHubadamwhitehat/judge-jury-and-executable

A file system forensics analysis scanner and threat hunting tool. Scans file systems at the MFT and OS level and stores data in SQL, SQLite or CSV.…

database-securitydigital-forensicsdisk-forensics+8
856 months ago
velociraptor preview

velociraptor

GitHubvelocidex/velociraptor

Digging Deeper....

data-recoverydefensive-toolsdigital-forensics+8
4.3k1 day ago
rita preview

rita

GitHubactivecm/rita

Real Intelligence Threat Analytics (RITA) is a framework for detecting command and control communication through network traffic analysis.
anomaly-detectioncommand-and-controldns-analysis+4
6553 months ago
DriverSentinel preview

DriverSentinel

GitHubbi8d0/driversentinel

DriverSentinel is a security tool developed in Go that detects malicious and vulnerable drivers on Windows systems by comparing them against the…

defensive-toolsforensicsincident-response+2
352 months ago
Blue-Team-Notes preview

Blue-Team-Notes

GitHubpurp1ew0lf/blue-team-notes

You didn't think I'd go and leave the blue team out, right?

curated-resourcesdigital-forensicseducation+5
1.8k15 days ago
GPEWebDefender preview

GPEWebDefender

GitHubgopasteverything/gpewebdefender

Lightweight web-attack monitor. One Go binary + SQLite. Not OSSEC, not a WAF.

defensive-toolsincident-responseinformation-gathering+8
21 month ago
netscaler-ctx697096-checker preview

netscaler-ctx697096-checker

GitHubthomaspoppelgaard/netscaler-ctx697096-checker

Read-only checker for Citrix NetScaler CTX697096 (CVE-2026-88771–88778): verifies build, CVE preconditions and upgrade risks, and sweeps public IoCs…
configuration-auditingdefensive-toolsforensics+9
125 days ago
bumblebee preview

bumblebee

GitHubperplexityai/bumblebee

Read-only developer endpoint scanner for on-disk package, extension, and developer-tool metadata, built to check exposure to known software…

devsecopsincident-responseinformation-gathering+3
5.1k6 days ago
pyrdp preview

pyrdp

GitHubgosecure/pyrdp

RDP monster-in-the-middle (mitm) and library for Python with the ability to watch connections live or after the fact

ctfeducationexploitation+9
1.8k4 months ago
Previous123456Next