
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
91 results
vol-rs preview

vol-rs

GitHubdaffainfo/vol-rs

Volatility 3 ported to Rust. Same output, much faster.
digital-forensicsforensicsincident-response+3
19120 days ago
halo-record preview

halo-record

GitHubbkuan001/halo-record

Tamper-evident audit trails for AI agents: hash-chained Runtime Records, dependency-free, verifiable by anyone.
ai-securityforensicsincident-response+1
8116 days ago
hawkopsec preview

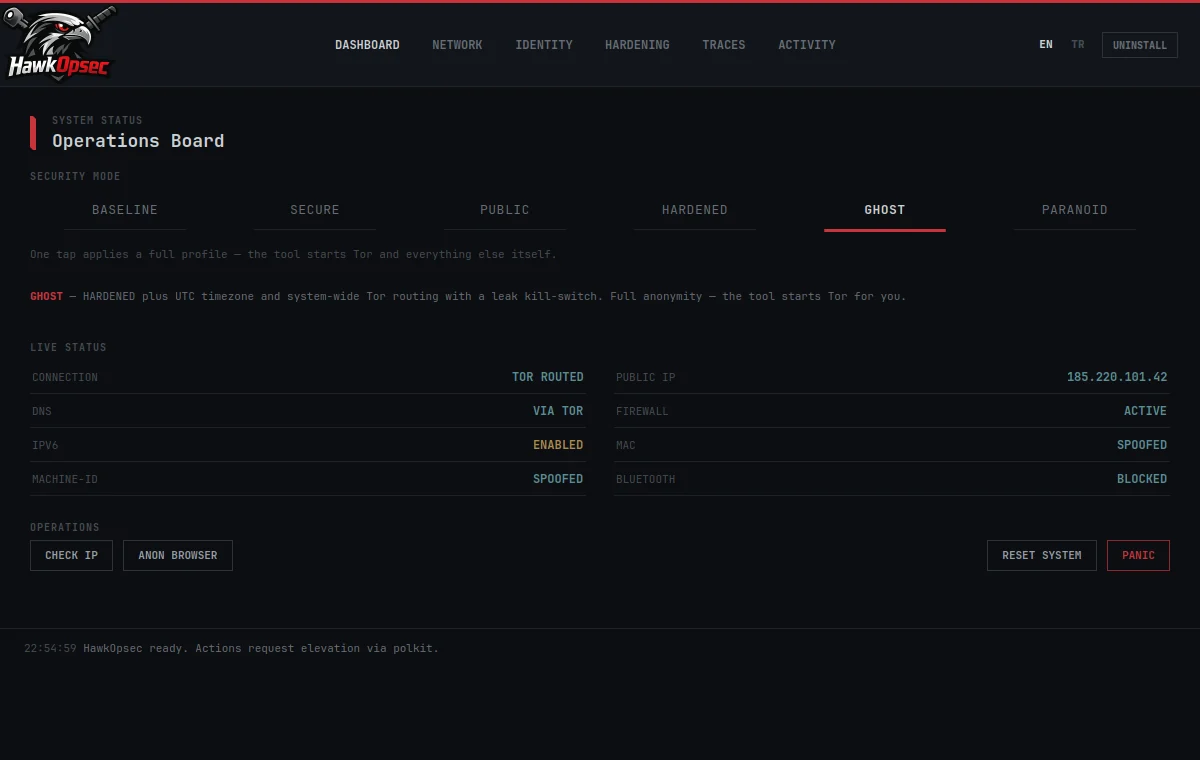
hawkopsec

GitHubemrekybs/hawkopsec

One-tap Linux OPSEC hardening & anonymity toolkit
configuration-auditingdefensive-toolsincident-response+2
319 days ago
Blue-Team-Notes preview

Blue-Team-Notes

GitHubpurp1ew0lf/blue-team-notes

You didn't think I'd go and leave the blue team out, right?

curated-resourcesdigital-forensicseducation+5
1.8k9 days ago
kraken preview

kraken

GitHubbotherder/kraken

Cross-platform Yara scanner written in Go
forensicsincident-responsemalware-analysis+1
3273 years ago
DriverSentinel preview

DriverSentinel

GitHubbi8d0/driversentinel

DriverSentinel is a security tool developed in Go that detects malicious and vulnerable drivers on Windows systems by comparing them against the…
defensive-toolsforensicsincident-response+2
365 months ago
Spip-Go preview

Spip-Go

GitHubhoneylabshq/spip-go

Spip network sensor written in Go

defensive-toolsincident-responseinformation-gathering+7
82 days ago
beelzebub preview

beelzebub

GitHubbeelzebub-labs/beelzebub

A secure low code deception runtime framework, leveraging AI for System Virtualization.

ai-securityapi-securitycontainer-security+7
2.2k1 day ago
botkube preview

botkube

GitHubkubeshop/botkube

An app that helps you monitor your Kubernetes cluster, debug critical deployments & gives recommendations for standard practices

cloud-securitycontainer-securitydevsecops+1
2.3k1 year ago
rita preview

rita

GitHubactivecm/rita

Real Intelligence Threat Analytics (RITA) is a framework for detecting command and control communication through network traffic analysis.
anomaly-detectioncommand-and-controldns-analysis+4
6503 months ago
spyre preview

spyre

GitHubspyre-project/spyre

simple YARA-based IOC scanner

forensicsincident-responseioc-management+1
1826 months ago
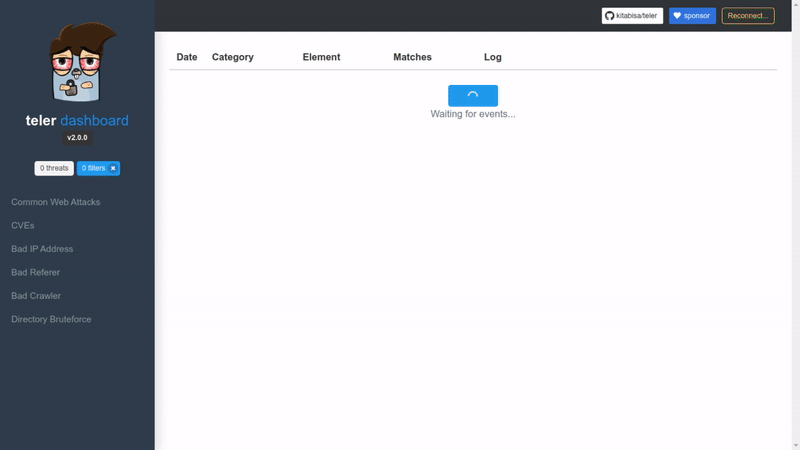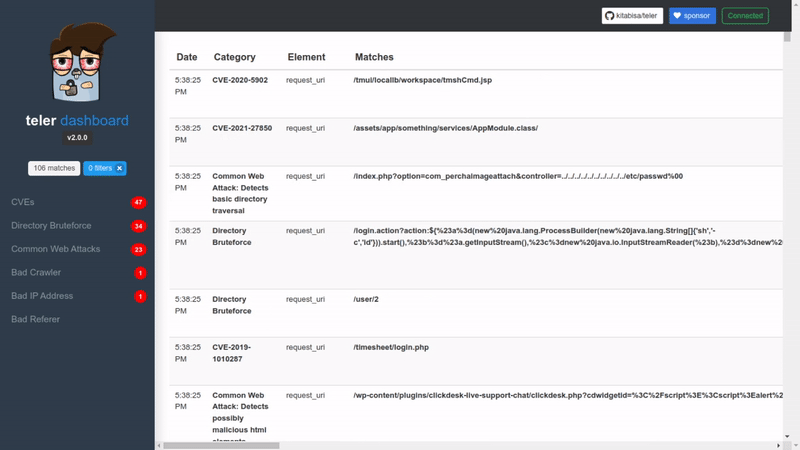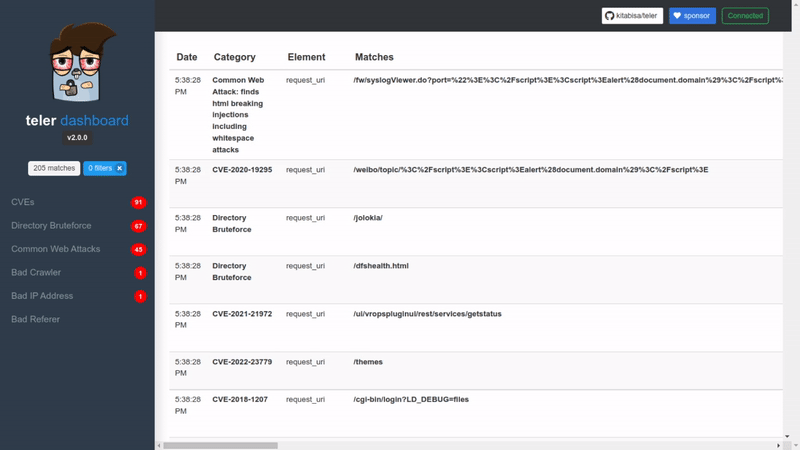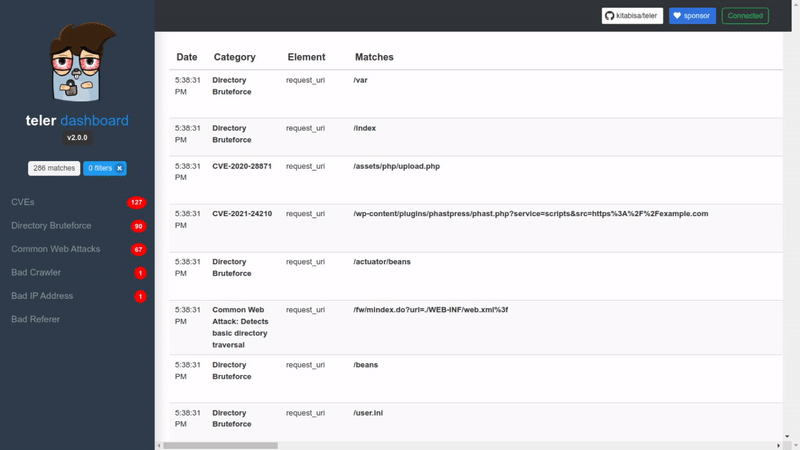
teler preview
Archived

teler

GitHubteler-sh/teler

Real-time HTTP Intrusion Detection

defensive-toolsincident-responseintrusion-detection+2
3.1k2 years ago
systeminformer preview

systeminformer

GitHubwinsiderss/systeminformer

Real-time Windows system monitor with advanced process, network, and disk analysis, stack trace debugging, malware detection, and service management.…

debuggersdigital-forensicsforensics+6
16.1k10h 26m ago
kubeshark preview

kubeshark

GitHubkubeshark/kubeshark

eBPF-powered network observability for Kubernetes. Indexes L4/L7 traffic with full K8s context, decrypts TLS without keys. Queryable by AI agents via…


ai-securitycloud-infrastructure-securitycloud-security+9
12.1k1 day ago
velociraptor preview

velociraptor

GitHubvelocidex/velociraptor

Digging Deeper....

data-recoverydefensive-toolsdigital-forensics+8
4.3k3 days ago
awesome-threat-detection preview

awesome-threat-detection

GitHub0x4d31/awesome-threat-detection

Curated list of threat detection and hunting resources: detection rules, SIEM and log analysis tools, endpoint/network monitoring, datasets,…
curated-resourceseducationincident-response+7
4.7k9 months ago
bumblebee preview

bumblebee

GitHubperplexityai/bumblebee

Read-only developer endpoint scanner for on-disk package, extension, and developer-tool metadata, built to check exposure to known software…
devsecopsincident-responseinformation-gathering+3
5.0k8 days ago
sysmon-modular preview

sysmon-modular

GitHubolafhartong/sysmon-modular

A repository of sysmon configuration modules

defensive-toolsdigital-forensicsincident-response+2
3.1k14 days ago
Previous123456Next