
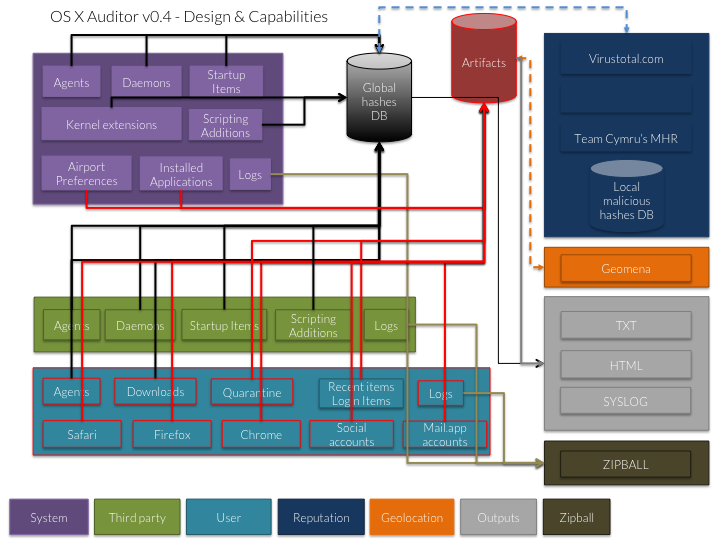
OSXAuditor
 jipegit/osxauditor
OS X Auditor is a free Mac OS X computer forensics tool
digital-forensicsdisk-forensicsforensics+4
jipegit/osxauditorOS X Auditor is a free Mac OS X computer forensics tool
 volatilityfoundation/volatility3
Advanced framework for extracting digital artifacts from volatile memory (RAM) samples, enabling deep forensic analysis of system runtime state…
 intuitem/ciso-assistant-community
GRC platform for risk management, compliance, and audit with 200+ frameworks, automatic control mapping, vulnerability management, and incident…
 intelowlproject/intelowl
Scalable threat intelligence platform that enriches observables and files using 200+ analyzers, with built-in GUI, REST API, and automated workflows…
 rabobank-cdc/dettect
Detect Tactics, Techniques & Combat Threats
 suprhackersteve/crescendo
Crescendo is a swift based, real time event viewer for macOS. It utilizes Apple's Endpoint Security Framework.
 activecm/rita
Real Intelligence Threat Analytics (RITA) is a framework for detecting command and control communication through network traffic analysis.
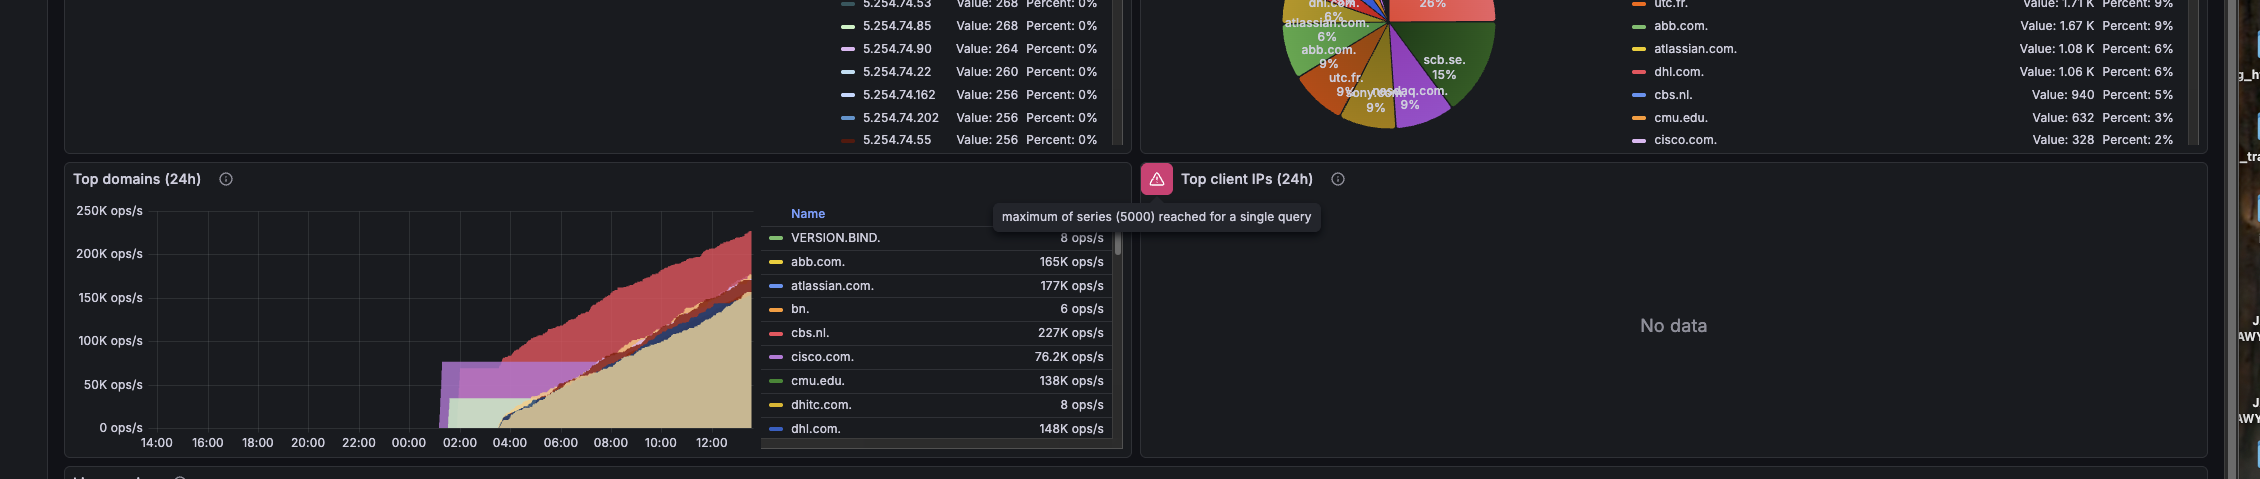
 aurva-io/aiostack
AI runtime inventory: discover shadow AI, trace LLM calls
 purp1ew0lf/blue-team-notes
You didn't think I'd go and leave the blue team out, right?
 rabbitstack/fibratus
Security sensor for realtime threat detection and protection
 nebulock-inc/agentic-threat-hunting-framework
ATHF is a framework for agentic threat hunting - building systems that can remember, learn, and act with increasing autonomy.
 adversarial-detection-engineering/adversarial-detection-engineering-framework
A framework and taxonomy for identifying, classifying, and reasoning about detection logic bugs in SIEM, EDR, and XDR rules, with concrete examples…
 spectralzero/netscope
Offline-first network investigation and response platform for Windows. Turns a pcap or live capture into a full forensic verdict — attack story,…
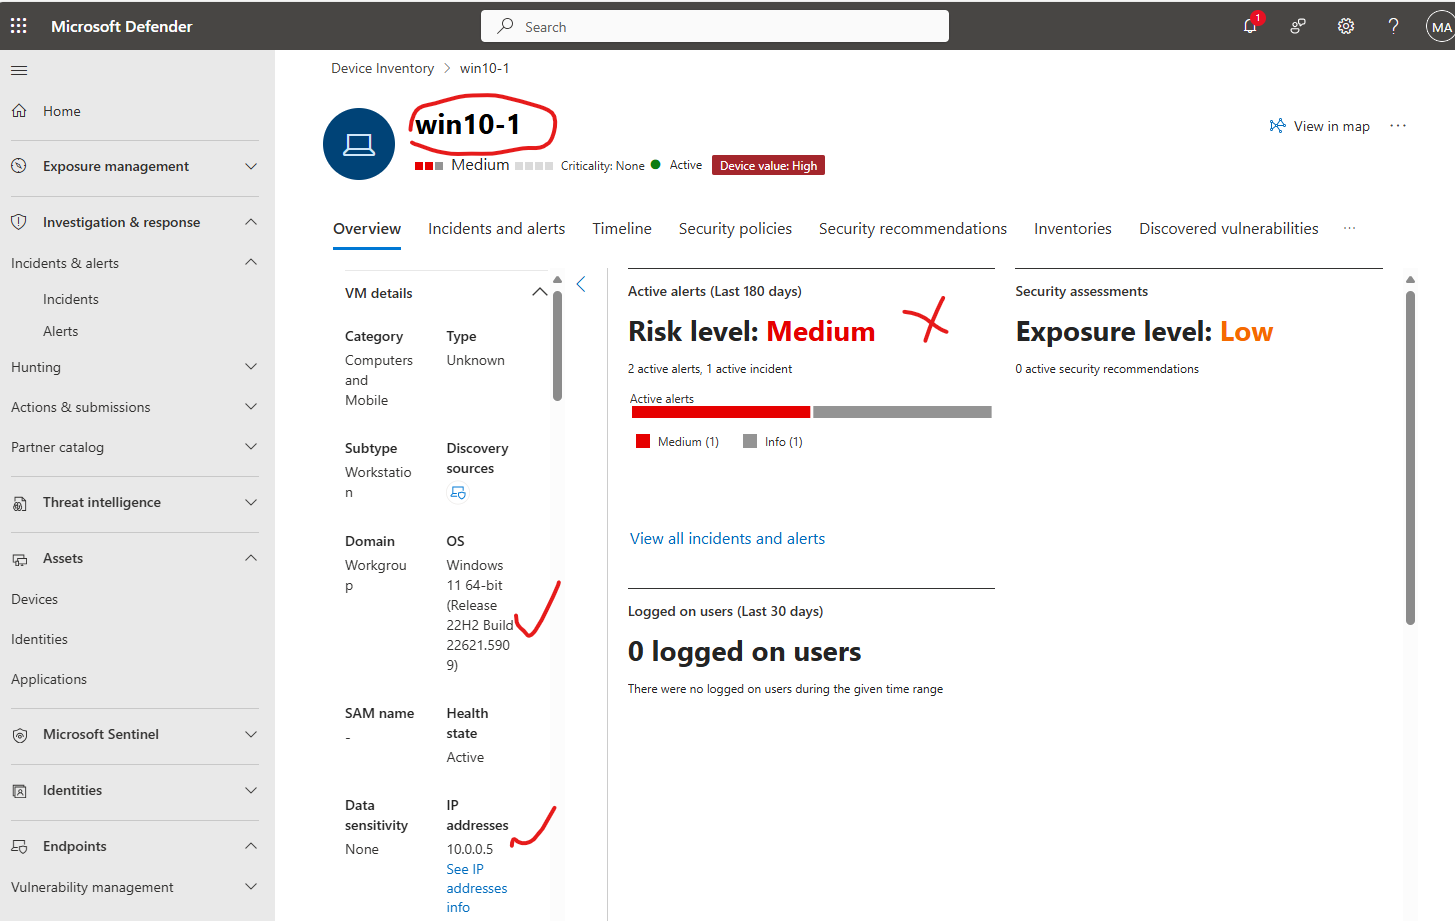 kamalideenak/microsoft-defender-for-endpoint-deployment-on-windows-10-11-device
This repository documents how deployment of Microsoft Defender for Endpoint on a Windows 11 device, including onboarding via local script, enabling…