
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
226 results
NginxHunter preview

NginxHunter

GitHubemrekybs/nginxhunter

Analyzes Nginx access logs to detect SQL injection, scanner tools, webshells, and exploitation attempts, aiding system administrators in server…

defensive-toolsincident-responselog-analysis+2
5
2 years ago
passivedns preview

passivedns

GitHubgamelinux/passivedns

A network sniffer that logs all DNS server replies for use in a passive DNS setup
dns-analysisforensicsincident-response+3
1.7k11 days ago
BruteRatel-DetectionTools preview

BruteRatel-DetectionTools

GitHubimmersive-labs-sec/bruteratel-detectiontools

A collection of Tools and Rules for decoding Brute Ratel C4 badgers
command-and-controldefensive-toolsincident-response+3
674 years ago
Simple-Live-Data-Collection preview

Simple-Live-Data-Collection

GitHubletsdefendio/simple-live-data-collection

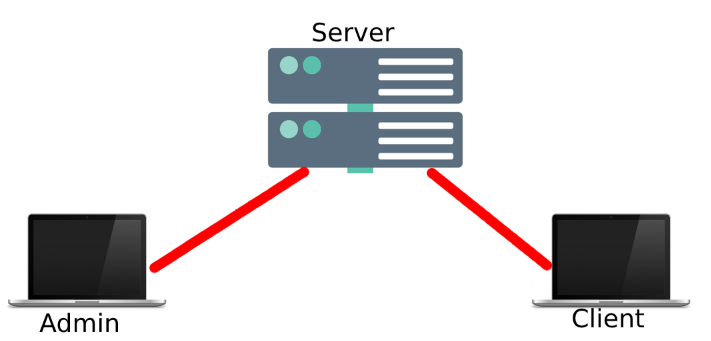
Client-server tool for live data collection during incident response. Admin sends requests to clients to gather system information for forensic…
digital-forensicsforensicsincident-response+1
226 years ago
squidmagic preview

squidmagic

GitHubaws-alchemy/squidmagic

analyze a web-based network traffic 🕶 to detect central command and control servers
command-and-controldns-analysisincident-response+3
818 years ago
FileWatchTower preview

FileWatchTower

GitHubiomoath/filewatchtower

FWT is a security analysis and file monitoring tool that utilizes Sysmon events.
digital-forensicsforensicshash-analysis+4
292 years ago
mediator preview

mediator

GitHublawndoc/mediator

An extensible, end-to-end encrypted reverse shell that works across networks without port forwarding.
command-and-controlencryption-decryption-toolsincident-response+5
1002 years ago
bulwark preview

bulwark

GitHubsoftrams/bulwark

An organizational asset and vulnerability management tool, with Jira integration, designed for generating application security reports.

api-securityauthentication-authorizationconfiguration-auditing+3
18711 months ago
capa preview

capa

GitHubmandiant/capa

Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…

ai-assisted-reversingbinary-analysiscode-analysis+10
6.3k9 days ago
sandbox-runtime preview

sandbox-runtime

GitHubanthropic-experimental/sandbox-runtime

A lightweight sandboxing tool for enforcing filesystem and network restrictions on arbitrary processes at the OS level, without requiring a container.

configuration-auditingcontainer-securitydefensive-tools+4
6.9k4 days ago
IPED preview

IPED

GitHubsepinf-inc/iped

IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…
data-recoverydigital-forensicsdisk-forensics+9
3.1k6 days ago
hayabusa preview

hayabusa

GitHubyamato-security/hayabusa

Multi-threaded Windows event log forensics timeline generator and threat hunting tool with full Sigma rule support, producing CSV/JSON timelines for…

digital-forensicsforensicsincident-response+2
3.4k1 day ago
ProcDump-for-Linux preview

ProcDump-for-Linux

GitHubmicrosoft/procdump-for-linux

A Linux version of the ProcDump Sysinternals tool

debuggersdynamic-analysis-sandboxingincident-response+2
3.1k1 day ago
OSXAuditor preview

OSXAuditor

GitHubjipegit/osxauditor

OS X Auditor is a free Mac OS X computer forensics tool
digital-forensicsdisk-forensicsforensics+4
3.1k6 years ago
DeepBlueCLI preview

DeepBlueCLI

GitHubsans-blue-team/deepbluecli

PowerShell-based threat hunting tool that analyzes Windows Event Logs to detect malicious activity including credential attacks, obfuscated commands,…

digital-forensicsincident-responseintrusion-detection+2
2.4k3 years ago
awesome-lists preview

awesome-lists

GitHubmthcht/awesome-lists

Curated repository of threat intelligence feeds, IoC lists, YARA rules, and DFIR tool references for SOC/CERT/CTI detection and incident response.
curated-resourcesdigital-forensicseducation+4
2.0k1h 15m ago
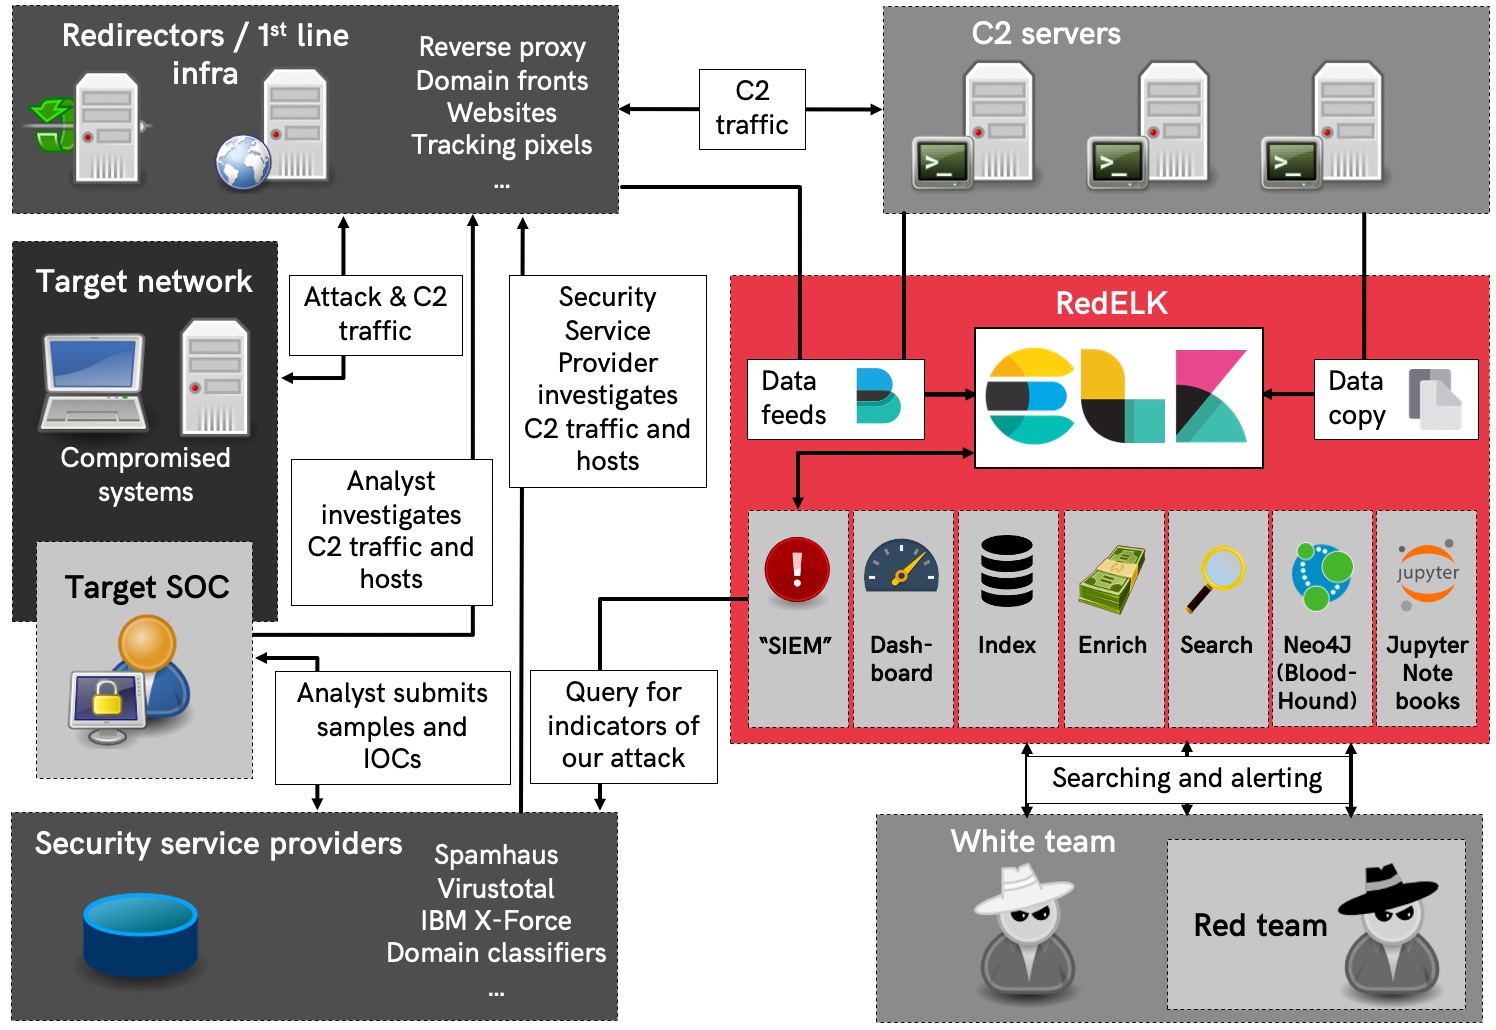
RedELK preview

RedELK

GitHuboutflanknl/redelk

Red Team's SIEM - tool for Red Teams used for tracking and alarming about Blue Team activities as well as better usability in long term operations.

defensive-toolsincident-responseinformation-gathering+4
2.7k11 months ago
attackgen preview

attackgen

GitHubmrwadams/attackgen

AttackGen is a cybersecurity incident response testing tool that leverages the power of large language models and the comprehensive MITRE ATT&CK…

ai-securityctfeducation+5
1.3k6 days ago
Previous12…13Next